Cybersecurity takes a leap forward with AI tools and techniques

Cybersecurity takes a leap forward with AI tools and techniques

Experts have taken a crucial action towards harnessing a variety of artificial intelligence acknowledged as deep reinforcement mastering, or DRL, to protect personal computer networks.

Autonomus cyber defense framework

When confronted with complex cyberattacks in a demanding simulation location, deep reinforcement understanding was successful at stopping adversaries from reaching their ambitions up to 95 per cent of the time. The outcome features promise for a part for autonomous AI in proactive cyber protection.

Experts from the Office of Energy’s Pacific Northwest National Laboratory (PNNL) documented their findings in a analysis paper.

The starting up position was building a simulation ecosystem to check multistage assault eventualities involving distinct kinds of adversaries. The development of such a dynamic assault-defense simulation environment for experimentation by itself is a win. The setting makes it possible for scientists to assess the performance of unique AI-centered defensive solutions less than controlled take a look at options.

These resources are crucial for evaluating the general performance of deep reinforcement mastering algorithms. The technique is emerging as a powerful conclusion-help instrument for cybersecurity experts – a protection agent with the capability to study, adapt to immediately modifying circumstances, and make selections autonomously. While other sorts of artificial intelligence are normal to detect intrusions or filter spam messages, deep reinforcement discovering expands defenders’ talents to orchestrate sequential choice-earning programs in their daily encounter-off with adversaries.

Deep reinforcement finding out gives smarter cybersecurity, the skill to detect improvements in the cyber landscape before, and the option to choose preemptive steps to scuttle a cyberattack.

DRL: Conclusions in a wide assault space

“An efficient AI agent for cybersecurity requires to feeling, understand, act and adapt, based mostly on the info it can collect and on the results of choices that it enacts,” claimed Samrat Chatterjee, a data scientist who introduced the team’s function. “Deep reinforcement learning holds fantastic opportunity in this area, where by the selection of technique states and action options can be massive.”

DRL, which brings together reinforcement learning and deep understanding, is especially adept in scenarios in which a sequence of conclusions in a elaborate natural environment need to have to be produced. Fantastic selections leading to fascinating effects are strengthened with a optimistic reward (expressed as a numeric benefit) undesirable selections main to undesirable outcomes are discouraged by using a detrimental expense.

It is comparable to how people today find out quite a few duties. A youngster who does their chores could acquire positive reinforcement with a preferred playdate a youngster who doesn’t do their perform gets unfavorable reinforcement, like the takeaway of a electronic system.

“It’s the identical notion in reinforcement understanding,” Chatterjee claimed. “The agent can pick from a established of steps. With just about every motion will come feed-back, excellent or undesirable, that becomes part of its memory. There’s an interplay among discovering new opportunities and exploiting previous encounters. The purpose is to produce an agent that learns to make very good choices.”

MITRE ATT&CK and Open AI Health club

The staff utilised an open up-source program toolkit recognized as Open AI Gym to build a tailor made and controlled simulation environment to appraise the strengths and weaknesses of 4 deep reinforcement understanding algorithms.

They also applied the MITRE ATT&CK framework and included 7 methods and 15 strategies deployed by a few unique adversaries. Defenders had been equipped with 23 mitigation actions to halt or stop an attack’s progression.

The stages of the attack integrated techniques of reconnaissance, execution, persistence, protection evasion, command and command, assortment and exfiltration (when knowledge is transferred out of the system). An assault was recorded as a earn for the adversary if they efficiently reached the last exfiltration phase.

“Our algorithms function in a aggressive environment—a contest with an adversary intent on breaching the technique,” mentioned Chatterjee. “It’s a multistage assault, in which the adversary can pursue multiple assault paths that can improve over time as they try to go from reconnaissance to exploitation. Our challenge is to display how defenses based mostly on deep reinforcement discovering can end these types of an attack.”

DQN (Deep Q-Community)

The workforce educated defensive brokers based mostly on four deep reinforcement studying algorithms: DQN and three variants of what’s regarded as the actor-critic tactic. The brokers have been qualified with simulated info about cyberattacks, then examined from attacks that they experienced not noticed in teaching. DQN performed the ideal.

The very least advanced assaults (based mostly on various ranges of adversary skill and persistence): DQN stopped 79 per cent of assaults halfway through attack stages and 93 {b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1} by the last stage.

Reasonably complex assaults: DQN stopped 82 per cent of assaults midway and 95 percent by the final phase.

Most refined attacks: DQN stopped 57 {b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1} of assaults halfway and 84 {b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1} by the remaining stage—far larger than the other a few algorithms.

“Our target is to generate an autonomous protection agent that can discover the most very likely future step of an adversary, plan for it, and then answer in the greatest way to defend the program,” Chatterjee said.

Regardless of the progress, no just one is ready to entrust cyber defense solely up to an AI method. In its place, a DRL-based cybersecurity method would require to perform in concert with people, mentioned coauthor Arnab Bhattacharya, previously of PNNL.

“AI can be fantastic at defending versus a distinct tactic but isn’t as excellent at being familiar with all the techniques an adversary may well acquire,” Bhattacharya mentioned. “We are nowhere in the vicinity of the phase exactly where AI can change human cyber analysts. Human feedback and steering are vital.”

In addition to Chatterjee and Bhattacharya, authors of the AAAI workshop paper include things like Mahantesh Halappanavar of PNNL and Ashutosh Dutta, a previous PNNL scientist. The get the job done was funded by DOE’s Workplace of Science.
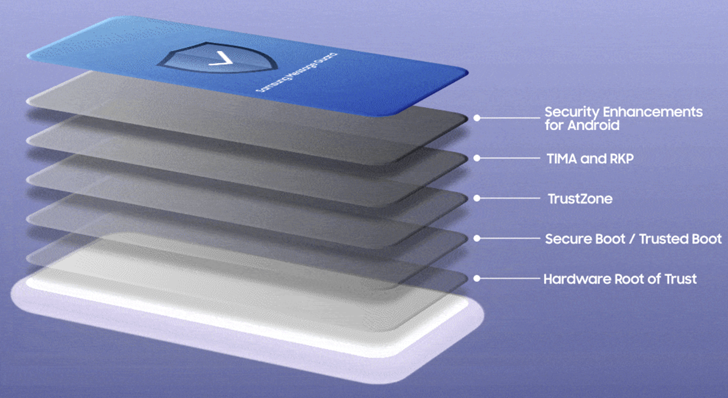
Samsung Introduces New Feature to Protect Users from Zero-Click Malware Attacks

Samsung Introduces New Feature to Protect Users from Zero-Click Malware Attacks

Feb 20, 2023Ravie LakshmananCell Protection / Zero Working day

Samsung Introduces New Feature to Protect Users from Zero-Click Malware Attacks

Samsung has introduced a new characteristic referred to as Message Guard that arrives with safeguards to guard people from malware and adware through what is referred to as zero-click on attacks.

The South Korean chaebol claimed the alternative “preemptively” secures users’ units by “restricting exposure to invisible threats disguised as image attachments.”

The stability feature, available on Samsung Messages and Google Messages, is at present constrained to the Samsung Galaxy S23 collection, with strategies to extend it to other Galaxy smartphones and tablets afterwards this 12 months that are jogging on Just one UI 5.1 or larger.

Zero-click on attacks are remarkably-focused and subtle assaults that exploit earlier mysterious flaws (i.e., zero-days) in software to bring about execution of destructive code with out demanding any user interaction.

Unlike classic strategies of remotely exploiting a machine wherein threat actors count on phishing techniques to trick a consumer into clicking on a destructive backlink or opening an rogue file, these assaults circumvent the will need for social engineering fully and provide an adversary with an entry stage.

A the greater part of the zero-click exploits are engineered to consider gain of vulnerabilities in apps these types of as messaging, SMS, or electronic mail applications that receive and approach untrusted knowledge.

As a consequence, if there exists a stability vulnerability in the manner an app interprets the incoming information, a threat actor could weaponize this shortcoming to craft a malicious impression that, when despatched to a target’s machine, immediately executes the code embedded within just it.

The absence of interaction included in zero-click on attacks indicates there are much less traces of any nefarious exercise, making them hugely-prized equipment to produce spy ware capable of monitoring people and harvesting a prosperity of delicate information.

Zero-Click Malware Attacks

Samsung’s Information Guard is effective versus a range of image formats, which includes PNG, JPG/JPEG, GIF, ICO, WEBP, BMP, and WBMP, and effectively acts as a sandbox that is made to quarantine photographs obtained by means of the app from the relaxation of the functioning method.

“Information Guard checks the file bit by bit and processes it in a controlled atmosphere to make sure it simply cannot infect the relaxation of your unit,” the firm said.

The function is also analogous to a element in Apple’s iMessage termed BlastDoor that the tech large included in iOS 14 as a means to counter zero-click attacks by way of its messaging app.

Apple, final calendar year, also released an “intense, optional protection” placing dubbed Lockdown Manner that hardens iPhones and iPads versus “really rare and very advanced cyber assaults.”

Discovered this report appealing? Observe us on Twitter and LinkedIn to examine far more exclusive material we post.

Goldman Sachs explains why you should ‘buy’ these 2 cybersecurity stocks

Goldman Sachs explains why you should ‘buy’ these 2 cybersecurity stocks

Our electronic environment operates on pc tech, and that tech is only going to turn into much more autonomous and more ubiquitous. And that, in switch, only underscores the ongoing worth of online security. With electronic automation developing, it is more critical than ever, right now, to start out firming up the digital protections.

Versus this backdrop, Goldman Sachs’ Gabriela Borges has turned her eye on the cybersecurity sector. The analyst sees numerous market dynamics that are favorable for very long-phrase buyers, including: “(1) Multi-product or service platforms have obtained momentum and are nearer to solving the challenge of remaining ground breaking in subsegments historically outlined by boom and bust product or service cycles. (2) The business is fewer cyclical as mix shifts away from components and towards SaaS, and offered constant prioritization of protection expend in business budgets.”

Borges does not go away us with a macro watch of the industry. The analyst goes on to give a drill-down to the micro degree, and picks out two cybersecurity shares that she sees as probable winners for the very long haul.

In simple fact, Borges is not the only just one singing these stocks’ praises. According to the TipRanks platform, each individual offers a “Strong Buy” consensus rating from the broader analyst community, and provides double-digit upside potential for the calendar year forward. Let us just take a nearer seem.

CrowdStrike Holdings (CRWD)

The initially Goldman-select we’ll glance at is CrowdStrike, the producer of the higher-conclude Falcon Endpoint Security line, and a chief in the cybersecurity ecosystem. CrowdStrike’s merchandise have set an industry regular for on line network defense and for digital safety, and consist of a selection of cloud-based mostly modules for a wide assortment of applications. The firm can make the goods available by membership by the Software program-as-a-Support model.

The corporation noted some seem metrics in its final quarterly report, for Q3 of fiscal 2023. Income was up 53{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1} 12 months-about-yr, at $581 million, and yearly recurring earnings, at $2.34 billion, was up 54{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1}. On the base line, CrowdStrike reported a fiscal Q3 earnings of 40 cents per share, by non-GAAP steps, beating consensus estimate of 32 cents for every share.

However, the business furnished revenue steerage that fell limited of estimates. Especially, Q4 income is expected to be in a range of $619.1 million to $628.2 million, underneath Road estimates of $634.2 million.

Although acknowledging that existing current market disorders act as a headwind on the inventory, Goldman Sachs’ Gabriela Borges believes it is very well-put for robust expansion.

“We hope to see a moderation in development rate… driven largely by slower advancement in the endpoint TAM and a slower rate of sector share obtain – and we consider this is perfectly comprehended by the marketplace. Over the medium phrase, 1) we hope to see constant advancement in endpoint (80{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1}+ of ARR), primarily based on our base-up industry share model suggesting subsequent-gen endpoint systems hold close to 50{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1} share nowadays 2) we expect to see outsized development in cloud, exactly where our market discussions counsel CrowdStrike is aggressive offered its main competencies in info assortment and monitoring,” Borges opined.

“Taken alongside one another with solid FCF generation right now and a reset to quantities in 3Q23 (2023 Avenue revenue has been revised down 3{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1} around the final 3 months), we believe that danger/reward is interesting,” the analyst summed up.

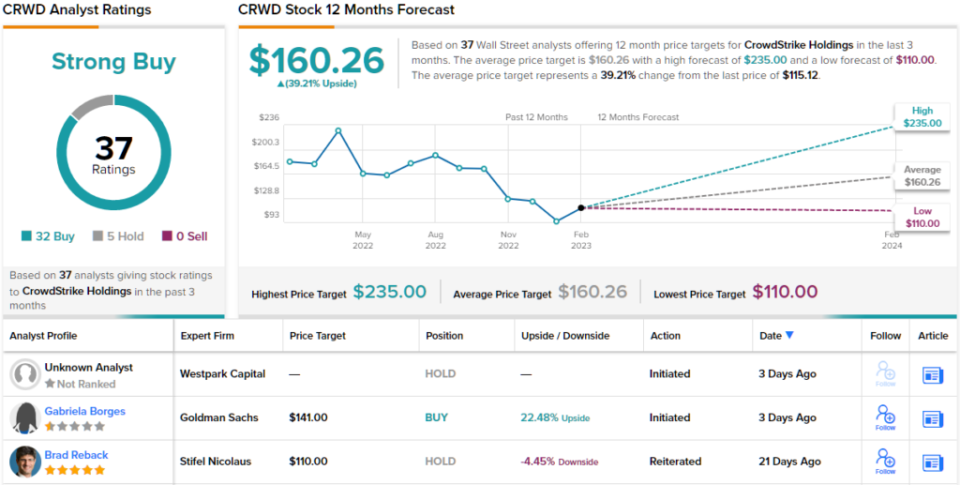
Over-all, Borges believes this is a inventory worthy of keeping on to. The analyst premiums CRWD shares a Acquire, and her $141 value focus on implies a 22{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1} upside in the next 12 months. (To view Borges’ monitor file, click on listed here)

Entirely, CrowdStrike has 37 recent analyst evaluations on file – these include things like 32 Purchases and just 5 Holds, for a Robust Buy consensus ranking. The shares are promoting for $115.12 and the common price tag concentrate on, now at $160.26, implies a 39{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1} a person-calendar year attain. (See CRWD stock forecast)

Palo Alto Networks (PANW)

The following stock on Goldman’s radar is Palo Alto Networks, another important title in electronic security. This company’s combination of firewall products and solutions and state-of-the-artwork cybertech gives consumers a substantial degree of protection for on-line techniques, such as defense versus malware assaults, and also allows automation of network and on the internet stability functions. Palo Alto also will make its enterprise-grade stability computer software accessible to residence and smaller small business end users looking to guard their network and cloud programs.

Over the past couple several years, Palo Alto has constructed a steadily expanding income stream based mostly on its merchandise line and marketplace-primary reputation. In the final claimed quarter, for fiscal 1Q23, the enterprise described $1.56 billion at the best line, dependent on $175 billion in whole billings. These figures represented yr-more than-12 months will increase of 25{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1} and 27{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1} respectively. The company’s backlog, a key indicator of foreseeable future operate and revenues stood at $8.3 billion as of Oct 31 last 12 months.

At the bottom line, Palo Alto posted an adjusted 83 cents per share, beating estimates of 69 cents per share. The firm finished its fiscal first quarter with a $1.2 billion in free of charge income movement, and almost $2.1 billion in funds on hand. We’ll see up coming 7 days, when Palo Alto stories earnings for fiscal Q2, how its performance is holding up.

In the meantime, Goldman’s Borges sees a distinct route ahead for the organization, and lays it out in effortless prose: “We watch Palo Alto as a portfolio of network, endpoint and cloud products at various phases of products maturity, each and every leveraging centralized domain knowledge in consumer interface/user encounter (UIUX), promoting, safety intelligence and machine mastering. Together with a thriving M&A strategy, we expect to see sturdy expansion of ~20{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1} for the subsequent 5 decades with best quartile software package KPIs, a route to GAAP profitability this calendar year, and energetic money allocation.”

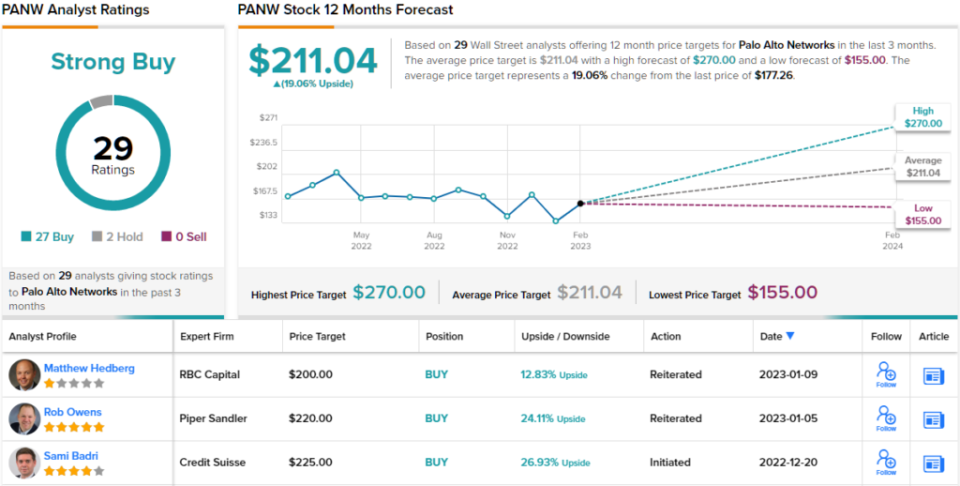
Tracking forward from below, Borges presents PANW shares a Get ranking, with a $205 just one-calendar year price focus on that implies a probable attain of 19{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1}.

The Solid Obtain consensus rating on this inventory demonstrates that the Road is clearly in-line with Goldman’s bullish look at of the 29 new analyst testimonials, 27 are to Obtain and only 2 to Hold. PANW shares have an typical price tag goal of $211.04, implying a 19{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1} upside from the trading price tag of $172.02. (See PANW stock forecast)

To discover superior ideas for stocks investing at interesting valuations, check out TipRanks’ Finest Shares to Purchase, a device that unites all of TipRanks’ equity insights.

Disclaimer: The opinions expressed in this post are solely those of the featured analysts. The articles is supposed to be used for informational functions only. It is really crucial to do your very own investigation before making any investment.

Critical RCE Vulnerability Discovered in ClamAV Open-Source Antivirus Software

Critical RCE Vulnerability Discovered in ClamAV Open-Source Antivirus Software

Feb 17, 2023Ravie LakshmananSysadmin / Endpoint Safety

Critical RCE Vulnerability Discovered in ClamAV Open-Source Antivirus Software

Cisco has rolled out protection updates to tackle a important flaw claimed in the ClamAV open up supply antivirus engine that could lead to distant code execution on prone units.

Tracked as CVE-2023-20032 (CVSS score: 9.8), the challenge relates to a case of distant code execution residing in the HFS+ file parser element.

The flaw impacts versions 1.. and previously, .105.1 and earlier, and .103.7 and previously. Google security engineer Simon Scannell has been credited with exploring and reporting the bug.

“This vulnerability is owing to a lacking buffer size verify that may well consequence in a heap buffer overflow write,” Cisco Talos stated in an advisory. “An attacker could exploit this vulnerability by publishing a crafted HFS+ partition file to be scanned by ClamAV on an impacted system.”

Prosperous exploitation of the weak point could empower an adversary to run arbitrary code with the exact same privileges as that of the ClamAV scanning process, or crash the method, ensuing in a denial-of-service (DoS) situation.

The networking tools reported the following items are susceptible –

  • Protected Endpoint, formerly Innovative Malware Security (AMP) for Endpoints (Home windows, macOS, and Linux)
  • Secure Endpoint Non-public Cloud, and
  • Secure Web Equipment, previously World wide web Stability Equipment

It more verified that the vulnerability does not effects Protected Electronic mail Gateway (previously E mail Security Equipment) and Safe Electronic mail and Web Manager (formerly Protection Administration Equipment) goods.

Also patched by Cisco is a distant data leak vulnerability in ClamAV’s DMG file parser (CVE-2023-20052, CVSS rating: 5.3) that could be exploited by an unauthenticated, remote attacker.

“This vulnerability is because of to enabling XML entity substitution that may perhaps outcome in XML external entity injection,” Cisco observed. “An attacker could exploit this vulnerability by distributing a crafted DMG file to be scanned by ClamAV on an influenced system.”

It really is truly worth pointing out that CVE-2023-20052 does not impact Cisco Safe Website Equipment. That mentioned, each vulnerabilities have been dealt with in ClamAV variations .103.8, .105.2, and 1..1.

Cisco independently also settled a denial-of-support (DoS) vulnerability impacting Cisco Nexus Dashboard (CVE-2023-20014, CVSS rating: 7.5) and two other privilege escalation and command injection flaws in E-mail Protection Equipment (ESA) and Secure E mail and Web Manager (CVE-2023-20009 and CVE-2023-20075, CVSS scores: 6.5).

Found this posting appealing? Follow us on Twitter and LinkedIn to browse much more exceptional content material we publish.

We’re starting a position in a cybersecurity stock that’s been in our Bullpen watch list

We’re starting a position in a cybersecurity stock that’s been in our Bullpen watch list

Sakorn Sukkasemsakorn | Istock | Getty Images

We’re initiating a position in Palo Alto Networks (PANW), buying 125 shares at roughly $175 each. Following Wednesday’s trade, Jim Cramer’s Charitable Trust will own 125 shares of PANW, starting its weighting in the portfolio at about 0.73{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1}.

We’re calling up this leader in cybersecurity from the bullpen. We originally added PANW to our “stocks in waiting list,” which we call our Bullpen, last August around $167 per share. Since then, shares of Palo Alto Networks have gained roughly 4{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1} compared to the S&P 500‘s decline of about 1{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1}.

Much like the broader market, PANW went through a nasty decline back in December and has since rallied nicely so far in 2023. But even after this year’s gains, shares are still down from the $180s in late August and the low $200s it reached last April. We think the stock can return to those prior highs in time. 

With earnings on the horizon, we are intentionally starting our PANW position on the smaller side. The company is scheduled to report earnings this coming Tuesday after the closing bell on Wall Street. This buy isn’t a call on the upcoming quarter — but if the stock were to fall for any reason that did not change our positive long-term view, we would greet weakness as an opportunity to bulk up our stake.

Stock Chart IconStock chart icon

hide content

Palo Alto Networks (PANW) 1-year performance

We’re starting a position in Palo Alto Networks because of its leadership in cybersecurity. Earlier this week, Goldman Sachs published a research initiation note on cybersecurity companies. The analysts, who rated Palo Alto with a buy, said they expect “secular tailwinds in security to drive budget growth ahead of broader information technology (IT) spending and broader software over the next decade.” Goldman believes security will continue to take share of total IT and software budgets for three reasons:

  • Security consistently screens as the first priority for investment in Goldman’s bi-annual survey of chief investment officers.
  • Companies need to continue to invest in leading-edge technology to defend against threats.
  • The evolving threat landscape has grown increasingly complex as more companies increase digital transformation projects.

Under this favorable backdrop of spending and Palo Alto Networks’ leading multi-platform approach, Goldman believes the company is positioned for “durable growth” of around 20{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1} for the next five years.

“We believe Palo Alto Networks is furthest along in the industry with executing a multi-platform strategy with technology leadership across several product vectors. Today, we view Palo Alto as a portfolio of network, endpoint and cloud products at different stages of product maturity, each leveraging centralized domain expertise in user interface/user experience (UIUX), marketing, security intelligence and machine learning.”

Cybersecurity isn’t completely immune to the weaker macro environment, but it should be one of — if not the — most resilient areas of enterprise spending. On the previous earnings call, management flagged how deals are starting to face more scrutiny and are taking longer to close. But on a more positive note, Palo Alto said it’s experiencing few deal cancelations. We do not think that changes no matter how tough things get in the economy.

If a threat were to arise, causing disruptions to your business, you don’t want to be the one that left the company vulnerable because you cut back spending on cyber.

Palo Alto Networks is also one of a handful of tech companies that has successfully made the pivot towards emphasizing profitability in this evolving macro environment. Management is doing an excellent job accelerating its efforts to drive incremental operating leverage. They have previously committed to 50 to 100 basis points of operating margin expansion and 100 to 150 basis points of adjusted cash flow margin expansion from fiscal 2022 through 2024.

There also could be a special catalyst on the horizon that could reward shareholders. Thanks to management’s push for profitability, Palo Alto Networks has delivered two consecutive quarters of GAAP (generally accepted accounting principles) profitability. If the next two quarters are also profitable, the company will meet all the requirements to be added to the S&P 500 index. We bring this up because a stock tends to jump when it gets included in the index due to the demand that is created by the mutual funds and exchange-traded funds (ETF) that are forced to buy the stock to keep their track to the index

To be clear, just because a company reports GAAP profits for four consecutive quarters it doesn’t guarantee a spot in the S&P 500. We would never recommend buying a stock solely on this basis. We buy stocks for fundamental reasons. However, the addition of Palo Alto to the index would be a nice bonus for shareholders based on the history of other stocks popping in reaction to the news.

We’re initiating our PANW position with a price target of $200 per share, about 15{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1} higher than current levels, representing roughly 49.5-times fiscal year 2024 earnings-per-share consensus estimates. The knock on PANW is obviously that it is an expensive stock on earnings. But if the company continues to handily beat expectations, then the stock will prove to be much a much better value than what it has appeared. Additionally, as the leader in cybersecurity, it’s consistent 20{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1} grow is more defensible than other areas of tech, which are experiencing problems from economic weakness.

(Jim Cramer’s Charitable Trust is long PAWN. See here for a full list of the stocks.)

As a subscriber to the CNBC Investing Club with Jim Cramer, you will receive a trade alert before Jim makes a trade. Jim waits 45 minutes after sending a trade alert before buying or selling a stock in his charitable trust’s portfolio. If Jim has talked about a stock on CNBC TV, he waits 72 hours after issuing the trade alert before executing the trade.

THE ABOVE INVESTING CLUB INFORMATION IS SUBJECT TO OUR TERMS AND CONDITIONS AND PRIVACY POLICY, TOGETHER WITH OUR DISCLAIMER.  NO FIDUCIARY OBLIGATION OR DUTY EXISTS, OR IS CREATED, BY VIRTUE OF YOUR RECEIPT OF ANY INFORMATION PROVIDED IN CONNECTION WITH THE INVESTING CLUB.  NO SPECIFIC OUTCOME OR PROFIT IS GUARANTEED.

Majority of Firms Make Cybersecurity Decisions Without Attacker Insight

Majority of Firms Make Cybersecurity Decisions Without Attacker Insight

Four out of 5 (79{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1}) businesses make most cybersecurity decisions devoid of insights into the menace actor targeting their infrastructures.

The claims appear from Google-owned threat analytics corporation Mandiant, which has also mentioned that when 67{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1} of cybersecurity choice makers imagine senior leadership groups however underestimate cyber-threats, 68{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1} agree their business requires to strengthen its knowing of the danger landscape.

The data in Mandiant’s International Views on Menace Intelligence report even more implies an just about consensus (96{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1}) between respondents who were happy with the excellent of danger intelligence their corporation employs.

At the exact same time, pretty much half of them (47{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1}) have admitted that proficiently making use of that intelligence in the course of the protection group was one of their most sizeable challenges, and nearly all (98{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1}) said they need to have to be a lot quicker at implementing variations to their cybersecurity tactic based mostly on accessible danger intelligence.

“Stability groups are outwardly self-confident but typically battle to preserve speed with the rapidly switching risk landscape. They crave actionable details that can be used all over their corporation,” stated Sandra Joyce, vice president of Mandiant Intelligence at Google Cloud.

“Security groups are worried that senior leaders do not fully grasp the nature of the threat. This means that significant cybersecurity conclusions are being built devoid of insights into the adversary and their techniques.”

In phrases of what threats groups felt most confident in tackling, financially motivated crime like ransomware was at the prime of the listing (91{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1}), adopted by hacktivist threats (89{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1}) and country-state actors (83{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1}).

The most up-to-date Mandiant report was compiled immediately after a worldwide survey of 1350 cybersecurity decision makers across 13 nations around the world and 18 sectors.

“This research signifies that one particular of the largest boundaries to setting up more robust defenses is the sheer quantity of facts: businesses ought to obtain much better procedures for placing intelligence into motion to get back substantially-wanted concentrate and identify distinct priorities,” described Jamie Collier, Mandiant senior menace intelligence advisor of EMEA at Google Cloud.

“British isles companies will need to place by themselves on the entrance foot, and that can only be realized by understanding your adversaries, utilizing changes at velocity, and making certain cyber-pitfalls are communicated properly amongst all stakeholders.”

A individual report by BlackBerry security researchers has revealed that several stability leaders are also fearful about ChatGPT, expecting the AI product to entire a productive cyber-attack in just a yr.