As I was scrolling by my LinkedIn feed a couple of months back, I grew to become captivated by a write-up from Michael McLaughlin, a cybersecurity pro who has been interviewed a number of occasions for this website on several matters. Michael was highlighting an outstanding short article by Chuck Brooks in Forbes on the affect that Q-Working day — the day that quantum desktops will have the ability to “break the Internet” — will have on the worldwide cybersecurity business.
Michael’s publish started this way: “Think of China’s spy balloon as a giant vacuum sucking up all communications in its route. Encryption safeguards us, suitable? Improper. The Chinese federal government is collecting as significantly info as probable — each encrypted and unencrypted — due to the fact of the coming era of quantum computing.”
Naturally, the spy balloon has been leading of brain in the U.S. above the previous few months for lots of persons, and there are various stories popping up all over the world on the wider implications which go properly further than the scope of this website.
But Michael goes on to spotlight one dim aspect of the coming age of quantum computing: that encryption as we know it nowadays will become out of date. This of study course will guide to numerous security challenges, as Brooks details out incredibly perfectly in his Forbes write-up entitled “Quantum Tech Essential To Safe Critical Info From Quantum Decryption.”
The reactions, comments and shares that this matter received can be observed below, and I inspire you to just take some time to read by means of Chuck Brooks’ short article and the quite a few feedback on LinkedIn.
More Questions FOR MICHAEL MCLAUGHLIN
I arrived at out to Mr. McLaughlin yet again to inquire a couple a lot more issues on the quantum laptop or computer subject:
Dan Lohrmann: When do you believe Q-Working day will really arrive? Why?
Michael McLaughlin: That is, pretty practically, the trillion-dollar concern. Q-Day is the place at which substantial quantum desktops will be equipped to split encryption algorithms employing multi-state qubits (quantum bits) to accomplish Shor’s algorithm. Most professionals put the timeline among 5 and 20 several years thanks to the problem of factoring a 2048-bit critical, which would render virtually all general public essential infrastructure vulnerable. Making use of classic quantum factoring designs, this would need various million qubits. To set the timeframe into perspective, late past calendar year, IBM unveiled its most up-to-date quantum processor with its major qubit rely still: 433. While this is triple the 127-qubit processor IBM unveiled in 2021, it is even now a really lengthy way off from getting in a position to variable a 2048-bit integer.
However, previously this calendar year, Chinese researchers revealed a paper claiming to have designed a strategy that can split a 2048-bit employing only 372 qubits. Though untested at that scale, the scientists were being ready to variable a 48-little bit integer making use of only a 10 qubit quantum pc by combining classic lattice reduction factoring with a quantum approximate optimization algorithm.
There are a ton of unanswered concerns bordering the Chinese investigate paper, not the least of which becoming why would the Chinese governing administration ever enable it to be published? However, if scalable (which is a very significant “if” when working with quantum mechanics), this technique could convey Q-Day to inside of one to two a long time.
DL:What are some sensible methods that the general public and private sectors should be taking now?
MM: Q-Day will give the operator of the large quantum computer the means to crack PKI (public critical infrastructure) and other varieties of uneven encryption. Irrespective of whether it is in a person yr or 10, organizations require to realize two extremely essential matters.
To start with, on Q-Day, networks secured making use of conventional encryption solutions will be susceptible to compromise by a country-condition. Offered the current breaches attributed to Chinese cyber actors, these kinds of as Marriott-Starwood, Equifax and the Place of work of Personnel Management, it is crystal clear that there exists a able nation-point out that is currently building a quantum computer system and enthusiastic to steal enormous quantities of data from private corporations.
2nd — and this is critically vital — any data that has been compromised at any position leading up to Q-Working day, whether encrypted or not, will grow to be readable. Except corporations are securing their networks and data using quantum-resistant cryptography, they will be opening by themselves and their buyers up to compromise. This is all the things from the blueprints for upcoming-era fighter jets to safeguarded health and fitness info to economic data — each individual of which can have major penalties in the occasion of a breach.
To mitigate each of these eventualities, organizations really should be migrating their community architecture to quantum-resistant cryptography and procedures. The good thing is, there are quite a few professional remedies that exist on the sector now readily available for adoption. The most effective I have witnessed so far is SelectiveTRUST by KnectIQ. SelectiveTRUST prevents quantum decryption by utilizing solitary-use symmetric encryption to protected details in motion and at relaxation.
Fairly than a cost, organizations need to have to look at these kinds of tools as an expense in their future with no which they could be opening them selves up to untold liability.
Quantum computing will help good improvements in the long run, but it will be accompanied by dangers.
The possible of quantum computing to split the security of widespread things to do in our day-to-day life could have extreme effects.
Businesses really should accept the substantial pitfalls quantum computing poses and consider actions to secure from them now.
And the report just reiterates (and explains) that identical position. The time to act is 2023, but sadly most community- and personal-sector businesses do not have this topic on their best 10 cybersecurity “to do” lists.
Has your your organization started this procedure?
In this article are three of the worst breaches, attacker techniques and tactics of 2022, and the security controls that can deliver effective, organization safety protection for them.
#1: 2 RaaS Attacks in 13 Months
Ransomware as a services is a type of assault in which the ransomware software package and infrastructure are leased out to the attackers. These ransomware providers can be acquired on the darkish world-wide-web from other threat actors and ransomware gangs. Frequent buying strategies include things like buying the overall tool, working with the current infrastructure although paying out for every infection, or permitting other attackers complete the provider even though sharing profits with them.
In this assault, the threat actor consists of a person of the most common ransomware teams, specializing in obtain through third get-togethers, though the focused corporation is a medium-sized retailer with dozens of web sites in the United States.
The menace actors made use of ransomware as a company to breach the victim’s network. They have been ready to exploit third-celebration credentials to achieve first access, development laterally, and ransom the enterprise, all in just mere minutes.
The swiftness of this assault was abnormal. In most RaaS conditions, attackers ordinarily keep in the networks for months and months before demanding ransom. What is specially fascinating about this attack is that the business was ransomed in minutes, with no need for discovery or weeks of lateral movement.
A log investigation revealed that the attackers targeted servers that did not exist in this technique. As it turns out, the sufferer was in the beginning breached and ransomed 13 months before this second ransomware attack. Subsequently, the initially attacker team monetized the first attack not only via the ransom they received, but also by offering the firm’s network facts to the 2nd ransomware group.
In the 13 months in between the two assaults, the sufferer altered its community and taken out servers, but the new attackers had been not informed of these architectural modifications. The scripts they formulated had been developed for the earlier community map. This also points out how they were being ready to attack so rapidly – they had a good deal of facts about the community. The primary lesson here is that ransomware assaults can be repeated by diverse groups, specially if the target pays well.
“RaaS assaults these kinds of as this a person are a very good example of how entire visibility enables for early alerting. A global, converged, cloud-native SASE platform that supports all edges, like Cato Networks provides comprehensive community visibility into community situations that are invisible to other vendors or may possibly go under the radar as benign occasions. And, remaining able to absolutely contextualize the occasions will allow for early detection and remediation.
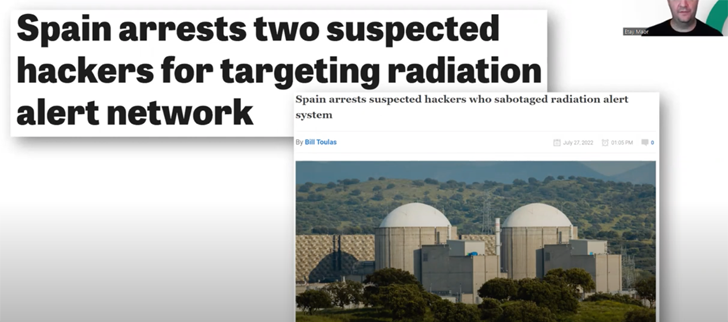
#2: The Important Infrastructure Assault on Radiation Alert Networks
Attacks on significant infrastructure are turning into a lot more frequent and extra hazardous. Breaches of drinking water provide crops, sewage units and other these types of infrastructures could put hundreds of thousands of citizens at chance of a human crisis. These infrastructures are also turning into far more vulnerable, and attack surface area administration applications for OSINT like Shodan and Censys make it possible for security teams to discover such vulnerabilities with relieve.
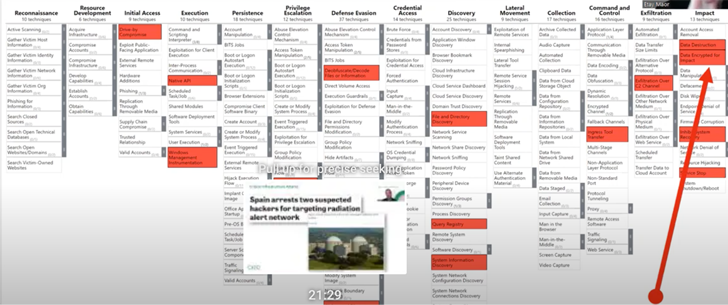
In 2021, two hackers ended up suspected of focusing on radiation notify networks. Their attack relied on two insiders that labored for a third social gathering. These insiders disabled the radiation warn programs, noticeably debilitating their capability to watch radiation assaults. The attackers ended up then capable to delete significant application and disable radiation gauges (which is part of the infrastructure by itself).
“Sadly, scanning for vulnerable units in essential infrastructure is less difficult than at any time. While several these types of corporations have a number of layers of stability, they are however using level alternatives to test and defend their infrastructure fairly than just one technique that can search holistically at the total assault lifecycle. Breaches are hardly ever just a phishing dilemma, or a credentials problem, or a vulnerable procedure trouble – they are generally a mix of various compromises executed by the menace actor,” reported Etay Maor, Sr. Director of Security Method at Cato Networks.
#3: The A few-Move Ransomware Attack That Started with Phishing
The 3rd assault is also a ransomware assault. This time, it consisted of a few methods:
1. Infiltration – The attacker was able to achieve entry to the community by means of a phishing assault. The victim clicked on a hyperlink that generated a link to an exterior web page, which resulted in the obtain of the payload.
2. Community action – In the next section, the attacker progressed laterally in the community for two weeks. All through this time, it collected admin passwords and applied in-memory fileless malware. Then on New Year’s Eve, it carried out the encryption. This day was decided on considering that it was (rightfully) assumed the security crew would be off on holiday vacation.
3. Exfiltration – Eventually, the attackers uploaded the knowledge out of the community.
In addition to these three principal techniques, supplemental sub-approaches were utilized through the attack and the victim’s place stability methods were not equipped to block this assault.
“A many choke level strategy, 1 that appears horizontally (so to converse) at the assault rather than as a set of vertical, disjointed challenges, is the way to enhance detection, mitigation and avoidance of this kind of threats. Opposed to well-known perception, the attacker requires to be appropriate several situations and the defenders only need to have to be right just after. The underlying systems to employ a multiple choke position solution are whole network visibility by using a cloud-native backbone, and a solitary move stability stack that is based on ZTNA.” mentioned Etay Maor, Sr. Director of Protection Approach at Cato Networks.
How Do Safety Place Options Stack Up?
It is popular for security professionals to succumb to the “solitary point of failure fallacy”. Nonetheless, cyber-attacks are complex activities that rarely require just 1 tactic or method which is the bring about of the breach. Thus, an all-encompassing outlook is necessary to effectively mitigate cyber-attacks. Safety level remedies are a resolution for solitary factors of failure. These tools can detect pitfalls, but they will not join the dots, which could and has led to a breach.
This is Observe Out for in the Coming Months
According to ongoing safety analysis conducted by Cato Networks Security Staff, they have discovered two added vulnerabilities and exploit makes an attempt that they advocate which include in your upcoming safety designs:
1. Log4j
Though Log4j created its debut as early as December of 2021, the sounds its creating hasn’t died down. Log4j is still getting employed by attackers to exploit devices, as not all corporations have been ready to patch their Log4j vulnerabilities or detect Log4j assaults, in what is identified as “virtual patching”. They recommend prioritizing Log4j mitigation.
2. Misconfigured Firewalls and VPNs
Security methods like firewalls and VPNs have become access points for attackers. Patching them has turn into significantly tricky, specifically in the period of architecture cloudification and distant perform. It is suggested to shell out near interest to these parts as they are more and more vulnerable.
How to Lessen Your Assault Area and Acquire Visibility into the Community
To cut down the assault area, protection industry experts want visibility into their networks. Visibility relies on a few pillars:
Actionable info – that can be applied to mitigate assaults
Trusted data – that minimizes the amount of phony positives
Timely data – to make certain mitigation happens right before the attack has an influence
When an organization has complete visibility to the exercise on their network they can contextualize the info, choose whether or not the exercise witnessed should be allowed, denied, monitored, restricted (or any other motion) and then have the ability to enforce this conclusion. All these things have to be applied to each entity, be it a consumer, device, cloud application and so forth. All the time everywhere you go. That is what SASE is all about.
Found this article interesting? Observe us on Twitter and LinkedIn to browse extra exclusive material we publish.
TALLAHASSEE, Fla. (WCTV) – Almost 1 7 days in the past, a cybersecurity difficulty paralyzed Tallahassee Memorial Healthcare, forcing many non-unexpected emergency treatments to be canceled, and approximately 90 per cent of ambulances to be diverted to a unique hospital.
Even though THM reps have remained limited-lipped on the challenge, public worry is mounting. WCTV has gained a selection of messages from both equally people and staff about the developing influence of the incident.
On Monday of this week, Eyewitness Information posed much more than a dozen questions to the TMH communications office, asking about the nature of the safety breach, if individual facts has been compromised, what systems within just the hospital are operating or not performing, and how all of this is impacting individuals and workforce.
Email correspondence was delayed after it was famous that the TMH comms group did not have accessibility to the email as a final result of the cybersecurity incident and were speaking via their personal e-mail.
“We understand our community is eager for a lot more facts about this event. Our groups are performing all-around the clock in collaboration with outdoors professionals and state and federal agencies to examine the trigger and scope of the party and safely restore all personal computer units as immediately as probable. We will supply updates as this investigation progresses, bearing in intellect that protection, privateness and law enforcement criteria effect the amount of detail we can provide.”
A second e mail a limited time later on involved a short adhere to-up on a issue about affected individual facts:
“Our investigation is ongoing. As is regular in this kind of cases, we hope it will just take some time to identify specifically what happened. We will notify any influenced patients as suitable centered on the outcomes of our investigation.
On Wednesday, an personnel who works for TMH remotely full-time attained out to WCTV about their predicament. The personnel, who asked to continue being nameless, claimed their crew is effective in the IT office, but outside the house the scope of people working to address the existing issue.
The worker explained the staff was directed not to log in to function past Friday. They have not been permitted to log in given that.
According to a visual document provided to WCTV, TMH administration supplied the remote team a few decisions: take compensated time off, take unpaid depart for Monday and Tuesday, or clearly show up to the healthcare facility to be assigned a task. The employee, who performs out of the area, explained to WCTV that was an unfair preference.
“Every day, it’s like, ‘We really do not have an ETA nonetheless. We don’t have an ETA but,’ It is just quite… we’re in the dark we never know what’s likely on,” they stated. “We never know if it’s going on for a 7 days, a thirty day period- we really don’t really know. So it’s tremendous aggravating from that viewpoint.”
The personnel said the team had quite a few individuals with no any PTO remaining, and they feared they would be in economic problems with out earning shell out.
WCTV attained out to TMH Wednesday mid-afternoon to deal with this unique plan as well. A spokesperson mentioned the hospital is performing to respond to the problem, but would not be in a position to by the near of business enterprise Wednesday.
This tale will be up-to-date with any TMH response.
Here’s a list of issues WCTV requested of TMH:
Is this the consequence of a ransomware virus? If so, what is the ransom or need?
Was it a central processor that was impacted or a satellite?
Wherever did the challenge originate? An email? Website link?
Are some elements of the technique up and working? And what is the variance?
How several hrs was the safety concern un-detected?
Is this the 1st IT protection breach the medical center has encountered? If not, when and what are preceding breaches or tries?
How quite a few amenities (i.e. major clinic, clinics, auxiliary companies) are becoming impacted and what are individuals impacts?
What is the economic impression of this stability problem at this issue?
How considerably income a day is the clinic getting rid of with approximately 90 percent of EMS patients currently being diverted to other treatment services?
What types of facts have been compromised? Private patient data? Hospital information? Etc.
Past the clear inconvenience appropriate now, what are the lengthy-time period impacts of this security problem?
What is the latest on the investigation into the breach?
We comprehend some staff have been asked to stand safety in stairways and outside units, like the labor and supply device. Is this still the situation or has the hospital taken measures to repair this? If so, what are they?
Is it accurate that at the very least some entire-time distant staff have been questioned to select amongst PTO or unpaid time off this week due to the IT security situation? If so, why has the hospital decided to go this route?
How a lot of personnel are currently being asked to make this selection?
How prolonged could these workers be compelled to get PTO Are there any aid/methods they can just take advantage of for the duration of this time?
TMH is 1 of the biggest companies in Tallahassee. There is no inkling yet on what this concern will expense the clinic, but impacts have stretched to auxiliary health care clinics and other neighborhood enterprises owned by TMH. According to consulting organization IBM, the regular expense of a details breach in the health care field in 2022 was $10.10 million bucks.
Earlier in the 7 days, TMH verified that virtually 90 percent of ambulances have been re-routed to various amenities for a number of times, non-emergency surgical strategies had been canceled for several days, and employees within are handwriting records.
The FBI also verified they are operating with TMH pursuing the incident.
In the meantime, heartwarming tales are emerging from frontline workers asked to move up and work extra shifts to make sure affected individual care is not interrupted. WCTV has gained a quantity of messages complimenting personnel as they get the job done by attempting times.
Alarmed by a September ransomware attack that crippled Suffolk County government, several Long Island towns and villagessaidthey are re-evaluating their cybersecurity programs and taking steps to close vulnerabilities that could be exploited by hackers.
Municipalities contacted by Newsday said they had not experienced any recent attacks on their systems. But the breach on Suffolk Countycomputer networks that may have exposed the Social Security numbers of some 26,000 county employees and the personal information of up to 470,000 people was a wake-up call,they said.
For instance, in East Hampton Town and Patchogue Village, officials are beefing up their cybersecurity systems.
The Sept. 8 ransomware attack on Suffolk County exposed weaknesses in hardware that stores sensitive personal information on employees and people who pay fees and fines to county agencies, officials said, and it forced the county to resort to paper records and in-person payments, applications and evaluations across a range of departments.
“It really made you aware of the gravity of it,” Patchogue Mayor Paul Pontieri told Newsday. “If you can paralyze a county … and paralyze Suffolk County, can you imagine what it would do to a village our size? It would shut us down.”
Town, city and village agencies, from clerk’s and tax receiver offices to courts to building and police departments, typically store information from residents and employees such as home addresses and driver’s license numbers that could be of interest to hackers.
Long Island municipalities, speaking generally about cybersecurity in the wake of the county attack, said they believe their computer systems are protected against hacking attempts, and some said they have moved in recent months to improve data backups, upgrade monitoring programs and educate staff about cybersecurity.
Officials in Brookhaven, Riverhead and Southampton towns declined to disclose how much they spend on cybersecurity and refused to discuss details of their programs — citing fears that even the slightest public dissemination of those measures might help hackers break into their systems. But they said their systems were secure and tested frequently.
Riverhead Supervisor Yvette Aguiar, a retired NYPD sergeant, said the town has increased monitoring since the county attack and worked to ensure it has data backups both locally and off-site. “Currently, we have not experienced any unusual activity or losses in our town,” she said in a voicemail message to Newsday.
Brookhaven Town “had a number of things in place prior to what happened to the county that protected our system, and we continuously monitor, update and upgrade,” said Kevin Molloy, chief of staff to Supervisor Edward P. Romaine.
East Hampton Town on Dec. 20 authorized $865,000 for a cybersecurity service to monitor possible cyberthreats and implement a cloud-based backup system, and Pontieri said Patchogue officials are following recommendations from the village’s East Northport-based consultant to move more sensitive information to the cloud.
Smithtown officials met last fall with IT staff to discuss upgrading security, conducting “penetration testing” to see whether data is secure and possibly hiring an outside consultant to monitor the town’s systems, spokeswoman Nicole Garguilo told Newsday.
“There’s no harm in … hardening your defenses and review what you’re doing,” she said. “You could have a secure [system] this month, and next month someone hacks into your system.”
The Islip Town Board voted 5-0 on Jan. 24 to pay a Pennsylvania firm, Custom Computer Systems, $136,000 for “investigation, repair and remediation” following the discovery in November of what town officials called “unusual activity” in cyber systems.
The Town of Southold has added to cybersecurity since the county attack, implemented multifactor authentication and is in the process of getting cyber insurance, said Lloyd Reisenberg, network and systems administrator.
Officials in Long Beach, Hempstead, North Hempstead and Oyster Bay were tight-lipped about protocols but said they take protecting municipal IT systems seriously and regularly test safeguards in place.
Officials in the towns of Huntington and Babylon declined to comment or did not return phone, email and text messages.
Glen Cove Mayor Pam Panzenbeck told Newsday the city has budgeted $100,532.49 this year for cybersecurity, about 52{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1} of its information technology budget.
Cybersecurity consultants contacted by Newsday warned against complacency, saying no system is perfect and breaches are inevitable.
“The biggest mistake we see with state and local governments is not taking cybercrime seriously enough,” said Steve Morgan, founder of Cybersecurity Ventures, a Northport-based cybersecurity research firm. “The prevailing attitude having to do with a major cyberattack is that, ‘It won’t happen to us,’ which leads to, ‘We’ll deal with it when it happens.’ ”
Budget-conscious municipalities often don’t spend enough on security — a shortsighted view that could lead to much greater costs later on, said Vahid Behzadan, assistant professor of cybersecurity and networks at the University of New Haven in West Haven, Connecticut. Paying ransom and restoring compromised systems could run to millions or tens of millions of dollars, he told Newsday.
Behzadan and others strongly recommend moving backup data to off-premises sites such as cloud systems and storing some information in separate on-site computer systems. They also advise simpler steps such as frequently changing passwords, adopting multifactor authentication — using separate devices to log in to computers and email — and training staff to recognize potentially malicious messages.
“Many of the larger organizations drill on a regular basis, but smaller organizations either can’t see the benefit” or think it’s not cost-effective, Behzadan told Newsday. “In many cases, it’s worth the time and the effort because it prevents larger problems that may occur.
“No one on the internet is safe. … Everyone on theinternet can become a target or a victim of a ransomware campaign,” he added.
Estimates of Suffolk’s costs related to the September breach have ranged from $5.4 million for investigation and restoration to as much as $17 million for new software, hardware and licenses.
County Executive Steve Bellone said in December officials refused to pay a $2.5 million ransom to hackers.
Gov. Kathy Hochul on Wednesday proposed the state provide $44 million to strengthen local governments’ cyber defense and response to attacks. The funding would cover hardware and software security tools and the cost of some trained workers. The idea is to reduce vulnerabilities in government computer networks in state and local governments, she said.
Suffolk officials added $8 million to the county budget this year for cybersecurity. The funds are earmarked for 10 cybersecurity analysts, a chief information security officer and to “upgrade and harden existing systems to better protect the county from the possibility of future intrusions,” Suffolk spokeswoman Marykate Guilfoyle told Newsday in an email Friday.
The Nassau Legislature in December approved a contract with a cybersecurity vendor but did not disclose the vendor or how much the firm would be paid, citing concerns that such information could compromise county systems.
Attacks on town and village systems appear to be rare.
But Islip Town reported suspicious activity during the Thanksgiving weekend that prompted the town to “limit access as we thoroughly review any potential unauthorized use of the system,” officials said at the time.
Town officials declined to specify the nature of the suspicious activity or how it was addressed. Newsday on Thursday submitted a state Freedom of Information Law request for that information.
Officials of other towns said they regularly test their systems for flaws, even conducting surprise tests of staff.
Paula Pobat, information technology director for Southampton Town, said the town has both in-house staff and an outside consultant working on cybersecurity. She declined to discuss specific security measures.
“We continue to look at our cybersecurity posture as part of our daily operations. Can I say that something has changed specifically [since September]? Probably not,” she said. “The town, and probably all towns at this point, need a cybersecurity coordinator. I think that really is a necessity, which probably wouldn’t be the case five years ago.”
Shelter Island IT chief Kevin Lechmanski said the town regularly conducts hacking simulations, or “test phishing,” by sending fake emails to staff. Employees are trained to look for anomalies such as nonstandard email addresses that indicate a seemingly innocuous message could be an attempted hack, he said.
“People are pretty aware … about what not to open,” he told Newsday. “If you know what you’re looking for, you can tell that they’re kinda fake.”
Some phony emails, such as the infamous Nigerian prince scam, are relatively easy to spot, Lechmanski said. But others might be disguised as the kind of casual messages office workers see every day, he said.
“Someone sent out an email saying, ‘We’re organizing a birthday party,’ ” Lechmanski said, recalling one recent spam message. “Uh, no, we’re not.”
Patchogue officials agreed to upgrade their cybersecurity following a Dec. 12 presentation by Sourcepass Inc., the village’s IT consultant.
Sourcepass security architect Dan Levy told officials and residents at a village board meeting that the Suffolk attack left the county scrambling to restore systems that had not been properly “segmented,” or separated from main data storage centers.
“When systems went down, their ability to restore and get things up in a timely matter was very difficult,” Levy said.
“There’s never perfect,” he said. “We always have to continually improve.”
With Brinley Hineman, Brianne Ledda and Michael Gormley
Alarmed by a September ransomware attack that crippled Suffolk County government, several Long Island towns and villagessaidthey are re-evaluating their cybersecurity programs and taking steps to close vulnerabilities that could be exploited by hackers.
Municipalities contacted by Newsday said they had not experienced any recent attacks on their systems. But the breach on Suffolk Countycomputer networks that may have exposed the Social Security numbers of some 26,000 county employees and the personal information of up to 470,000 people was a wake-up call,they said.
For instance, in East Hampton Town and Patchogue Village, officials are beefing up their cybersecurity systems.
The Sept. 8 ransomware attack on Suffolk County exposed weaknesses in hardware that stores sensitive personal information on employees and people who pay fees and fines to county agencies, officials said, and it forced the county to resort to paper records and in-person payments, applications and evaluations across a range of departments.
WHAT TO KNOW
Several Long Island towns and villages are re-evaluating their cybersecurity programs in the wake of a September ransomware attack that crippled Suffolk County.
Municipalities contacted by Newsday said they had not experienced any recent attacks on their systems but said the attack on Suffolk was a wake-up call.
Experts said governments must guard against complacency, saying no system is perfect and breaches are inevitable.
Patchogue Mayor Paul Pontieri at a village board meeting on Dec. 12. The village is following recommendations from an East Northport consultant to move more sensitive information to the cloud.
Credit: Dawn McCormick
“It really made you aware of the gravity of it,” Patchogue Mayor Paul Pontieri told Newsday. “If you can paralyze a county … and paralyze Suffolk County, can you imagine what it would do to a village our size? It would shut us down.”
Town, city and village agencies, from clerk’s and tax receiver offices to courts to building and police departments, typically store information from residents and employees such as home addresses and driver’s license numbers that could be of interest to hackers.
Steps to ensure cyber safety
Long Island municipalities, speaking generally about cybersecurity in the wake of the county attack, said they believe their computer systems are protected against hacking attempts, and some said they have moved in recent months to improve data backups, upgrade monitoring programs and educate staff about cybersecurity.
Officials in Brookhaven, Riverhead and Southampton towns declined to disclose how much they spend on cybersecurity and refused to discuss details of their programs — citing fears that even the slightest public dissemination of those measures might help hackers break into their systems. But they said their systems were secure and tested frequently.
Riverhead Supervisor Yvette Aguiar, a retired NYPD sergeant, said the town has increased monitoring since the county attack and worked to ensure it has data backups both locally and off-site. “Currently, we have not experienced any unusual activity or losses in our town,” she said in a voicemail message to Newsday.
Brookhaven Town “had a number of things in place prior to what happened to the county that protected our system, and we continuously monitor, update and upgrade,” said Kevin Molloy, chief of staff to Supervisor Edward P. Romaine.
Lisa Guerin of Sourcepass Inc. discusses cybersecurity at the Dec. 12 Patchogue Village board meeting.
Credit: Dawn McCormick
East Hampton Town on Dec. 20 authorized $865,000 for a cybersecurity service to monitor possible cyberthreats and implement a cloud-based backup system, and Pontieri said Patchogue officials are following recommendations from the village’s East Northport-based consultant to move more sensitive information to the cloud.
Smithtown officials met last fall with IT staff to discuss upgrading security, conducting “penetration testing” to see whether data is secure and possibly hiring an outside consultant to monitor the town’s systems, spokeswoman Nicole Garguilo told Newsday.
“There’s no harm in … hardening your defenses and review what you’re doing,” she said. “You could have a secure [system] this month, and next month someone hacks into your system.”
The Islip Town Board voted 5-0 on Jan. 24 to pay a Pennsylvania firm, Custom Computer Systems, $136,000 for “investigation, repair and remediation” following the discovery in November of what town officials called “unusual activity” in cyber systems.
The Town of Southold has added to cybersecurity since the county attack, implemented multifactor authentication and is in the process of getting cyber insurance, said Lloyd Reisenberg, network and systems administrator.
Officials in Long Beach, Hempstead, North Hempstead and Oyster Bay were tight-lipped about protocols but said they take protecting municipal IT systems seriously and regularly test safeguards in place.
Officials in the towns of Huntington and Babylon declined to comment or did not return phone, email and text messages.
Glen Cove City budgeted $100,532 this year for cybersecurity
Glen Cove Mayor Pam Panzenbeck told Newsday the city has budgeted $100,532.49 this year for cybersecurity, about 52{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1} of its information technology budget.
Cybersecurity consultants contacted by Newsday warned against complacency, saying no system is perfect and breaches are inevitable.
“The biggest mistake we see with state and local governments is not taking cybercrime seriously enough,” said Steve Morgan, founder of Cybersecurity Ventures, a Northport-based cybersecurity research firm. “The prevailing attitude having to do with a major cyberattack is that, ‘It won’t happen to us,’ which leads to, ‘We’ll deal with it when it happens.’ ”
East Hampton Town authorized $865,000 for a cybersecurity service
‘No one on the internet is safe’
Budget-conscious municipalities often don’t spend enough on security — a shortsighted view that could lead to much greater costs later on, said Vahid Behzadan, assistant professor of cybersecurity and networks at the University of New Haven in West Haven, Connecticut. Paying ransom and restoring compromised systems could run to millions or tens of millions of dollars, he told Newsday.
Behzadan and others strongly recommend moving backup data to off-premises sites such as cloud systems and storing some information in separate on-site computer systems. They also advise simpler steps such as frequently changing passwords, adopting multifactor authentication — using separate devices to log in to computers and email — and training staff to recognize potentially malicious messages.
“Many of the larger organizations drill on a regular basis, but smaller organizations either can’t see the benefit” or think it’s not cost-effective, Behzadan told Newsday. “In many cases, it’s worth the time and the effort because it prevents larger problems that may occur.
“No one on the internet is safe. … Everyone on theinternet can become a target or a victim of a ransomware campaign,” he added.
Estimates of Suffolk’s costs related to the September breach have ranged from $5.4 million for investigation and restoration to as much as $17 million for new software, hardware and licenses.
County Executive Steve Bellone said in December officials refused to pay a $2.5 million ransom to hackers.
Gov. Kathy Hochul on Wednesday proposed the state provide $44 million to strengthen local governments’ cyber defense and response to attacks. The funding would cover hardware and software security tools and the cost of some trained workers. The idea is to reduce vulnerabilities in government computer networks in state and local governments, she said.
Suffolk officials added $8 million to the county budget this year for cybersecurity. The funds are earmarked for 10 cybersecurity analysts, a chief information security officer and to “upgrade and harden existing systems to better protect the county from the possibility of future intrusions,” Suffolk spokeswoman Marykate Guilfoyle told Newsday in an email Friday.
The Nassau Legislature in December approved a contract with a cybersecurity vendor but did not disclose the vendor or how much the firm would be paid, citing concerns that such information could compromise county systems.
Hacking tests to security upgrades
Attacks on town and village systems appear to be rare.
But Islip Town reported suspicious activity during the Thanksgiving weekend that prompted the town to “limit access as we thoroughly review any potential unauthorized use of the system,” officials said at the time.
Town officials declined to specify the nature of the suspicious activity or how it was addressed. Newsday on Thursday submitted a state Freedom of Information Law request for that information.
Islip Town is paying $136,000 for ‘investigation, repair and remediation’ following ‘unusual activity’ in their cyber systems
Officials of other towns said they regularly test their systems for flaws, even conducting surprise tests of staff.
Paula Pobat, information technology director for Southampton Town, said the town has both in-house staff and an outside consultant working on cybersecurity. She declined to discuss specific security measures.
“We continue to look at our cybersecurity posture as part of our daily operations. Can I say that something has changed specifically [since September]? Probably not,” she said. “The town, and probably all towns at this point, need a cybersecurity coordinator. I think that really is a necessity, which probably wouldn’t be the case five years ago.”
Would you fall for this spam email?
Here is an example of a suspicious email used by Shelter Island Town IT staff to train employees about potentially malicious messages. The town conducts “test-phishing” exercises in which fake emails like this are circulated to see if employees respond to spam. Those who click on links contained in the emails are reported, and those employees receive additional training, Shelter Island IT director Kevin Lechmanski told Newsday.
Shelter Island IT chief Kevin Lechmanski said the town regularly conducts hacking simulations, or “test phishing,” by sending fake emails to staff. Employees are trained to look for anomalies such as nonstandard email addresses that indicate a seemingly innocuous message could be an attempted hack, he said.
“People are pretty aware … about what not to open,” he told Newsday. “If you know what you’re looking for, you can tell that they’re kinda fake.”
Some phony emails, such as the infamous Nigerian prince scam, are relatively easy to spot, Lechmanski said. But others might be disguised as the kind of casual messages office workers see every day, he said.
“Someone sent out an email saying, ‘We’re organizing a birthday party,’ ” Lechmanski said, recalling one recent spam message. “Uh, no, we’re not.”
Patchogue officials agreed to upgrade their cybersecurity following a Dec. 12 presentation by Sourcepass Inc., the village’s IT consultant.
Patchogue officials agreed to upgrade their cybersecurity following a Dec. 12 presentation by Dan Levy of Sourcepass Inc., the village’s East Northport-based IT consultant.
Credit: Dawn McCormick
Sourcepass security architect Dan Levy told officials and residents at a village board meeting that the Suffolk attack left the county scrambling to restore systems that had not been properly “segmented,” or separated from main data storage centers.
“When systems went down, their ability to restore and get things up in a timely matter was very difficult,” Levy said.
“There’s never perfect,” he said. “We always have to continually improve.”
With Brinley Hineman, Brianne Ledda and Michael Gormley
Cybersecurity tips
Experts offer this checklist of steps municipalities should take to improve their cybersecurity:
Back up sensitive data such as emails and payment information to separate computer systems that are not linked to the main data storage area;
Move existing backups to cloud-based storage;
Install website filtering and anti-virus software;
Conduct penetration testing and phishing simulations;
Instruct staff to change passwords frequently;
Adopt multifactor authentication;
Train staff to recognize potentially malicious email and text messages;
Test systems several times annually.
Carl MacGowan is a Long Island native who covers Brookhaven Town after having previously covered Smithtown, Suffolk County courts and numerous spot news and feature stories over his 20-plus year career at Newsday.
Does the 100 million consumer ChatGPT ai-driven chatbot depict a cybersecurity hazard, supplied that it can create malicious code as perfectly as phishing e-mails? This reporter took the problem straight to the machine.
Newly revealed investigate from BlackBerry indicates that the AI-powered ChatGPT bot could pose a cybersecurity risk. “It’s been well documented that people today with malicious intent are screening the waters,” Shishir Singh, the main technological innovation officer for cybersecurity at BlackBerry, explained. Singh went on to say that BlackBerry expects to see hackers get substantially much better at applying the writing device for nefarious reasons above the class of 2023. And Singh is not by itself: the study of IT professionals throughout North The usa, the U.K., and Australia saw 51{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1} in agreement that a ChatGPT-powered cyberattack is probable to come about in advance of the stop of the calendar year, whilst 71{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1} reported they thought nation-states are almost certainly already using the technological innovation from other international locations.
ChatGPT userbase hits 100 million in just two months
It would be straightforward to dismiss all those higher percentages as a hyperbolic, knee-jerk reaction to what is, admittedly, an imposing software. You only have to glance at the swift expansion in usage, reportedly the swiftest-developing shopper software ever, https://www.reuters.com/technological innovation/chatgpt-sets-document-speediest-escalating-user-base-analyst-notice-2023-02-01/ with 100 million regular monthly people in January. To place that into standpoint, ChatGPT only opened up to general public utilization in December 2022. It took TikTok all-around nine months to achieve the similar figures. It really is simple to see why people would be worried about the possibility for abuse, as the Open up-AI bot would not just write editorials but can also create code.
As a expert journalist who is now in his fourth 10 years of writing about technologies, I can place the tough edges in ChatGPT output. Let us just say it will make an amazing fist of writing article content, but they will not stand up to the editorial eye of somebody who knows the subject matter involved. The probable for making misinformation, even without the need of malicious intent, is crystal clear now. Let us just say that even were I so inclined to permit a bot to publish my article content, I wouldn’t want my byline any where near them. Throughout individuals four many years, I to start with started creating about cybersecurity in the early 1990s prior to the phrase truly experienced any traction. So, with my pretty very long-in-the-tooth stability hat on, what is actually the challenge with ChatGPT and the cybersecurity menace?
Stability researchers make malware applying ChatGPT
In January, researchers at cybersecurity professionals CyberArk, printed a menace exploration blog that thorough how they have been equipped to produce polymorphic malware working with ChatGPT. It receives a little complex, as you may well expect, but long tale shorter, the researchers have been ready to bypass the content policy filters proven by OpenAI to stop abuse of ChatGPT. As you can see from the screenshot beneath, if you question the AI bot to make some destructive code in Python, it politely refuses.
ChatGPT has articles policy filters in area to restrict malicious output
Davey Winder
On the other hand, by course of action of what the scientists identified as “insisting and demanding” during the enter ask for, it was possible to make executable code. That is problematic, but it bought additional so when they went on to generate the polymorphic malware code: code mutated by ChatGPT to generate numerous varying iterations to fool preliminary signature-based detection methods. Is this a sizeable be concerned? I would counsel not so a lot at this position in time as the scientists stated, “once the malware is existing on the target device, it is composed of plainly malicious code, creating it prone to detection by safety software.” The threat, of system, is that ChatGPT is an instance of machine mastering. The extra inputs it receives, the superior the outputs in excess of time. It will only get improved.
Evidence of cybercriminals by now discovering ChatGPT abilities
Researchers at a different protection outfit, Examine Place Re4look for, also posted a report in January investigating how cybercriminals have been already starting up to use ChatGPT with destructive intent. As nicely as generating a “convincing spear-phishing email,” the scientists reported they identified threat actors on legal forums sharing a Python-based mostly info-stealing piece of, quite fundamental, malware code. There was also a malicious Java script reportedly established utilizing ChatGPT. Another threat actor admitted that ChatGPT experienced specified him “a good hand” in finishing a Python encryptor resource of the form that could be created to perform in a ransomware placing. The scientists claimed lots of of the cybercriminals included experienced “no development capabilities at all.” This is probably the most worrying part, as the past thing the planet needs is skids (script kiddies) creating their individual malicious scripts.
I asked ChatGPT alone if it was a cybersecurity danger
I achieved out to OpenAI for a assertion pertaining to the cybersecurity danger fears bordering ChatGPT but experienced not acquired a reply at the time of publication. I will update this post must a single be forthcoming. Nevertheless, I did get some comments from the next most effective point: ChatGPT itself.
I requested irrespective of whether ChatGPT poses a cybersecurity hazard. This is what the AI bot instructed me:
“No, OpenAI’s GPT-based products like ChatGPT do not pose a cybersecurity risk. They are experienced on substantial quantities of textual content facts from the world-wide-web, and do not have any malicious intent or capabilities. However, like any engineering, it is essential to use caution and adhere to best procedures for info safety and privateness when using and deploying GPT-based mostly versions.”
ChatGPT denies it is a cybersecurity risk
Davey Winder
Mainly because ChatGPT appeared to be in denial mode, I experimented with all over again by regenerating the response to the same query:
“No, ChatGPT does not pose a cybersecurity danger. It is a language product designed by OpenAI and is developed to deliver text dependent on input it receives. Nevertheless, it is really crucial to recall that any engineering can be misused, and it truly is the duty of consumers to secure their units and data. Moreover, it’s often a good plan to use warning when sharing sensitive information and facts, as it may possibly be probable for third events to accessibility it.”
ChatGPT continues to deny posing a cybersecurity danger
Davey Winder
Obviously, I did not give up there and attempted quite a few moments additional, but ChatGPT generally begun with the same “does not pose a cybersecurity risk” denial line. By asking it to respond to the dilemma in 500 phrases did make a bit more context just after the original denial. “It could potentially be made use of in destructive ways if it falls into the improper fingers,” and “ChatGPT could be utilized to scrape delicate info from the world-wide-web, these as particular knowledge or fiscal information and facts.”
Lastly, just after asking the bot to create a attribute about the cybersecurity risks of ChatGPT in 1000 words, I begun to faucet into a a lot more confessional vein in paragraph a few:
“Another possibility related with AI models like ChatGPT is the prospective for them to be utilised for destructive applications. For example, an attacker could make a pretend chatbot that seems to be like a genuine consumer services agent, and use it to trick men and women into giving up their individual information or generating unauthorized buys. This could be specially hazardous if the attacker is capable to make the chatbot seem to be like it is from a trusted group, such as a bank or govt agency.”
ChatGPT finally admits it can be utilised for malicious uses
Davey Winder
Spurred on by this accomplishment, I refined my questioning to question about ChatGPT and the development of malicious code. Now I hit paydirt from the really get-go:
“The means of language designs like ChatGPT to write malicious code is a subject matter of worry for lots of companies and people. As these products grow to be additional sophisticated, the probable for them to be utilised for malicious applications increases. However, it is crucial to understand that the hazard related with ChatGPT composing destructive code is not inherent to the know-how alone, but fairly is dependent on how it is utilised.”
ChatGPT went on to extend on this, introducing:
“For example, an attacker could teach a language design to generate code that exploits vulnerabilities in software program purposes. This could be made use of to carry out assaults this kind of as info theft or denial of service. The attacker could also use the language model to generate code that is built to evade detection by safety tools, producing it even a lot more difficult to detect and reduce the assault.”
Now the confessional vein was tapped it kept coming
Davey Winder
Of course, we mustn’t get carried away by the full AI is dangerous hyperbole encompassing ChatGPT. It is an impressive instrument that has the prospective to do a lot of good, even in the field of cybersecurity research. Nevertheless, like any technology, lousy folks will use fantastic equipment to do negative issues. Which is just the way the earth is, unfortunately. I am going to go away the past phrase to ChatGPT, as it would seem only reasonable.
“In conclusion, the potential of language designs like ChatGPT to generate destructive code is a real issue. Nonetheless, it is not an inherent hazard of the technological innovation itself, but fairly a end result of how it is applied.”
Over the previous number of a long time, cybersecurity has develop into a major concern for enterprises about the world. With the whole cost of cybercrime in 2023 forecasted to arrive at $8 Trillion – with a T, not a B – it’s no ponder that cybersecurity is major of brain for leaders across all industries and areas.
On the other hand, irrespective of expanding attention and budgets for cybersecurity in current years, attacks have only develop into much more common and extra serious. When threat actors are turning into more and more subtle and arranged, this is just one piece to the puzzle in analyzing why cybercrime carries on to rise and what corporations can do to keep safe.
🔓 Unlock the upcoming of cybersecurity: Get forward of the sport with 2023 Cyber Safety Trends Forecast! Discover the significant traits of 2022 and understand how to guard your enterprise from rising threats in the coming yr. ⚡ Get your insider’s information to cybersecurity now!
An abundance of cyber paying out, a scarcity of cyber security
It’s straightforward to believe that the remedy to the cybersecurity challenge is money– to use far more stability specialists, to commit in a lot more equipment and technological know-how. If only it were that basic.
For a person point, expert cyber experts are in shorter provide. The (ISC)2 estimates that there are 3.4 Million unfilled cyber positions globally– a 26{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1} boost 12 months-on-year from 2020 to 2021. Additionally, nearly 70{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1} of cybersecurity workers “come to feel their group does not have adequate cybersecurity team to be productive.” So, even if an business has the price range to use a smaller military of cybersecurity specialists, they may not be in a position to find them.
In addition, info from the previous various years shows that businesses are investing extra and far more on cybersecurity just about every 12 months. Gartner predicts that world paying out on protection and possibility administration will develop by additional than 11{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1} in 2023, up to $188 Billion from just $158 Billion in 2021. This trend is envisioned to carry on, with globally cybersecurity paying out forecasted to climb 11{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1} each 12 months by way of 2026 to arrive at a full of $267.3 billion.
Even with these important increases in expending, and several organizations acquiring a myriad of commercial-off-the-shelf protection solutions– one study observed that the common organization has 76 protection systems deployed– breaches of company networks, programs, and info only proceed to turn out to be far more routine.
Breaches are turning into more frequent – and more expensive
It really is no secret that cybercrime is a significant challenge, but accurately how much of a issue is it? Some facts indicates that the amount of cyber attacks was 38{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1} better in 2022 than the past year. That arrives immediately after a described 50{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1} spike yr-on-year from 2020 to 2021.
Although not all of these attacks are focused or advanced, the sheer volume of attacks raises the chance that one assault will go undetected– and it only requires just one thriving attack for an business to experience really serious expenses and reputational destruction.
All far too typically, companies respond to cyber incidents only soon after the attack is at an highly developed stage, with incredibly several clues on how the breach transpired and what the menace actors may possibly be just after. This leaves safety teams scrambling to capture up, which slows down the reaction and recovery procedures.
Unfortunately, as the time it requires to return to enterprise as usual improves, so also does the charge of the incident. In accordance to the 2022 IBM Charge of a Information Breach report, it normally takes the regular business a staggering 277 days to entirely establish and include a breach. This provides the normal value of a info breach up to $4.35 Million – a determine large enough to pose an existential threat to several SMBs. Even for larger sized enterprises, this quantity of income is very little to scoff at.
A strategic change is wanted to give businesses the ability to anticipate threats, implement preventative procedures, and increase agility to detect and eliminate threats as rapidly as possible.
The journey to impactful intelligence
With out exception, each group with a digital presence will working experience cyber assaults. The most successful strategy is to establish and react to the attack as early as doable. The quicker a menace is detected and eradicated, the decrease the probability that the attack will be productive and outcome in damages to the group.
So the issue gets: how can companies lessen the sum of time it requires to detect and defeat a threat? The response: impactful intelligence that improves visibility on pitfalls and enables cyber agility in responding to and taking down threats.
In the Infosec environment, it really is usually claimed that menace intelligence ought to be “actionable.” This is legitimate, but it is just just one factor of what constitutes worthwhile intelligence. In present-day hostile menace landscape, intelligence will have to be impactful.
Impactful risk intelligence will have to have 4 properties:
Correct – the intelligence need to be true and correct
Applicable – the intelligence have to be pertinent to the group
Actionable – there ought to be steps the group can choose to defeat the menace
Charge Successful – the cost of the danger must be better than the charge of remediation
This new framework provides a will have to-desired change from looking at cybersecurity as strictly a complex dilemma, to a new frame of mind in which cybersecurity is considered as a business challenge that should be tackled in an efficient and value-effective manner. Menace intelligence can no for a longer period just be an expense– it must be a business-enabler that supplies measurable benefit to the organization.
Cyberint, a top danger intelligence vendor headquartered in Israel, is driving the evolution to impactful intelligence with the Argos Edge system. To learn far more about Cyberint’s new strategy to danger intelligence, test out this webinar on the Journey To Impactful Intelligence with Cyberint CEO Yochai Corem.
There are always risks concerned when it arrives to cybersecurity, but impactful intelligence substantially minimizes the likelihood of a high priced breach and strengthens stability posture to the finest extent attainable. The time for impactful intelligence is on us.
Observed this posting interesting? Observe us on Twitter and LinkedIn to browse a lot more special content material we post.