5 secrets only cybersecurity pros and hackers know

5 secrets only cybersecurity pros and hackers know

Some security actions are prevalent knowledge. I really don’t need to have to remind you to install that most recent update on your laptop, suitable?

Others are considerably less clear. Do you lock your personal computer each individual time you get up? Unless of course you are living by itself, you should. Here’s the easiest way to do it if you’re lazy.

On your telephone, you’d most likely hardly ever guess leaving your Bluetooth linked 24/7 is a mistake. Here’s why — and what to do if you just can’t live with no your AirPods.

I have obtained your back again with extra tricks only tech execs know to continue to keep you protected and safe.

1. See if an individual is secretly finding copies of your email messages

I often get calls to my national radio exhibit from men and women anxious that somebody is viewing everything they do. 

One of the initially techniques I propose is: Make certain your inbox is locked down. Listed here are ways if you discover or suspect any standard logins.

  • Log in to your electronic mail, then go to your account or security options.
  • You will find an choice that will allow you to watch your the latest login activity or login heritage. It will be labeled something like “Recent Activity,” “Security,” or “Login Heritage.”
  • Professional idea: Use Gmail? Click the Aspects hyperlink future to the Last account exercise at the base of any Gmail site.
  • Evaluation the record of new logins. See anything at all that isn’t you or 1 of your gadgets? You might see a strange spot, too.

If you spot an unfamiliar place or a product that is not yours, act speedy. Improve your password, be guaranteed two-variable authentication is turned on, and log all units out of your account.


cybersecurity
Kim Komando offers you the strategies that only cybersecurity execs know to shield you from hackers.
Getty Photos/iStockphoto

2. Make certain your printer didn’t get hacked

Like your laptop, your printer is a goldmine for hackers. Why? Printers typically retail outlet copies of the docs that have been printed. Any cybercriminal could get copies of sensitive details, like your fiscal records.

Right here are three indicators your printer has been hacked:

  1. Your printer commences printing blank pages or a bunch of people. 
  2. You see print work you did not initiate. 
  3. Your printer’s configurations have improved — and it was not you.

What need to you do? 

  • Unplug the printer. Push and hold its Reset button, usually on the printer’s back again or base.  
  • When keeping the Reset button, plug the printer back in, and change it on. In about 20 seconds, lights will flash to reveal it’s completed.

Managing out of ink mid-print is the worst. Use these insider secrets to help save on ink expenses.


Kim Komando

Seem like a tech professional, even if you are not! Award-profitable popular host Kim Komando is your mystery weapon. Pay attention on 425+ radio stations or get the podcast. And be part of in excess of 400,000 individuals who get her absolutely free 5-moment day-to-day electronic mail e-newsletter.


3. There’s a hidden place tracker on your Iphone

I propose you search by way of the spot options on your cellphone. That will go a extended way in shutting down a good deal of the GPS monitoring. But you just cannot stop there. 

Why does your telephone inform you how lengthy it’ll consider to get to the office environment or is familiar with your ETA to the grocery store when you get in the vehicle for Saturday early morning errands? That is section of Sizeable Areas.

Apple claims this aspect exists so your telephone can master sites sizeable to you and provide personalised companies, like traffic routing and greater Images Recollections.

Here’s how to entry it — and shut it down.

  • Open your iPhone’s configurations, then tap Privacy & Stability.
  • Pick out Place Solutions.
  • Scroll down and tap System Products and services.
  • Scroll till you see Major Areas and tap that.

If you really don’t want your Apple iphone to keep track of your whereabouts, slide the toggle next to Important Places to the still left to disable the placing.

Want to wipe out this listing of considerable areas? Comply with the methods listed here.

4. You can wipe your phone if you reduce it

The extremely idea of your cell phone in another person else’s arms is creepy. Picture a stranger rifling by means of your pics, movies, applications, discussions, and browser tabs.

So what if your mobile phone goes missing? You can choose a step to shield your info, even if you under no circumstances get that cellular phone again.

To remotely erase your Iphone:

  • Open up iCloud.com/come across and go to the Discover Apple iphone function.
  • Find your shed cellular phone, then find Erase Iphone.

To remotely erase your Android mobile phone:

  • Go to android.com/uncover and sign in to your Google account. Choose your dropped cellular phone, and you will get details on its place.
  • When prompted, pick Empower lock & erase.
  • Select Erase gadget to wipe its data.

Verify out my information here for far more techniques to come across, back again up, or erase your phone.

5. Apps are desperate for you to share the juicy particulars

Social media firms are dying to get their fingers on your contacts’ birthdays, photographs, entire names, e mail addresses, and a lot more. They tell you it is a useful resource to obtain your close friends, but your friends’ info is not yours to give away. Which is their possess to make a decision where by to share. 

From your address book, providers make so-known as Shadow Profiles. They can understand a ton from those you know, even if they’re not utilizing those people platforms. Sneaky things.

How can you make a variance? Never give applications accessibility to your phone’s contacts. Overview which apps do have accessibility and flip it off. And always pay back focus and end sharing details without having a true gain to you. 

Even your cellular phone number is powerful in the wrong palms.

Lansing Community College suspends classes for ‘cybersecurity incident’

Lansing Community College suspends classes for ‘cybersecurity incident’

LANSING — One of the state’s greatest neighborhood colleges is shutting down for the rest of the 7 days as it grapples with an “ongoing cybersecurity incident,” officers mentioned on social media.

Lansing Neighborhood Higher education is suspending nearly all classes and all things to do and asking college students and most workforce not to get the job done or log into the college’s techniques or arrive to campus.

Most classes are canceled for Thursday and Friday.

The university stated it has no evidence that worker or student data has been compromised, but acknowledged that “We do not know anything nevertheless, and conversation is heading to be incredibly tough once we disconnect from the network.”

What It Means for Cybersecurity Startups’ Access to Capital

What It Means for Cybersecurity Startups’ Access to Capital

Previous week’s spectacular collapse of Silicon Valley Bank (SVB) could put a damper on the capability of venture-backed cybersecurity startups to safe very important cash for functions and strategic investments.

Safety professionals understand that even the US government’s swift go more than the weekend to guard SVB customer deposits will possible do little to tamp down the uncertainty that the bank’s sudden exit has brought about.

Young Startups Will Really feel the Brunt

“Economical assistance in the type of lines of credit rating and undertaking personal debt is likely to become considerably far more tricky [for startups] to arrive by,” says Rob Ackerman, founder and taking care of director of AllegisCyber Cash. “SVB was the main supply of that funding and with them absent, the slope of the hill for young startups just became that substantially extra complicated.”

SVB was, until the center of final 7 days, the 16th greatest bank in the US with property of far more than $200 billion and total deposits of some $175 billion. Its difficulties started March 8 when the lender, in a midquarter update, introduced that it had dropped $1.8 billion from the sale of US treasuries and house loan-backed securities that it experienced ordered seriously in the latest yrs. On the exact working day, SVB declared designs to increase $2.25 billion by using community supplying to pay out clients searching for to withdraw their deposits from the bank.

The news brought on a around rapid run on the institution, as spooked investors and prospects withdrew a staggering $42 billion from the bank in a 24-hour period — leaving SVB with a adverse harmony of $958 million by close of enterprise March 9. A day afterwards, on Friday, March 10, federal regulators declared the financial institution bancrupt and seized its deposits, signaling the largest banking failure given that the collapse of Lehman Brothers in 2008.

Containing the Harm

Above the weekend, the Federal Deposit Insurance coverage Company (FDIC) as receiver designed a new entity referred to as the Deposit Insurance coverage Countrywide Bank of Santa Clara (DINB) and transferred all of SVB’s deposits to it. On March 12, a US federal government scrambling to reduce a broad meltdown throughout the banking sector swiftly announced that depositors would have whole obtain to all of their income at SVB starting Monday, March 13. In a assertion, Secretary of the Treasury Janet Yellen claimed the government would lengthen the same exception for consumers of Signature Financial institution of New York, which also went bancrupt more than the weekend.

Analysts see SVB’s failure as getting an primarily heavy toll on the technological innovation sector. “SVB was a foundational cornerstone of the funding ecosystem for the innovation ecosystem, and the cybersecurity business is no exception,” Ackerman suggests. “They were being arguably more influential than any other solitary player to the growth and results of tech startups.”

Virtually each and every undertaking agency was engaged with SVB at some level — be it the undertaking companies them selves or their portfolio firms banking at SVB. And inside the stability neighborhood, they were being crucial to the banking and funding requires of the sector in the US, Israel, and the British isles, Ackerman says.

A Revaluation of Investment Procedures?

Richard Stiennon, chief study analyst at IT-Harvest, claims public experiences exhibit that some 500 cybersecurity sellers banked with SVB — a not-stunning variety considering there are 640 cybersecurity firms just in California by itself. The move by federal regulators to guarantee that SVB buyer deposits remained untouched has relieved some of the early stress and anxiety more than the failure when numerous cybersecurity corporations faced the authentic prospect of currently being unable to make payroll.

“The VCs that ended up locked out of their accounts on Friday invested a prolonged weekend trying to help save their portfolio firms, whilst their very own money had been unavailable,” Stiennon suggests.

That experience will most likely leave them reevaluating their practices. “I totally count on a death in new investments in cybersecurity,” Stiennon tells Darkish Reading through. Cybersecurity expenditure activity in the initial two months of 2023 has previously been low at just $1.7 billion so far, it truly is back again at 2020 amounts. 

“Businesses, which were boosting to lengthen runways, will either have dramatic down rounds or in fact have to shut down,” he states. Limited companions, or the buyers who back VC initiatives, are likely to be unwilling to set a lot more funds into cash. And with the generous enterprise funding that was accessible only by way of SVB now long gone, startups have three selections, he says. They have to either come across a way to come to be rewarding, significantly slice prices, or obtain a new funding supply.

“Organizations with excellent engineering and very good groups could be snapped up by strategic investors at rock-base valuations,” Stiennon notes. “Private fairness firms will have a unique chance to snap up some great corporations.”

Spreading the Monetary Risk

Anticipate to see VC companies and their portfolio organizations diversify the place they keep their deposits, Ackerman provides. Increasingly, they are going to be looking for the safety available by substantially greater monetary establishments — which, having said that, are not likely likely to be as supportive or as being familiar with of the prerequisites of modern cybersecurity companies, he notes.

Analysts also expect that the SVB debacle will have an impact on how and from wherever company companies source their cybersecurity prerequisites, at least in the small term. SVB’s failure has drawn interest to the challenges related with buying from startups, and numerous corporations are going to be looking for the stability that far more founded, mature corporations supply.

“I’d anticipate procurement teams to introduce much more hurdles in the because of diligence course of action of before-stage sellers to have an understanding of the underlying resilience of the cybersecurity vendors’ economical ecosystem,” Forrester analyst Jeff Pollard tells Darkish Looking through. Enterprise procurement employees are going to want to know far more about the concentration possibility and resilience of their vendor’s banking processes, he adds. And they will possible need reassurances that if a comparable situation performs out all over again, their early seller can go on to make payroll or pay crucial suppliers for a specific period of time.

Also, cybersecurity startups will progressively seem to financial institution with additional than 1 entity to distribute possibility. “The dilemma with that is quite a few startups worked with SVB due to the fact SVB made it uncomplicated for startups to do the job with them,” Pollard states. 

Now startups are heading to have a really hard time doing work with other banks, for the reason that cyber startups are inclined to have far more volatility in their cash flows, he notes. “In addition, quite a few founders may perhaps not be US citizens, which can create its personal set of troubles when making an attempt to establish accounts.”

KamiKakaBot Malware Used in Latest Dark Pink APT Attacks on Southeast Asian Targets

KamiKakaBot Malware Used in Latest Dark Pink APT Attacks on Southeast Asian Targets

Mar 13, 2023Ravie LakshmananCyber Attack / Malware

KamiKakaBot Malware Used in Latest Dark Pink APT Attacks on Southeast Asian Targets

The Dim Pink state-of-the-art persistent menace (APT) actor has been connected to a fresh new set of assaults concentrating on government and army entities in Southeast Asian nations with a malware known as KamiKakaBot.

Darkish Pink, also identified as Saaiwc, was very first profiled by Team-IB previously this calendar year, describing its use of custom made tools such as TelePowerBot and KamiKakaBot to run arbitrary instructions and exfiltrate delicate information and facts.

The threat actor is suspected to be of Asia-Pacific origin and has been lively since at minimum mid-2021, with an enhanced tempo observed in 2022.

“The newest assaults, which took spot in February 2023, were being practically equivalent to former assaults,” Dutch cybersecurity firm EclecticIQ disclosed in a new report revealed very last week.

“The main change in the February marketing campaign is that the malware’s obfuscation routine has improved to far better evade anti-malware measures.”

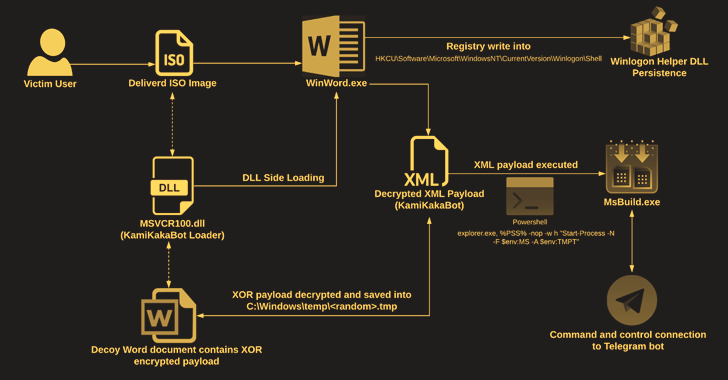
The attacks engage in out in the kind of social engineering lures that have ISO image file attachments in e-mail messages to produce the malware.

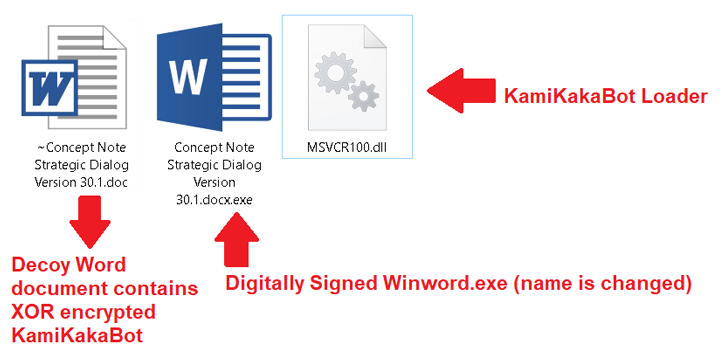
The ISO graphic involves an executable (Winword.exe), a loader (MSVCR100.dll), and a decoy Microsoft Phrase document, the latter of which will come embedded with the KamiKakaBot payload.

KamiKakaBot Malware

The loader, for its part, is made to load the KamiKakaBot malware by leveraging the DLL side-loading system to evade protection protections and load it into the memory of the Winword.exe binary.

KamiKakaBot is generally engineered to steal facts stored in net browsers and execute distant code using Command Prompt (cmd.exe), even though also embracing evasion tactics to mix in with victim environments and hinder detection.

WEBINAR

Find out the Concealed Dangers of Third-Party SaaS Apps

Are you conscious of the hazards related with third-bash application access to your company’s SaaS applications? Sign up for our webinar to learn about the types of permissions currently being granted and how to limit danger.

RESERVE YOUR SEAT

Persistence on the compromised host is accomplished by abusing the Winlogon Helper library to make destructive Home windows Registry key modifications. The gathered facts is subsequently exfiltrated to a Telegram bot as a ZIP archive.

“The use of legitimate website companies as a command-and-manage (C2) server, these as Telegram, remains the variety 1 decision for various menace actors, ranging from normal cyber criminals to sophisticated persistent menace actors,” the Amsterdam-centered company explained.

“The Dim Pink APT group is very probably a cyber espionage-determined menace actor that especially exploits relations between ASEAN and European nations to produce phishing lures through the February 2023 campaign.”

Identified this short article exciting? Abide by us on Twitter and LinkedIn to read through a lot more exceptional information we write-up.

Make Sure Your Cybersecurity Budget Stays Flexible

Make Sure Your Cybersecurity Budget Stays Flexible

The tsunami of cyberattacks in recent several years has wreaked havoc among businesses’ infrastructures and drowned quite a few defense methods throughout all industries. Incorporating added strain is the point that cyberattacks are normally connected to world activities. For occasion, hackers have exploited the vulnerabilities within just progressively complex distant work infrastructures ignited by the pandemic, presenting new challenges for security leaders. The reality is, these days hackers aren’t breaking in — they’re logging in by using human-dependent assaults.

With today’s uncertain overall economy and superior inflation prices, this year’s spending budget forecast phone calls for dry disorders throughout the security landscape. This year’s budgets now have been accepted, but vital priorities might shift throughout the 12 months — earning comprehending when and how to pivot limited budgets a important element of guaranteeing the stability of CISOs’ infrastructures.

A single technique CISOs are pursuing is to apply comparable ideas as attackers who are exploiting economic, social, and technical disruptions within just modern society.

Priorities to Contemplate When Shifting Budgets

With the switching mother nature of the financial state and workforce constructions, there are numerous diverse things to look at when executing a correctly informed funds shift. So, from 1 CISO to another, below are 5 critical priorities for stability leaders to look at when getting ready for possible price range shifts this 12 months and further than:

  1. Geopolitical influences of cybersecurity: Hackers have developed their assaults to exploit geopolitical disruptions. These impacts, like the war in Ukraine, have refined the use of common attack types to improve the good results of attackers’ ransomware efforts.For occasion, Russian hackers this sort of as the Conti ransomware group have thwarted US and worldwide war attempts to assist Ukraine via the concentrating on and injection of ransomware into corporations working in critical infrastructures. A short while ago, the popular approaches leveraged to infect corporations with ransomware across the world consist of password spraying, spear-phishing, and credential stuffing. Owing to these progressively refined assaults, CISOs must combine technological defense techniques capable of thwarting assaults that are continually evolving.
  2. Uncertain economic climate: Desperate instances contact for determined measures, and historically, unsure financial durations mean an maximize in cyberattacks. Attackers are leveraging state-of-the-art technologies to have interaction in substantial-risk, identification-linked fraud practices to steal staff credential details and extort businesses. In fact, considering that 2021, there has been extra than a 60{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1} increase in corporate email compromises, top to added enterprise losses totaling above $40 billion.

    As present economic standings reel in uncertainty, CISOs should prepare to alter their budgets towards ongoing hazard management, with distinctive emphasis on tools that will assist mitigate human mistake. From compliance to threat assessments, techniques will need to revolve about minimizing superior-chance identity assaults.

  3. Evolving laws: As we know, cybersecurity is ever-evolving. This usually means that new polices are constantly designed — and others that are already in result, these types of as GDPR and CCPA, are turning out to be stricter. The present problems concerned with adhering to dynamic — and usually overlapping, field-focused, regional, and cross-nations prerequisites — can trigger very the headache for security leaders. So, how can CISOs repeatedly comply in an increasing safety landscape?

    The appropriate financial commitment in thorough defense measures, this sort of as zero-have faith in access, will make certain the stability of enterprises’ info, aiding them continue to be compliant and adherent to the variety of crossover regulation.

  4. Teaching: In the cybersecurity field, CISOs and safety leaders won’t be able to pay for for their enterprises to be impacted by the current expertise hole. A lack of competent staff can end result in potentially devastating vulnerabilities in just their infrastructure.

    Stability leaders will have to thoroughly prepare for paying reprioritizations as the competencies gap widens. This makes certain that their workforce has the needed awareness to engage in powerful in-dwelling modern day reskilling and upskilling strategies. One particular vital spending plan shift could be towards the implementation of assistive, highly developed cloud-based mostly services, these types of as high-hazard identity administration answers, which can also be built-in to reinforce the organization’s electronic infrastructure.

  5. Fashionable strategies: At this time, 80{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1} of breaches count on personnel entry qualifications. To increase their defenses, CISOs must confirm their latest procedures are proficient ample to combat the continuous inflow of human-centered attack kinds, like Kerberoasting and go-the-hash attacks. If infrastructures are unstable and priorities want to change, CISOs can switch to frequent equipment, which include zero-rely on entry and significant-hazard identity-centered manage alternatives — which can fight developing offense attempts.

    As identity-centered assaults rise, corporations will have to have security tools programmed to have faith in no just one, not even their possess sellers. This will improve compliance steps and permit the protection and sole ownership of inner, exterior, third-occasion, purchaser, and stakeholder’s person knowledge. It will also make it possible for for more powerful authentication, the monitorization of interior and exterior user operations, and the halting of lateral motion inside businesses’ infrastructures.

    As cyber threats evolve, companies will will need to retain speed and allocate for improved security methods that give seamless management in their budgets.

Evolution Is Critical

Hackers will proceed to change their methods of attack and exploit the vulnerabilities in latest world-wide geopolitical events. To prevent them, protection leaders will want to make guaranteed their latest budgets can pivot and are adaptable sufficient to deploy modern defense strategies and technologies, and capable of handling precedence shifts as the 12 months progresses.

This involves leaders taking the recent financial, social, and technological factors into thought though producing their defense approach. Performing so will assistance them make extra educated decisions around the ideal use of their cybersecurity budgets for the upcoming calendar year and beyond.

Hold up with the most recent cybersecurity threats, freshly-learned vulnerabilities, information breach information, and emerging trends. Shipped daily or weekly suitable to your e-mail inbox.

Cybersecurity is a ‘resilient industry’ in spite of recession fears: CrowdStrike CEO

Cybersecurity is a ‘resilient industry’ in spite of recession fears: CrowdStrike CEO

Fears of an financial downturn or possible economic downturn, not to mention bigger curiosity premiums, could have some businesses slicing expending on things like cloud computing, but CrowdStrike (CRWD) CEO George Kurtz claims the very same just cannot be mentioned of cybersecurity paying.

“Cybersecurity is anything you may possibly be able to pause, but you can not place off indefinitely,” Kurtz instructed Yahoo Finance Live. “That’s definitely what we’ve been looking at.”

In accordance to a survey of 1,000 business executives done by the International Info Technique Safety Certification Consortium (ISC)2, a nonprofit that gives education certifications for cybersecurity workers, cybersecurity employees are the least probable to deal with layoffs in a economic downturn.

The cause? The danger of cybercrime tends to boost during recessions and financial downturns, as criminals appear for new ways to get paid funds. What’s far more, the cybersecurity market is already experiencing a significant worker scarcity, with (ISC)2 expressing the international cybersecurity workforce has to grow by 3.4 million workers to address the world’s safety demands.

And according to Kurtz, that danger coupled with an at any time-evolving cybersecurity surroundings suggests that companies basically are not keen to reduce their cybersecurity budgets at this stage.

“Organizations are searching to shield on their own. There are mandates from the board, there are compliance mandates, and it unquestionably is a resilient business,” he reported. “What we have observed is that budgets are modestly up in some circumstances, other people flat. But we have not seriously observed them go down.”

Sign up for Yahoo Finance's tech newsletter.

Sign up for Yahoo Finance’s tech e-newsletter.

The Biden administration, in the meantime, is trying to realign conversations all over cybersecurity to put more emphasis on corporate accountability for shielding essential data.

According to the administration’s approach, individuals, compact firms, and area municipalities shouldn’t bear the stress of working with highly developed cyberthreats. Alternatively organizations that can improved insulate those groups from criminals should really.

Which is precisely what Jen Easterly, director of the Cybersecurity and Infrastructure Protection Agency explained to Yahoo Finance at CES 2023 in January. Easterly says she thinks firms like Microsoft, Amazon, and other individuals want to strengthen their protection posture to prevent downstream protection lapses from turning into significant intrusions for smaller sized companies that don’t have the assets to react to these types of threats.

Photo by: STRF/STAR MAX/IPx 2020 12/24/20 Suspected Russian hackers made failed attempt to breach CrowdStrike. STAR MAX File Photo: 12/3/20 A CROWDSTRIKE logo shot off an iphone SE 2020.

Photo by: STRF/STAR MAX/IPx 2020 12/24/20 Suspected Russian hackers designed failed attempt to breach CrowdStrike. STAR MAX File Picture: 12/3/20 A CROWDSTRIKE brand shot off an apple iphone SE 2020.

“We’ve basically accepted as normal that technological know-how is produced to market place with dozens or hundreds or 1000’s of vulnerabilities and problems and flaws,” Easterly explained through a discussion at the trade clearly show.

“We’ve recognized the point that cyber safety is my work and your position and the occupation of my mother and my kid, but we’ve set the stress on consumers, not on the providers who are most effective outfitted to be in a position to do a thing about it.”

For his component, Kurtz states cybersecurity is a shared obligation.

“When we assume about program in basic. When you appear at Microsoft, there were 30 zero-day vulnerabilities [exploitable flaws with no fix yet],” he said. “So there’s a shared duty in creating confident that application, like Windows, is really secure.”

Acquired a suggestion? E-mail Daniel Howley at dhowley@yahoofinance.com. Comply with him on Twitter at @DanielHowley.

Click listed here for the most up-to-date inventory industry information and in-depth assessment, together with situations that shift stocks

Read the most up-to-date money and organization news from Yahoo Finance