(KXNET) — North Dakota is the first point out in the country to approve legislation demanding cybersecurity instruction.
“This is a historic initially-in-country piece of legislation which is going to profit North Dakota’s faculties, students, families in our institutions,” said Governor Doug Burgum.
Governor Burgum signed into law Property Monthly bill 1398 which involves the training of pc science and cybersecurity and the integration of these content requirements into the lecture rooms of K-12 grade.
“Cybersecurity is a person of the most urgent concerns we have in North Dakota,” mentioned Gov. Burgum.
Governor Burgum states we now stay in a entire world where by facts no more time only arrives from textbooks. As before long as little ones are born, they are surrounded by engineering.
“All of that generates option, but it also produces threat. And getting an comprehension of both of those the energy and probable but also the difficulties of technologies is the essential to what cyber instruction is,” stated Burgum.
Do the job on Household Invoice 1398 begun back again in 2015 when the Division of General public Instruction shaped a operating team of legislators and other stakeholders to craft a vision for K-12 education’s laptop or computer science and cybersecurity tutorial requirements.
“Our eyesight is to integrate and underscore the relevance of laptop science and cybersecurity instruction into the lessons our learners consider as they transfer by means of our K-12 technique,” claimed Kirsten Baesler, North Dakota Faculty Superintendent.
The Governor has demonstrated his assistance for cyber security by encouraging the younger technology to go after and embrace the globe of computer science. He has promoted events this sort of as CyberMadness tournaments and Girls Go Cyberstart competitions in North Dakota’s universities. Now he has signed a invoice that will enable equip future leaders and teachers to navigate the ever-evolving environment of technology.
“This invoice is truly rewriting the narrative for college students, for teachers, and for the leaders of nowadays and tomorrow. Our pupils are presently functioning hard to make our state better and to resolve the problems that the environment is dealing with,” mentioned Zoey Bundy, a senior at Davies Superior University.
And our older technology has a chance to study about cyber security as effectively. Any North Dakota resident can acquire on the net classes in cybersecurity, networking, programming, and extra so that they may well also have the skills and tools to live in a cyber world.
In this article, we will discuss the 12 best cybersecurity stocks to buy now. If you want to explore similar stocks, you can also take a look at 5 Best Cybersecurity Stocks to Buy Now.
The importance of cybersecurity in today’s digital age cannot be overstated. As pointed out in one of our articles, cyberattacks are increasing across the globe. A report by Nasdaq shows that cyberattacks rose globally throughout 2020, relative to the levels seen in 2019 and 2018. As businesses go digital, their vulnerability to cyberattacks is increasing, and cybersecurity spend is going up.
On February 27, Tenable (NASDAQ:TENB) CEO Amit Yoran appeared in an interview on CNBC to discuss his outlook for the cybersecurity space. Yoran noted that the environment for cybersecurity is “incredibly healthy” as an increased number of cyberattacks is driving cybersecurity spend and thus propelling the sector’s outperformance. At the end of Q4 2022, Tenable (NASDAQ:TENB) was held by 30 hedge funds. As of March 22, Tenable (NASDAQ:TENB) has returned 15.91{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1} to investors on year-to-date basis.
On March 17, Cloudflare (NYSE:NET) CEO Mathew Prince weighed in on the risks of increased cyberattacks amid the recent banking failures. Prince noted that he is seeing a rise in cyberattacks on companies that are clients of the banks that have failed, as hackers are impersonating the banks and exploiting the customers. As of March 22, Cloudflare (NYSE:NET) has gained 28.87{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1} year to date.
The cybersecurity industry has experienced rapid growth in recent years as cyber threats have become more frequent and sophisticated. With the increasing reliance on technology, cybersecurity has become a critical issue for both national and organizational security. This trend has led to a significant increase in investments in the cybersecurity sector, as governments, corporations, and individuals seek to protect themselves from potential cyber attacks.
Portfolio Manager: “Still Playing Pretty Defensive”
On March 21 Independent Solutions Wealth Management’s portfolio manager, Paul Meeks, appeared in an interview on CNBC to discuss his outlook for tech and where he is looking to invest. Paul Meeks anticipates a recession and thinks that right now the best way to go about investing in tech stocks is to remain on the defensive side. Paul Meeks is bullish on small-cap and mid-cap names in tech that are in relatively recession-resistant sectors. Paul Meek said:
“I try to target what I think are the best, most resilient, industries. Right now I got the China reopening trade, I have data networking, semiconductors but all about automobile and industrial applications, (and) cybersecurity.”
While Paul Meeks thinks that these sectors are not completely immune to a recession, he thinks that they are not going to suffer as much as other areas within tech.
In a high interest rate environment, growth investors are repositioning and investing in areas that are not as vulnerable to an economic slowdown. The cybersecurity space can be thought of as a relatively defensive sector within tech due to its importance to corporate and national security. Some of the best cybersecurity stocks to buy now according to analysts and hedge funds include Datadog, Inc. (NASDAQ:DDOG), CrowdStrike Holdings, Inc. (NASDAQ:CRWD), and Palo Alto Networks, Inc. (NYSE:PANW). Let’s discuss these, among others, in detail below.
12 Best Cybersecurity Stocks to Buy Now
Our Methodology
We sifted through cybersecurity ETFs and found 30 cybersecurity stocks. We then sourced the hedge fund sentiment for each stock using Insider Monkey’s database of over 900 elite hedge funds. We narrowed down our selection to stocks that were the most popular among hedge funds and ranked them in ascending order of the number of hedge funds that have positions in them. Along with each stock, we have included the hedge fund sentiment, analyst ratings, and top shareholders.
12 Best Cybersecurity Stocks to Buy Now
12. Check Point Software Technologies Ltd. (NASDAQ:CHKP)
Number of Hedge Fund Holders: 33
On February 14, Truist analyst Joel Fishbein raised his price target on Check Point Software Technologies Ltd. (NASDAQ:CHKP) to $140 from $130 and maintained a Buy rating on the shares. As of March 22, the stock has returned 13.31{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1} to investors over the past 6 months and is trading at a PE multiple of 19.94. The stock is one of the best cybersecurity stocks to buy now according to analysts and hedge funds.
At the end of the fourth quarter of 2022, 33 hedge funds were bullish on Check Point Software Technologies Ltd. (NASDAQ:CHKP) and disclosed positions worth $754.8 million in the company. This is compared to 32 positions in the preceding quarter with stakes worth $680.4 million. The hedge fund sentiment for the stock is positive.
As of December 31, D E Shaw is the leading shareholder in Check Point Software Technologies Ltd. (NASDAQ:CHKP) and has a stake worth $166.8 million.
Gen Digital Inc. (NASDAQ:GEN) is a leading American cybersecurity company best known for Norton. The stock is placed eleventh among the best cybersecurity stocks to buy now and is trading at a PE multiple of 17x, as of March 22, and is offering a forward dividend yield of 3{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1}.
On February 2, Gen Digital Inc. (NASDAQ:GEN) posted strong earnings for the fiscal third quarter of 2023. The company reported an EPS of $0.45 and outperformed EPS estimates by $0.02. The company generated a revenue of $936 million, up 33.33{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1} year over year and ahead of Wall Street consensus by $114.50 million.
At the end of Q4 2022, Gen Digital Inc. (NASDAQ:GEN) was held by 34 hedge funds. These funds disclosed positions worth $1.17 billion in the company. As of December 31, Starboard Value LP is the top investor in the company and has a stake worth $405.3 million.
Leidos Holdings Inc (NYSE:LDOS) serves the defense, intelligence, civil, and health markets across the globe. At the close of Q4 2022, Leidos Holdings Inc (NYSE:LDOS) was spotted on 37 investors’ portfolios. These funds held collective stakes worth $615.2 million in the company, up from $409.7 million in the preceding quarter when 35 hedge funds held stakes in the company. The hedge fund sentiment for the stock is positive.
This February, Wells Fargo analyst Matthew Akers revised his price target on Leidos Holdings Inc (NYSE:LDOS) to $103 from $114 and maintained an Equal Weight rating on the shares.
As of December 31, Citadel Investment Group is the largest shareholder in Leidos Holdings Inc (NYSE:LDOS) and has a position worth $86 million.
Wedgewood Partners made the following comment about Leidos Holdings, Inc. (NYSE:LDOS) in its Q4 2022 investor letter:
“Leidos Holdings, Inc. (NYSE:LDOS) was a top contributor to portfolio performance during the 4th quarter. The Company ended the quarter with a strong adjusted book to bill ratio of about 1.4X. While the significant change in the global defense situation to date has caused some near-term pauses and noise around the ramping of different projects and priorities, Leidos is positioned exceedingly well as a defense contractor particularly to the U.S. and its allies, as we expect a significant increase in U.S. government defense and civilian spending during fiscal 2023. This increased spending should in turn flow through to Leidos’ order book, as they focus on modernizing IT environments and cybersecurity. We continue to hold Leidos has a top weighting as it still trades at historically attractive forward earnings multiple against the backdrop of a new “Cold War.””
Other top names in the cybersecurity space that are on hedge funds’ radars include Datadog, Inc. (NASDAQ:DDOG), CrowdStrike Holdings, Inc. (NASDAQ:CRWD), and Palo Alto Networks, Inc. (NYSE:PANW).
On March 14, SentinelOne, Inc. (NYSE:S) announced earnings for the fourth quarter of fiscal 2023, in which the company beat EPS expectations by $0.03. The company reported a revenue of $126.10 million, up 92.11{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1} year over year and ahead of market consensus by $1.41 million.
This March, Wedbush analyst Taz Koujalgi raised his price target on SentinelOne, Inc. (NYSE:S) to $22 from $19 and maintained an Outperform rating on the shares. The stock is placed ninth among the best cybersecurity stocks to buy now according to analysts and hedge funds.
38 hedge funds disclosed having stakes in SentinelOne, Inc. (NYSE:S) at the close of Q4 2022. The total value of these stakes amounted to $731 million. As of December 31, Third Point is the top stockholder in the company and has a position worth $214 million.
This February, Wells Fargo analyst Andrew Nowinski raised his price target on Cloudflare, Inc. (NYSE:NET) to $75 from $55 and maintained an Overweight rating on the shares.
On February 9, Cloudflare, Inc. (NYSE:NET) reported market-beating earnings for the fiscal fourth quarter of 2022. The company generated a revenue of $274.70 million, up 41.89{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1} year over year and ahead of Wall Street expectations by $0.63 million. The company reported an EPS of $0.06 and beat EPS estimates by $0.01.
At the end of the fourth quarter of 2022, 40 hedge funds were long Cloudflare, Inc. (NYSE:NET) and disclosed stakes worth $635.9 million in the company. This is compared to 53 positions in the preceding quarter with stakes worth $629 million. As of December 31, Marshall Wace LLP is the leading investor in the company and has a position worth $119.5 million.
Here is what Baron Funds had to say about Cloudflare, Inc. (NYSE:NET) in its Q3 2022 investor letter:
“We continued to build our position in Cloudflare, Inc. (NYSE:NET) during the quarter as the shares declined with the overall software space and the long-term risk/ reward balance became more compelling. The company reported a strong second quarter, with revenue growth accelerating to 54{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1}, as well as better gross and operating margins. Third quarter guidance was also ahead of Wall Street expectations. Given Cloudflare’s proprietary network and massive global scale, its software products have a disruptive price-performance advantage over competitors. As the company introduces new products as well as disruptive packaging/pricing, its unit level economics should continue to improve over time, with the company already well ahead of its long-term gross margin target of 74{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1}, reporting 78.9{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1} for the second quarter. This drives strong cross/upselling activity with customers, reflected in strong net-dollar expansion rates in excess of 125{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1}. Indeed, in the most recent quarters, customers purchasing five or more products reached 81{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1} of the base, six or more products reached 70{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1} of the base, and seven or more products reached 58{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1} of the base. Enterprise penetration continues to be a key long-term driver, with 1,749 customers now spending over $100,000 annually with the company, growing 61{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1} and now accounting for over 60{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1} of total revenue. With approximately 152,000 paying customers at the end of last quarter, large enterprise customers still represent just 1{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1} of total paid customers and thus a material growth opportunity in the coming years. We continue to have high confidence in the company’s ability to innovate at a rapid pace (announced 20 new products or enhancements in September alone), package and bundle with disruptive pricing, and take material share in its large and growing addressable markets.”
Zscaler, Inc. (NASDAQ:ZS) was a part of 42 hedge funds’ portfolios at the end of Q4 2022. These funds held collective positions worth $540.3 million in the company. As of December 31, Two Sigma Advisors is the most prominent stockholder in the company and has a position worth $80.9 million.
On March 3, Wells Fargo updated its price target on Zscaler, Inc. (NASDAQ:ZS) to $156 from $160 and reiterated an Overweight rating on the shares. Zscaler, Inc. (NASDAQ:ZS) is one of the best cybersecurity stocks to buy now according to analysts and hedge funds.
Here is what Artisan Partners had to say about Zscaler, Inc. (NASDAQ:ZS) in its Q4 2022 investor letter:
“Zscaler, Inc. (NASDAQ:ZS) provides cloud-based Internet security solutions. In the quarter, it announced 54{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1} revenue growth and expected growth of nearly 40{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1} in 2023 (ahead of expectations). Despite solid fundamental momentum, shares have underperformed this year as investors have grown concerned about slowing demand for enterprise software as the broader global economy slows. We believe the dual trends of rising security vulnerability and increased enterprise digitization will lead to sustained demand, even in a recession. Cybersecurity remains a top concern for businesses and governments alike as cyberattacks can have devastating financial and reputational consequences. Meanwhile, managing the security needs of legacy on-premise applications, a growing number of cloud-based applications (Office 365, Salesforce, etc.) and a more remote workforce (versus pre-pandemic) make operating IT infrastructures increasingly complex. Give the attractive long-term outlook and depressed valuations, we added to the position.”
Fortinet, Inc. (NASDAQ:FTNT) is a global leader in cybersecurity and networking solutions. As of March 22, the stock has returned 26.15{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1} to investors year to date. Fortinet, Inc. (NASDAQ:FTNT) ranks sixth on our list of the best cybersecurity stocks to buy now.
On February 14, Goldman Sachs analyst Gabriela Borges took coverage of Fortinet, Inc. (NASDAQ:FTNT) with a Buy rating and a $73 price target.
47 hedge funds disclosed having stakes in Fortinet, Inc. (NASDAQ:FTNT) at the close of Q4 2022. The total value of these stakes amounted to $1.88 billion, up from $1.74 billion in the previous quarter with 47 positions. As of December 31, Viking Global is the leading stockholder in the company and has a position worth $348 million.
In addition to Fortinet, Inc. (NASDAQ:FTNT), Datadog, Inc. (NASDAQ:DDOG), CrowdStrike Holdings, Inc. (NASDAQ:CRWD), and Palo Alto Networks, Inc. (NYSE:PANW) are also poised to benefit from the secular tailwinds in the cybersecurity space.
In 2022 by yourself, global cyberattacks elevated by 38{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1}, ensuing in considerable business enterprise reduction, such as economic and reputational problems. Meanwhile, company protection budgets have risen drastically simply because of the escalating sophistication of attacks and the number of cybersecurity methods introduced into the sector. With this rise in threats, budgets, and options, how prepared are industries and nations to effectively tackle present day cyber danger?
CYE’s new Cybersecurity Maturity Report 2023 tackles this issue by shedding mild on the power of cybersecurity in distinct sectors, organization sizes, and countries. It highlights which industries and international locations have the most robust cyber postures and which are lagging, as effectively as the most commonplace vulnerabilities in present-day cyber risk landscape.
The investigation is based mostly on two years’ well worth of details, collected from more than 500 organizations in 15 countries, and spanning 11 industries and a variety of enterprise measurements. It actions cybersecurity maturity throughout 7 unique protection domains, together with software degree security, community level security, identification administration and remote entry, and far more.
Listed here are the top findings:
Finding #1: Much larger Budgets You should not Automatically Signify Improved Cybersecurity
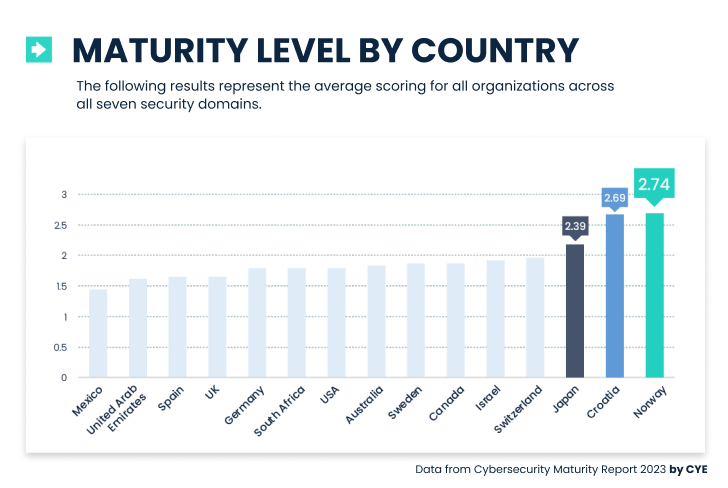
Among the nations, Norway scored the greatest on in general cybersecurity maturity level, adopted by Croatia and Japan. Whilst these international locations do not have the significant cybersecurity budgets of countries these kinds of as the US, United kingdom, and Germany, they do have state-of-the-art regulatory programs. Other feasible motives that Norway, Croatia, and Japan took the direct include early cybersecurity adoption in these countries and unified arranging by governments and companies. This obtaining illustrates how big economical investments do not necessarily translate into significant maturity amounts.
Acquiring #2: Tech Businesses Rating Typical
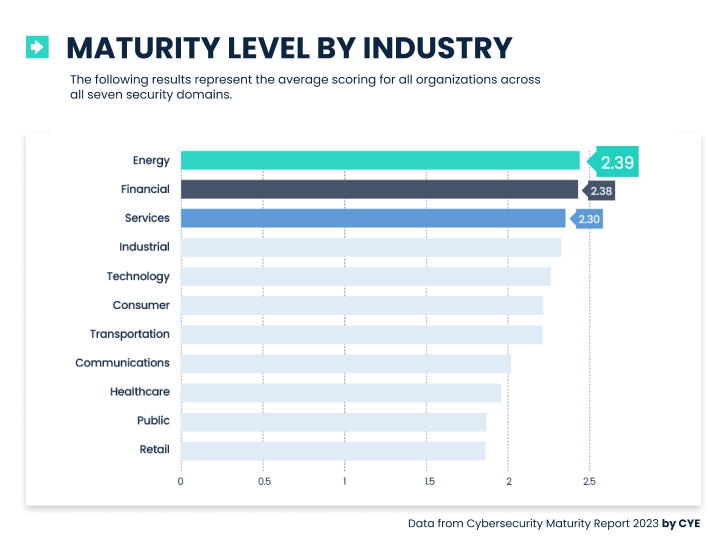
Amongst sectors, electrical power and economic industries arrived out on major for in general cybersecurity maturity amount, though healthcare, retail, and federal government businesses ended up among the the most affordable. Amazingly, the tech business scored about common, which is quite possibly simply because of the larger sized attack surface area this sort of businesses typically need to protect in comparison to other sectors.
The average rating could also be because tech companies are inclined to adopt new technologies that could be notably susceptible to assaults and exploits. In addition, tech companies are inclined to experience growth a lot a lot quicker than other sectors, which can be an added obstacle when striving to retain a solid cyber posture.
Finding #3: Modest and Medium Corporations Score Bigger Than Massive Companies
Incredibly, modest- and medium-sized companies experienced better cybersecurity maturity scores than organizations with about 10,000 staff members. This could be due to the fact little businesses may well have an easier time defending their tiny attack surfaces. With medium-sized organizations, investing in cybersecurity options is clearly a priority. When it will come to big businesses, however, obtaining to protect this sort of a huge attack surface area plainly has an result on the degree of cybersecurity maturity.
Getting #4: Approximately A single-Third of Businesses Deficiency Effective Password Guidelines
The research found that 32{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1} of companies had been identified to have weak password policies—a highly solvable problem that firms apparently have not sufficiently tackled. In addition, 23{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1} of corporations had been observed to have weak authentication mechanisms. This is regarding, mainly because the blend of the two challenges empowers hackers, who can then just log in with minimum effort.
Recommendations for Improved Cybersecurity Maturity
The all round takeaway from the report is that most corporations are not adequately ready for the threat of cyberattacks. Having said that, companies can still accomplish a large cybersecurity maturity posture without having a substantial spending plan, if they strategy and expend effectively.
To secure themselves, companies should invest in abilities, relatively than applications complete extensive assessments to stop hackers from exploiting vulnerabilities and acquire an integrated tactic to cybersecurity with board-amount accountability. Cybersecurity optimization options this sort of as CYE can help by combining technological innovation, people today, and processes to deal with organizational cyber possibility and accomplish cyber threat quantification to understand threats and prioritize mitigation.
Businesses keep on to value cybersecurity competencies, but several have moved their aim from employing cybersecurity industry experts to education up in-property workers on desired cybersecurity skills.
The regular monthly number of cybersecurity-associated position postings plummeted by nearly a third (31{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1}) in the past thirty day period, when compared with its peak a year back, according to work solutions agency In fact.com. But cybersecurity is the No. 1 ideal skill set that corporations would like their personnel to understand, with 59{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1} of technologies leaders ranking cybersecurity as a top rated-a few subject for coaching, ahead of the two information science and cloud capabilities, according to training agency Pluralsight.
For organizations that need to have to fill gaps in their employee’s technical abilities, teaching workers in new ability sets — “upskilling” in the industry parlance — is a relative deal, as opposed with the charge of using the services of a new worker, states Gary Eimerman, chief solution officer at Pluralsight.
“Specified the degree of hazard, cybersecurity hacks are a boardroom discussion across businesses,” he states. “Upskilling internally for cybersecurity talent is considerably much more value productive than selecting externally for cybersecurity expertise.”
Companies would each seek the services of and prepare cybersecurity pros, but given the shortage in offered skilled staff, teaching has taken priority, claims Monthly bill Reynolds, exploration director at Foote Partners, a workforce research business. The common estimate to employ the service of a engineering employees, these as a entire-time developer, is about $32,000.
“They are absolutely doing both of those, but with the sizeable shortfall in the market for qualified cybersecurity gurus, the feeling I am acquiring by talking to hundreds of employers … is that they are focusing more suitable now on instruction and establishing expertise from inside of,” he suggests. “And it is not just technological abilities — they want a total sector basket of tender nontech skills [as well].”
Cybersecurity Techniques as Layoff Defense?
As economic downturn fears go on to roil the engineering field, on March 20 Amazon introduced its second tranche of layoffs — this time, setting up to reduce 9,000 company and technological know-how workers, bringing the complete amount of career impacted to 27,000. Cybersecurity vendors have not been spared, shedding countless numbers of employees in the last a few quarters, with some companies cutting much more than a quarter of their workforce, in accordance to tracking site Layoffs.fyi.
Cybersecurity takes the prime spot amid techniques chosen by employers for teaching applications. Resource: Pluralsight
Yet, general, employees with cybersecurity capabilities have mainly been secured from layoffs, because of to the relative problem in hiring or changing them. Only 10{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1} of C-level executives intend to lay off cybersecurity team, a great deal decreased than other departments, this kind of as human assets (30{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1}), finance (24{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1}), and even facts know-how (14{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1}).
As one more metric, two-thirds of tech executives have been questioned to lower prices, but 72{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1} however program to maximize investments in the enhancement of technology competencies, in accordance to Pluralsight’s “2023 State of Upskilling” report.
“When layoffs are on the table for an business, exactly where the cuts are made is highly individualized centered on enterprise will need,” Pluralsight’s Eimerman states. “Amid layoffs that have been accomplished in the tech market, handful of have targeted on technological innovation-specific roles.”
Cybersecurity as the Most-Wanted Tech Talent
Among engineering competencies, cybersecurity is most often in the best-3 expertise demanded by technologies leaders. General, if workforce experienced a weekly dash for discovering, 59{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1} of executives would want them to find out cybersecurity expertise, although 44{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1} chosen info-science abilities, and 42{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1} chosen cloud skill sets, according to Pluralsight’s report.
But learning such abilities has attained priority for staff members, too, who list their best motives for upskilling as wage expansion, personal growth, and position security.
Throughout the 53 noncertified cybersecurity abilities tracked by Foote Partners, the ordinary employee commands a 12.3{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1} base-income hard cash high quality. Skills these kinds of as security auditing, penetration testing, vulnerability scanning and management, DevSecOps, and cyberthreat intelligence all have sizeable premiums, Reynolds states.
Some combos of abilities are in even higher demand, these types of as cloud and cybersecurity, he says. With corporations targeted on shrinking their attack floor spot and placing a lot more security abilities into a extremely small footprint, for case in point, workers with cybersecurity, embedded OS, optimizing, and danger detection competencies jointly would garner even higher premiums.
“From a profession viewpoint, there is so a lot possibility for cybersecurity gurus,” he suggests.
Though a lack of time and spending plan has undermined upskilling endeavours in the past, employees have new incentives in the tighter employment current market: Just about fifty percent say that a using the services of freeze or pause has resulted in them accomplishing far more duties outdoors their job operate. In 2022, 60{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1} of employees cited “I’m much too fast paced” as the top barrier to getting new technological know-how capabilities, according to Pluralsight. In 2023, that quantity dropped to 42{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1}, though 30{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1} cited uncertainty in in which to aim their efforts as a major barrier.
Good morning! This is David, Tim’s researcher for The Cybersecurity 202. I’m anchoring today’s newsletter. (Yes, I am nervous). I also research The Technology 202 with Cristiano Lima. Send tips, scoops, exclusives and nut-free banana bread recipes to david.dimolfetta@washpost.com.
Reading this online? Sign up for The Cybersecurity 202 to get scoops and sharp analysis in your inbox each morning.
Below: A pair of senators re-up civilian cyber workforce legislation, and the number of zero-day exploits in 2022 reportedly drops. First:
Credit ratings increasingly looking at cybersecurity
U.S. companies face a wide array of issues potentially impacting their ability to borrow money. In recent months, a banking crisis and high interest rates have stretched some companies thin, leading to layoffs and decreases in spending.
At the same time, credit rating agencies, which assess companies’ ability to pay back borrowed money, are increasingly factoring in cybersecurity as part of their credit assessment criteria as they try to get a handle on the risks companies face.
Companies are dedicating more resources to protecting their assets because the potential risk that cyberattacks have against their credit is “real and significant,” said Scott Kessler, the global sector lead for technology, media and telecommunications at Third Bridge, an investment research firm.
Despite an uncertain global economic backdrop, Kessler consistently sees companies devoting resources toward cybersecurity.
“It’s almost a requirement now to have certain protections in place to ensure your valuable assets are safeguarded,” he said.
To be sure, cybersecurity is still a small piece of the puzzle for credit rating agencies, and boosting cyber defenses is not always the top issue on many corporate executives’ minds. But experts say that companies need to be focused on cybersecurity as they try to mitigate risks — and assure lenders that they’re doing so.
For companies that deal with any type of risk in their business model, what they do from a cyber policy and staffing standpoint is crucial to how attractive they are for investments and doing business, said Colby Stilson, a partner, portfolio manager and co-head of the global taxable fixed income team at Brown Advisory.
“If you have a breach, but you don’t have the right governance in place to avoid risk like that, there are very real monetary damages associated with that kind of event,” Stilson said. If an event is catastrophic enough, that may facilitate the downgrade of a company’s credit rating, he added. That has massive implications for the company’s cost of capital and investors in its bonds.
Despite a recent emphasis on cybersecurity by credit rating agencies, there’s no one-size-fits-all approach for an organization to earn a good rating through their cyber posture, experts told The Cybersecurity 202. That makes it difficult for ratings agencies and analysts to predict the credit outlook for organizations and governments as they brace for potentially destructive cyberattacks in a tense geopolitical situation, especially if they have smaller budgets.
Smaller entities are not investing as much in cybersecurity as their larger counterparts, said Lesley Ritter, a vice president and senior credit officer leading cyber risk for Moody’s Investors Service, a major credit ratings agency.
“Company size seems to be a very detailed driver to the level of investment in cybersecurity and the sophistication of the overall cyber governance structure,” she said.
Credit rating agencies also look at organizational issues and priorities, like whether a company has a chief information security officer who has a seat at the table during important discussions.
Complicating matters, the most significant sources of risk for cyber incidents are humans, said Gerry Glombicki, a senior director at Fitch Ratings’s insurance group.
To prevent a hack, a company can enable multi-factor authentication, give staff awareness training or buy anti-virus software, “but if you have the wrong person click on the wrong link, all of that stuff doesn’t matter,” he said.
Some companies’ credit ratings have suffered after major cyberattacks. But recent victims say that they’ve been able to bounce back by focusing on cybersecurity investments.
Equifax, whose credit outlook was downgraded by Moody’s in 2019 following its 2017 data breach, said the incident was a “catalyst for change” at the company. (U.S. prosecutors have accused Chinese military hackers of stealing the company’s data.)
And SolarWinds, which was hit by Russian hackers, rebounded in 2022 with a stable credit outlook. The investments in cyber after the incident “have enabled us to retain the vast majority of our customers while also returning to our historically high customer retention rates and strong public sector business,” a spokesperson said.
Staying ahead of geopolitics
The war in Ukraine isn’t significantly factoring into cyber-related credit ratings — for now, said Jon Bateman, a senior fellow in the Technology and International Affairs Program at the Carnegie Endowment for International Peace.
So far, cyber risks from Russia and Ukraine have not significantly materialized in the United States. That could change if the United States enters into a direct conflict with a country with significant cyber capabilities, like Russia or China.
Even then, there might be bigger problems at hand for U.S. businesses besides wanting a good credit rating, he said.
Sens. Jacky Rosen (D-Nev.) and Marsha Blackburn (R-Tenn.) introduced a pair of bills today that would create civilian cyber reserve pilot programs in the Defense Department and Department of Homeland Security, according to a release shared exclusively with The Cybersecurity 202.
The Civilian Cybersecurity Reserve Act would allow the agencies to recruit civilian cybersecurity personnel to serve in reserve capacities in the event that the United States needs to respond to large-scale malicious cyber incidents.
Participation in the programs would be voluntary and would not include Selected Reserve military members, the release notes.
A similar bill that passed in the Senate last Congress was introduced by Rosen with the support of Blackburn, but only directed the creation of a cyber reserve program in the Defense Department. The release for the new pair of bills does not mention any new cosponsors.
The news comes amid continued concerns over a growing gap in the U.S. cyber workforce. The Government Accountability Office in January said the federal government should work to address the shortage, calling it a risk to national security.
Greek authorities reportedly spied on and wiretapped Meta manager
The report, citing documents and people familiar with the matter, is “the first known case of an American citizen being targeted in a European Union country” with advanced surveillance technology, Stevis-Gridneff writes.
Artemis Seaford from 2020 to 2022 worked as a trust and safety manager at Meta and lived part-time in Greece. Her phone was hacked by Predator spyware for at least 2 months beginning in September 2021.
The spyware was manufactured in Athens, though the story notes the Greek government denied its use and had previously banned it.
“The Greek authorities and security services have at no time acquired or used the Predator surveillance software. To suggest otherwise is wrong,” government spokesman Giannis Oikonomou told the New York Times in an email. “The alleged use of this software by nongovernmental parties is under ongoing judicial investigation.”
Zero-day vulnerability exploits dipped in 2022, but were most linked to China
Researchers spotted fewer previously-unknown software vulnerabilities known as “zero-days” being exploited in 2022 than in 2021, though hackers linked to China continued to carry out the majority of the exploits, according to reports citing Google-owned Mandiant data.
Last year “was largely a story of consistency,” Mandiant principal analyst James Sadowski told CyberScoop’s Elias Groll.
Last year, zero-days were used against the three largest software vendors by market size: Apple, Microsoft and Alphabet, the parent company of Google, Matt Kapko from Cybersecurity Dive reports.
The cybersecurity market can leverage GPT-3 opportunity as a co-pilot to assist defeat attackers, according to Sophos.
The most recent report particulars projects made by Sophos X-Ops working with GPT-3’s big language types to simplify the research for malicious action in datasets from stability software, more properly filter spam, and speed up examination of “living off the land” binary (LOLBin) assaults.
“Since OpenAI unveiled ChatGPT again in November, the protection neighborhood has mostly focused on the possible dangers this new technological know-how could deliver. Can the AI enable wannabee attackers compose malware or aid cybercriminals write significantly much more convincing phishing e-mail? Probably, but, at Sophos, we’ve extensive viewed AI as an ally instead than an enemy for defenders, making it a cornerstone technological know-how for Sophos, and GPT-3 is no distinctive. The protection community need to be shelling out consideration not just to the probable pitfalls, but the possible chances GPT-3 brings,” explained Sean Gallagher, principal menace researcher, Sophos.
ChatGPT cybersecurity prospective
Sophos X-Ops researchers, which include SophosAI Principal Information Scientist Younghoo Lee, have been doing the job on a few prototype jobs that show the opportunity of GPT-3 as an assistant to cybersecurity defenders. All 3 use a procedure referred to as “few-shot learning” to prepare the AI design with just a few info samples, reducing the want to gather a huge quantity of pre-classified information.
The 1st application Sophos analyzed with the number of-shot mastering system was a purely natural language question interface for sifting as a result of malicious exercise in security software telemetry. Sophos tested the model versus its endpoint detection and response product or service. With this interface, defenders can filter by way of the telemetry with fundamental English commands, eliminating the need to have for defenders to comprehend SQL or a database’s fundamental composition.
GPT-3 can simplify selected labor-intensive procedures
Following, Sophos analyzed a new spam filter using ChatGPT and uncovered that, when in contrast to other device mastering versions for spam filtering, the filter using GPT-3 was significantly more precise.
Last but not least, Sophos researchers had been ready to generate a program to simplify the course of action for reverse-engineering the command traces of LOLBins. This kind of reverse-engineering is notoriously difficult, but also crucial for being familiar with LOLBins’ behavior—and putting a quit to these sorts of assaults in the upcoming.
“One of the rising considerations inside protection procedure facilities is the sheer total of ‘noise’ coming in. There are just too a lot of notifications and detections to form as a result of, and a lot of providers are working with constrained assets. We have proved that, with some thing like GPT-3, we can simplify particular labor-intense processes and give back again beneficial time to defenders. We are previously performing on incorporating some of the prototypes previously mentioned into our goods, and we have created the outcomes of our attempts out there on our GitHub for all those fascinated in testing GPT-3 in their have analysis environments. In the potential, we believe that GPT-3 may quite very well come to be a common co-pilot for security specialists,” reported Gallagher.