New gov’t cybersecurity strategy rolls out amid AI buzz, concerns it could be abused by criminals

New gov’t cybersecurity strategy rolls out amid AI buzz, concerns it could be abused by criminals

The Biden administration is shifting to carry out a new countrywide safety technique focused on halting hackers, as buzz about artificial intelligence applications raises issue between some specialists that criminals may possibly attempt to exploit AI abilities.

One particular goal of the administration system is to change the concentrate of blame away from the victims of cybercrime, U.S. stability officials mentioned. Soon after-the-point assessments usually concentrate on the focus on for currently being vulnerable adequate to hack — but if that target is a rural clinic, for instance, limitations could exists on what that clinic can do to shield against bad actors, particularly individuals backed by foreign governments.

As a substitute, the new program focuses on strengthening the general public-personal partnerships that inspire safety companies to share what they know about hacker networks in buy to convey them to justice.

Rising technological know-how will test the viability of the approach heading forward, experts informed ABC Information, specifically with AI posing new security issues.

The similar positive aspects witnessed in AI applications like ChatGPT from study lab OpenAI, which formulates human-like responses to issues posed by a person, are vulnerable to nefarious use, in accordance to Ari Jacoby, a tech govt who has targeted on working with AI to combat fraud.

A lot more: Possible hacking victims could be underprepared for threats from the shadows: Report

Specified the volumes of publicly obtainable details on software program engineering, hackers could use the chat bots to create or enrich destructive computer system code, Jacoby said.

According to OpenAI’s person coverage, applying ChatGPT to write malware, generate hateful or destructive content or interact in fraudulent action is explicitly prohibited. The problem is no matter if tech corporations are capable of enforcing these types of rules as AI engineering spreads.

“The ChatGPTs of the globe — who do way additional great than damage — make accessible resources that can write software package code in significantly less than a moment that would have taken a poor actor or a undesirable network most likely times or weeks to run,” Jacoby said.

As a substitute of using ChatGPT to supply tips for recipes or generate simple perform e-mail, terrible actors could try to compose significant volumes of phishing e-mail that trick recipients into downloading malware or supplying up own monetary details.

Alternatively, similar equipment applied to examine and evaluate trends in significant sets of knowledge can likely be employed to struggle fraud, Jacoby explained. Credit score card firms, for example, could reward from remaining capable to detect anomalies in a customer’s actions to ascertain if buys are reliable.

In the meantime, the U.S. is dealing with a every day onslaught of cybersecurity breaches from Russian, Chinese and North Korea-backed groups, according to recent U.S. government assessments and personal cyber intelligence firms. Experts assume those initiatives will exam the resilience of the administration’s new cyber tactic.
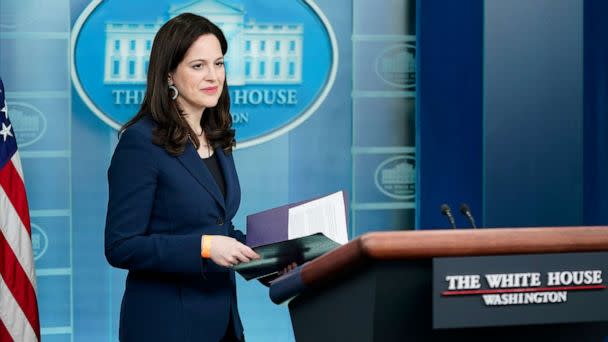
PHOTO: In this March 21, 2022 file photo Anne Neuberger, Deputy National Security Advisor for Cyber and Emerging Technology, arrives to speak at a press briefing at the White House in Washington. (Patrick Semansky/AP, FILE)

Photo: In this March 21, 2022 file photo Anne Neuberger, Deputy Nationwide Stability Advisor for Cyber and Emerging Know-how, arrives to communicate at a push briefing at the White House in Washington. (Patrick Semansky/AP, FILE)

“They are unbelievably complex and they are unbelievably properly-funded and nicely-tooled,” Jacoby explained. “They have a great deal of AI instruments at their disposal.”

A latest analysis of underground hacking communities by the cyber company Test Level Study observed on the net boards where by new approaches to hacking tools ended up reviewed, including a person discussion thread identified as “ChatGPT – Advantages of Malware.”

The author wrote they had been trying to use ChatGPT to recreate destructive computer code based on research papers about hacking.

Whilst the Biden administration’s tactic does not delve into the specifics of emerging technological innovation, these as AI, it truly is intended to be nimble enough to account for new developments in the promptly modifying cybersecurity landscape.

Additional: Cybersecurity industry experts split down a cyberattack as they become escalating menace

“These are multi-year initiatives where by we are going to uncover gaps and wherever Congress will then have to have to lean in to assistance us get to wherever we have to have to go,” acting National Cyber Director Kemba Walden stated at a forum dialogue of the strategy previous 7 days. “It’s a symphony, not a solitary movement.”

“This is an ongoing procedure,” she added.

Walden emphasized the significant position that cloud computing company providers play in securing data as a “pressure multiplier” for cyber threat first responders.

Google Cloud, for instance, delivers a wide variety of knowledge storage and internet site hosting providers. The company’s ability to defend its units was bolstered by its acquisition of the cybersecurity agency Mandiant past 12 months.

“Absolutely everyone has a shared duty below,” explained Stacy O’Mara, who leads govt tactic and partnership at Mandiant. “I believe that is the objective of the system — to strengthen this principle of a shared protection.”

“We’ve obtained a extended system in advance of us,” O’Mara claimed, ” but I’m encouraged by the administration’s initiatives.”

New gov’t cybersecurity tactic rolls out amid AI buzz, worries it could be abused by criminals initially appeared on abcnews.go.com

NIST launches cybersecurity community of interest for small businesses

NIST launches cybersecurity community of interest for small businesses

The Countrywide Institutes of Requirements and Technological innovation has introduced a new cybersecurity neighborhood of interest for small businesses across the United States.

Senior leaders at the Office of Commerce company on Monday declared the new system at an party at its Cybersecurity Centre of Excellence in Maryland.

The launch of the initiative arrives following the Biden administration last week issued a new National Cyber Strategy, which sought to “fundamentally reimagine” America’s cyber social deal, notably by shifting the duty for protecting the security of pc units away from individuals and smaller corporations on to more substantial software program makers.

The program is intended to foster larger collaboration in between NIST and small enterprises that the two offer and take in cybersecurity expert services. Senior officials say it is anticipated to assist strengthen the two-way sharing of details and very best methods that has fashioned a cornerstone of the Biden administration’s cybersecurity policy.

Deputy Secretary of Commerce Don Graves at the function underscored the value of NIST’s connection with the personal sector and its get the job done to provide business owners with distinct, actionable cybersecurity guidance.

“NIST’s modest small business local community of interest, which will not just contain but go outside of things to do that tumble below NCCoE’s cybersecurity connections energy, aims to improved reflect smaller companies’ requires – the passions and capabilities that they have – in all of NIST’s cybersecurity routines,” he reported.

Graves included: “So more compact businesses that take part in this effort and hard work will advise NIST’s selections about its wide portfolio of cybersecurity pursuits to ensure that they are as pertinent and powerful as ever. Yet again, functional methods – remedies that essentially get the job done for businesses, for communities all throughout the region. Irrespective of whether you’re below in Montgomery County, you’re in Idaho, you’re in rural Alaska … doesn’t seriously make any difference. They will support to make sure that NIST advice is equally significant and useful for the smaller organizations and other businesses to put into use.”

Through the function, NIST Performing Director Natalia Martin named on little businesses to use the new initiative to interact with the centre and reported it would acknowledge and be receptive to any input it gets.

“You have the option to make your voice heard, and we will constantly answer to you … please choose benefit of this opportunity,” Martin mentioned. “Every solitary venture we do, we inquire [the question]: What does this signify for small organization?”

NIST also in the course of the event celebrated the renewal of a collaborative partnership involving the agency’s Cybersecurity Middle of Excellence, the point out of Maryland and Montgomery County. It signifies the extension of a 3-way partnership that was very first signed when the heart was released in 2012, with the intention of aiding to speed up cybersecurity analysis and development even though guaranteeing nearby companies and communities advantage from connected innovation.

Cybersecurity Is Becoming A Priority For GCC Nations

Cybersecurity Is Becoming A Priority For GCC Nations

With world geopolitical instability elevating the threat of cyberattacks towards firms and governing administration organizations, the six nations of the GCC are quickly making much more sturdy and in depth cybersecurity procedures to answer to the evolving mother nature of cyberthreats.

In a January 2023 study of 117 world wide leaders from 32 international locations and 22 industries, 91{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1} of respondents considered that a considerably-reaching, catastrophic cyber-function was at minimum fairly probably in the subsequent two years, even though 43{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1} believed that a cyberattack would materially have an impact on their organisations. The findings were posted by the Environment Economic Forum (WEF) in its “Global Cybersecurity Outlook 2023”, created in collaboration with Accenture.

Cyber-resilience in the GCC

Because suffering from their to start with significant cyberattacks in the early 2010s, GCC countries have seemed at methods to bolster their cybersecurity by growing cyber-resilience and upgrading capability.

Having said that, Russia’s invasion of Ukraine in early 2022, which saw an enhance in the quantity and sophistication of global attacks, has prompted far more urgent action.

Some GCC international locations have now forged strong cybersecurity defences, according to the Portulans Institute’s “Network Readiness Index 2022”, which ranks nations around the world utilizing a host of metrics relevant to electronic transformation. In conditions of cybersecurity, Saudi Arabia rated 2nd globally behind the US, though the UAE rated eighth, Oman 28th, Qatar 34th, Bahrain 68th and Kuwait 73rd.

When these rankings suggest that the GCC is in a fairly potent situation, the typical price tag of cyberattacks is also higher in the area, with a knowledge breach costing $6.93m for every incident, previously mentioned the world wide common of $4.24m, in accordance to Mohamed Al Kuwaiti, running director of the Nationwide Info Centre below the UAE’s Supreme Council for National Security.

Al Kuwaiti designed this declare in December in Bahrain, which hosted the to start with Arab Intercontinental Cybersecurity Summit, a system for the world market to obtain entry to the region’s rising cybersecurity sector.

Presented the dimensions and scope of the challenge, the GCC has embraced political and technological cooperation. In October the GCC Ministerial Committee for Cybersecurity held its very first meeting in Riyadh at the headquarters of the GCC Secretariat Common, with the heads of cybersecurity from all 6 nations in attendance.

The meeting included issues of mutual desire and finished with programs to implement joint cybersecurity exercise routines to bolster the exchange of details and abilities and to produce the sector throughout the area.

Threats to electronic economies

The altering mother nature of cyberthreats is prompting a holistic reassessment of approach and techniques to cybersecurity. A key takeaway from the WEF’s outlook is that respondents imagine that cyberattacks are far more very likely to focus on producing business disruption and reputational damage likely forwards.

GCC nations have very long-time period strategies to diversify their economies absent from extractive industries in the direction of technological innovation and innovation and have already invested in a raft of technological advancements in synthetic intelligence (AI), facts and cloud computing. These options not only underscore the want for sturdy cybersecurity, but also need a a lot more holistic approach to guarding facts-driven networks.

“As info is more and more distributed in extensive networks, consumers are only as safe as their suppliers as a consequence, cybersecurity should put the focus on the integrity of the community, which requires each cybersecurity corporations and regulators to build mechanisms that allow for for the safety of info on the aspect of customers, distributors and partners,” Mirza Asrar Baig, CEO and founder of CTM360, a Bahraini digital possibility-protection enterprise, instructed OBG.

Meanwhile, momentum to expand the GCC’s intercontinental achieve in cybersecurity and ICT continues apace.

In November 2022 Saudi Arabia’s Nationwide Cybersecurity Authority (NCA) hosted the Global Cybersecurity Forum – initially held in 2020 – to deal with the macroeconomic, geopolitical and strategic issues shaping world cybersecurity.

Very last 12 months the NCA introduced the Countrywide Portal for Cyber Security Companies (HASEEN), a system that aims to create and control cyber-companies, guidance interaction mechanisms and boost cybersecurity capacities. All government businesses have entry to HASEEN, which the NCA options to use to conduct 7000 cybersecurity assessments in 2023.

In October Dubai’s Gitex International 2022 introduced collectively 10,000 programmers and builders from many intercontinental know-how businesses including US tech big Microsoft and 26 of its partners, which launched a slew of new systems for cloud computing, combined-actuality activities, AI and cybersecurity.

Last thirty day period, Saudi Arabia’s Ministry of Communications and Facts Engineering also held the next annual LEAP tech meeting, which developed a host of partnerships and about $16bn in expense, in line with Saudi Eyesight 2030 digitalisation aims.

“There is possible in the area to switch the area landscape, which is dominated by systems integrators, into a single with IT businesses driven by regional expertise and developing proprietary alternatives with a worldwide achieve, in cybersecurity and other areas,” Baig explained to OBG. “One of the key difficulties in recruiting IT professionals in the region is acquiring these keen to establish new alternatives from the ground up and who fully grasp that regional talent can produce innovation, relatively than replicating types applied elsewhere.”

Area potential building

Ambitions to bolster cybersecurity in the GCC will involve schooling initiatives to create neighborhood human ability.

In August 2022 the NCA released the CyberIC programme to develop countrywide capabilities and localise technological know-how enhancement in cybersecurity. The programme is slated to boost the number cybersecurity begin-ups by aiding much more than 60 countrywide companies, 40 by the cybersecurity accelerator programme and 20 via the cybersecurity obstacle.

Before final 12 months Saudi Arabia also set up Wamda, an initiative to foster the leadership competencies of female Saudi cybersecurity professionals.

In the meantime, Dubai Cyber Innovation Park held its 2nd Cybersecurity Bootcamp in February 2023 to train a specialised and qualified cybersecurity workforce from a pool of new graduates and other people looking to create a job in the discipline.

Bahrain’s labour fund Tamkeen is next match by graduating the initially cohort from its 8-thirty day period Cyber Security Teaching Programme conducted in partnership with SANS Institute, a cybersecurity teaching and education and learning service provider. Graduates are envisioned to deal with the needs of govt organisations and personal sector providers at the community and global level.

By Oxford Small business Group

Far more Leading Reads From Oilprice.com:

School cybersecurity expert weighs in: What’s happening in Minneapolis?

School cybersecurity expert weighs in: What’s happening in Minneapolis?

Minneapolis Public University college students and personnel returned to lecture rooms on Monday this 7 days, but disruptions prompted by an “encryption virus” —  including losing obtain to district accounts, units and shutting down just after-college routines —  ongoing throughout a lot of the week. 

“I assume the district is striving incredibly challenging not to flat-out say that they’ve seasoned a ransomware incident… But this has all the hallmarks of people types of incidents and that’s what I would take into account it to be,” stated Doug Levin, countrywide director of the K12 Stability Details Exchange and an professional on school cybersecurity.

Cybersecurity is becoming an progressively well known concern for public university districts.

In September of previous calendar year, the country’s next-greatest district was qualified. In accordance to Levin, there have been close to 200 comparable incidents focusing on both huge and smaller districts all over the state in the very last a few several years — and the ransom demanded has grown from $5-$10 thousand to nearer to $1 million or far more. 

What does that signify? The information, examination and local community conversation uncovered right here is funded by donations from persons. Make a gift of any total now to aid this useful resource for all people.

“(This is) affecting college districts from coast to coastline — from some of the greatest school districts in the country to considerably more compact and more rural faculty districts,” Levin reported. “I do believe that these incidents are going on additional frequently than people notice.” 

The Minneapolis district has moved from saying on Monday this 7 days that it’s discovered “no evidence” that personalized data was compromised, to emailing people that “an unauthorized menace actor might have been in a position to entry specific facts positioned inside of the MPS natural environment.”  

Here’s what Levin thinks you need to have to know about what is occurring in Minneapolis: What is a ransomware assault? 

A ransomware attack is carried out virtually completely by felony gangs functioning overseas, largely in Russia, according to Levin. 

The groups obtain accessibility to a pc method and make it unusable and then demand a payment from their victims.

Why is the Minneapolis college district not calling this a ransomware assault or currently being much more forthright? 

The Minneapolis faculty district has denied MPR News requests for interviews on the ongoing incident. In accordance to Levin, there could be several distinctive challenges at stake.

First, most states do not have reporting demands when it will come to what college districts are obligated to do when they knowledge a cyber attack. Most states also lack any kind of cybersecurity standard that university districts are demanded to adhere to.

Levin also posits the Minneapolis district may possibly be having suggestions from insurance policy suppliers or lawyers who are telling them they can restrict their liability if they stay away from making use of certain words and phrases in community communications. 

What really should families, pupils and workforce do to defend them selves? 

Levin implies people today linked to the district improve their passwords — particularly if they are reusing them on many accounts — help two-issue authentication, and preserve a closer eye on e mail, social media and financial accounts.

Dad and mom should freeze their minors’ credit rating accounts to stop identification theft (The Minneapolis district is directing persons to report major fraud or freeze credit by credit rating reporting bureaus this kind of as Equifax, Experian and TransUnion) . 

“Presume that information has been breached by felony actors,” Levin stated. “Take methods to guard your identity.” 

What ought to the Minneapolis General public Faculty district do likely ahead? 

Levin claimed it’s attainable the district will carry on to practical experience cyber assaults. 

“Unfortunately, a faculty method that on their own are victims of cybersecurity attacks like this a single are essentially rather most likely to practical experience repeat assaults likely ahead,” Levin said. 

He also implies families and employees question their board and district leaders to make guaranteed there is a devoted budget for cyber protection, and a strategy in location to handle cyber attacks when they happen. 

“What I would recommend for dad and mom… make absolutely sure that the university board and superintendent are making sure that the college system will take cybersecurity dangers just as very seriously as they choose pitfalls of physical violence on the university campus,” Levin stated. 

Do other Minnesota districts need to have to be concerned? 

Cyber assaults are becoming increasingly common, and have the probable to actually halt faculty programming and shut down devices. 

“At this position, offered the facts that we’ve noticed, it can be truly only a make a difference of time just before you know any individual school technique is a victim,” Levin explained. “We’ve viewed attacks in, you know, some of the major university districts from, you know, state to state to point out, as well, as lots of little ones.”

Levin factors college leaders to a the latest federal report on cyber safety threats to educational institutions, but also states districts may perhaps need help from condition and federal resources. 

“This is a escalating national disaster,” Levin stated. “While there are absolutely matters that we should and can hope superintendents and university boards to do, in the long run we’re going to have to have far more support from the condition and federal governing administration.”

U.S. Cybersecurity Agency Raises Alarm Over Royal Ransomware’s Deadly Capabilities

U.S. Cybersecurity Agency Raises Alarm Over Royal Ransomware’s Deadly Capabilities

Mar 03, 2023Ravie LakshmananEndpoint Security / Ransomware

U.S. Cybersecurity Agency Raises Alarm Over Royal Ransomware’s Deadly Capabilities

The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has unveiled a new advisory about Royal ransomware, which emerged in the threat landscape past calendar year.

“Just after attaining accessibility to victims’ networks, Royal actors disable antivirus program and exfiltrate substantial amounts of details prior to eventually deploying the ransomware and encrypting the systems,” CISA mentioned.

The tailor made ransomware plan, which has qualified U.S. and worldwide organizations since September 2022, is considered to have evolved from previously iterations that had been dubbed Zeon.

What is actually additional, it’s mentioned to be operated by seasoned menace actors who utilised to be component of Conti Crew One particular, cybersecurity corporation Trend Micro disclosed in December 2022.

The ransomware team employs connect with again phishing as a indicates of offering their ransomware to victims, a approach broadly adopted by criminal teams that splintered from the Conti company previous calendar year next its shutdown.

Other modes of first access consist of remote desktop protocol (RDP), exploitation of public-dealing with applications, and by means of preliminary entry brokers (IABs).

Ransom calls for built by Royal change from $1 million to $11 million, with assaults focusing on a variety of essential sectors, together with communications, instruction, healthcare, and manufacturing.

“Royal ransomware employs a exclusive partial encryption technique that will allow the menace actor to opt for a certain share of information in a file to encrypt,” CISA famous. “This method will allow the actor to decrease the encryption percentage for more substantial documents, which can help evade detection.”

The cybersecurity company mentioned many command-and-handle (C2) servers related with Qakbot have been used in Royal ransomware intrusions, despite the fact that it can be now undetermined if the malware exclusively depends on Qakbot infrastructure.

The intrusions are also characterised by the use of Cobalt Strike and PsExec for lateral movement as nicely as deleting shadow copies to prevent program recovery. Cobalt Strike is also repurposed for info aggregation and exfiltration.

As of February 2023, Royal ransomware is able of focusing on both of those Home windows and Linux environments. It has been connected to 19 assaults in the thirty day period of January 2023 on your own, putting it at the rear of LockBit, ALPHV, and Vice Modern society.

Uncovered this article interesting? Observe us on Twitter and LinkedIn to examine extra distinctive information we write-up.

CISOs Share Their 3 Top Challenges for Cybersecurity Management

CISOs Share Their 3 Top Challenges for Cybersecurity Management

Taking care of possibility on a world-wide scale has usually been challenging, but in the aftermath of the COVID pandemic, CISOs have had to turn out to be even more agile. The shift to hybrid get the job done, the speedy deployment of cloud applications, and the go to ongoing integration and ongoing improvement (CI/CD) have emboldened menace actors with new and broader targets.

In the meantime, the range of devices and endpoints on organizations’ networks have amplified exponentially. Two veteran CISOs lamented the worries these alterations have imposed through a webinar last week organized by Sepio, an asset detection and hazard administration startup. Sepio’s CISO Ilan Kaplan moderated an hour-extensive dialogue with HSBC CISO Monique Shivanandan and Carl Froggett, who was CISO at Citi for 17 yrs just before becoming a member of startup Deep Intuition previous summer as CIO.

Shivanandan and Froggett shared with Kaplan what they see as a few of the most major problems the rapidly shifting cybersecurity and threat landscape provides.

1. Maintaining Visibility of All Network Assets

Cybersecurity experts have traditionally struggled to obtain complete visibility into what’s on their networks and threats directed at them. Froggett noted that more recent cloud-indigenous technologies, this kind of as container-primarily based apps and SaaS, offer far better visibility than conventional program since modern applications were being designed to be additional safe.

But overshadowing that profit is the sheer scale of all the elements linked with fashionable programs. “An asset employed to endure 5, 6, 7 years, or for a longer time if you incorporate the fundamental operating techniques, whereas now the lifetime of the container can be calculated in seconds or possibly minutes,” Froggett said. That results in “a full new set of [visibility] troubles from that perspective.”

Shivanandan mentioned that common techniques of capturing inventories, trying to keep them up to day, and monitoring them ended up predicated on the notion of incorporating belongings to a community manually. But with modern-day purposes, that isn’t going to get the job done, she explained, mainly because of the scale and the pace by which units and software program are deployed. “1 of the most important issues that every CIO and each and every CISO faces is having that visibility and creating guaranteed that visibility is up to date,” Shivanandan mentioned.

2. Staying away from New Threats When Introducing Apps

Other than addressing the mounds of present regulatory dangers and the recent menace landscape, protection groups must also keep away from getting the source of new threats. Asked how they make certain that, Shivanandan said that, whilst examining the resource code of each individual element additional to the infrastructure is not possible, HSBC has demanding processes about onboarding a new technology, which contains “a whole lot of pen testing and red teaming.”

“Regrettably, with the quantity of get-togethers we have, we simply cannot do it for everyone,” she added. “We do it for a decide on couple of.” The challenge is “just about every software change and just about every new release can knowingly or unknowingly introduce one thing new. It really is a frequent struggle that we are struggling with.”

Froggett said that Citi has rigid processes around onboarding new know-how, together with pen testing and purple teaming, but with the current release cadences, enforcement has develop into challenging. “Finally, you are unable to ordinarily do source code evaluations” of every thing that will come in, he mentioned.

3. Recruiting and Retaining Proficient Talent

The shortage of skilled cybersecurity specialists is practically nothing new, but Shivanandan claimed it stays 1 of her major problems. “All the engineering in the planet is only as superior as the folks there to make positive that we install [everything] accurately and preserve it up to date,” she said.

Shivanandan stated despite considerable progress, it continues to be complicated for women to crack the glass ceiling. She believes men have an outsized existence in senior cybersecurity roles compared to the overall IT field.

“When you commence out at the decrease stages, you will find [an] equal [proportion of] males and ladies, 50-50, at times even 60-40 ladies,” she explained. “Then, as you go through the progression, the girls fall out, and the adult men continue to progress from a seniority degree.”

However, Shivanandan stated girls encounter less boundaries these days compared with when she started out. She reported, “When I was starting up out, they wished to pat you on the head and say, ‘dear, do not get worried your very little head, I will choose care of technical issues.’ But not anymore. There’s no ceiling for a woman to get into any situation now. It can be a make any difference of just perseverance.”

Shivanandan considers herself fortuitous at HSBC, in which 40{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1} of her management team is women. “The females and the males are both of those superb, and which is the issue that you seriously want to glimpse for,” she explained.

Froggett claimed for the duration of his just about 25 many years at Citi, most of his bosses were females. “The job’s not performed for positive, but there is undoubtedly a lot more of a balance [of men and women in senior leadership roles than] I saw 5 or 10 several years back.”

Shivanandan emphasized that developing a numerous staff goes past gender. A big part of her staff has some type of neurodiversity, she reported. According to analysis, an estimated 15{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1}-20{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1} of people today have some variety of neurodivergence this kind of as autism, notice deficit hyperactivity problem (ADHD), mental well being circumstances, or studying disabilities.

Shivanandan reported these conditions are generally belongings: “Which is what will make them fantastic in the position.” But she added, “I imagine that’s most likely more durable to overcome from a vocation development standpoint, from a leadership vs . a specialized perspective.”