Cyber security expert surprised by lack of public charging port safety awareness

Cyber security expert surprised by lack of public charging port safety awareness
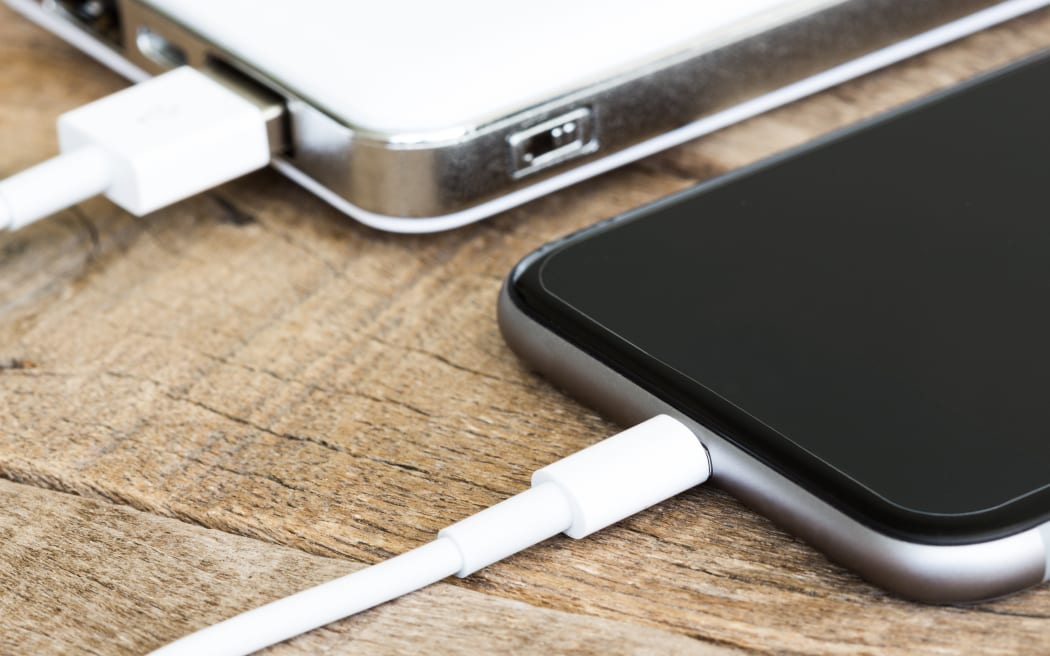
closeup phone charging white power bank portable devie

The potential risks of plugging gadgets into open up charging ports have been recognized for some time, but general public consciousness may well stay restricted.
Image: 123rf

A cyber stability qualified says he is amazed by how several persons in New Zealand keep on being unaware of potential risks posed by plugging telephones into USB chargers in community spaces.

Public charging stations are conveniently dotted around the outlets, airports and inns throughout the country.

Nevertheless, a new tweet by the the Federal Bureau of Details (FBI) warning the US community to prevent utilizing these because of to the risk of hacking. It has also served to remind New Zealanders of the hazards of utilizing community charging ports.

The FBI claimed “poor actors” experienced located ways to use these to introduce malware and monitoring application on to equipment.

Cyber security company Cert NZ has echoed the warnings. Menace and incident reaction team supervisor Jordan Heerspring told Checkpoint men and women ought to not to plug telephones and laptops instantly into people public USB charging ports.

“You really should be bringing your personal charging product, which you can plug into a wall socket, and then use that to charge your units,” he explained.

“In the airports you can expect to see community charging stations, some motels will have them even in the rooms. Some buses if they are pleasant extravagant buses, and even some planes will have them. So all of them are most secure to prevent, if you can.”

Heerspring explained it was not a significantly nicely-publicised piece of assistance, even if prolonged-standing.

“If I am remaining entirely trustworthy, I thought this was pretty community understanding. But talking to mates and spouse and children lately, I have found out that there are a whole lot of people who are not mindful of this. I am pretty happy that there is been some dialogue going all-around and raising that recognition for individuals.”

He suspected the FBI warning mirrored an maximize in cyber attacks involving charging ports in the US.

Even so, the fact was most ports had been in all probability good to use in New Zealand, Heerspring reported.

“We will not see a large amount of these attacks, but they’re genuinely simple points to retain you protected from, our advices is it is really ideal to stay clear of them.”

Hackers have devised ways to infiltrate the bits of application and components guiding the charging stations, so that an attacker can likely these use to load possibly destructive program onto equipment, or they can use that to extract details straight from units, he claimed.

“With the two of all those strategies, they’re going to be ready to extract own or other delicate or fiscal data from your machine if they are exploiting that distinct charging station.”

Cyber prison could accessibility the information and facts remotely, or may well have to return to the charging port, relying on the malware utilised, he claimed.

“It truly is type of like creating a street to the enemy camp. You can nonetheless have your gates up, so you will find continue to some safety measures that they will have to bypass, but giving them their accessibility invites them to do that.”

Being aware of your phone has been compromised is at times tricky, but there are some symptoms to look out for.

“There’s a handful of items that are truly worth wanting further into, like if your cellular phone is working very little by little, noticeably a lot more so than standard. Or if you get diverse apps or windows popping up that you really don’t assume or have not informed the product to do. Which is well worth getting investigated,” he claimed.

One more piece of essential suggestions was in no way plug a USB unit into your cell phone or laptop if you did not know its resource.

“If you obtain a USB unit, a tiny USB vital or get presented one – specifically if you will not absolutely believe in that human being – you shouldn’t be placing that into your own laptops or phones or other devices at household,” he explained.

“Additional generically, hold two-variable authentication on your accounts and have excellent password hygiene and those people a few items, along with retaining your gadgets updated, so patching to the most recent versions, will maintain you safeguarded from the bulk of the attacks out there.”

Federal panel says agencies need to focus on harmonizing cyber regulations

Federal panel says agencies need to focus on harmonizing cyber regulations

Comment

Welcome to The Cybersecurity 202! Why am I obsessed with eating mass-manufactured cherry pies and orange cupcakes of late? (I won’t name the brand.) It’s unhealthy and I get grossed out right after doing it, then, bam, next day, I’m ready for more of them.

Reading this online? Sign up for The Cybersecurity 202 to get scoops and sharp analysis in your inbox each morning.

Below: The Defense Department says it secured a previously exposed server that leaked sensitive military emails, and gaming giant Activision falls victim to a phishing scheme. First: 

An advisory committee recommended the creation of an office to deconflict cyber rules

The Biden administration needs to take numerous steps to deconflict and organize the proliferation of cybersecurity regulations, according to a report that a presidential advisory committee approved Tuesday.

That includes things like creating an office within the Cybersecurity and Infrastructure Security Agency to harmonize cybersecurity rules across the federal government, or directing a trio of federal agencies to coordinate with foreign governments to develop consensus cybersecurity standards.

The recommendations arrive as the U.S. cyber scene awaits publication of the Biden administration’s national cybersecurity strategy, the White House pushes for mandates on numerous industries, and CISA writes a rule to require critical infrastructure owners and operators to report major cyber incidents to the agency.

The advisory panel, named the National Security Telecommunications Advisory Committee (NSTAC), voted Tuesday to send the report to Biden for his consideration.

The committee draws its membership from the business community, with a heavy emphasis on cybersecurity companies. Many industry groups have indicated opposition to the Biden administration pushing a more muscular federal role for cyber mandates.

But an official with the Office of the National Cyber Director, which led the writing of the national cybersecurity strategy, saw overlap between that strategy and the NSTAC report.

“The recommendations regarding regulatory harmonization align very well with the strategic goals of the strategy,” said Rob Knake, the acting principal deputy at the cyber director’s office.

One such recommendation is for CISA to establish an Office of Cybersecurity Regulatory Harmonization. There are already some federal initiatives with a similar mission, such as the Cyber Incident Reporting Council, and the Cybersecurity Forum for Independent and Executive Branch Regulators. But the new office would have the job of building expertise on cybersecurity regulation and assisting other federal agencies during the cybersecurity rulemaking process.

The report recommended housing the office in CISA for a few reasons, as incoming NSTAC chair Scott Charney, vice president for security policy at Microsoft, explained:

  • “The primary advantage of housing this effort in CISA is that most other departments, such as Treasury or [Health and Human Services], are primarily concerned” with the industries they regulate, Charney said. “By contrast, CISA’s focus on protecting critical infrastructures gives it a broader, cross-vertical perspective.”
  • “The proposed office would act in an advisory capacity to other regulators,” Charney said, “which is consistent with CISA’s existing interactions with regulators.”
  • Furthermore, he said, CISA’s parent agency, the Department of Homeland Security, is home to the aforementioned Cyber Incident Reporting Council. That council was formed as part of legislation Congress passed last year that directed CISA to write a rule requiring critical infrastructure owners and operators to report major cyberattacks within 72 hours.

Agencies writing cyber rules would have to report how their regulations align with the new office’s guidelines. 

Separate from the recommendations about the new office and how agencies would interact with it, the report calls on agencies to review their rules at least every five years and update them as needed. 

And “the Department of State and Department of Commerce, in coordination with the Department of Homeland Security, shall develop and execute a strategy to encourage more foreign government participation in the development and adoption of specific consensus standards,” the report states.

Recommendations that aren’t about harmonization

The report isn’t only about harmonizing regulations.

Among its other recommendations:

  • CISA and the General Services Administration should “draft core, universally applicable procurement language that clearly defines the government’s requirements and preferences” on secure software and services.
  • CISA should expand and enhance a federal program focused on scanning and monitoring services to help federal agencies better protect their networks.
  • CISA and the National Institute of Standards and Technology should form a partnership “focusing on transition to post quantum cryptography” — in other words, making computers safe against quantum computers that could break current encryption.

Private U.S. military emails were exposed online

The Defense Department on Monday afternoon said it secured a server that was left online without a password for two weeks, exposing internal military emails to anyone on the internet, TechCrunch’s Zack Whittaker reports.

The server, which was left without a password due to a misconfiguration, was hosted on Microsoft’s Azure government cloud for Defense Department customers. That platform is typically used to share sensitive but unclassified government data, but in this case it stored about three terabytes of internal military emails, including those related to the U.S. Special Operations Command. 

Anurag Sen, a security researcher who discovered the breach, said the exposed server contained military emails dating back years, with at least one file in particular including a completed SF-86 questionnaire full of highly sensitive personal and health information. 

The server is now inaccessible. U.S. Special Operations Command spokesperson Ken McGraw said in an email to TechCrunch on Tuesday that an investigation into the leak began Monday and is still underway.

“We can confirm at this point is no one hacked U.S. Special Operations Command’s information systems,” McGraw said. It’s not clear if anyone besides Sen found the server during the two weeks that it was exposed.

Supreme Court knocks down Wikipedia operator’s bid to challenge NSA oversight

The Supreme Court on Tuesday denied a request from the operator of Wikipedia to reopen a lawsuit against the National Security Agency challenging broad internet surveillance, Reuters’s Andrew Chung reports.

In 2015, the Wikimedia Foundation, represented by the American Civil Liberties Union, sought to confront the legality of NSA’s “upstream” program used to surveil foreign targets through the collection and searching of internet traffic on data transmission lines flowing into and out of the United States. The lawsuit alleges that the practice violates Americans’ right to privacy and freedom of speech.

The NSA has defended the surveillance by pointing to the Foreign Intelligence Surveillance Act of 2008. Its existence was leaked in 2013 by former NSA contractor Edward Snowden, who later fled to Russia. 

Tuesday’s decision upholds a lower court’s previous dismissal of the lawsuit because of the state secrets privilege, or a legal doctrine that can shut down litigation if disclosure of certain information, like details about the surveillance, would damage national security. 

Hacker gains access to Activision Slack, steals Call of Duty info

A hacker was able to breach a Slack channel of the game publishing giant Activision after convincing an employee to give them a two-factor authentication token, Motherboard’s Joseph Cox reports.

After the breach, the bad actor posted offensive messages from the targeted staff account and apparently stole information related to upcoming Call of Duty release dates, according to screenshots posted online by the cybersecurity collective vx-underground. 

Activision told Motherboard in a statement: “The security of our data is paramount, and we have comprehensive information security protocols in place to ensure its confidentiality. On Dec. 4, 2022, our information security team swiftly addressed an SMS phishing attempt and quickly resolved it.”

“Following a thorough investigation, we determined that no sensitive employee data, game code, or player data was accessed,” the statement added. Activision did not respond when asked specifically by Motherboard about the data that the hacker seemingly did access, such as the Call of Duty scheduling. 

The attack comes as the gaming sector is increasingly facing cyberthreats, with the industry seeing a 167 percent increase in web application attacks in 2021, and last year becoming the most targeted industry for distributed denial of service (DDoS) attacks. Last month, hackers broke into Riot Games, another gaming giant. In 2021, hackers breached Electronic Arts and CD Projekt.

White House mulls scaling up Login-dot-gov to reach every American (Federal Computer Week)

House Dems call for info on racially-motivated cyberattacks (NextGov)

Tor Project moves away from infrastructure ran by internet monitoring firm (Motherboard)

Hackers extort less money, are laid off as new tactics thwart more ransomware attacks (Wall Street Journal)

Ukraine’s volunteer cyber army could be model for other nations, experts say (Newsweek)

Hackers scored corporate giants’ logins for Asian data centers (Bloomberg News)

Civil liberties groups call for EU-wide ban on spyware (The Record)

Ukraine’s largest charity wants to raise $1.3 million for ‘cyber offensive’ (The Record)

  • The Atlantic Council holds a discussion with the authors of two new reports on Russian narratives to justify the war in Ukraine today at 9 a.m. 
  • The R Street Institute holds a webinar on the state of cybersecurity careers for Black professionals on Thursday at noon.
  • Former U.S. national security adviser John Bolton will join The Washington Post for a conversation about the war in Ukraine and rising tensions with China on Friday at 11 a.m. 

Thanks for reading. See you tomorrow.

IT services industry looks to cyber, cloud consulting for growth

IT services industry looks to cyber, cloud consulting for growth
&#13

Economic alerts stage to a difficult IT expert services environment in 2023. But latest sector moves propose cloud consulting and cybersecurity solutions might confirm active marketplaces.

Gartner final week trimmed its 2023 outlook for the IT providers market from the 7.9{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1} calendar year-around-year growth the marketplace study business forecast in Oct 2022 to its present projection of 5.5{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1}. John-David Lovelock, an analyst at Gartner, stated the up-to-date outlook demonstrates a slowdown in company investing. But he observed IT budgets go on to grow and are expected to do so at a better price than past year’s 3{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1} uptick.

Inflation, meanwhile, remains a macroeconomic component and continues to floor in IT commodities. Fears about a economic downturn persist as primary engineering businesses shrink their workforces, with Microsoft and Google last 7 days disclosing designs to lay off thousands of staff members.

Towards that backdrop, some IT companies businesses are expanding their organizations and including companies:

  • Logically, a providers company centered in Portland, Maine, stated final 7 days it will increase its target this calendar year on cybersecurity as it goes to sector as a managed protection companies company (MSSP). Logically has promoted Joshua Skeens, the company’s COO with a cybersecurity background, to lead the organization as CEO.
  • Aptum Team, a cloud managed providers company in Toronto, earlier this month acquired CloudOps Inc., a transaction that will develop the company’s multi-cloud and DevOps providers
  • Thirdera, a consulting company with headquarters in Broomfield, Colo., earlier this month agreed to acquire SilverStorm Options, growing Thirdera’s ServiceNow products and services company in Europe and boosting its workforce to practically 1,000 staff members.

Logically moves ahead as MSSP

Logically, which has constructed a security company around the a long time via acquisitions and organic development, is now generating cyber its prime emphasis.

Joshua Skeens, CEO, LogicallyJoshua Skeens

“Usually, Logically has been an MSP in this area,” Skeens claimed. “With my background and other key strategic hires we have manufactured, we are hunting to travel Logically forward in 2023 as an MSSP.”

Skeens joined Logically in 2021 via the company’s acquisition of Cerdant, an MSSP the place Skeens was COO and CTO.

Logically will manage the MSP facet of its functions, but it aims to completely transform into a “pretty stability-focused enterprise,” Skeens reported. The company’s purpose is guaranteeing more than half of its recurring income arrives from cybersecurity products and services in the upcoming two years, he observed. Logically will present cybersecurity expert services to buyers ranging from SMBs to huge enterprises.

Investigate from Canalys, a market place analyst organization based mostly in Singapore, suggests Logically is transferring in the appropriate course. The corporation forecasted cybersecurity solutions to expand at a 14.1{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1} clip in 2023 — well ahead of the advancement fee for the IT assistance sector in general. Canalys stated the industry for cybersecurity solutions, which incorporates consulting, outsourcing, deployment, integration, maintenance and managed products and services, will reach $144.3 billion globally in 2023.

“Cybersecurity solutions is growing more rapidly than other parts in IT solutions due to heightened danger ranges and the require for businesses to elevate their cybersecurity posture,” mentioned Srikara Upadhyaya, an analyst at Canalys.

He mentioned cybersecurity managed providers has turn out to be a critical expansion place. Current market motorists include the lack of skilled men and women, the greater complexity of controlling cybersecurity in home, and the have to have to deploy safety operations heart (SOC)-centered detection and reaction abilities.

“As a result, channel partners are investing in setting up up their cybersecurity managed services, possibly investing in their own SOCs or reselling MDR [managed detection and response] kind companies from third-get together providers,” Upadhyaya additional.

Logically’s MSSP choices incorporate extended detection and reaction, endpoint detection and reaction, and MDR business-level managed firewall companies and cybersecurity assessments, according to Skeens. The company operates a SOC. The company’s IT security engineering associates include things like Sonic Wall, Fortinet, SentinelOne, Extreme, Seceon and Blackberry’s Cylance business.

Aptum expands multicloud, DevOps products and services

The cloud consulting enterprise is a different IT solutions discipline that has been keeping up properly despite the economy.

Susan Bowen, CEO and president, Aptum GroupSusan Bowen

Aptum’s acquire of CloudOps Inc., centered in Montréal, aims to broaden the firm’s hybrid multicloud providers. These kinds of acquisitions aid the enterprise speedy track its growth system, mentioned Susan Bowen, CEO and president at Aptum Group. The enterprise balances M&A with retaining a pipeline of expertise, investing in schooling, certifications and retention techniques, she included.

Clients carry on to faucet assistance suppliers for cloud guidance, even in a hard financial system, as they appear to harmonize the multitude of as-a-services offerings they have deployed because COVID-19.

“In modern a long time, several firms accelerated their ideas to put into action the cloud,” Bowen mentioned.

But a lot of businesses realized they have a lot to study, building an opening for MSPs. Supporting consumers handle multicloud issues, these kinds of as integration, is a single this kind of prospect.

“The truth is that most organizations — unless of course they are solely cloud indigenous — are being forced to use a lot more than 1 cloud,” Bowen stated. The CloudOps Inc. transaction puts Aptum in a posture to solve hybrid multicloud difficulties much more correctly than prospects could manage on their have.

M&As will spark the want for linkages amid disparate clouds.

“As markets commoditize as a end result of M&A, even more integration tasks are wanted to permit multicloud solutions” to co-exist, Bowen claimed.

The CloudOps Inc. deal also seeks to enhance Aptum’s DevOps expert services. Aptum experienced previously been partnering with CloudOps Inc. for its managed DevOps presenting prior to the offer. Managed DevOps expert services enable a customer’s in-dwelling software developers concentrate on innovation even though the services provider manages and maintains the customer’s DevOps ecosystem, Bowen reported.

Thirdera grows European ServiceNow footprint

Thirdera’s agreement to buy SilverStorm is its sixth deal in the last two decades. SilverStorm presents Thirdera a bigger European existence, with headquarters in Spain and an office environment in the United Kingdom.

Jason Wojahn, CEO of ThirderaJason Wojahn

“We acknowledged we require to be world wide and want to be scaled and have to have to be complete throughout ServiceNow’s platforms,” stated Jason Wojahn, CEO of Thirdera.

Organic and natural expansion is also part of Thirdera’s system, possessing previously this year hired a number of ServiceNow authorities in the Netherlands.

European prospects, and individuals elsewhere, are on the lookout to get the most out of their preceding investments in digital systems, possessing promptly adopted these kinds of choices following the onset of COVID-19, Wojahn mentioned. Fears relating to the prospective for a recession have also brought about companies to concentration on optimization and efficiency.

“After any important electronic transformation, there tends to be a interval of incremental change — continuous advancement and refinement — to get even further efficiencies” he mentioned. “As very well, the place macroeconomic problems exist, there tends to be a concentration on garnering related incremental, continuous advancement efficiencies.”

Thirdera is effective with buyers to identify opportunities for approach advancement inside their ServiceNow deployments and associated workflows. Constant advancement methodologies enable with this activity, Wojahn observed. In addition, data-centered techniques utilizing forensics applications like Celonis can also enable discover constraints and bottlenecks, he additional.

The objective: assess how companies use ServiceNow today and how they can re-envision the long term. Acquiring to that to-be atmosphere in the recent overall economy, nevertheless, phone calls for a pragmatic method, Wojahn recommended.

Certainly, some organizations are breaking down digital transformation initiatives into more compact chunks to mitigate risk. But in undertaking so, corporations have to have not get rid of sight of the larger aims of transformation, Wojahn mentioned. An group can go after modest, strategic efficiency improvements but even now maintain in intellect the broader context of how all those incremental advancements relate to every single other and in shape into an overarching transformation agenda.

He stated customers are innovative and comprehend the spectrum of digital transformation, from small, dash-dependent wins to the greater photograph of foundational transform.

“That is a substantially much more simple way of approaching it,” Wojahn stated.

Cyber job openings remains steady amid tech industry layoffs

Cyber job openings remains steady amid tech industry layoffs
Illustration of a lone keyboard key with a briefcase icon on it.

Illustration: Aïda Amer/Axios

The demand from customers for cyber personnel stored constant in latest months as the broader tech field endured from a wave of price-reducing layoffs, in accordance to information released today.

Why it matters: Cybersecurity work openings present a bright place in an usually grim employing outlook for the tech sector.

By the figures: The whole amount of employed cybersecurity workers in 2022 remained rather unchanged from preceding estimates at about 1.1 million, according to new data from the Nationwide Initiative for Cybersecurity Education at the Nationwide Institute of Requirements and Technological know-how, trade team CompTIA and details company Lightcast.

  • At the very same time, businesses posted 755,743 cyber position openings through all of 2022 — down around 2{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1} from the 769,736 posted concerning Oct 2021 and September 2022, the past time these groups compiled this kind of info.
  • Community-sector cybersecurity desire grew 25{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1} in the course of 2022 with 45,708 job postings, the report states. Personal-sector demand grew about 21{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1} to about 710,000 listings.

The large picture: Will Markow, vice president of applied analysis at Lightcast, told Axios that though demand for new cyber hires failed to skyrocket, it “surely continue to remains as powerful as it has ever been.”

  • The two most in-desire roles continue to be cybersecurity engineers and cybersecurity analysts, Markow said, including that there is also strong demand for penetration testers and network stability architects.

Zoom out: Businesses have been having difficulties for years to fill open up cybersecurity roles.

  • In 2022, there had been 68 cybersecurity workers for each individual 100 open up roles, in accordance to the new data. The U.S. wants virtually 530,000 added cybersecurity workers to bridge the gap.

Between the traces: The shortage of staff places cybersecurity workforce in a greater position to survive layoffs throughout the tech field, Markow reported.

  • “There is continue to heading to be assaults coming from every single angle,” Markow stated. “Laying off cybersecurity personnel feels a large amount like firing the sheriff when Billy the Kid is using into town.”

Yes, but: Some cyber workers have nevertheless been victims of layoffs. Past 7 days, TechCrunch noted that Sophos programs to lay off 450 workforce, or around 10{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1} of its workforce.

The intrigue: An financial downturn could inspire much more companies to prioritize entry-degree cybersecurity hires, who often have reduced salaries and have traditionally had difficulties breaking into the field.

  • Only 10{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1} of cyber careers are open to anyone who would not have a bachelor’s diploma, and about 10{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1} to 15{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1} of roles are open up to men and women who have a lot less than 3 years’ practical experience, Markow explained to Axios.
  • “This is efficiently chopping out the entry-degree rung in the cybersecurity job ladder and building it really tough for us to provide fresh new blood into the sector,” he added.

The bottom line: As hacks and breaches boost, cybersecurity isn’t really seeing the very same devastating round of layoffs as other tech industries.

  • Alternatively, the industry is nonetheless struggling to make up the workforce it wants to meet up with desire.

Signal up for Axios’ cybersecurity e-newsletter Codebook here.

From Log4j to zero trust, agencies have another busy year in cyber

From Log4j to zero trust, agencies have another busy year in cyber

To nobody’s surprise, 2022 was a different action-packed yr for federal chief info stability officers and cybersecurity teams across govt.

It commenced with the clear-up from the Log4j software package vulnerability, and has continued with a flurry of new advice and initiatives.

The zero-working day vulnerability in the open source Java library, known as “Log4Shell,” essentially surfaced in late November 2021 and stored stability teams hectic as a result of the holidays. The criticality of the vulnerability is owing to its prevalent…

Browse Much more

To nobody’s surprise, 2022 was yet another action-packed 12 months for federal main information safety officers and cybersecurity groups across govt.

It started off with the cleanse-up from the Log4j software package vulnerability, and has ongoing with a flurry of new advice and initiatives.

The zero-day vulnerability in the open up supply Java library, termed “Log4Shell,” actually surfaced in late November 2021 and kept protection groups chaotic by means of the holiday seasons. The criticality of the vulnerability is due to its common use in networked programs, its simplicity of exploitation, and the important accessibility it gives to productive attackers.

The Cybersecurity and Infrastructure Security Agency led attempts to remediate the vulnerability across agency networks.

“We have witnessed amazing awareness on this vulnerability across federal companies,” CISA Executive Assistant Director for Cybersecurity Eric Goldstein stated in early January. “I think, frankly, the most focused emphasis that we have ever noticed for an energy like this.”

At the identical time, CISA officials stated remediation initiatives were being far from over.

The Cyber Security Overview Board, in its to start with ever report, also warned that unpatched circumstances of Log4j will carry on to crop up for yrs to appear, perhaps up to a 10 years.

Individuals warnings came to fruition in November, when CISA unveiled an inform revealing that concerning mid-June and mid-July, it uncovered proof of Iranian-backed hackers applying Log4shell to compromise the network of an unnamed civilian company. The Washington Publish later on documented the agency in query was the Advantage Programs Defense Board.

But the Log4j incident underscored a push presently in motion to strengthen the stability of application employed across businesses. The motion was initiated by the May possibly 2021 cybersecurity executive buy, and resulted in new protected software growth tactics issued by the Nationwide Institute of Standards and Technology in the spring.

In September, the White Home Office of Administration and Finances issued very expected advice for how businesses ought to adopt the NIST tactics.

The directive, “Enhancing the Protection of the Computer software Offer Chain via Secure Software Enhancement Techniques,” applies to agencies’ use of third-party software, in turn impacting the large array of contractors and software producers in the federal procurement ecosystem.

Less than forthcoming acquisition principles, companies will require software package sellers to self-certify that they are following NIST’s protected progress techniques. The OMB advice also leaves the door open for organizations to mandate third-bash protection assessments as effectively.

It also inspired agencies to use Application Payments of Materials or SBOMs, but it did not need the use of the so-named “software components lists.” The Cyber Protection Evaluate Board in its Log4j report touted the possible use of SBOMs to maximize software transparency, whilst acknowledging more developments in SBOM tooling and adoption are continue to necessary.

The tech field, in the meantime, productively lobbied lawmakers to fall new SBOM prerequisites in the last model of the fiscal 2023 defense authorization invoice. Business associations argued SBOMs have limited utility nowadays simply because of a deficiency of standardization.

But the issue will be one particular to continue on to view in 2023. The Military is transferring forward with potential SBOM adoption across its enormous contracting apparatus. And the Nationwide Security Agency and other direct cyber businesses have endorsed their use as properly.

Zero belief procedures get off floor

The White Property also established organizations on an ambitious cybersecurity path into the long term when it launched the federal zero believe in technique in January. The system addresses a vary of pillars, but functions a “significant emphasis on more powerful organization id and access controls, which include multi-factor authentication.”

It in the end sets a objective for agencies to obtain zero rely on ideas by the stop of fiscal calendar year 2024. Each agency was needed to post an implementation strategy to the White Dwelling, as nicely.

In a new job interview, Chris DeRusha, the federal chief info stability officer, claimed the zero believe in approach has led to what he named “strategy-primarily based budgeting” in the federal cybersecurity realm.

“We were being ready to combine that into the finances procedure by having implementation strategies from each individual company, and then also managing our information calls in by means of the spending budget procedure for fiscal year 24, exactly where we did our cyber funds info phone calls aligned to the zero belief capacity space, so that we can map the tooling to the abilities to the pillars and the approach,” DeRusha reported. “And so we definitely, you can swing up and down with our info that we’ve got now, and fully grasp a real zero believe in funding selection.”

The Protection Section also launched its possess zero believe in method in late November. It lays out a roadmap for how DoD components ought to immediate their cybersecurity investments and endeavours in the coming years to arrive at a “target” stage of zero have faith in maturity more than the future five years.

DoD’s strategy contains 45 separate “capabilities” organized all over seven “pillars”: people, gadgets, networks and environments, purposes and workloads, facts, visibility and analytics, and automation and orchestration.

The Pentagon is also performing with professional cloud companies on how to integrate the zero belief standards into their choices, a notable growth as both defense and civilian agencies ever more adopt cloud providers as the basis of their IT applications.

What White House cyber team thinks about it

What White House cyber team thinks about it

Cyber security education needs to be increased to ward off threats, Principal Deputy National Cyber Director says

Right after Federal Bureau of Investigation Director Christopher Wray explained to lawmakers this 7 days that he has countrywide safety problems about TikTok’s functions in the U.S., a vital member of the White House’s Office of the National Cyber Director expressed support for the FBI and “any measure that will raise security,” but stopped brief of voicing aid for a ban on TikTok that some govt officers assume is needed.

The Biden White Household hasn’t produced any resolve but on a TikTok ban, Kemba Walden, Principal Deputy National Cyber Director, claimed at the CNBC Technologies Govt Council Summit on Tuesday. But growing on her view of a sophisticated national security difficulty with the nation’s major know-how rival, she additional, “we want to concentration on getting in entrance of the adversary. We do not want to just take a reactionary posture in developing policy. We really don’t want transgressors to set our agenda. … We are considerably additional focused on strategic outlook. What is our agenda, and let the transgressors chase us. … If we are reactionary, we continue being reactionary. And there is a spot for that … but if we continue to be in that room, we are just losing a lot more bit by bit.”

With countrywide protection the concentrate, she stated the White Residence is looking at strategic investments to identify how to make domestic units far more resilient and counter information functions. But she also reported TikTok has a accountability to uphold.

“All of these platforms, such as TikTok, will have to preserve security in intellect,” she explained. “Each individual stakeholder has a function in this place, together with the users of TikTok, the builders … all platforms have that obligation in purchase to be equipped to have a net that provides on what we assume, and so I assist any evaluate that will increase safety so that our communities can thrive safely.”

TikTok, which is owned by Beijing-primarily based tech large ByteDance, is applied by over 1 billion folks worldwide each month.

Artur Widak | Nurphoto | Getty Visuals

Wray informed members of the Residence Homeland Protection Committee in a listening to about around the globe threats on Tuesday that he is “particularly concerned” about TikTok’s functions in the U.S.

“They include the probability that the Chinese federal government could use it to regulate details collection on millions of consumers. Or management the suggestion algorithm, which could be employed for influence operations if they so selected. Or to regulate program on hundreds of thousands of equipment, which offers it opportunity to probably technically compromise particular products,” Wray mentioned.

Walden reported she is anxious about TikTok’s impact on youngsters, but also framed the problem in phrases of the bigger issue of adequately educating the younger for the online planet of data.

“I have young adults who expend their whole life on TikTok and since it is so absorbing, but you do ponder about the Chinese government’s inspiration in feeding all of that information stream to thousands and thousands of Americans. And then also all the monitoring that goes along with that,” reported CNBC’s Senior Washington Correspondent Eamon Javers all through the interview. “So you communicate about security has to be a precedence, but if Beijing has very distinct priorities than you do, how do you consider this substantial influence procedure that China is functioning on TikTok for hundreds of thousands of Us residents? At the exact same time they’re obtaining a very various standpoint on what they want the outcome to be.”

“I have young children much too, and I would like that just like drivers licenses are required in advance of they drive a automobile, would not it be charming if they had been needed to have a license?” Walden mentioned in reaction to Javers’ question. She pressured that there was no formal program for the U.S. authorities to make an investment specifically associated to this idea, but included, “which is type of exactly where I start out to believe about assisting our learners, supporting our communities turn out to be much more resilient. It can be not just the know-how and the apps, it’s the people today and the processes and doctrine. … My 9-yr-previous could result in a nationwide safety incident and that’s terrifying, ideal?”

Issues above the Chinese-owned video platform’s capacity to defend U.S. person info from China have developed amid govt officials and customers of Congress in modern months. A Federal Communications Commissioner explained before this month that the U.S. govt should really ban TikTok, and the Committee on Overseas Investment in the U.S. (CFIUS) in the Treasury Office is examining the company’s opportunity national stability implications.

Walden mentioned CFIUS performs an crucial job in countrywide security and cybersecurity, but is ordinarily used as “a surgical knife, not a hammer.”

“I assume it would be a miscalculation for CFIUS to be utilized as a system to establish broad plan. But they absolutely have a potent resource,” she mentioned.

The concern lies with a Chinese law that makes it possible for the governing administration to pressure providers to hand about internal facts. TikTok guardian-firm ByteDance has continued to keep that it isn’t going to retail outlet U.S. person data in China, the place the legislation could be used.

Wray reported on Tuesday that legislation by yourself was “lots of purpose by alone to be very concerned.”

In a assertion, a TikTok spokesperson instructed CNBC on Tuesday that “we are self-assured that we are on a path to thoroughly satisfy all sensible U.S. nationwide protection issues.”

Strengthening cybersecurity education

Walden, who became the 1st person named to her White House cybersecurity placement in May following serving as the assistant general counsel in Microsoft’s digital crimes device, pressured the function of instruction on various situations during the interview with Javers.

“Regardless of what an app is undertaking, we need to actually elevate cybersecurity education in our devices and increase cyber awareness amongst our people today to make certain they’re resilient,” she explained. “Important pondering is a great antidote to some of the perform that other transgressors are working on.”

The Workplace of the National Cyber Director was founded by the Biden administration in 2021, with Chris Inglis remaining named the initial National Cyber Director. The workplace serves as a principal advisor to the president on cybersecurity plan and strategy, aiming to guarantee that Individuals can “share in the full added benefits” of the electronic ecosystem even though addressing and mitigating the dangers and threats located in cyberspace.

Walden explained rising cybersecurity education and learning is just just one of the methods the White Residence is aiming to “get in entrance of the adversary.”

Correction: Owing to an editing error, an before version of this short article misattributed a quote to Kemba Walden, Principal Deputy National Cyber Director. The posting has been up-to-date to contain appropriate attribution.

FBI Director Christopher Wray raises national security concerns over TikTok