The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has unveiled a new advisory about Royal ransomware, which emerged in the threat landscape past calendar year.
“Just after attaining accessibility to victims’ networks, Royal actors disable antivirus program and exfiltrate substantial amounts of details prior to eventually deploying the ransomware and encrypting the systems,” CISA mentioned.
The tailor made ransomware plan, which has qualified U.S. and worldwide organizations since September 2022, is considered to have evolved from previously iterations that had been dubbed Zeon.
What is actually additional, it’s mentioned to be operated by seasoned menace actors who utilised to be component of Conti Crew One particular, cybersecurity corporation Trend Micro disclosed in December 2022.
The ransomware team employs connect with again phishing as a indicates of offering their ransomware to victims, a approach broadly adopted by criminal teams that splintered from the Conti company previous calendar year next its shutdown.
Other modes of first access consist of remote desktop protocol (RDP), exploitation of public-dealing with applications, and by means of preliminary entry brokers (IABs).
Ransom calls for built by Royal change from $1 million to $11 million, with assaults focusing on a variety of essential sectors, together with communications, instruction, healthcare, and manufacturing.
“Royal ransomware employs a exclusive partial encryption technique that will allow the menace actor to opt for a certain share of information in a file to encrypt,” CISA famous. “This method will allow the actor to decrease the encryption percentage for more substantial documents, which can help evade detection.”
The cybersecurity company mentioned many command-and-handle (C2) servers related with Qakbot have been used in Royal ransomware intrusions, despite the fact that it can be now undetermined if the malware exclusively depends on Qakbot infrastructure.
The intrusions are also characterised by the use of Cobalt Strike and PsExec for lateral movement as nicely as deleting shadow copies to prevent program recovery. Cobalt Strike is also repurposed for info aggregation and exfiltration.
As of February 2023, Royal ransomware is able of focusing on both of those Home windows and Linux environments. It has been connected to 19 assaults in the thirty day period of January 2023 on your own, putting it at the rear of LockBit, ALPHV, and Vice Modern society.
Uncovered this article interesting? Observe us on Twitter and LinkedIn to examine extra distinctive information we write-up.
CAMBRIDGE, Mass., March 2, 2023 /PRNewswire/ — Akamai Technologies, Inc. (NASDAQ: AKAM), the cloud firm that powers and shields existence on-line, today announces that it has entered into a definitive agreement to acquire Ondat, a cloud-primarily based storage technology company with a Kubernetes-indigenous platform for functioning stateful apps wherever at scale. Ondat’s technological know-how delivers persistent storage instantly onto any Kubernetes cluster for managing enterprise-significant, stateful purposes safely and securely throughout any public, personal and hybrid clouds. The acquisition of Ondat’s cloud storage technological innovation and its sector-regarded talent is meant to bolster Akamai’s cloud computing offerings.
“Final thirty day period we shared particulars of Akamai Related Cloud, the world’s most distributed system for cloud computing, safety, and content material shipping and delivery,” stated Adam Karon, chief functioning officer and general manager, Cloud Technology Group, Akamai Technologies. “Storage is a vital part of cloud computing and Ondat’s technology will increase Akamai’s storage abilities, enabling us to present a fundamentally various method to cloud that integrates core and dispersed computing websites with a massively scaled edge network.”
Ondat’s workforce, which include founder and chief technological innovation officer Alex Chircop, will be a part of Akamai’s cloud computing small business.
Akamai Related Cloud is a massively distributed edge and cloud platform for cloud computing, protection, and written content supply that retains applications and experiences closer and threats farther absent. Akamai’s cloud computing expert services help developers to develop, run and safe very performant workloads closer to anywhere businesses and users join on the web. In creating out Akamai Related Cloud, Akamai is introducing main and distributed internet sites on major of the very same underlying backbone that powers its edge community today — spanning much more than 4,100 areas throughout 134 international locations. Much more especially, Akamai is inserting compute, storage, databases and other expert services closer to big inhabitants, market and IT facilities.
Ondat, headquartered in London, U.K., is a privately funded enterprise. The acquisition is predicted to near in the initially quarter of 2023. Akamai anticipates no substance effect to the company’s financial steerage for 2023 as a outcome of the transaction.
Akamai powers and protects everyday living on the internet. Major providers around the globe choose Akamai to develop, deliver, and secure their electronic ordeals — aiding billions of people reside, get the job done, and perform every single working day. With the world’s most dispersed compute platform — from cloud to edge — we make it straightforward for clients to acquire and operate purposes, whilst we retain experiences closer to consumers and threats farther away. Study far more about Akamai’s safety, compute, and shipping and delivery alternatives at akamai.com and akamai.com/weblog, or adhere to Akamai Technologies on Twitter and LinkedIn.
Akamai Assertion Below the Non-public Securities Litigation Reform Act
This release includes statements that are not statements of historical fact and constitute forward-wanting statements for functions of the safe harbor provisions less than The Personal Securities Litigation Reform Act of 1995, such as, but not confined to, statements about expectations, designs and potential customers of Akamai. True success may well differ materially from those indicated by these forward-on the lookout statements as a end result of different crucial variables such as, but not limited to, the failure of our investments in innovation to create options that are approved in the sector effects of competition, including pricing pressure and altering organization designs influence of macroeconomic traits, like financial uncertainty disorders and uncertainties in the geopolitical ecosystem continuing source chain and logistics prices, constraints, variations or disruptions flaws or disruptions in our products and solutions or IT devices, together with cyberattacks, information breaches or malware failure to understand the envisioned rewards of any of our acquisitions or reorganizations variations to economic, political and regulatory conditions in the United States and internationally hold off in producing or failure to develop new services offerings or functionalities, and if formulated, absence of current market acceptance of this kind of service choices and functionalities or failure of these remedies to function as expected, and other aspects that are mentioned in our Annual Report on Variety 10-K, quarterly reports on Form 10-Q, and other paperwork periodically filed with the SEC. In addition, the statements in this push release and on our quarterly earnings conference simply call depict Akamai’s expectations and beliefs as of the date of this push release. Akamai anticipates that subsequent situations and developments could result in these expectations and beliefs to adjust. Nevertheless, when Akamai may elect to update these forward-hunting statements at some level in the potential, it precisely disclaims any obligation to do so. These forward-on the lookout statements need to not be relied on as representing Akamai’s anticipations or beliefs as of any day subsequent to the day of this push release.
Media Make contact with Gina Sorice (646) 320-4107 [email protected]
Trader Call Tom Barth (617) 274-7130 [email protected]
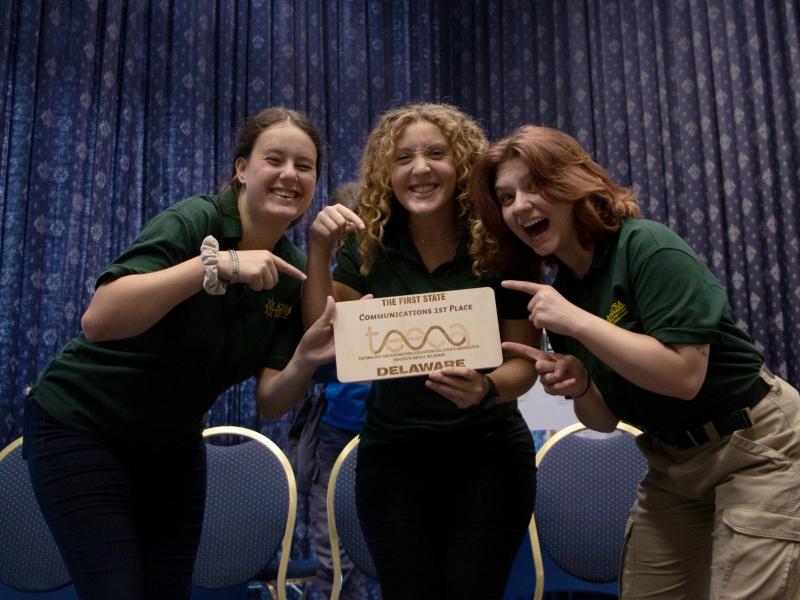
The university’s OTSA (Oswego Technological innovation Scholar Association) finished initially in 3 competitions, and in the leading a few in many many others, in a prestigious regional convention in Delaware.
OTSA traveled to Rehoboth Beach to participate in the once-a-year TEECA (Technological innovation and Engineering Education Collegiate Affiliation) East Regional Meeting, element of ITEEA (Global Technological innovation and Engineering Educators Association).
In the a few-working day conference held every drop, learners from increased training establishments throughout the east coast participate in a series of fingers-on and interactive competitions. TEECA’s mission is to help learners use what they study in the classroom and collaborate on fun and distinctive creations together with their friends.
OTSA’s crew of students, faculty and connected devices arrived in Delaware pursuing the 8-hour push from SUNY Oswego and participated in day a single of the festivities. They scored their original initial-position complete with Sport On Night, a new addition to the meeting, which included a 3-on-3 basketball event and volleyball games for the faculties to break a sweat and crack the ice ahead of the key event.
With the aid of faculty member Mark Springston, who was liable for pitching the plan, the tournament was a bonding activity that established the phase for aggressive occasions.
Scoring wins
Represented by president Bryleigh Beauchat, pupils Ben Sullivan, Zach Hilbert, Jack Hickey, Rich Sgueglia, Springston and coaches Maggie Romano and Adam Parente in the basketball tournament, OTSA concluded very first in the inaugural contest.
A unique twist of the basketball opposition was that it coincided with the Conversation Challenge, as learners made use of the footage from the games to develop a sports activities documentary.
Although OTSA marched to victory through the basketball online games, Beauchat checked in with staff users Eliza Sarigiannis and Taylor Mackowiak for the Communications Challenge, which she was also a component of. Soon just after the 3-on-3 competition concluded, Beauchat, Sarigiannis and Mackowiak would devote the upcoming working day organizing and enhancing the footage they recorded to prepare for submission.
“We had 24 hours in the Communications Obstacle to develop, edit, do any voiceovers we may perhaps want and submit the movie the future working day,” Beauchat said. “It was grind time to get that all in.”
Even with the speedy turnaround, the team made a concerted effort to develop a large-high quality movie, modeling it after the ESPN documentary film series “30 for 30.” The dedication led to a first-position finish in the levels of competition, as the team credited the interviews performed in the course of the 3-on-3 contest and the powerful basketball enjoy in securing the victory.
“The assist of Eliza and all people else on OTSA… aided us get that excess edge on the video,” said Beauchat.
The video also marked a indication of redemption for Beauchat and Mackowiak. The duo participated in the Communications Problem during the ITEEA Meeting in March 2022 but felt the movie submission they designed didn’t meet their very own superior benchmarks.
Scoring solutions
OTSA also concluded to start with in the Dilemma Solving Obstacle. In this levels of competition, learners Parente, Sgueglia and Daniel Hall had been responsible for bringing assigned components to the meeting to support create a solution to a distinct difficulty.
“Huge accomplishment,” Beauchat explained of the victory. “I’m super very pleased they had been equipped to dedicate the time, do the job, and effort.”
The next two times saw the educational institutions take part in the remaining 8 challenges, such as the Integrated STEM and Manufacturing Challenges, the place OTSA concluded 2nd in both of those gatherings, and Robotics and Educating Lesson, where by OTSA finished third in equally.
“We come closer collectively as peers… performing with each other on a challenge, in which you have a prospect to get an award,” mentioned Beauchat. “We’re building some thing of our individual that’s not centered on regardless of whether we move or are unsuccessful.”
Each group represented by OTSA completed in the major 3 at the TEECA East Meeting, as they reaped the benefits of their critical preparation and challenging operate throughout the event.
OTSA will arrange the function throughout the slide 2023 conference in the identical site, and seems to repeat its efficiency from the final TEECA and the approaching ITEEA meeting in April. Those accomplishments designed on some achievements at last year’s ITEEA conference, including a 2nd place in the Countrywide Communications Problem.
Eegardless of what is subsequent, technological know-how professor and faculty advisor Richard Bush will reminisce on his team’s unforgettable run.
“Sometimes in the earlier, we occur home a very little gentle on the trophies,” Bush reported. “This was quite successful, and we’re very pleased of our achievements.”
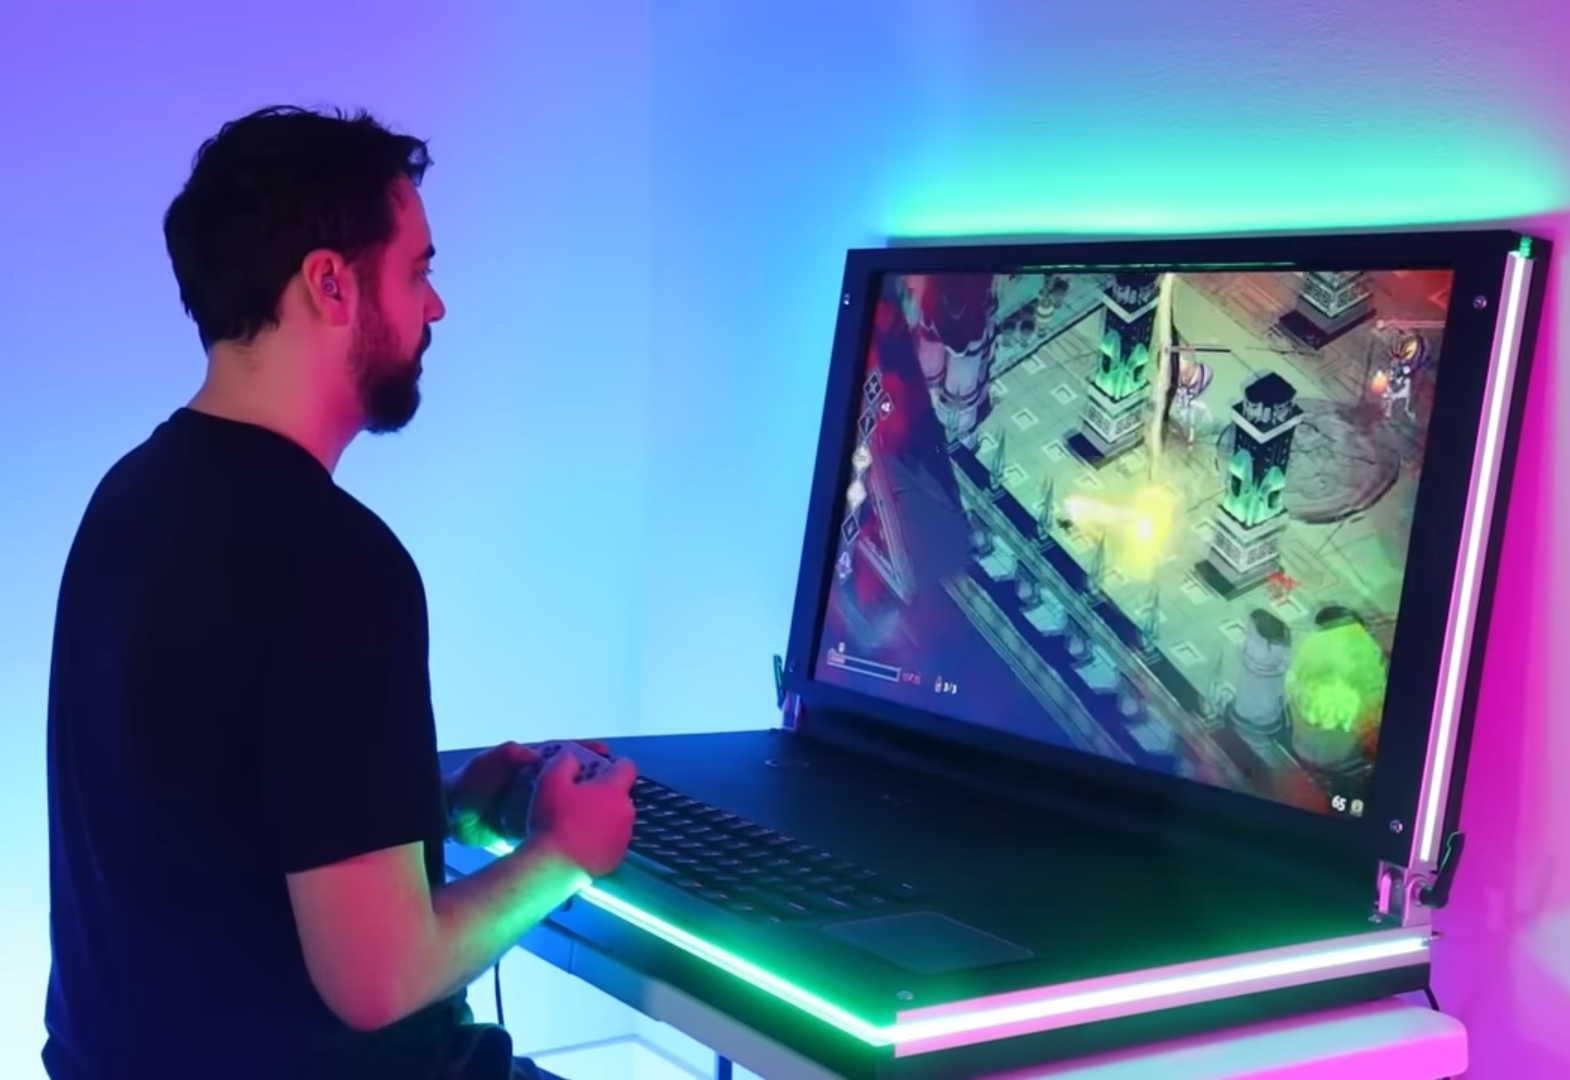
The BFL is built around a 43-inch TV screen. (Image Source: YouTube)
This wacky DIY project uses a 43-inch TV as its screen, and the computing power is provided via an Intel NUC 11 with i7-1165G7 processor and RTX 2060 dGPU that is hidden under the keyboard together with three high capacity batteries, which can sustain 260 W in full load.
YouTuber couple Evan and Katelyn came up with a crazy DIY project involving maybe the biggest laptop ever. How big? Think 43-inch big. The monster was named BFL (Big Fun Laptop) and it all started with the screen that is actually an LCD TV. Then a chassis was built around it, complete with personalized logo and some RGB light strips.
The chassis includes aluminum extrusions with two big hinges. Plywood was chosen for the upper and lower lids, while ABS sheets with a touch vinyl were added on the interior. Nevertheless, Evan and Katelyn tried to keep the laptop profile at a reasonable thickness, so they needed to find pretty compact components including three batteries that can provide enough power for a 260 W load.
One of the batteries is powering the screen alone, a second one is for a mini PC plus the peripherals attached to it, and the third one is for the LED strips. Of course, all these components needed to be fixed in place with a bunch of 3D-printed brackets. At the heart of the BFL lies a NUC 11 mini PC with Intel i7-1165G7 processor and RTX 2060 dGPU. Certainly not the fastest NUC, but a TSP of over 300 W would have probably needed four batteries. There is also a USB hub and a pretty big mechanical keyboard that still feels small for the laptop size.
It looks like the total thickness is around 4 inches, which is fair enough all things considered. The problem is the weight. This monster laptop is failing the portability test with flying colors as it weighs around 100 lbs (45.35 kg).
Bogdan Solca – Senior Tech Writer – 1959 articles published on Notebookcheck since 2017
I first stepped into the wondrous IT&C world when I was around seven years old. I was instantly fascinated by computerized graphics, whether they were from games or 3D applications like 3D Max. I’m also an avid reader of science fiction, an astrophysics aficionado, and a crypto geek. I started writing PC-related articles for Softpedia and a few blogs back in 2006. I joined the Notebookcheck team in the summer of 2017 and am currently a senior tech writer mostly covering processor, GPU, and laptop news.
Iowa basketball picked up a substantially-needed acquire on Saturday afternoon as the Hawkeyes took down Michigan State, 112-106, in overtime. The Hawkeyes were down 13 details with 1:30 remaining in the next half, but uncovered a way to arrive back and pressure overtime. Iowa then took care of small business in the extra five minutes to safe the victory.
Iowa arrived into the activity losers of two straight contests and a decline would not have helped the Hawkeyes’ resume. Iowa is on the brink of generating its fourth NCAA Match in five seasons, with the lone a single it skipped being the COVID 12 months. Experienced it been a usual event, Iowa would’ve been in the field, way too.
“Yeah, all over the system of the yr, a great deal of things transpire,” Iowa head mentor Fran McCaffery said previous 7 days. “You have accidents. You think about when we played a 10:30 match in New York and received household at 5 a.m., and we had to play less than 40 hrs later on. The young ones performed great. You just go on to the next. You don’t obsess about it. We bussed residence yesterday, we didn’t bus residence immediately after the video game. So what? We’re heading to bus property one way or the other. What distinction does it make what time we get back?”
“You have to stay locked in, and if you have some guys that are out, you action up and do your job.”
The Hawkeyes have two regular year game titles remaining on the street at Indiana and then at dwelling towards Nebraska. Immediately after that, Iowa will enjoy in the Big 10 Match. There is a great deal that continue to can figure out the seeding in the meeting match.
As of Sunday, it seems that Iowa is a sixth seed in the Massive Ten as it retains the tiebreaker more than Illinois in the head-to-head group. There are seven teams in the Massive Ten with eight, nine, or 10 meeting wins, so a ton will be decided in this final 7 days of the frequent time.
Other folks teams on the seven, 8, and 9 lines in order (Bracket Matrix): Maryland, Michigan Point out, Texas A&M, Duke, Providence, Kentucky, Arkansas, IOWA, Missouri, NC Point out, Auburn, and Rutgers
Other projected Massive 10 groups in the discipline (Bracket Matrix – Updated on Feb. 26): Purdue (No. 1 seed), Indiana (No. 4 seed), Northwestern and Illinois (No. 6 seeds), Maryland and Michigan Condition (No. 7 seeds), Iowa (No. 8 seed), Rutgers (No. 9 seed), and Wisconsin (No. 11 seed)
Significant Ten teams on the bubble:Penn Point out and Michigan
You can get anonce-a-year membership for 30{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1} off.Acquire benefit now and be the to start with to know every thing heading on concerning Iowa soccer, basketball, and recruiting!Click In this article!
Cloud and edge networks are placing up a new line of protection, identified as confidential computing, to protect the expanding prosperity of details people approach in those environments.
Private Computing Defined
Confidential computing is a way of shielding data in use, for example although in memory or throughout computation, and avoiding any one from viewing or altering the perform.
Making use of cryptographic keys linked to the processors, confidential computing makes a reliable execution surroundings or secure enclave. That harmless electronic place supports a cryptographically signed proof, named attestation, that the hardware and firmware is properly configured to stop the viewing or alteration of their data or software code.
In the language of protection specialists, confidential computing gives assurances of knowledge and code privateness as well as information and code integrity.
What Can make Private Computing Exclusive?
Private computing is a reasonably new capability for defending info in use.
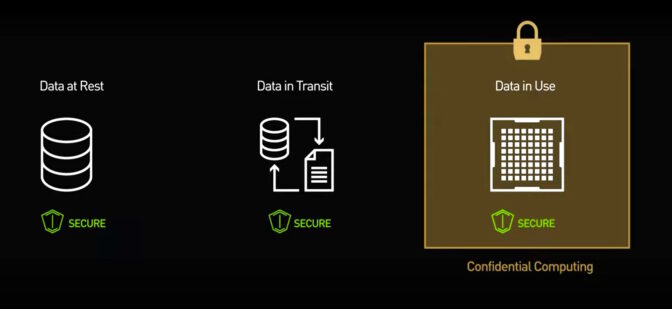
For several yrs, personal computers have utilized encryption to secure data that’s in transit on a network and details at relaxation, stored in a drive or non-volatile memory chip. But with no useful way to run calculations on encrypted info, users confronted a hazard of owning their facts viewed, scrambled or stolen when it was in use within a processor or main memory.
With private computing, methods can now include all three legs of the details-lifecycle stool, so information is in no way in the obvious.
Private computing adds a new layer in pc stability — defending knowledge in use when functioning on a processor.
In the past, computer system safety primarily centered on protecting facts on programs customers owned, like their company servers. In this situation, it’s all right that system software sees the user’s data and code.
With the advent of cloud and edge computing, customers now routinely operate their workloads on desktops they don’t own. So private computing flips the focus to protecting the users’ data from whoever owns the equipment.
With private computing, software jogging on the cloud or edge laptop or computer, like an running procedure or hypervisor, still manages function. For example, it allocates memory to the person application, but it can under no circumstances read or alter the info in memory allocated by the user.
How Private Computing Received Its Name
A 2015 investigation paper was one of many applying new Safety Guard Extensions (Intel SGX) in x86 CPUs to display what is possible. It identified as its technique VC3, for Verifiable Confidential Cloud Computing, and the identify — or at the very least element of it — trapped.
“We started out calling it confidential cloud computing,” claimed Felix Schuster, direct author on the 2015 paper.
Four many years later, Schuster co-established Edgeless Devices, a firm in Bochum, Germany, that develops resources so users can make their individual confidential-computing apps to increase data defense.
Confidential computing is “like attaching a deal to your details that only allows specific matters to be finished with it,” he said.
How Does Private Computing Perform?
Taking a deeper look, private computing sits on a foundation referred to as a root of trust, which is primarily based on a secured crucial distinctive to each and every processor.
The processor checks it has the proper firmware to get started working with what is named a safe, calculated boot. That course of action spawns reference information, verifying the chip is in a acknowledged risk-free condition to commence work.
Up coming, the processor establishes a safe enclave or dependable execution surroundings (TEE) sealed off from the rest of the process where the user’s application runs. The application brings encrypted information into the TEE, decrypts it, operates the user’s application, encrypts the outcome and sends it off.
At no time could the device proprietor perspective the user’s code or information.
A single other piece is important: It proves to the consumer no one particular could tamper with the knowledge or program.
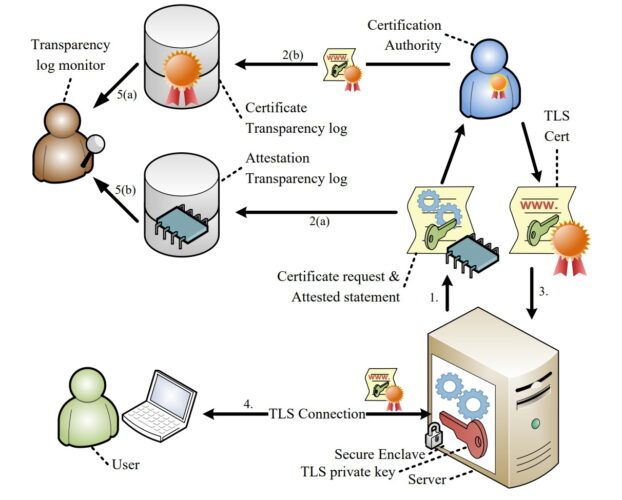
Attestation takes advantage of a private key to build stability certificates stored in general public logs. Buyers can obtain them with the web’s transportation layer protection (TLS) to verify confidentiality defenses are intact, protecting their workloads.
The proof is shipped via a multi-stage procedure termed attestation (see diagram over).
The very good news is researchers and commercially offered companies have demonstrated confidential computing is effective, usually furnishing info safety without substantially impacting overall performance.
A significant-degree search at how private computing will work.
Shrinking the Safety Perimeters
As a final result, consumers no more time have to have to rely on all the application and techniques administrators in separate cloud and edge companies at remote destinations.
Private computing closes numerous doors hackers like to use. It isolates systems and their facts from attacks that could appear from firmware, working programs, hypervisors, virtual machines — even bodily interfaces like a USB port or PCI Categorical connector on the laptop or computer.
The new stage of safety guarantees to lessen knowledge breaches that rose from 662 in 2010 to extra than 1,000 by 2021 in the U.S. by yourself, according to a report from the Id Theft Source Center.
That reported, no stability measure is a panacea, but private computing is a wonderful stability instrument, placing command straight in the hands of “data owners”.
Use Scenarios for Confidential Computing
Consumers with sensitive datasets and regulated industries like banks, healthcare providers and governments are between the to start with to use confidential computing. But that’s just the start.
Because it protects delicate facts and mental home, confidential computing will enable teams truly feel they can collaborate properly. They share an attested proof their content material and code was secured.
Illustration programs for confidential computing involve:
Businesses executing intelligent contracts with blockchains
Investigation hospitals collaborating to teach AI versions that examine developments in individual information
Shops, telecom suppliers and other folks at the network’s edge, defending private details in places the place physical obtain to the computer is attainable
Software package vendors can distribute products and solutions which contain AI products and proprietary algorithms when preserving their mental property
Even though private computing is finding its commence in public cloud expert services, it will unfold rapidly.
Users will need confidential computing to safeguard edge servers in unattended or challenging-to-reach areas. Business knowledge centers can use it to guard against insider attacks and guard one private workload from a further.
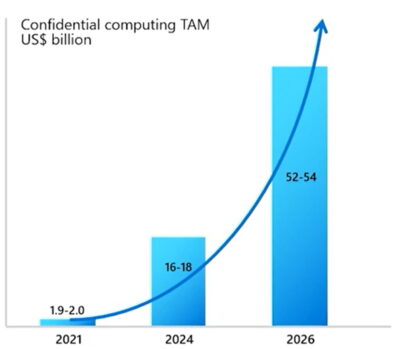
Industry scientists at Everest Team estimate the offered industry for private computing could improve 26x in 5 years.
So significantly, most end users are in a evidence-of-principle stage with hopes of placing workloads into output quickly, said Schuster.
On the lookout ahead, private computing will not be minimal to unique-goal or sensitive workloads. It will be applied broadly, like the cloud services hosting this new stage of security.
In truth, experts predict confidential computing will develop into as widely utilised as encryption.
The technology’s prospective motivated suppliers in 2019 to start the Confidential Computing Consortium, section of the Linux Basis. CCC’s members consist of processor and cloud leaders as perfectly as dozens of program organizations.
The group’s tasks include the Open Enclave SDK, a framework for setting up dependable execution environments.
“Our most important mandate is supporting all the open-source initiatives that are foundational sections of the ecosystem,” explained Jethro Beekman, a member of the CCC’s technological advisory council and vice president of technological know-how at Fortanix, 1 of the very first startups started to produce confidential computing computer software.
“It’s a powerful paradigm to set protection at the facts level, fairly than get worried about the particulars of the infrastructure — that need to final result in not needing to examine about facts breaches in the paper just about every working day,” mentioned Beekman, who wrote his 2016 Ph.D. dissertation on confidential computing.
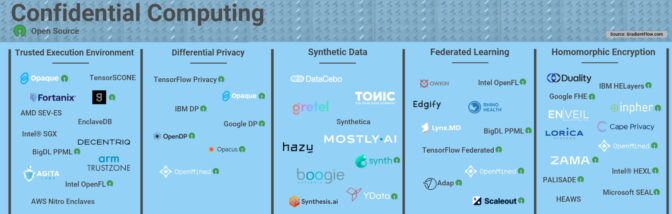
A rising sector of safety businesses is doing the job in confidential computing and adjacent regions. (Supply: GradientFlow)
How Confidential Computing Is Evolving
Implementations of confidential computing are evolving rapidly.
At the CPU stage, AMD has launched Secure Encrypted Virtualization with Safe Nested Paging (SEV-SNP). It extends the course of action-stage protection in Intel SGX to complete digital machines, so consumers can employ confidential computing with no needing to rewrite their programs.
Top rated processor makers have aligned on supporting this tactic. Intel’s help comes through new Trusted Area Extensions. Arm has explained its implementation, known as Realms.
Proponents of the RISC-V processor architecture are utilizing confidential computing in an open up-source task called Keystone.
Accelerating Confidential Computing
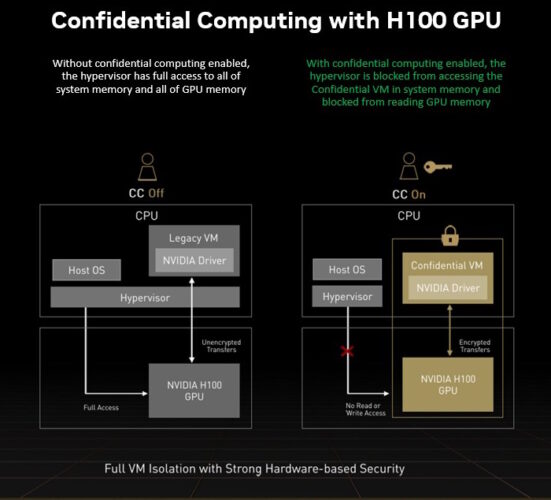
NVIDIA is bringing GPU acceleration to VM-style private computing to market place with its Hopper architecture GPUs.
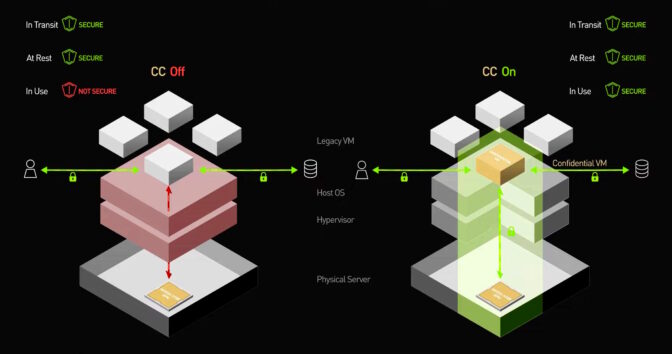
The H100 Tensor Main GPUs enable confidential computing for a wide swath of AI and significant effectiveness computing use cases. This gives users of these safety services entry to accelerated computing.
An example of how GPUs and CPUs operate jointly to provide an accelerated confidential computing services.
In the meantime, cloud service providers are presenting services today dependent on one particular or more of the underlying technologies or their possess special hybrids.
What’s Up coming for Private Computing
More than time, industry suggestions and expectations will arise and evolve for features of private computing such as attestation and productive, protected I/O, explained Beekman of CCC.
Whilst it is a reasonably new privacy software, private computing’s ability to shield code and info and deliver assures of confidentiality makes it a highly effective one.
Hunting forward, experts anticipate private computing will be blended with other privacy solutions like fully homomorphic encryption (FHE), federated learning, differential privateness, and other types of multiparty computing.
Using all the elements of the modern-day privacy toolbox will be key to success as need for AI and privateness grows.
So, there are numerous moves forward in the great chess match of stability to defeat the difficulties and know the positive aspects of private computing.
Choose a Deeper Dive
To understand additional, look at “Hopper Confidential Computing: How it Performs Under the Hood,” session S51709 at GTC on March 22 or later on (absolutely free with registration).
Check out out “Confidential Computing: The Developer’s Look at to Protected an Application and Details on NVIDIA H100,” session S51684 on March 23 or later on.
You also can attend a March 15 panel dialogue at the Open up Private Computing Conference moderated by Schuster and showcasing Ian Buck, NVIDIA’s vice president of hyperscale and HPC. And watch the online video under.