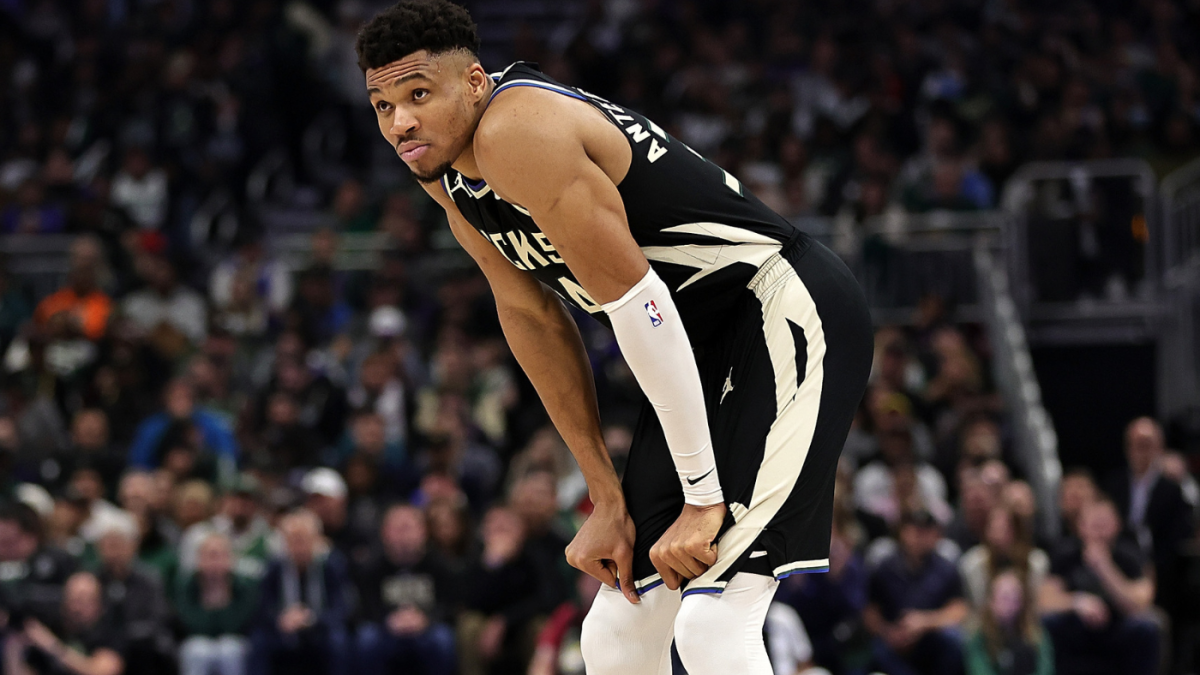
MILWAUKEE — Milwaukee Bucks star Giannis Antetokounmpo left the team’s 130-117 loss to the Miami Heat in Game 1 of their first-round playoff series with a lower back contusion. He suffered no structural damage, but his status for Game 2 and beyond will depend on how his back responds. The Bucks are optimistic that Antetokounmpo will be available for Game 2, per Shams Charania, but the two-time MVP is also reportedly dealing with a ligament issue in his wrist.
“There was an X-ray that was clear here, so we’ll monitor him, see how he does,” Bucks head coach Mike Budenholzer said. “See how he wakes up, how he feels the rest of tonight and tomorrow.”
In the middle of the first quarter, Antetokounmpo took a swing pass from Joe Ingles and drove hard to the basket. As he took off for the rim from just outside the charge circle, Kevin Love slid underneath in an attempt to take a charge. Antetokounmpo had his legs taken out in the process and crashed hard to the floor on his lower back.
The play was ruled a blocking foul on Love, and Antetokounmpo remained in the game to shoot his free throws, then continued playing for a few more minutes before checking out at the end of his usual first quarter stint. Upon exiting the game, he went straight to the locker room, but was back out on the bench for the start of the second quarter.
With 9:56 remaining in the second quarter, Antetokounmpo checked back into the game and went through a series of twists and jumps near mid-court to try and loosen up his back. He only lasted a little over a minute, however, and subbed back out with 8:33 on the clock. Moving gingerly, he again went right down the tunnel to the locker room and was officially ruled out a short time later.
Please check the opt-in box to acknowledge that you would like to subscribe.
Thanks for signing up!
Keep an eye on your inbox.
Sorry!
There was an error processing your subscription.
The Bucks were trailing by eight when Antetokounmpo left the game and never truly recovered. A run in the third quarter briefly cut the deficit to three, but they trailed by double digits for large portions of the second half and eventually lost by 13.
“That’s our guy, we hope he’s gonna be well and back out there with us Wednesday,” Khris Middleton said. “But we just gotta focus on who’s out there at the same time. They had a guy go down also and they continued to compete and play well. Same mindset we tried to have. Sucks that our guy goes down or can’t return, but we still got a job to do out there.”
Milwaukee has plenty of experience playing without Antetokounmpo, both this season when he missed 19 games and in the 2021 playoffs when he suffered a hyperextended knee in the Eastern Conference finals. It goes without saying, though, that they would prefer to have their two-time MVP on the floor.
“We don’t want him to be hurt, but it’s still next man up mentality,” Jrue Holiday said. “We have enough talent on this team to cover for him until he comes back or possibly comes back. Again, I just don’t want to see him hurt because I know what it feels like, especially Game 1 of the playoffs.”
During the regular season, Antetokounmpo averaged 31.1 points, 11.8 rebounds and 5.7 assists per game. He was the only player in the league to put up at least 30 points, 10 rebounds and five assists a night, and the Bucks were 47-16 when he played compared to 11-8 when he sat.
FTX, the once beloved crypto exchange that went down in a ball of financially flames last November, appears to have spent very little effort protecting its customers’ vast reserves of digital assets. The company’s latest bankruptcy report reveals that, in addition to managing its finances like a Jim-Beam-swigging monkey, the disgraced crypto exchange also had some of the worst cybersecurity practices imaginable.
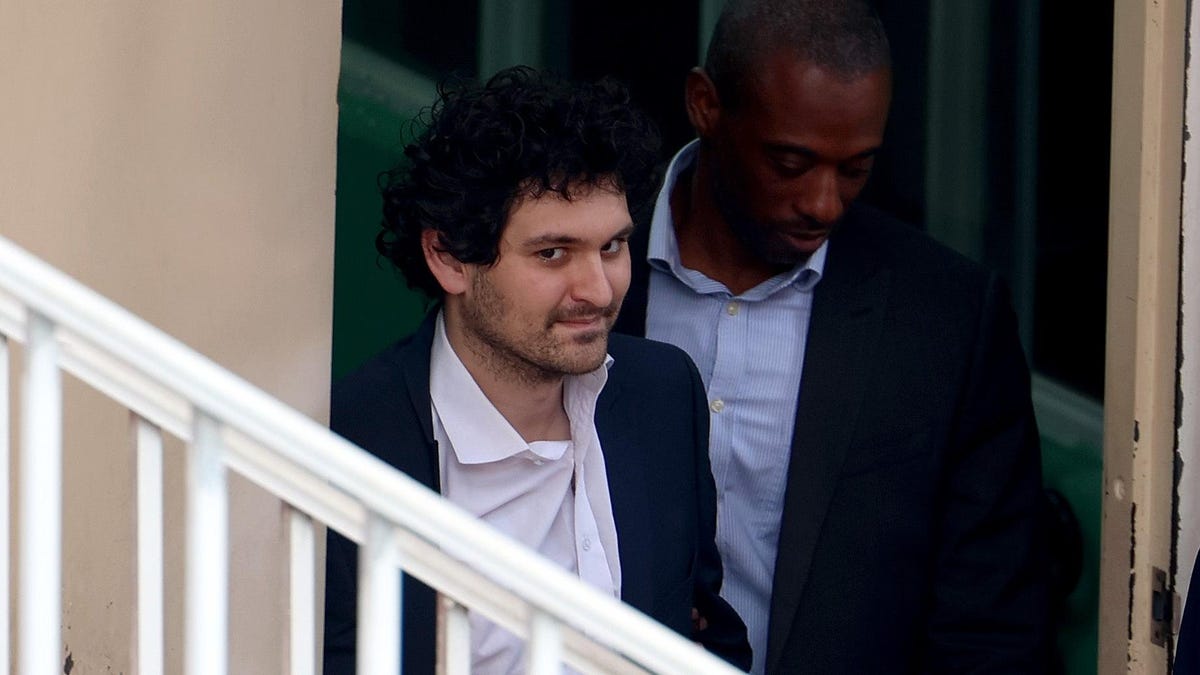
Of course, we’ve known that FTX sucked at cyber since at least last November when, less than 24 hours after the company declared Chapter 11 bankruptcy and its former CEO, Sam Bankman-Fried, aka SBF stepped down, the company suffered a massive digital robbery. The robber, whoever they were, made off with $432 million in assets, a bundle of digital cash that is still unaccounted for—just like a whole lot more of FTX customers’ money.
At the time, the hacking incident seemed like just more bad news on top of an already epic shit sundae, but now we have a little more context for the episode. Monday’s report, which extensively reviews the company’s failure to put basic digital protections in place, is a comic masterpiece that will make you wonder how the company didn’t get hacked earlier.
G/O Media may get a commission
Save $400
2021 14″ 1TB MacBook Pro
MacBook Pro’s are the way to go Up to 10-core CPU delivers up to 3.7x faster performance to fly through pro workflows quicker than ever. Up to 32-core GPU with up to 13x faster performance for graphics-intensive apps and games
“The FTX Group failed to implement basic, widely accepted security controls to protect crypto assets. Each failure was egregious in the context of a business entrusted with customer transactions,” the filing states. Here are some of the takeaways about those failures.
FTX Didn’t Have a Cybersecurity Staff
Despite being a company tasked with protecting tens of billions of dollars in crypto assets, FTX had no dedicated cybersecurity staff, according to Monday’s filing. None. The company never bothered to hire a CISO (a chief information security officer) to manage the company’s risks for them. Instead, they relied on two of the company’s software developers who, the report notes, did not have formal training in security and whose jobs put them at odds with prioritizing security. The report states:
The FTX Group had no independent Chief Information Security Officer, no employee with appropriate training or experience tasked with fulfilling the responsibilities of such a role, and no established processes for assessing cyber risk, implementing security controls, or responding to cyber incidents in real time…as with critical controls in other areas, the FTX Group grossly deprioritized and ignored cybersecurity controls, a remarkable fact given that, in essence, the FTX Group’s entire business—its assets, infrastructure, and intellectual property—consisted of computer code and technology.
Granted, lots of tech companies suffer from staffing shortages when it comes to cybersecurity but that’s really only excusable if you’re a unicorn or a startup and don’t have the manpower or capital to hire competent people. In the days before its implosion, FTX was reported to be worth as much as $32 billion. Suffice it to say, I think they could’ve hired a guy.
FTX Pretty Much Never Used Cold Storage, the Industry Standard
Another really dumb thing that FTX did was fail to keep its users’ crypto assets in cold storage—a standard security practice that most crypto exchanges claim to abide by.
In general, crypto assets can be stored in two separate ways: “hot wallets,” which are software-based accounts connected to the internet; and “cold storage,” which is an offline, hardware-based form of storage. Cold storage is considered secure, while “hot wallets” are riskier, because—being linked to the web—they can (and often do) get hacked.
Common wisdom suggests that companies keep just as much crypto in hot wallets as necessary to keep accounts liquid, while the rest of the crypto should be kept in cold storage. However, FTX didn’t do that; instead, the report says it kept “virtually all” of its customers’ assets in hot wallets.
Did FTX not know that cold storage was more secure or something? Nope, worse than being too stupid to implement proper controls, the exchange’s leadership appears to have just not given much of a shit.
“The FTX Group undoubtedly recognized how a prudent crypto exchange should operate, because when asked by third parties to describe the extent to which it used cold storage, it lied,” the report states, listing off a number of examples in which FTX executives—including SBF—claimed that they kept users’ assets in cold storage. In one instance, the company told investors that, in keeping with industry best practices, it kept a small amount of crypto in hot wallets, while the rest was “stored offline in air gapped encrypted laptops, which are geographically distributed.” But this was, according to the report, just bullshit.
Instead, as the report notes, “the FTX Group made little use of cold storage” except in Japan, “where [it was] required by regulation to use” it.
Private Cryptographic Keys Were Left Unencrypted
Another totally idiotic thing that the FTX peeps did is keep clients’ sensitive cryptographic keys and seed phrases stored in plaintext documents that were apparently accessible by staff.
In crypto, the key or seed phrase is the password that gets you inside a user’s individual wallet. Suffice it to say, industry standards compel crypto exchanges to keep that information encrypted and, thus, safe from prying eyes. Not so, with FTX—which apparently kept keys that could open wallets worth tens of millions of dollars unencrypted, in plaintext, just lying around in AWS.
According to the report, this was part and parcel of a generally disorganized approach to security, in which “private keys and seed phrases used by FTX.com, FTX.US, and Alameda were stored in various locations throughout the FTX Group’s computing environment in a disorganized fashion, using a variety of insecure methods and without any uniform or documented procedure.”
The FTX Gang Didn’t Really Use Multi-Factor Authentication
SBF and his merry band of hipsters also apparently “failed to effectively enforce the use” of multi-factor authentication (MFA)—a very basic form of web security that pretty much everybody who works in an office knows about. The recently released report states that the crypto exchange’s leadership “failed to implement in an appropriate fashion even the most widely accepted controls relating to Identity and Access Management (“IAM”).” This included a failure to use MFA as well as single-sign on services—also widely considered to be an industry best practice.
And much, much more!
There are a lot of other hilarious jewels of security negligence that FTX appears to have committed, so I’d suggest reading the full report if you want your jaw to drop to the floor.
The earnings season for the banking sector will start off with HDFC Bank’s success scheduled to be declared on April 15 adopted by ICICI Lender’s on April 22.
Motilal Oswal expects credit progress of 15.7{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1} on year for the banking sector in FY23 and 13.3{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1} in FY24.
As deposit charges have been mounting with hike in desire prices, analysts are favourable on deposits but worry about credit growth amid high borrowing premiums.
Banking institutions are envisioned to report a healthy credit score expansion in the January to March quarter driven by traction in retail, little and medium organization (SME) and company shoppers, as per analysts at Motilal Oswal.
The earnings year for the banking sector will commence with HDFC Bank’s benefits, scheduled to be introduced on April 15, adopted by ICICI Bank’s on April 22.
The brokerage residence expects credit rating progress of 15.7{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1} on 12 months for the banking sector in FY23 and 13.3{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1} in FY24.
While the credit score book of the corporate section witnessed a gradual recovery, a pick-up in capex among the corporates would be key to maintain development momentum ahead.
“Home, vehicle, unsecured, and little company segments carry on to do well, though demand for commercial vehicles is also improving upon. The credit score card company is seeing nutritious momentum, with sturdy progress in spends,” said the report by Motilal Oswal.
Financial institution deposits up with charge hikes but credit score advancement value viewing As deposit fees have been soaring with hike in fascination premiums, analysts are positive on deposits, but get worried about credit rating advancement amid higher borrowing fees.
Considering the fact that May possibly 2022, RBI has hiked the repo charge six occasions, creating bank deposits appealing once again. This is reflected in the wholesome advancement in lender deposits in the March quarter. HDFC Financial institution on Tuesday claimed potent advancement in deposits and advances with 21{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1} development in deposits and 16.9{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1} in innovations at ₹18.8 lakh crore and ₹16 lakh crore respectively as on March 31, 2023.
At the same time, non-public sector loan company Bandhan Bank’s innovations grew 9.8{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1} and deposits jumped 12.2{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1} in the March quarter.
“Deposit costs have elevated sharply above the earlier couple months, with legal responsibility accretion attaining great importance. However, the hole v/s credit score progress even now continues to be significant. When we expect a steady-favourable bias in margins in 4QFY23, the increase in the cost of deposits and further more fee hikes would affect the margin trajectory in FY24. Margins are very likely to see some strain in FY24, in our watch,” said the report by Motilal Oswal.
This 7 days will present course to the sector growth going in advance as the Reserve Lender of India is predicted to announce a choice on fascination level hike in its bi-monthly financial plan this Thursday. Economists are expecting an increment of 25 foundation points in the repo rate to 6.75{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1}.
Even more, any improve in the desire ecosystem, taking into consideration the tough macro problem, elevated inflation and a higher base impact are critical monitoring points for the sector.
Hope muted income advancement for IT sector in Q4 amid weak macro Earnings time for the details engineering expert services sector will commence with the outcomes of Tata Consultancy Companies that will be out on April 12 followed by Infosys on April 13 and HCL Systems on April 20.
Motilal Oswal expects muted earnings growth for the sector as weak macroeconomic aspects like the modern banking disaster in the essential marketplaces of the US and Europe may possibly effect expending by banking institutions there.
“Our IT Providers coverage universe is anticipated to deliver a median profits expansion of .8{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1} quarter-on-quarter and 9.2{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1} 12 months-on-year in continuous currency (CC) terms in 4QFY23,” said a report by Motilal Oswal.
The report suggests that even though Indian IT products and services companies do not have meaningful exposure to the affected US regional banking companies, fears of a banking disaster could effects near-time period IT expending by banking companies.
Furthermore, the impact of the disaster in the companies’ March quarter earnings will be the important monitorable throughout the 4Q administration commentaries.
“Apart from banking, economic services and insurance policy (BFSI), hello-tech, manufacturing and retail may well also report muted progress in 4Q. Consumers have started out to slice discretionary spends whilst raising aim on expense efficiency. IT expert services providers are looking at a change to value optimisation specials, together with greater seller consolidation specials in the pipeline,” explained the report.
SEE ALSO: Forbes Billionaires 2023: 3 of India’s 16 newcomers on the record are gals Bank loan advancement exhibiting symptoms of reversal from cyclical highs, but asset high-quality to remain nutritious
Regardless of a tumultuous 12 months, the volume of people today working in the technological know-how sector has grown, in accordance to new exploration from CompTIA.
The company’s annual State of the Tech Workforce uncovered that web tech work grew by 3.2{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1} in the United States in 2022, with the range of people utilized in technologies escalating by an approximated net new 286,400 staff.
Extra than 9.1 million people today work in tech work, spanning equally technical and non-technical employees utilized by tech companies and tech specialists who do the job in industries across the economic system, the company said.
Tech Position Advancement
All 50 states and the District of Columbia observed improves in tech work in 2022. Texas led the country in net tech employment advancement, including an approximated 45,331 careers. The other prime states involved:
California (+38,186)
Florida (+22,029)
New York (+18,487)
Washington (+17,962)
Possibly additional interesting, the range of tech-related employment options also grew in states not historically thought of as tech hubs. Those included:
South Carolina (+3,853)
Indiana (+3,525)
Alabama (+2,430)
Kansas (+1,786)
Idaho (+1,503)
Unsurprisingly, the Silicon Valley corridor of San Francisco to San Jose continues to be an vital careers progress engine. However, the analyze showed that, in excess of the earlier five decades, 86{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1} of tech employment growth transpired in other metro parts across the place.
Tim Herbert, main investigation officer for CompTIA, commented:
“In a 12 months of even much more uncertainty than typical, the tech labor market place routinely defied expectations. The data carries on to validate the degree to which technological know-how underpins so several aspects of company exercise across the economic climate and the breadth of businesses reliant on complex and electronic techniques.”
The pandemic’s influence on tech work did not go unnoted, with 34{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1} of employer task postings for tech positions specifying get the job done-from-property or hybrid get the job done choices – somewhat extra than 1.4 million positions. That is a 146{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1} increase over the pre-pandemic charge, the researchers explained.
The Upcoming State of Tech Work
On the lookout ahead, CompTIA forecasts a 3{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1} maximize – much more than 272,000 new careers – in tech employment for 2023. The distinct occupations poised for growth, according to the researchers, are data scientists and analysts (5.5{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1}), cybersecurity analysts and engineers (5.2{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1}), website designers and UI/UX experts (4.7{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1}), software program developers and engineers (4.7{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1}), and computer software good quality assurance and testers (4.1{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1}).
Just over 30{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1} of all tech jobs postings were for occupations linked to rising technologies or for positions that essential emerging tech expertise. New York Metropolis, Washington, D.C., San Francisco, Dallas and Los Angeles ended up the leading 5 metropolitan areas for emerging tech position postings.
In 2022 by yourself, global cyberattacks elevated by 38{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1}, ensuing in considerable business enterprise reduction, such as economic and reputational problems. Meanwhile, company protection budgets have risen drastically simply because of the escalating sophistication of attacks and the number of cybersecurity methods introduced into the sector. With this rise in threats, budgets, and options, how prepared are industries and nations to effectively tackle present day cyber danger?
CYE’s new Cybersecurity Maturity Report 2023 tackles this issue by shedding mild on the power of cybersecurity in distinct sectors, organization sizes, and countries. It highlights which industries and international locations have the most robust cyber postures and which are lagging, as effectively as the most commonplace vulnerabilities in present-day cyber risk landscape.
The investigation is based mostly on two years’ well worth of details, collected from more than 500 organizations in 15 countries, and spanning 11 industries and a variety of enterprise measurements. It actions cybersecurity maturity throughout 7 unique protection domains, together with software degree security, community level security, identification administration and remote entry, and far more.
Listed here are the top findings:
Finding #1: Much larger Budgets You should not Automatically Signify Improved Cybersecurity
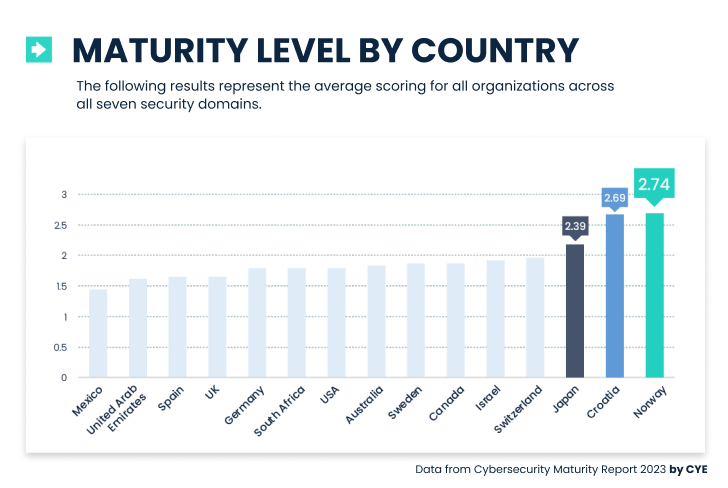
Among the nations, Norway scored the greatest on in general cybersecurity maturity level, adopted by Croatia and Japan. Whilst these international locations do not have the significant cybersecurity budgets of countries these kinds of as the US, United kingdom, and Germany, they do have state-of-the-art regulatory programs. Other feasible motives that Norway, Croatia, and Japan took the direct include early cybersecurity adoption in these countries and unified arranging by governments and companies. This obtaining illustrates how big economical investments do not necessarily translate into significant maturity amounts.
Acquiring #2: Tech Businesses Rating Typical
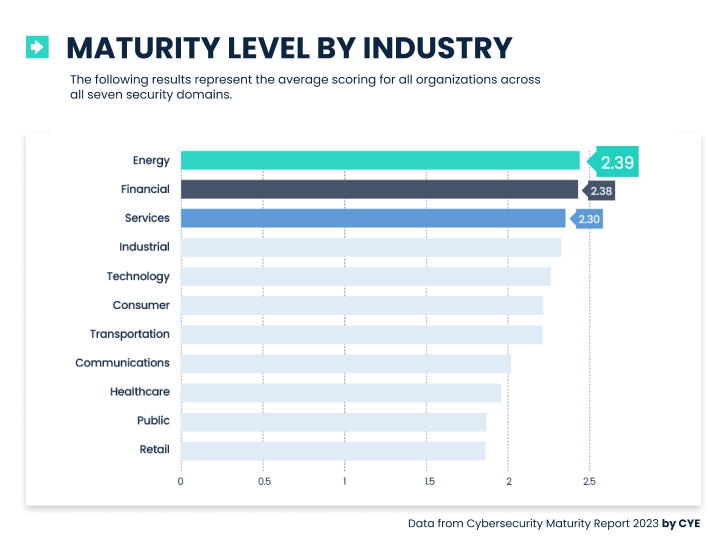
Amongst sectors, electrical power and economic industries arrived out on major for in general cybersecurity maturity amount, though healthcare, retail, and federal government businesses ended up among the the most affordable. Amazingly, the tech business scored about common, which is quite possibly simply because of the larger sized attack surface area this sort of businesses typically need to protect in comparison to other sectors.
The average rating could also be because tech companies are inclined to adopt new technologies that could be notably susceptible to assaults and exploits. In addition, tech companies are inclined to experience growth a lot a lot quicker than other sectors, which can be an added obstacle when striving to retain a solid cyber posture.
Finding #3: Modest and Medium Corporations Score Bigger Than Massive Companies
Incredibly, modest- and medium-sized companies experienced better cybersecurity maturity scores than organizations with about 10,000 staff members. This could be due to the fact little businesses may well have an easier time defending their tiny attack surfaces. With medium-sized organizations, investing in cybersecurity options is clearly a priority. When it will come to big businesses, however, obtaining to protect this sort of a huge attack surface area plainly has an result on the degree of cybersecurity maturity.
Getting #4: Approximately A single-Third of Businesses Deficiency Effective Password Guidelines
The research found that 32{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1} of companies had been identified to have weak password policies—a highly solvable problem that firms apparently have not sufficiently tackled. In addition, 23{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1} of corporations had been observed to have weak authentication mechanisms. This is regarding, mainly because the blend of the two challenges empowers hackers, who can then just log in with minimum effort.
Recommendations for Improved Cybersecurity Maturity
The all round takeaway from the report is that most corporations are not adequately ready for the threat of cyberattacks. Having said that, companies can still accomplish a large cybersecurity maturity posture without having a substantial spending plan, if they strategy and expend effectively.
To secure themselves, companies should invest in abilities, relatively than applications complete extensive assessments to stop hackers from exploiting vulnerabilities and acquire an integrated tactic to cybersecurity with board-amount accountability. Cybersecurity optimization options this sort of as CYE can help by combining technological innovation, people today, and processes to deal with organizational cyber possibility and accomplish cyber threat quantification to understand threats and prioritize mitigation.
The US government and cybersecurity instruments are effectively preventing specific cyberattacks, per the WSJ.
One hacker group reportedly let go of 45 connect with-centre operators.
More nations around the world are targeting payments produced to appease ransomware attackers, in accordance to Gartner.
Many thanks for signing up!
Obtain your favorite subject areas in a individualized feed even though you are on the go.
Hackers and others perpetuating ransomware threats feel to be the latest tech market workers navigating a shaky position sector.
As US Section of Justice investigators and firms beef up their oversight of cybersecurity threats, the impression of ransomware attacks — hackers need ransom payments from targets — has been blunted, in accordance to a Wall Road Journal report.
The amplified vigilance has led to declines in equally the number of these kinds of on the internet ransomware assaults that specified cybersecurity industry experts fielded past yr and the dimension of ransom payments that hackers had been attempting to get for them, cybersecurity teams told the WSJ.
Just one hacker group termed Conti even laid off 45 get in touch with-middle operators last yr who have been functioning as portion of an evident scheme to unfold ransomware attacks just after the get in touch with facilities unsuccessful to make dollars, the publication noted, citing an government at Red Sense, an intelligence firm.
Ransomware hacks can have large stakes, specifically when hackers blackmail targets around personal facts in order to extract payments.
The DOJ has signaled in new many years that it is ramping up its policing of cybercrime. In 2021, the agency designed new groups internally, together with the Nationwide Cryptocurrency Enforcement Team and the Ransomware and Electronic Extortion Job Force.
Such efforts have assisted the DOJ look into and extradite alleged hackers to the US, the agency explained. For occasion, federal prosecutors stated previous 12 months that they brought in a guy who experienced been detained in Poland to surface prior to a federal courtroom. The company stated he experienced used the Sodinokibi/REvil ransomware against firms like software package agency Kaseya.
The agency has also stepped up its oversight amid higher-profile assaults on domestic infrastructure, which includes the Colonial Pipeline hack that influenced a 5,000 mile fuel pipeline serving the East Coastline of the US in 2021.
In the DOJ’s cybersecurity report in July, the section reported it experienced been hunting into far more than “100 variants of ransomware” and groups it “suspected of triggering about $1 billion in losses to victims.”
Countries are typically also stepping up their oversight of ransomware assaults and hoping to increase privacy laws, according to the analysis and consulting firm Gartner.
Close to a third of nation-states are predicted to devise laws governing ransomware by 2025, the company reported in a June report on its anticipated cybersecurity tendencies in the next year. In 2021, that figure was smaller than 1{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1}, in accordance to the report.