
KamiKakaBot Malware Used in Latest Dark Pink APT Attacks on Southeast Asian Targets

KamiKakaBot Malware Used in Latest Dark Pink APT Attacks on Southeast Asian Targets

Mar 13, 2023Ravie LakshmananCyber Attack / Malware

KamiKakaBot Malware Used in Latest Dark Pink APT Attacks on Southeast Asian Targets

The Dim Pink state-of-the-art persistent menace (APT) actor has been connected to a fresh new set of assaults concentrating on government and army entities in Southeast Asian nations with a malware known as KamiKakaBot.

Darkish Pink, also identified as Saaiwc, was very first profiled by Team-IB previously this calendar year, describing its use of custom made tools such as TelePowerBot and KamiKakaBot to run arbitrary instructions and exfiltrate delicate information and facts.

The threat actor is suspected to be of Asia-Pacific origin and has been lively since at minimum mid-2021, with an enhanced tempo observed in 2022.

“The newest assaults, which took spot in February 2023, were being practically equivalent to former assaults,” Dutch cybersecurity firm EclecticIQ disclosed in a new report revealed very last week.

“The main change in the February marketing campaign is that the malware’s obfuscation routine has improved to far better evade anti-malware measures.”

The attacks engage in out in the kind of social engineering lures that have ISO image file attachments in e-mail messages to produce the malware.

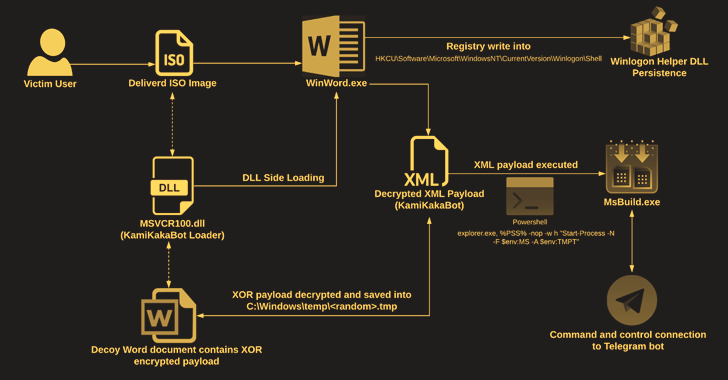
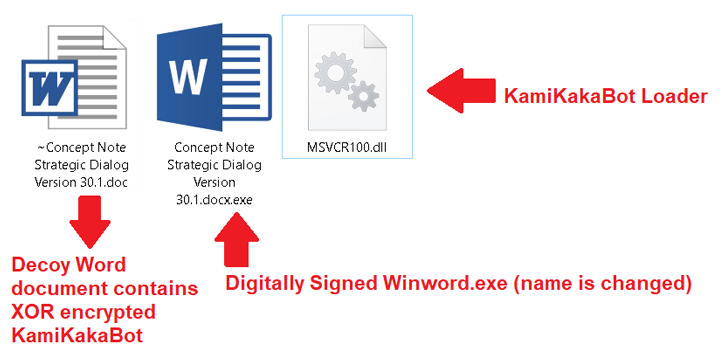
The ISO graphic involves an executable (Winword.exe), a loader (MSVCR100.dll), and a decoy Microsoft Phrase document, the latter of which will come embedded with the KamiKakaBot payload.
KamiKakaBot Malware

The loader, for its part, is made to load the KamiKakaBot malware by leveraging the DLL side-loading system to evade protection protections and load it into the memory of the Winword.exe binary.

KamiKakaBot is generally engineered to steal facts stored in net browsers and execute distant code using Command Prompt (cmd.exe), even though also embracing evasion tactics to mix in with victim environments and hinder detection.

WEBINAR

Find out the Concealed Dangers of Third-Party SaaS Apps

Are you conscious of the hazards related with third-bash application access to your company’s SaaS applications? Sign up for our webinar to learn about the types of permissions currently being granted and how to limit danger.

RESERVE YOUR SEAT

Persistence on the compromised host is accomplished by abusing the Winlogon Helper library to make destructive Home windows Registry key modifications. The gathered facts is subsequently exfiltrated to a Telegram bot as a ZIP archive.

“The use of legitimate website companies as a command-and-manage (C2) server, these as Telegram, remains the variety 1 decision for various menace actors, ranging from normal cyber criminals to sophisticated persistent menace actors,” the Amsterdam-centered company explained.

“The Dim Pink APT group is very probably a cyber espionage-determined menace actor that especially exploits relations between ASEAN and European nations to produce phishing lures through the February 2023 campaign.”
Identified this short article exciting? Abide by us on Twitter and LinkedIn to read through a lot more exceptional information we write-up.

Samsung Introduces New Feature to Protect Users from Zero-Click Malware Attacks

Samsung Introduces New Feature to Protect Users from Zero-Click Malware Attacks

Feb 20, 2023Ravie LakshmananCell Protection / Zero Working day

Samsung Introduces New Feature to Protect Users from Zero-Click Malware Attacks

Samsung has introduced a new characteristic referred to as Message Guard that arrives with safeguards to guard people from malware and adware through what is referred to as zero-click on attacks.

The South Korean chaebol claimed the alternative “preemptively” secures users’ units by “restricting exposure to invisible threats disguised as image attachments.”

The stability feature, available on Samsung Messages and Google Messages, is at present constrained to the Samsung Galaxy S23 collection, with strategies to extend it to other Galaxy smartphones and tablets afterwards this 12 months that are jogging on Just one UI 5.1 or larger.

Zero-click on attacks are remarkably-focused and subtle assaults that exploit earlier mysterious flaws (i.e., zero-days) in software to bring about execution of destructive code with out demanding any user interaction.

Unlike classic strategies of remotely exploiting a machine wherein threat actors count on phishing techniques to trick a consumer into clicking on a destructive backlink or opening an rogue file, these assaults circumvent the will need for social engineering fully and provide an adversary with an entry stage.

A the greater part of the zero-click exploits are engineered to consider gain of vulnerabilities in apps these types of as messaging, SMS, or electronic mail applications that receive and approach untrusted knowledge.

As a consequence, if there exists a stability vulnerability in the manner an app interprets the incoming information, a threat actor could weaponize this shortcoming to craft a malicious impression that, when despatched to a target’s machine, immediately executes the code embedded within just it.

The absence of interaction included in zero-click on attacks indicates there are much less traces of any nefarious exercise, making them hugely-prized equipment to produce spy ware capable of monitoring people and harvesting a prosperity of delicate information.

Zero-Click Malware Attacks

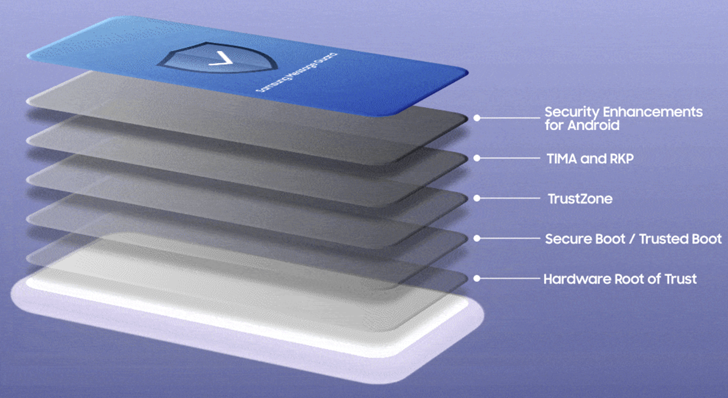
Samsung’s Information Guard is effective versus a range of image formats, which includes PNG, JPG/JPEG, GIF, ICO, WEBP, BMP, and WBMP, and effectively acts as a sandbox that is made to quarantine photographs obtained by means of the app from the relaxation of the functioning method.

“Information Guard checks the file bit by bit and processes it in a controlled atmosphere to make sure it simply cannot infect the relaxation of your unit,” the firm said.

The function is also analogous to a element in Apple’s iMessage termed BlastDoor that the tech large included in iOS 14 as a means to counter zero-click attacks by way of its messaging app.

Apple, final calendar year, also released an “intense, optional protection” placing dubbed Lockdown Manner that hardens iPhones and iPads versus “really rare and very advanced cyber assaults.”

Discovered this report appealing? Observe us on Twitter and LinkedIn to examine far more exclusive material we post.