
Make Sure Your Cybersecurity Budget Stays Flexible

Make Sure Your Cybersecurity Budget Stays Flexible

The tsunami of cyberattacks in recent several years has wreaked havoc among businesses’ infrastructures and drowned quite a few defense methods throughout all industries. Incorporating added strain is the point that cyberattacks are normally connected to world activities. For occasion, hackers have exploited the vulnerabilities within just progressively complex distant work infrastructures ignited by the pandemic, presenting new challenges for security leaders. The reality is, these days hackers aren’t breaking in — they’re logging in by using human-dependent assaults.

With today’s uncertain overall economy and superior inflation prices, this year’s spending budget forecast phone calls for dry disorders throughout the security landscape. This year’s budgets now have been accepted, but vital priorities might shift throughout the 12 months — earning comprehending when and how to pivot limited budgets a important element of guaranteeing the stability of CISOs’ infrastructures.

A single technique CISOs are pursuing is to apply comparable ideas as attackers who are exploiting economic, social, and technical disruptions within just modern society.

Priorities to Contemplate When Shifting Budgets

With the switching mother nature of the financial state and workforce constructions, there are numerous diverse things to look at when executing a correctly informed funds shift. So, from 1 CISO to another, below are 5 critical priorities for stability leaders to look at when getting ready for possible price range shifts this 12 months and further than:

  1. Geopolitical influences of cybersecurity: Hackers have developed their assaults to exploit geopolitical disruptions. These impacts, like the war in Ukraine, have refined the use of common attack types to improve the good results of attackers’ ransomware efforts.For occasion, Russian hackers this sort of as the Conti ransomware group have thwarted US and worldwide war attempts to assist Ukraine via the concentrating on and injection of ransomware into corporations working in critical infrastructures. A short while ago, the popular approaches leveraged to infect corporations with ransomware across the world consist of password spraying, spear-phishing, and credential stuffing. Owing to these progressively refined assaults, CISOs must combine technological defense techniques capable of thwarting assaults that are continually evolving.
  2. Uncertain economic climate: Desperate instances contact for determined measures, and historically, unsure financial durations mean an maximize in cyberattacks. Attackers are leveraging state-of-the-art technologies to have interaction in substantial-risk, identification-linked fraud practices to steal staff credential details and extort businesses. In fact, considering that 2021, there has been extra than a 60{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1} increase in corporate email compromises, top to added enterprise losses totaling above $40 billion.

    As present economic standings reel in uncertainty, CISOs should prepare to alter their budgets towards ongoing hazard management, with distinctive emphasis on tools that will assist mitigate human mistake. From compliance to threat assessments, techniques will need to revolve about minimizing superior-chance identity assaults.

  3. Evolving laws: As we know, cybersecurity is ever-evolving. This usually means that new polices are constantly designed — and others that are already in result, these types of as GDPR and CCPA, are turning out to be stricter. The present problems concerned with adhering to dynamic — and usually overlapping, field-focused, regional, and cross-nations prerequisites — can trigger very the headache for security leaders. So, how can CISOs repeatedly comply in an increasing safety landscape?

    The appropriate financial commitment in thorough defense measures, this sort of as zero-have faith in access, will make certain the stability of enterprises’ info, aiding them continue to be compliant and adherent to the variety of crossover regulation.

  4. Teaching: In the cybersecurity field, CISOs and safety leaders won’t be able to pay for for their enterprises to be impacted by the current expertise hole. A lack of competent staff can end result in potentially devastating vulnerabilities in just their infrastructure.

    Stability leaders will have to thoroughly prepare for paying reprioritizations as the competencies gap widens. This makes certain that their workforce has the needed awareness to engage in powerful in-dwelling modern day reskilling and upskilling strategies. One particular vital spending plan shift could be towards the implementation of assistive, highly developed cloud-based mostly services, these types of as high-hazard identity administration answers, which can also be built-in to reinforce the organization’s electronic infrastructure.

  5. Fashionable strategies: At this time, 80{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1} of breaches count on personnel entry qualifications. To increase their defenses, CISOs must confirm their latest procedures are proficient ample to combat the continuous inflow of human-centered attack kinds, like Kerberoasting and go-the-hash attacks. If infrastructures are unstable and priorities want to change, CISOs can switch to frequent equipment, which include zero-rely on entry and significant-hazard identity-centered manage alternatives — which can fight developing offense attempts.

    As identity-centered assaults rise, corporations will have to have security tools programmed to have faith in no just one, not even their possess sellers. This will improve compliance steps and permit the protection and sole ownership of inner, exterior, third-occasion, purchaser, and stakeholder’s person knowledge. It will also make it possible for for more powerful authentication, the monitorization of interior and exterior user operations, and the halting of lateral motion inside businesses’ infrastructures.

    As cyber threats evolve, companies will will need to retain speed and allocate for improved security methods that give seamless management in their budgets.

Evolution Is Critical

Hackers will proceed to change their methods of attack and exploit the vulnerabilities in latest world-wide geopolitical events. To prevent them, protection leaders will want to make guaranteed their latest budgets can pivot and are adaptable sufficient to deploy modern defense strategies and technologies, and capable of handling precedence shifts as the 12 months progresses.

This involves leaders taking the recent financial, social, and technological factors into thought though producing their defense approach. Performing so will assistance them make extra educated decisions around the ideal use of their cybersecurity budgets for the upcoming calendar year and beyond.

Hold up with the most recent cybersecurity threats, freshly-learned vulnerabilities, information breach information, and emerging trends. Shipped daily or weekly suitable to your e-mail inbox.

Cybersecurity is a ‘resilient industry’ in spite of recession fears: CrowdStrike CEO

Cybersecurity is a ‘resilient industry’ in spite of recession fears: CrowdStrike CEO

Fears of an financial downturn or possible economic downturn, not to mention bigger curiosity premiums, could have some businesses slicing expending on things like cloud computing, but CrowdStrike (CRWD) CEO George Kurtz claims the very same just cannot be mentioned of cybersecurity paying.

“Cybersecurity is anything you may possibly be able to pause, but you can not place off indefinitely,” Kurtz instructed Yahoo Finance Live. “That’s definitely what we’ve been looking at.”

In accordance to a survey of 1,000 business executives done by the International Info Technique Safety Certification Consortium (ISC)2, a nonprofit that gives education certifications for cybersecurity workers, cybersecurity employees are the least probable to deal with layoffs in a economic downturn.

The cause? The danger of cybercrime tends to boost during recessions and financial downturns, as criminals appear for new ways to get paid funds. What’s far more, the cybersecurity market is already experiencing a significant worker scarcity, with (ISC)2 expressing the international cybersecurity workforce has to grow by 3.4 million workers to address the world’s safety demands.

And according to Kurtz, that danger coupled with an at any time-evolving cybersecurity surroundings suggests that companies basically are not keen to reduce their cybersecurity budgets at this stage.

“Organizations are searching to shield on their own. There are mandates from the board, there are compliance mandates, and it unquestionably is a resilient business,” he reported. “What we have observed is that budgets are modestly up in some circumstances, other people flat. But we have not seriously observed them go down.”

Sign up for Yahoo Finance's tech newsletter.

Sign up for Yahoo Finance’s tech e-newsletter.

The Biden administration, in the meantime, is trying to realign conversations all over cybersecurity to put more emphasis on corporate accountability for shielding essential data.

According to the administration’s approach, individuals, compact firms, and area municipalities shouldn’t bear the stress of working with highly developed cyberthreats. Alternatively organizations that can improved insulate those groups from criminals should really.

Which is precisely what Jen Easterly, director of the Cybersecurity and Infrastructure Protection Agency explained to Yahoo Finance at CES 2023 in January. Easterly says she thinks firms like Microsoft, Amazon, and other individuals want to strengthen their protection posture to prevent downstream protection lapses from turning into significant intrusions for smaller sized companies that don’t have the assets to react to these types of threats.

Photo by: STRF/STAR MAX/IPx 2020 12/24/20 Suspected Russian hackers made failed attempt to breach CrowdStrike. STAR MAX File Photo: 12/3/20 A CROWDSTRIKE logo shot off an iphone SE 2020.

Photo by: STRF/STAR MAX/IPx 2020 12/24/20 Suspected Russian hackers designed failed attempt to breach CrowdStrike. STAR MAX File Picture: 12/3/20 A CROWDSTRIKE brand shot off an apple iphone SE 2020.

“We’ve basically accepted as normal that technological know-how is produced to market place with dozens or hundreds or 1000’s of vulnerabilities and problems and flaws,” Easterly explained through a discussion at the trade clearly show.

“We’ve recognized the point that cyber safety is my work and your position and the occupation of my mother and my kid, but we’ve set the stress on consumers, not on the providers who are most effective outfitted to be in a position to do a thing about it.”

For his component, Kurtz states cybersecurity is a shared obligation.

“When we assume about program in basic. When you appear at Microsoft, there were 30 zero-day vulnerabilities [exploitable flaws with no fix yet],” he said. “So there’s a shared duty in creating confident that application, like Windows, is really secure.”

Acquired a suggestion? E-mail Daniel Howley at dhowley@yahoofinance.com. Comply with him on Twitter at @DanielHowley.

Click listed here for the most up-to-date inventory industry information and in-depth assessment, together with situations that shift stocks

Read the most up-to-date money and organization news from Yahoo Finance

New gov’t cybersecurity strategy rolls out amid AI buzz, concerns it could be abused by criminals

New gov’t cybersecurity strategy rolls out amid AI buzz, concerns it could be abused by criminals

The Biden administration is shifting to carry out a new countrywide safety technique focused on halting hackers, as buzz about artificial intelligence applications raises issue between some specialists that criminals may possibly attempt to exploit AI abilities.

One particular goal of the administration system is to change the concentrate of blame away from the victims of cybercrime, U.S. stability officials mentioned. Soon after-the-point assessments usually concentrate on the focus on for currently being vulnerable adequate to hack — but if that target is a rural clinic, for instance, limitations could exists on what that clinic can do to shield against bad actors, particularly individuals backed by foreign governments.

As a substitute, the new program focuses on strengthening the general public-personal partnerships that inspire safety companies to share what they know about hacker networks in buy to convey them to justice.

Rising technological know-how will test the viability of the approach heading forward, experts informed ABC Information, specifically with AI posing new security issues.

The similar positive aspects witnessed in AI applications like ChatGPT from study lab OpenAI, which formulates human-like responses to issues posed by a person, are vulnerable to nefarious use, in accordance to Ari Jacoby, a tech govt who has targeted on working with AI to combat fraud.

A lot more: Possible hacking victims could be underprepared for threats from the shadows: Report

Specified the volumes of publicly obtainable details on software program engineering, hackers could use the chat bots to create or enrich destructive computer system code, Jacoby said.

According to OpenAI’s person coverage, applying ChatGPT to write malware, generate hateful or destructive content or interact in fraudulent action is explicitly prohibited. The problem is no matter if tech corporations are capable of enforcing these types of rules as AI engineering spreads.

“The ChatGPTs of the globe — who do way additional great than damage — make accessible resources that can write software package code in significantly less than a moment that would have taken a poor actor or a undesirable network most likely times or weeks to run,” Jacoby said.

As a substitute of using ChatGPT to supply tips for recipes or generate simple perform e-mail, terrible actors could try to compose significant volumes of phishing e-mail that trick recipients into downloading malware or supplying up own monetary details.

Alternatively, similar equipment applied to examine and evaluate trends in significant sets of knowledge can likely be employed to struggle fraud, Jacoby explained. Credit score card firms, for example, could reward from remaining capable to detect anomalies in a customer’s actions to ascertain if buys are reliable.

In the meantime, the U.S. is dealing with a every day onslaught of cybersecurity breaches from Russian, Chinese and North Korea-backed groups, according to recent U.S. government assessments and personal cyber intelligence firms. Experts assume those initiatives will exam the resilience of the administration’s new cyber tactic.

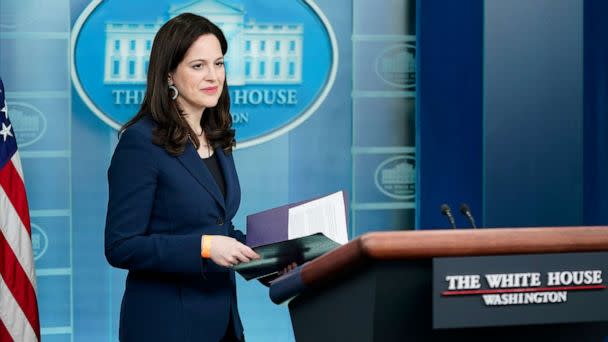
PHOTO: In this March 21, 2022 file photo Anne Neuberger, Deputy National Security Advisor for Cyber and Emerging Technology, arrives to speak at a press briefing at the White House in Washington. (Patrick Semansky/AP, FILE)

Photo: In this March 21, 2022 file photo Anne Neuberger, Deputy Nationwide Stability Advisor for Cyber and Emerging Know-how, arrives to communicate at a push briefing at the White House in Washington. (Patrick Semansky/AP, FILE)

“They are unbelievably complex and they are unbelievably properly-funded and nicely-tooled,” Jacoby explained. “They have a great deal of AI instruments at their disposal.”

A latest analysis of underground hacking communities by the cyber company Test Level Study observed on the net boards where by new approaches to hacking tools ended up reviewed, including a person discussion thread identified as “ChatGPT – Advantages of Malware.”

The author wrote they had been trying to use ChatGPT to recreate destructive computer code based on research papers about hacking.

Whilst the Biden administration’s tactic does not delve into the specifics of emerging technological innovation, these as AI, it truly is intended to be nimble enough to account for new developments in the promptly modifying cybersecurity landscape.

Additional: Cybersecurity industry experts split down a cyberattack as they become escalating menace

“These are multi-year initiatives where by we are going to uncover gaps and wherever Congress will then have to have to lean in to assistance us get to wherever we have to have to go,” acting National Cyber Director Kemba Walden stated at a forum dialogue of the strategy previous 7 days. “It’s a symphony, not a solitary movement.”

“This is an ongoing procedure,” she added.

Walden emphasized the significant position that cloud computing company providers play in securing data as a “pressure multiplier” for cyber threat first responders.

Google Cloud, for instance, delivers a wide variety of knowledge storage and internet site hosting providers. The company’s ability to defend its units was bolstered by its acquisition of the cybersecurity agency Mandiant past 12 months.

“Absolutely everyone has a shared duty below,” explained Stacy O’Mara, who leads govt tactic and partnership at Mandiant. “I believe that is the objective of the system — to strengthen this principle of a shared protection.”

“We’ve obtained a extended system in advance of us,” O’Mara claimed, ” but I’m encouraged by the administration’s initiatives.”

New gov’t cybersecurity tactic rolls out amid AI buzz, worries it could be abused by criminals initially appeared on abcnews.go.com

NIST launches cybersecurity community of interest for small businesses

NIST launches cybersecurity community of interest for small businesses

The Countrywide Institutes of Requirements and Technological innovation has introduced a new cybersecurity neighborhood of interest for small businesses across the United States.

Senior leaders at the Office of Commerce company on Monday declared the new system at an party at its Cybersecurity Centre of Excellence in Maryland.

The launch of the initiative arrives following the Biden administration last week issued a new National Cyber Strategy, which sought to “fundamentally reimagine” America’s cyber social deal, notably by shifting the duty for protecting the security of pc units away from individuals and smaller corporations on to more substantial software program makers.

The program is intended to foster larger collaboration in between NIST and small enterprises that the two offer and take in cybersecurity expert services. Senior officials say it is anticipated to assist strengthen the two-way sharing of details and very best methods that has fashioned a cornerstone of the Biden administration’s cybersecurity policy.

Deputy Secretary of Commerce Don Graves at the function underscored the value of NIST’s connection with the personal sector and its get the job done to provide business owners with distinct, actionable cybersecurity guidance.

“NIST’s modest small business local community of interest, which will not just contain but go outside of things to do that tumble below NCCoE’s cybersecurity connections energy, aims to improved reflect smaller companies’ requires – the passions and capabilities that they have – in all of NIST’s cybersecurity routines,” he reported.

Graves included: “So more compact businesses that take part in this effort and hard work will advise NIST’s selections about its wide portfolio of cybersecurity pursuits to ensure that they are as pertinent and powerful as ever. Yet again, functional methods – remedies that essentially get the job done for businesses, for communities all throughout the region. Irrespective of whether you’re below in Montgomery County, you’re in Idaho, you’re in rural Alaska … doesn’t seriously make any difference. They will support to make sure that NIST advice is equally significant and useful for the smaller organizations and other businesses to put into use.”

Through the function, NIST Performing Director Natalia Martin named on little businesses to use the new initiative to interact with the centre and reported it would acknowledge and be receptive to any input it gets.

“You have the option to make your voice heard, and we will constantly answer to you … please choose benefit of this opportunity,” Martin mentioned. “Every solitary venture we do, we inquire [the question]: What does this signify for small organization?”

NIST also in the course of the event celebrated the renewal of a collaborative partnership involving the agency’s Cybersecurity Middle of Excellence, the point out of Maryland and Montgomery County. It signifies the extension of a 3-way partnership that was very first signed when the heart was released in 2012, with the intention of aiding to speed up cybersecurity analysis and development even though guaranteeing nearby companies and communities advantage from connected innovation.

Cybersecurity Is Becoming A Priority For GCC Nations

Cybersecurity Is Becoming A Priority For GCC Nations

With world geopolitical instability elevating the threat of cyberattacks towards firms and governing administration organizations, the six nations of the GCC are quickly making much more sturdy and in depth cybersecurity procedures to answer to the evolving mother nature of cyberthreats.

In a January 2023 study of 117 world wide leaders from 32 international locations and 22 industries, 91{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1} of respondents considered that a considerably-reaching, catastrophic cyber-function was at minimum fairly probably in the subsequent two years, even though 43{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1} believed that a cyberattack would materially have an impact on their organisations. The findings were posted by the Environment Economic Forum (WEF) in its “Global Cybersecurity Outlook 2023”, created in collaboration with Accenture.

Cyber-resilience in the GCC

Because suffering from their to start with significant cyberattacks in the early 2010s, GCC countries have seemed at methods to bolster their cybersecurity by growing cyber-resilience and upgrading capability.

Having said that, Russia’s invasion of Ukraine in early 2022, which saw an enhance in the quantity and sophistication of global attacks, has prompted far more urgent action.

Some GCC international locations have now forged strong cybersecurity defences, according to the Portulans Institute’s “Network Readiness Index 2022”, which ranks nations around the world utilizing a host of metrics relevant to electronic transformation. In conditions of cybersecurity, Saudi Arabia rated 2nd globally behind the US, though the UAE rated eighth, Oman 28th, Qatar 34th, Bahrain 68th and Kuwait 73rd.

When these rankings suggest that the GCC is in a fairly potent situation, the typical price tag of cyberattacks is also higher in the area, with a knowledge breach costing $6.93m for every incident, previously mentioned the world wide common of $4.24m, in accordance to Mohamed Al Kuwaiti, running director of the Nationwide Info Centre below the UAE’s Supreme Council for National Security.

Al Kuwaiti designed this declare in December in Bahrain, which hosted the to start with Arab Intercontinental Cybersecurity Summit, a system for the world market to obtain entry to the region’s rising cybersecurity sector.

Presented the dimensions and scope of the challenge, the GCC has embraced political and technological cooperation. In October the GCC Ministerial Committee for Cybersecurity held its very first meeting in Riyadh at the headquarters of the GCC Secretariat Common, with the heads of cybersecurity from all 6 nations in attendance.

The meeting included issues of mutual desire and finished with programs to implement joint cybersecurity exercise routines to bolster the exchange of details and abilities and to produce the sector throughout the area.

Threats to electronic economies

The altering mother nature of cyberthreats is prompting a holistic reassessment of approach and techniques to cybersecurity. A key takeaway from the WEF’s outlook is that respondents imagine that cyberattacks are far more very likely to focus on producing business disruption and reputational damage likely forwards.

GCC nations have very long-time period strategies to diversify their economies absent from extractive industries in the direction of technological innovation and innovation and have already invested in a raft of technological advancements in synthetic intelligence (AI), facts and cloud computing. These options not only underscore the want for sturdy cybersecurity, but also need a a lot more holistic approach to guarding facts-driven networks.

“As info is more and more distributed in extensive networks, consumers are only as safe as their suppliers as a consequence, cybersecurity should put the focus on the integrity of the community, which requires each cybersecurity corporations and regulators to build mechanisms that allow for for the safety of info on the aspect of customers, distributors and partners,” Mirza Asrar Baig, CEO and founder of CTM360, a Bahraini digital possibility-protection enterprise, instructed OBG.

Meanwhile, momentum to expand the GCC’s intercontinental achieve in cybersecurity and ICT continues apace.

In November 2022 Saudi Arabia’s Nationwide Cybersecurity Authority (NCA) hosted the Global Cybersecurity Forum – initially held in 2020 – to deal with the macroeconomic, geopolitical and strategic issues shaping world cybersecurity.

Very last 12 months the NCA introduced the Countrywide Portal for Cyber Security Companies (HASEEN), a system that aims to create and control cyber-companies, guidance interaction mechanisms and boost cybersecurity capacities. All government businesses have entry to HASEEN, which the NCA options to use to conduct 7000 cybersecurity assessments in 2023.

In October Dubai’s Gitex International 2022 introduced collectively 10,000 programmers and builders from many intercontinental know-how businesses including US tech big Microsoft and 26 of its partners, which launched a slew of new systems for cloud computing, combined-actuality activities, AI and cybersecurity.

Last thirty day period, Saudi Arabia’s Ministry of Communications and Facts Engineering also held the next annual LEAP tech meeting, which developed a host of partnerships and about $16bn in expense, in line with Saudi Eyesight 2030 digitalisation aims.

“There is possible in the area to switch the area landscape, which is dominated by systems integrators, into a single with IT businesses driven by regional expertise and developing proprietary alternatives with a worldwide achieve, in cybersecurity and other areas,” Baig explained to OBG. “One of the key difficulties in recruiting IT professionals in the region is acquiring these keen to establish new alternatives from the ground up and who fully grasp that regional talent can produce innovation, relatively than replicating types applied elsewhere.”

Area potential building

Ambitions to bolster cybersecurity in the GCC will involve schooling initiatives to create neighborhood human ability.

In August 2022 the NCA released the CyberIC programme to develop countrywide capabilities and localise technological know-how enhancement in cybersecurity. The programme is slated to boost the number cybersecurity begin-ups by aiding much more than 60 countrywide companies, 40 by the cybersecurity accelerator programme and 20 via the cybersecurity obstacle.

Before final 12 months Saudi Arabia also set up Wamda, an initiative to foster the leadership competencies of female Saudi cybersecurity professionals.

In the meantime, Dubai Cyber Innovation Park held its 2nd Cybersecurity Bootcamp in February 2023 to train a specialised and qualified cybersecurity workforce from a pool of new graduates and other people looking to create a job in the discipline.

Bahrain’s labour fund Tamkeen is next match by graduating the initially cohort from its 8-thirty day period Cyber Security Teaching Programme conducted in partnership with SANS Institute, a cybersecurity teaching and education and learning service provider. Graduates are envisioned to deal with the needs of govt organisations and personal sector providers at the community and global level.

By Oxford Small business Group

Far more Leading Reads From Oilprice.com:

School cybersecurity expert weighs in: What’s happening in Minneapolis?

School cybersecurity expert weighs in: What’s happening in Minneapolis?

Minneapolis Public University college students and personnel returned to lecture rooms on Monday this 7 days, but disruptions prompted by an “encryption virus” —  including losing obtain to district accounts, units and shutting down just after-college routines —  ongoing throughout a lot of the week. 

“I assume the district is striving incredibly challenging not to flat-out say that they’ve seasoned a ransomware incident… But this has all the hallmarks of people types of incidents and that’s what I would take into account it to be,” stated Doug Levin, countrywide director of the K12 Stability Details Exchange and an professional on school cybersecurity.

Cybersecurity is becoming an progressively well known concern for public university districts.

In September of previous calendar year, the country’s next-greatest district was qualified. In accordance to Levin, there have been close to 200 comparable incidents focusing on both huge and smaller districts all over the state in the very last a few several years — and the ransom demanded has grown from $5-$10 thousand to nearer to $1 million or far more. 

What does that signify? The information, examination and local community conversation uncovered right here is funded by donations from persons. Make a gift of any total now to aid this useful resource for all people.

“(This is) affecting college districts from coast to coastline — from some of the greatest school districts in the country to considerably more compact and more rural faculty districts,” Levin reported. “I do believe that these incidents are going on additional frequently than people notice.” 

The Minneapolis district has moved from saying on Monday this 7 days that it’s discovered “no evidence” that personalized data was compromised, to emailing people that “an unauthorized menace actor might have been in a position to entry specific facts positioned inside of the MPS natural environment.”  

Here’s what Levin thinks you need to have to know about what is occurring in Minneapolis: What is a ransomware assault? 

A ransomware attack is carried out virtually completely by felony gangs functioning overseas, largely in Russia, according to Levin. 

The groups obtain accessibility to a pc method and make it unusable and then demand a payment from their victims.

Why is the Minneapolis college district not calling this a ransomware assault or currently being much more forthright? 

The Minneapolis faculty district has denied MPR News requests for interviews on the ongoing incident. In accordance to Levin, there could be several distinctive challenges at stake.

First, most states do not have reporting demands when it will come to what college districts are obligated to do when they knowledge a cyber attack. Most states also lack any kind of cybersecurity standard that university districts are demanded to adhere to.

Levin also posits the Minneapolis district may possibly be having suggestions from insurance policy suppliers or lawyers who are telling them they can restrict their liability if they stay away from making use of certain words and phrases in community communications. 

What really should families, pupils and workforce do to defend them selves? 

Levin implies people today linked to the district improve their passwords — particularly if they are reusing them on many accounts — help two-issue authentication, and preserve a closer eye on e mail, social media and financial accounts.

Dad and mom should freeze their minors’ credit rating accounts to stop identification theft (The Minneapolis district is directing persons to report major fraud or freeze credit by credit rating reporting bureaus this kind of as Equifax, Experian and TransUnion) . 

“Presume that information has been breached by felony actors,” Levin stated. “Take methods to guard your identity.” 

What ought to the Minneapolis General public Faculty district do likely ahead? 

Levin claimed it’s attainable the district will carry on to practical experience cyber assaults. 

“Unfortunately, a faculty method that on their own are victims of cybersecurity attacks like this a single are essentially rather most likely to practical experience repeat assaults likely ahead,” Levin said. 

He also implies families and employees question their board and district leaders to make guaranteed there is a devoted budget for cyber protection, and a strategy in location to handle cyber attacks when they happen. 

“What I would recommend for dad and mom… make absolutely sure that the university board and superintendent are making sure that the college system will take cybersecurity dangers just as very seriously as they choose pitfalls of physical violence on the university campus,” Levin stated. 

Do other Minnesota districts need to have to be concerned? 

Cyber assaults are becoming increasingly common, and have the probable to actually halt faculty programming and shut down devices. 

“At this position, offered the facts that we’ve noticed, it can be truly only a make a difference of time just before you know any individual school technique is a victim,” Levin explained. “We’ve viewed attacks in, you know, some of the major university districts from, you know, state to state to point out, as well, as lots of little ones.”

Levin factors college leaders to a the latest federal report on cyber safety threats to educational institutions, but also states districts may perhaps need help from condition and federal resources. 

“This is a escalating national disaster,” Levin stated. “While there are absolutely matters that we should and can hope superintendents and university boards to do, in the long run we’re going to have to have far more support from the condition and federal governing administration.”