LastPass hack: Cybersecurity experts sound the alarm over data breaches

LastPass hack: Cybersecurity experts sound the alarm over data breaches

Cybersecurity authorities are expressing worry in excess of the most current data breach suffered by password supervisor LastPass, as the cloud safety firm remains mum in the deal with of a course-motion lawsuit joined to numerous hacks on the organization past year.

LastPass initial alerted buyers in August 2022 that “an unauthorized bash obtained accessibility to parts” of its network by a developer’s compromised account, and determined at the time that no consumer info or encrypted password vaults were being accessed by the hacker.

LastPass logo phone

Cybersecurity experts are sounding the alarm above the prolong of safety breaches suffered by password supervisor LastPass. (Photo Illustration by Mateusz Slodkowski/SOPA Photos/LightRocket by way of Getty Photos / Getty Photos)

The enterprise then admitted a 2nd breach in late November, declaring another person utilized info accessed in the August hack to “attain entry to sure components of our customers’ information.” LastPass insisted users’ passwords remained safely and securely encrypted at that time.

But In the firm’s most recent weblog update on Dec. 22 regarding the safety incidents, LastPass CEO Karim Toubba acknowledged that a “danger actor” experienced copied a backup of shopper vault knowledge that integrated “fully-encrypted sensitive fields such as web page usernames and passwords, secure notes, and kind-milled data.” That has authorities sounding the alarm.

CHATGPT Being Used TO Write MALWARE, RANSOMWARE: Stories

Yiddy Lemmer, who owns IT support and cybersecurity company CompuConnect primarily based out of New York, advised FOX Business he continue to suggests men and women use password administrators to hold their details secure — but he no lengthier recommends LastPass. In reality, he stop employing LastPass himself a handful of weeks back just after identifying the extent of the breach.

internet hacker computer

A hacker was capable to access LastPass customer details in numerous stability breaches final 12 months. (Jakub Porzycki/NurPhoto by using Getty Visuals / Getty Illustrations or photos)

“When I learned the depths of how bad it was, I switched appropriate away,” Lemmer mentioned. “I am not heading to wait around all over for the next hack until it receives even worse.” Lemmer now makes use of LastPass rival Bitwarden to deal with his passwords.

Nashville, Tennessee-based mostly cybersecurity agency Galactic Advisors sent out a warning to buyers above the LastPass hack on Jan. 3, saying it experienced “gained data indicating that some of the unencrypted information” uncovered in the attack “could be made use of for extra than phishing.”

CHICK-FIL-A URGES Buyers TO Acquire Action, INVESTIGATES ‘FRAUDULENT ACTIVITY’ ON Mobile Application ACCOUNTS

The similar week, LastPass was strike with a course-action lawsuit from a former shopper who claims the hack resulted in someone accessing the non-public keys he had stored on LastPass to steal around $53,000 really worth of bitcoin.

LastPass hack

Password manager LastPass experienced multiple details breaches in 2022. (Image by Leon Neal/Getty Visuals / Getty Pictures)

LastPass CEO Toubba has not provided an update on the protection incidents on the company’s blog site given that Dec. 22, and the firm has not still responded to several requests for remark from FOX Enterprise.

Russ Reeder, CEO of cybersecurity company Netrix Global, claims it is essential for companies to offer obvious communications to both equally tell clientele and protect those people impacted by info breaches early on.

GET FOX Enterprise ON THE GO BY CLICKING Listed here

He extra, “It is terrifying when a password keeper enterprise we have all been educated to count on will get breached.”

LogMeIn declared in Dec. 2021 that it was spinning off LastPass as a standalone company. At the time, LastPass experienced 30 million end users and served a lot more than 85,000 companies.

AWS security heads offer top cybersecurity predictions for 2023

AWS security heads offer top cybersecurity predictions for 2023

Look at out all the on-demand periods from the Intelligent Protection Summit below.


Previous 12 months (2022) was an unprecedented 1 for cybersecurity, in the two fantastic and negative means. On the good side, we noticed elevated use of passwordless and multifactor authentication (MFA) and zero-rely on methods on the damaging, the expense of info breaches reaching an all-time large, the rise of commoditized cybercrime (ransomware-as-a-assistance), and significant breaches of Twitter, WhatsApp, Rockstar and Uber.

What could possibly we see in 2023? VentureBeat posed this problem to numerous AWS security leaders. Here are their best cybersecurity predictions for 2023. 

MFA will turn out to be pervasive

“MFA [multifactor authentication] adoption will go on to increase for both business and personal use, together with greater use of biometric forms of authentication that strengthen stability and convenience (that is, unlocking equipment with a fingerprint or face identification). 

“By going in this direction, the foreseeable future of MFA will blend sturdy security with usability, guaranteeing that consumers have a frictionless working experience whilst enhancing their stability posture. As just one of the most basic and most crucial protections, MFA is remaining inspired as a baseline on the net security by the FIDO Alliance, NIST and the U.S. government, which not too long ago issued a assertion urging all firms to undertake it.

Occasion

Intelligent Safety Summit On-Need

Find out the vital part of AI & ML in cybersecurity and marketplace particular case reports. Look at on-desire sessions nowadays.


Look at Here

“The amplified prioritization that governments and outstanding protection businesses have put on safety above the past couple of a long time suggests MFA will need to have to be utilised even additional to meet significantly stringent requires and anticipations for security. 

“Organizations ought to keep track of predicted enhancements in MFA around the up coming a number of years to see how they can strengthen an present functionality or make new MFA abilities into their organization’s society and procedures.”

– CJ Moses, CISO for AWS stability

Progressively inclusive workforce will tackle talent gap

“The need to address the continuing stability expertise workforce scarcity will be a leading precedence for lots of businesses. In 2023, corporations will significantly notice that attracting the best expertise from various backgrounds will not only assist fill crucial open up positions, it will assistance organizations improve their total protection posture.

“People make, generate, assume and provide in various techniques, and this is a significant profit when it arrives to solving evolving safety requires. With a extra numerous mentality, distinct factors of view appear into perform that empower stability teams to have new and distinctive outlooks on both equally the digital and physical landscapes they must preserve secure.

“New methods of thinking can be transformative to cybersecurity teams simply because it lessens many years of bias and groupthink and aids raise limitations on beliefs. Numerous backgrounds and teams also assistance identify how to help crucial company initiatives and aims. Security is no lengthier the ‘department of no,’ it is the ‘department of “how can I help?”‘ — and with a numerous staff construction, this form of organizational frame of mind is enabled.”

– Jenny Brinkley, director of Amazon protection

Collaboration will enhance preparedness and incident reaction

“The protection industry and the digital environment it supports is benefiting from collaborations viewed in 2022, and this trend will proceed. The ‘better together’ product will acquire momentum in 2023 and outside of.

“For example, as the a short while ago proven Open Cybersecurity Schema Framework gains new users, collective defenses will be improved, enabling security teams to correlate much more data sources much more easily, do their work opportunities with much less time invested on details munging and use improved facts to proactively make improvements to safety postures.

“More providers will see worth in contributing to engineering initiatives and assignments, applications, schooling and suggestions to assistance standardize safety applications and facts formats throughout the marketplace, such as major contributions from members of the Open up Source Stability Basis (OpenSSF).”

– Mark Ryland, director in the business office of the CISO, AWS safety

Education ideal methods will inspire motion and strengthen safety

“Training and education are key to utilizing excellent protection steps. Even with the most strong and modern resources, security is successful only when people know what to do and how to do it. Anyone who touches information or builds instruments and programs to retail outlet details need to be vested in safeguarding that information.

“Most workers really do not perform in stability, nor do they have ‘security’ in their titles, possibly top them to feel it’s another person else’s situation to ‘fix.’ Corporations of all shapes and measurements need to encourage employees to care about stability and empower them to consider significant actions to make sure protected results. Stability instruction requirements to consist of a whole-photo attitude that assists absolutely everyone embrace security as a small business problem at all levels of a firm.

“As we continuously seem for approaches to have interaction workers and increase safety outcomes, new best tactics include creating individualized, multimodal studying strategies that include a blend of presentations, discussions and palms-on labs that creatively attraction to all learning models. Serving to workers clearly recognize the ‘why’ guiding security very best procedures is vital. This can be achieved by sharing true-globe examples, lessons learned and case research that illustrate why safety ought to appear initially in anything they do.

“For both equally tech and non-tech workers, comprehending how particular actions affects protection, equally positively and negatively, builds the perception of shared obligation that results in better protection cleanliness and prioritizes protection as a feature — not an afterthought. Multimodal security education is complemented by an ongoing recognition model that cultivates a stability society in a daily exertion to tell and interact staff, when augmenting their function.”

– Jyllian Clarke, world-wide head of safety schooling, Amazon security 

Embedded protection will develop into more tangible with IaC

“Security stays prime of brain, and entities will more and more shift to cloud since they want to ‘shift left’ to embed security early in the product advancement lifecycle to attain better, a lot more scalable methods to application enhancement. Now that cloud suppliers have eliminated the undifferentiated weighty lifting of creating and sustaining data centers and invested in developing secure components, the electricity and flexibility of the cloud makes it possible for for entities to spin up and down immutable and ephemeral environments. 

“This is a apparent business enterprise enabler: It lets developers to move speedy and develop security in. It implies that with a number of keystrokes, Fortune 100s and smaller startups alike now have the capability to do infrastructure-as-code (IaC), leveraging templatization [and] such as stability controls, permissioning and guardrailing — in other terms, now they can also do safety as code. And, they can validate or reason about individuals permissions, working with math-like formal methods.

“These environments with embedded protection criteria are the ‘paved roads’ that security groups assistance outline and refine, enabling developers to spin up (and dissolve) environments rapidly. The consequence is far more automation, less manual evaluation of ‘snowflake’ 1-off environments, superior builder encounters and security at scale. As cloud adoption raises, ‘cloud’ and ‘security’ will be even far more intertwined, as cloud empowers builders to bake protection concerns into their code and architecture conclusions.

“I search ahead to this as one particular illustration of embedding protection primacy into all teams: Making the protected factor to do, the uncomplicated issue to do.”

– Merritt Baer, principal in the business of the CISO, AWS security

Orgs will raise financial commitment and target on enterprise resiliency

“As electronic transformation and cloud adoption systems consider hold across all industries, security and operational resiliency will receive elevated scrutiny from stakeholders, shareholders, the board of administrators, insurers and other people. Tests small business continuity plans and treatments when or two times a calendar year by the IT division will no extended be adequate.

“Resilient, really out there technological architectures and supporting organization procedures have to be developed and inspected for what could go erroneous in a worst-scenario situation. Budgets will contain ‘ongoing routine maintenance and improvement’ line things that will ensure that devices are not only highly performant, but secure and resilient right up until they are retired. With the power of automation and the scale of cloud technologies, it will no lengthier be just a dream to rebuild and re-hydrate protected, resilient environments with out human intervention. 

“Business leaders will turn out to be a lot more digitally fluent, and will make investments that genuinely modify the way they do organization (innovation, organizational buildings, business enterprise processes, up/re-skilling) and how they prepare for gatherings that problem their organization’s resiliency. The C-suite and the board will frequently participate in tabletop/video game-working day workout routines, answering the ‘what if?’ dilemma.

“’What if’: We experience a cyber celebration (to us or a person of our suppliers/associates)? a organization-crucial program is unavailable? we are negatively impacted from an economic downturn/world wide well being emergency/climate-associated turmoil/war or other event.

“With exercise, leaders will grow to be extra relaxed staying unpleasant and occur to phrases with the reality that there is no ‘normal’ in company any longer. Having said that, by continuing to find out and renovate them selves (there is no ‘end’ to a electronic transformation), organizations will come to be extra secure and resilient in 2023.”

– Clarke Rodgers, director of AWS company strategy 

“Accelerated digital transformation, distant operating, more connected equipment, new know-how, and need for mobility and obtain build at any time-growing environments for protection groups to guard and safeguard. More and a lot more security alerts from across complete businesses will generate rising volumes of disparate log and function knowledge that ought to be gathered, investigated and responded to immediately to efficiently address probable problems.

“In the months and many years in advance, rising deployment of intent-constructed tools such as protection information lakes will enable security groups to quickly centralize, quickly entry and far more competently evaluate all protection data from cloud and on-premises resources. This larger visibility signifies additional probable threats and vulnerabilities can be proactively determined to assistance protect against upcoming stability occasions.”

– Rod Wallace, general manager of Amazon security lake

Cloud security will increase with automated reasoning

“Automated reasoning allows us to accurately reply many proactive safety inquiries in seconds — or even milliseconds — which would usually take billions of yrs with brute-pressure screening. For the foreseeable future, it is predicted that automatic reasoning resources will double in capacity and overall performance every single year. This prediction is centered on a few observations:

  • Nearly all automated reasoning instruments are centered on the translation of issues to satisfiability solvers for mathematical logic. When evaluating the past two decades of satisfiability solvers apples-to-apples on the same benchmarks and hardware (so, making it possible for us to issue out Moore’s legislation), we see that they’ve previously been rising in potential and efficiency by 20{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1} per year. 
  • Moore’s legislation proceeds to present us with more, on a yearly basis escalating computational electric power for challenges that can be parallelized and dispersed. 
  • Recent scientific final results give us a new breakthrough system of distributing the operate of satisfiability fixing across microprocessors that gives speedups around the theoretical restrict from Amdahl’s law. 

“When these three details are place jointly, calculations level to the probability of annual ability and overall performance doubling. This developing functionality will unlock new and innovative cloud protection equipment that are unimaginable currently.”

– Byron Cook, VP and distinguished scientist for automated reasoning at AWS 

Stability groups will get additional really serious about quantum-resistant cryptography

In 2023, businesses will start to double down on crypto-agility. The Nationwide Institute for Standards and Know-how (NIST)’s envisioned to start with-draft specification from the Write-up-Quantum Cryptography (PQC) Standardization approach and the Quantum Computing Cybersecurity Preparedness Act will push IT leaders to get started transitioning from classical crypto-units to new write-up-quantum algorithms.

We will also see business and govt establish migration methods for acknowledged use conditions of cryptography. For instance, with the emergence of hybrid important establishment, the use of classical essential establishment procedures — like elliptic curve Diffie-Hellman combined with a new post-quantum vital encapsulation mechanisms this kind of as Kyber — will be utilised in the to start with iteration of publish-quantum criteria to deliver lengthy-phrase confidentiality towards likely long term quantum adversaries.”

– Matthew Campagna, senior principal engineer for AWS cryptography 

VentureBeat’s mission is to be a electronic city sq. for technological conclusion-makers to gain understanding about transformative business technology and transact. Uncover our Briefings.

Laid Off by Big Tech? Cybersecurity is a Smart Career Move

Laid Off by Big Tech? Cybersecurity is a Smart Career Move

Large technologies corporations are laying off staff as marketplace conditions alter.

The shift follows a selecting blitz in the beginning triggered by the uptick in pandemic-driven remote get the job done — according to Bloomberg, businesses are now reducing employment at a level approaching that of early 2020. For case in point, in November 2022 by yourself, providers laid off extra than 52,000 staff. Providers like Amazon and Meta also system to let far more than 10,000 personnel associates go about the up coming handful of decades.

As mentioned by Stanford Graduate College of Business enterprise Professor Jeffrey Pfeffer, component of this thrust to reduce positions stems from a bursting bubble of organization valuations. Pfeffer helps make it apparent, however, that in lots of conditions, the trigger below is imitative behavior. When a single enterprise starts off laying off workers, other folks comply with in what he phone calls a “social contagion”.

Regardless of the fundamental reason, many skilled IT specialists now locate them selves out of a occupation. But it is not all digital doom and gloom. There’s a person tech sector which is still battling to obtain talented staff: Cybersecurity.

Here’s why generating the go to infosec could be a wise vocation move for previous massive tech personnel.

The Increasing Will need for Infosec Gurus

According to info from Cyber Look for, much more than a million IT experts are presently section of the cybersecurity workforce. This variety has been steadily escalating over the earlier couple of a long time. Despite the uptick, even so, there are however more than 750,000 open cybersecurity positions across the region. In states this kind of as Florida, Texas and California, there are anyplace among 25,000 and 83,000 career openings out there.

The explanation for this increasing hole is uncomplicated: Cybersecurity threats are on the rise, and there aren’t more than enough competent gurus to satisfy expanding demand from customers. From the ongoing pitfalls of ransomware to rising attack vectors designed by get the job done-from-property insurance policies and the adoption of everywhere, whenever source obtain, providers now confront a myriad of outdated and new threats that can promptly derail business enterprise operations.

Oppositional Alternatives: The Reward of Terrible Guys

For IT gurus not too long ago laid off from big tech careers, the move to cybersecurity can feel like a unusual shift. Take into account a application engineer or application developer out of a task and hunting for new prospects. They might bypass infosec openings simply simply because they’re not certain stability would be a excellent in shape.

They are not erroneous. While cybersecurity is on the similar spectrum as other IT prospects, it comes with a distinctive tactic. Conflict rather than regularity is at the coronary heart of these protective positions. Irrespective of its considerable departure from other roles, it gives a special opportunity for development.

Place simply just? Owning an adversary fuels innovation. Instead of doing the job on assignments with a constant path amongst level A and point B, cybersecurity team must be ready to respond at a moment’s observe. Even as they’re occupied employing strategies and options to detect attackers previously and mitigate malware impacts, they’re also the to start with line of defense towards assaults in development.

As a outcome, these roles are not for absolutely everyone but give a persuasive vocation selection for those people searching to challenge them selves.

Competencies to Fork out the Charges

Cybersecurity-unique certifications and teaching can enable staff members stand out to recruiters and make the transition to new roles less complicated. But current qualifications also engage in a position in helping IT experts make the changeover.

Take into account a software program engineer with two a long time worth of working experience who was just lately laid off from their job. Though their talent in coding, screening and revision may well not feel right away applicable to cybersecurity, they deliver a exceptional set of positive aspects to the table.

Take the typical illustration of a ransomware attack. Cybersecurity teams put together for these assaults using a blend of risk intelligence options and incident detection applications that aid shorten the time amongst assault and discovery. Around time, however, attackers master — and increase. The existence of Ransomware-as-a-Company (RaaS) marketplaces showcases the motivation of malicious actors to collaborate when it rewards their potential to break down organization defenses.

In apply, this indicates that existing controls could slowly but surely start out to fall short as attackers greatly enhance their tactic. Our laid-off application engineer, nonetheless, can compile new code in-household to raise present options and frustrate attacker efforts.

Earning the Go to Cybersecurity

Of training course, it’s a single detail to contemplate a transfer to cybersecurity. It’s an additional to just take the plunge and start out placing out programs.

1 way to assistance streamline the shift is with certification-based education. Think about that of the much more than a single million presently employed cybersecurity professionals, 213,000 hold the CompTIA Security+ certification, and 94,000 have done the Qualified Facts Methods Stability Professional (CISSP) study course. What’s more, 140,000 of the at this time unfilled stability positions are inquiring for CISSP, whilst 100,000 want CompTIA Security+ completion.

Not only do classes this sort of as Protection+ offer a excellent introduction to cybersecurity procedures and priorities, but they also pave the way for development inside new companies. What is a lot more, many of these certification options are now available as on the net, self-paced classes that let IT gurus determine how and when they find out most effective.

One more choice for laid-off tech personnel is applying for positions that incorporate paid coaching to get them up to velocity. A fast query of the work research website Just Employed turns up extra than 600 positions that never call for prior cybersecurity practical experience and supply paid coaching.

Tech to Cybersecurity: From Toughness to Power

Unquestionably layoffs will stabilize and IT hiring will inevitably start off all over again in earnest. On the other hand, this is chilly ease and comfort for technologies professionals who come across on their own struggling with the unpleasant fact of probable unemployment.

As one particular digital door closes, nevertheless, yet another opens. And strangely enough, it’s one that sees know-how specialists acquiring approaches to continue to keep community doorways shut tight versus probable attackers. Even though the go to cybersecurity is not for all people, the competencies acquired in past positions combined with the compelling activity of adapting to an adversary’s movements make this lateral shift a excellent way for IT professionals to capitalize on existing strengths and create new ability sets that established them up for ongoing occupation steadiness.

US Army Analytics Group – Cybersecurity Anomaly Detection 1000X Faster With Less False Positives

US Army Analytics Group – Cybersecurity Anomaly Detection 1000X Faster With Less False Positives

The US Army Analytics Group (AAG) presents analytical services for various organizational functions and features, including cybersecurity. AAG signed a Cooperative Study and Growth Arrangement (CRADA) with Entanglement, Inc., and strategic associate Groq, Inc., a US semiconductor firm, to ascertain an optimal cybersecurity anomaly detection ability.

AAG has introduced a Validation Report confirming Entanglement AI’s remedy that solves cybersecurity anomaly detection 3 orders of magnitude faster than regular techniques with much less bogus positives. In this report, I will unpack the information behind these dramatic results.

Techniques for detecting cyber anomalies

All cyber-assaults, no matter whether zero-day or ransomware, share a common thread: cyber anomalies. A cyber anomaly is something out of the everyday, an outlier, this sort of as abnormal logins, spikes in targeted visitors, or a sizeable quantity of remote logins.

The 3 principal types of anomaly detection are: unsupervised, supervised, and semi-supervised. Security analysts use every technique to various levels of effectiveness in cybersecurity purposes.

Unsupervised anomaly detection utilizes an unlabeled test established of information. It entails schooling a equipment finding out (ML) design to establish usual habits making use of an unlabeled dataset. The assumption is that most instances in the information established will be ordinary. The anomaly detection algorithm detects occasions that show up not to healthy with the info established. Unsupervised anomaly detection algorithms involve Autoencoders, K-suggests, Gaussian Mixture Modelling (GMMs), hypothesis tests-based examination, and Principal Component Evaluation (PCAs).

Supervised anomaly detection takes advantage of info set with a established of “ordinary” and “irregular” labels and a experienced classification algorithm.

ML builds a predictive product from a labeled teaching set with typical and irregular details. Supervised approaches incorporate Bayesian networks, k-nearest neighbors, conclusion trees, supervised neural networks, and assist vector machines (SVMs).

Semi-supervised anomaly detection methods use a combination of a little established of labeled data and massive amount of money of unlabeled info for coaching. That product then detects anomalies by tests how most likely the design is to make any one particular occasion encountered.

Government order to undertake zero-believe in stability

In May well of 2021, President Biden issued an Executive Purchase mandating all federal organizations to adopt zero-belief security. One particular thirty day period later on, in June 2021, Entanglement, Inc., and strategic husband or wife Groq, Inc., a US semiconductor corporation, built a no-price tag provide of guidance to detect and take care of anomalies in assist of a zero-belief natural environment.

The project’s objective was to repeatedly watch a zero-belief stability architecture, necessitating an anomaly detection algorithm able of continually vetting all users on a network and steps. A comparable algorithmic framework will be appropriate for demonstrating Intrusion Detection Units (IDS) and expanded threat consciousness at community endpoints.

The venture focused on a few regions: improving upon auto-encoder features and effectiveness in excess of existing methods, accelerating generative adversarial community (GAN) features, and integrating a quantum-encouraged optimization SVM algorithm employing Quadratic Unconstrained Binary Optimization (QUBO).

Cybersecurity anomaly detection speedier than standard procedures

The work by Entanglement and Groq less than the CRADA demonstrated cybersecurity anomaly detection a lot quicker than standard solutions and much better performance measured by Critical Functionality Parameters (KPPs). The KPP’s lined metrics linked to complete inferences per next, proportion of threats detected, accuracy, recall, precision, other confusion matrix-based mostly metrics, and Place Beneath the Curve (AUC).

Former AAG endeavours detected 120,000 inferences for each 2nd, the benchmark and normal achievable employing a QUBO design.

Within just six months, Entanglement achieved an anomaly detection charge of 72,000,000 inferences for every next and shown the probable of attaining 120,000,000 inferences per second throughout a broad area of information processing programs.

Validation conditions utilised the KDD Cup 1999 (KDD99) and CICIDS2017 details sets.

The calculated output demonstrated for the Autoencoder and GAN resolution was hugely effective in identifying anomalies. The QUBO SVM was created in quantum-completely ready type and was also efficient at anomaly detection.

Wrapping up

Entanglement has delivered a significantly faster and far more precise cybersecurity anomaly detection functionality – with considerably much less wrong positives – than regular technological know-how. The Entanglement and Groq alternative supplied anomaly detection at 120 million inferences for each 2nd, 3 orders of magnitude speedier than any other technology.

What is most stunning is that Entanglement employed quantum-based algorithms, but there wasn’t a quantum pc that could perform as quick as GroqChip. The reply lies in the main Groq technologies, a objective-designed digital circuit layout with superior levels of parallelism, earning it for solving a range of troubles this sort of as deep neural community styles and Quadratic Unconstrained Binary Optimization (QUBO) difficulties.

We have regarded for a though that realizing the rewards of AI, ground breaking infrastructure, and predictive intelligence will involve a significantly less complicated and a lot more scalable processing architecture than a legacy alternative.

Groq developed a chip that delivers predictable and repeatable efficiency with reduced latency and significant throughput across the method referred to as the tensor streaming processor (TSP). The new, less difficult processing architecture is developed specially for the general performance demands of ML purposes and other compute-intense workloads.

Groq now has various shoppers across verticals who have employed their accelerator methods to achieve orders of magnitude efficiency enhancements. I appear ahead to sharing people tales with you in the long term.

Moor Insights & Technique, like all investigation and tech market analyst corporations, supplies or has supplied paid out providers to know-how companies. These companies contain research, evaluation, advising, consulting, benchmarking, acquisition matchmaking, and speaking sponsorships. The company has experienced or currently has paid out small business interactions with 8×8, Accenture, A10 Networks, Sophisticated Micro Products, Amazon, Amazon Net Companies, Ambient Scientific, Anuta Networks, Used Mind Research, Utilized Micro, Apstra, Arm, Aruba Networks (now HPE), Atom Computing, AT&T, Aura, Automation Wherever, AWS, A-10 Tactics, Bitfusion, Blaize, Box, Broadcom, , C3.AI, Calix, Campfire, Cisco Techniques, Crystal clear Application, Cloudera, Clumio, Cognitive Devices, CompuCom, Cradlepoint, CyberArk, Dell, Dell EMC, Dell Systems, Diablo Systems, Dialogue Team, Electronic Optics, Dreamium Labs, D-Wave, Echelon, Ericsson, Excessive Networks, Five9, Flex, Foundries.io, Foxconn, Frame (now VMware), Fujitsu, Gen Z Consortium, Glue Networks, GlobalFoundries, Revolve (now Google), Google Cloud, Graphcore, Groq, Hiregenics, Hotwire Worldwide, HP Inc., Hewlett Packard Business, Honeywell, Huawei Technologies, IBM, Infinidat, Infosys, Inseego, IonQ, IonVR, Inseego, Infosys, Infiot, Intel, Interdigital, Jabil Circuit, Keysight, Konica Minolta, Lattice Semiconductor, Lenovo, Linux Foundation, Lightbits Labs, LogicMonitor, Luminar, MapBox, Marvell Engineering, Mavenir, Marseille Inc, Mayfair Equity, Meraki (Cisco), Merck KGaA, Mesophere, Micron Technological know-how, Microsoft, MiTEL, Mojo Networks, MongoDB, Countrywide Devices, Neat, NetApp, Nightwatch, NOKIA (Alcatel-Lucent), Nortek, Novumind, NVIDIA, Nutanix, Nuvia (now Qualcomm), onsemi, ONUG, OpenStack Foundation, Oracle, Palo Alto Networks, Panasas, Peraso, Pexip, Pixelworks, Plume Layout, PlusAI, Poly (previously Plantronics), Portworx, Pure Storage, Qualcomm, Quantinuum, Rackspace, Rambus, Rayvolt E-Bikes, Red Hat, Renesas, Residio, Samsung Electronics, Samsung Semi, SAP, SAS, Scale Computing, Schneider Electric powered, SiFive, Silver Peak (now Aruba-HPE), SkyWorks, SONY Optical Storage, Splunk, Springpath (now Cisco), Spirent, Splunk, Sprint (now T-Cellular), Stratus Systems, Symantec, Synaptics, Syniverse, Synopsys, Tanium, Telesign,TE Connectivity, TensTorrent, Tobii Technology, Teradata,T-Mobile, Treasure Details, Twitter, Unity Technologies, UiPath, Verizon Communications, Extensive Details, Ventana Micro Techniques, Vidyo, VMware, Wave Computing, Wellsmith, Xilinx, Zayo, Zebra, Zededa, Zendesk, Zoho, Zoom, and Zscaler. Moor Insights & Technique founder, CEO, and Chief Analyst Patrick Moorhead is an investor in dMY Technologies Group Inc. VI, Dreamium Labs, Groq, Luminar Systems, MemryX, and Movandi.

How well did Israel’s cybersecurity industry do in 2022? • TechCrunch

How well did Israel’s cybersecurity industry do in 2022? • TechCrunch

The huge valuations and funding rounds of 2021 left some space for optimism all-around the state of the Israeli cybersecurity business in 2022, instilling a perception of security in Q1 of the new yr. When other sectors commenced to truly feel the shifting tides of the marketplace as the yr progressed, cash ongoing to freely move into cybersecurity, additional reinforcing the belief that it is a persistently resilient outlier in tech, immune to industry instabilities and unable to be shocked into a downturn.

Soon after closing the e book on 2022 this 7 days, it is safe to say that this optimism was fairly misguided. With hindsight, 2021 can be classified as an anomaly that sent the marketplace into a tailspin, with bloated valuations exceeding real earnings and funding rounds scaling at what quite a few warned was an unhealthy speed. The repercussions of this spiral are obvious in our 2022 assessment of funding and M&A details for the Israeli cybersecurity ecosystem.

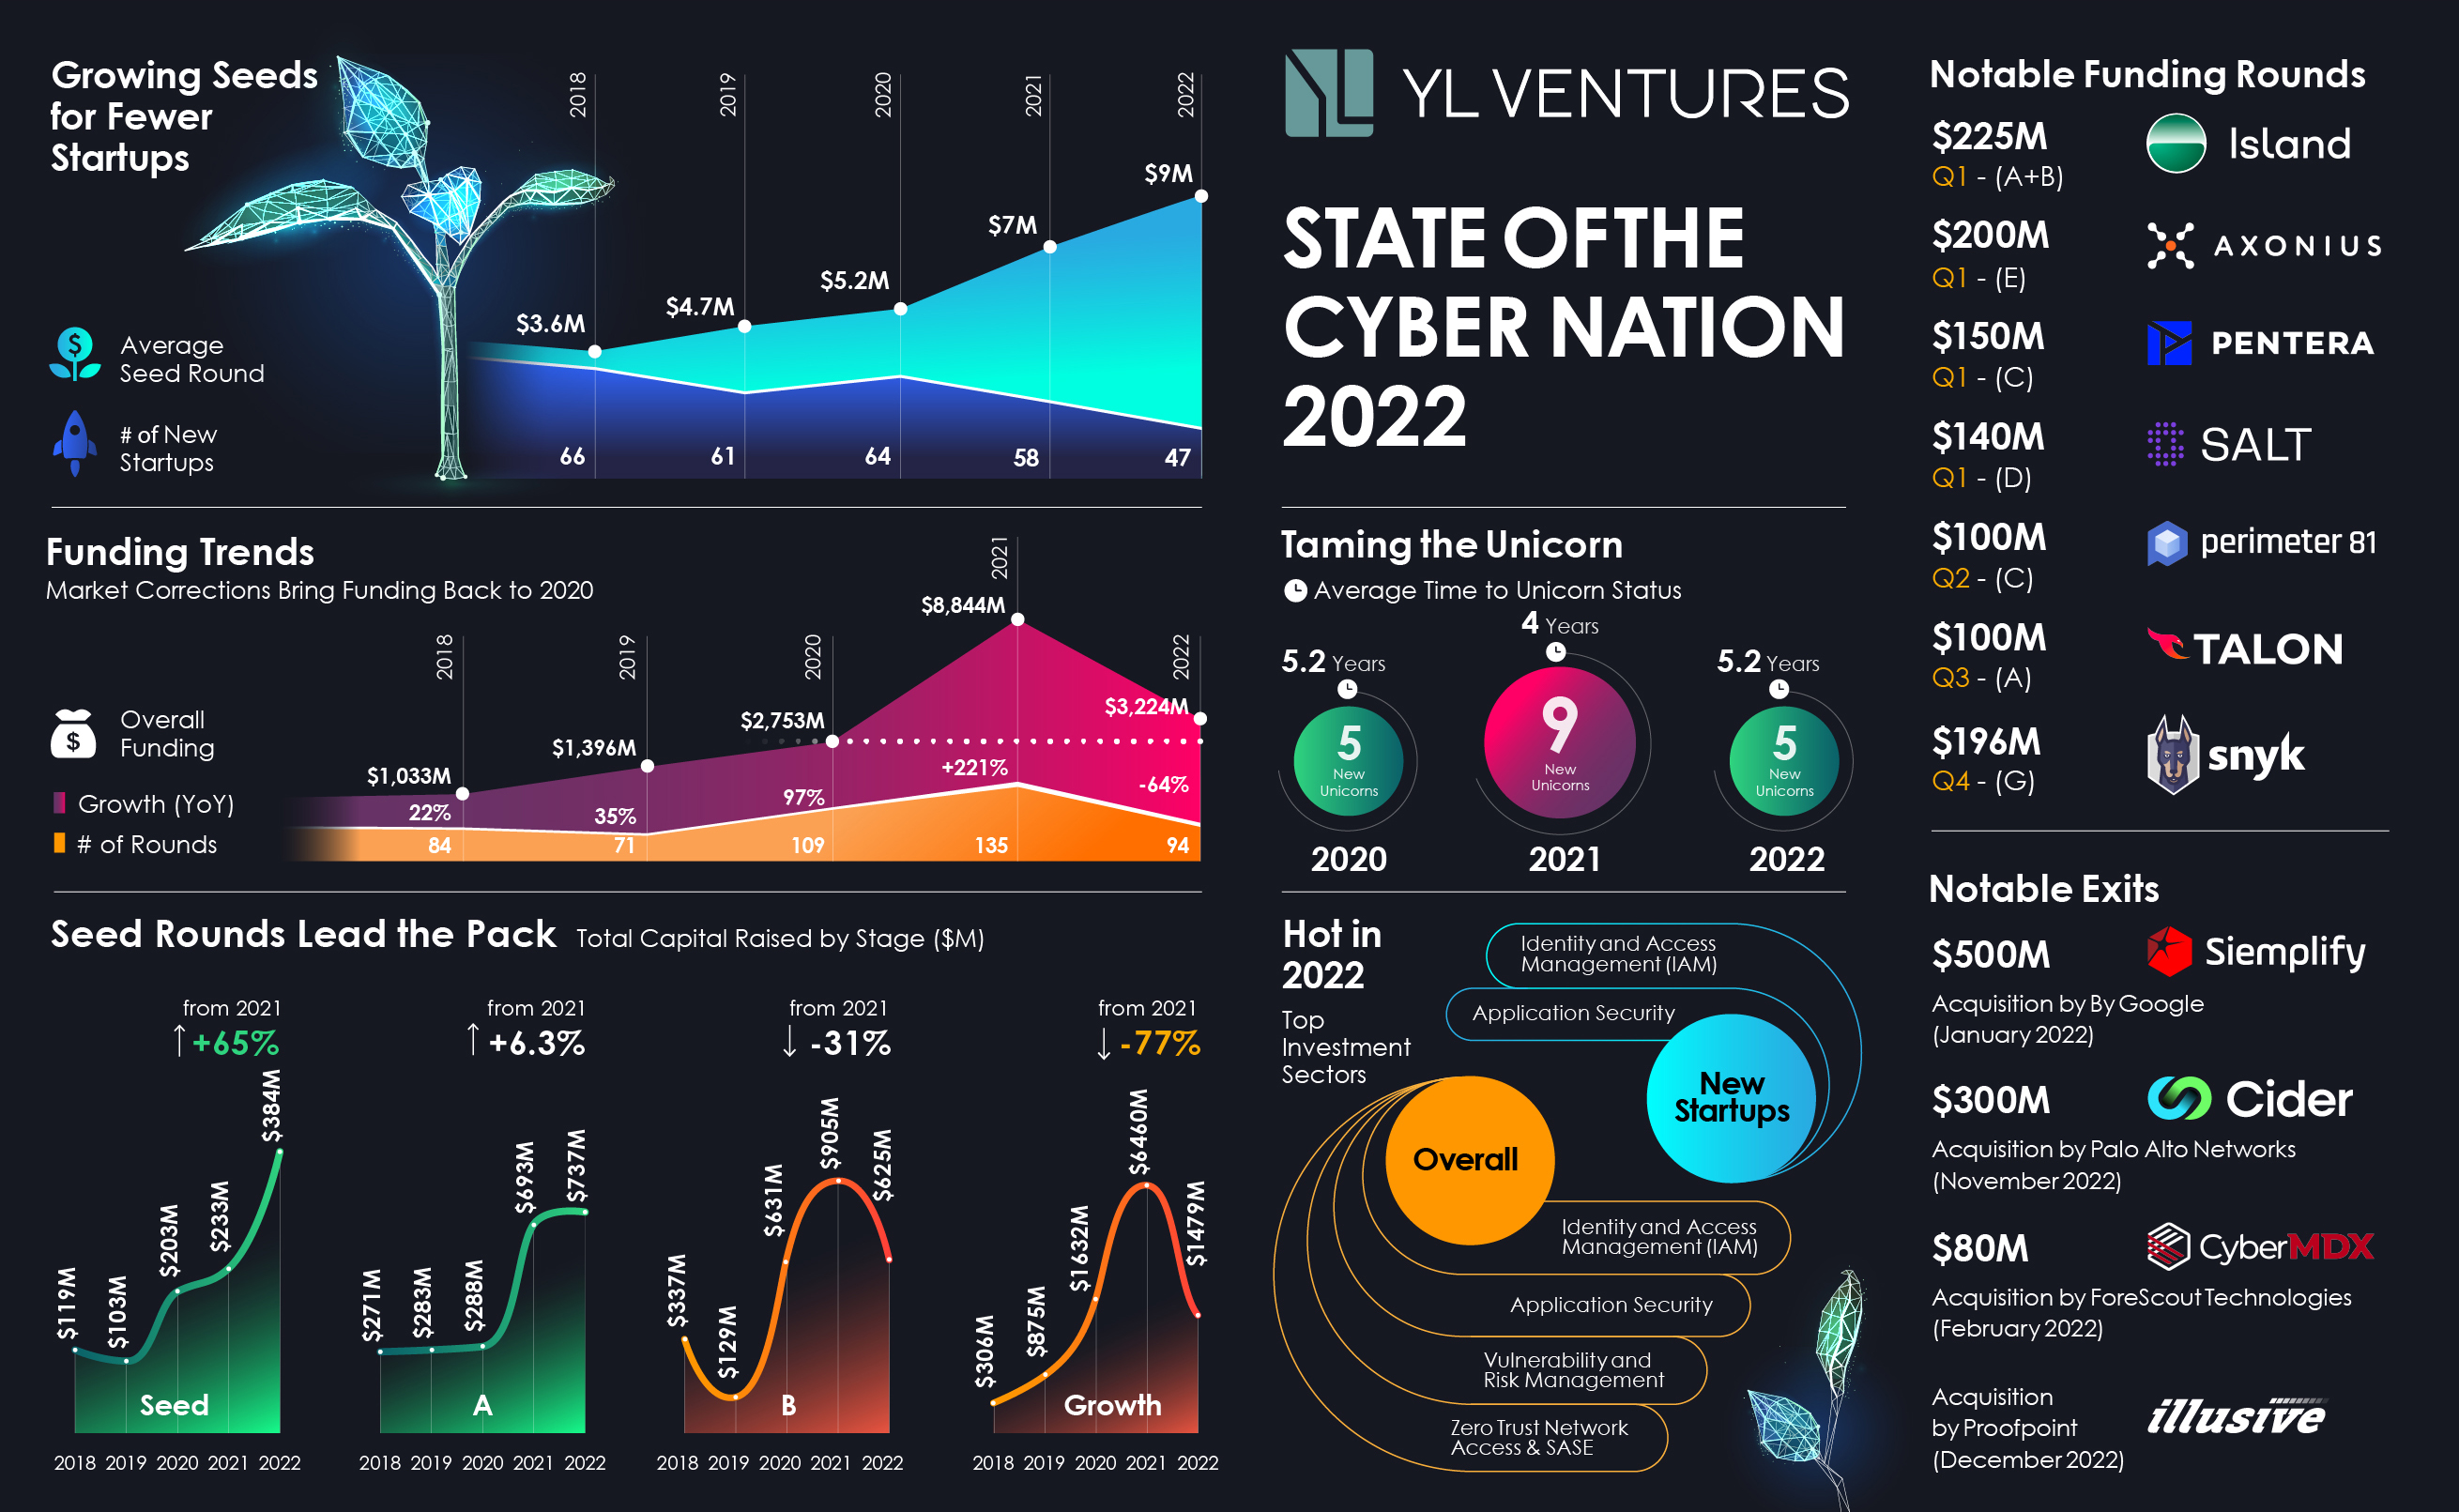
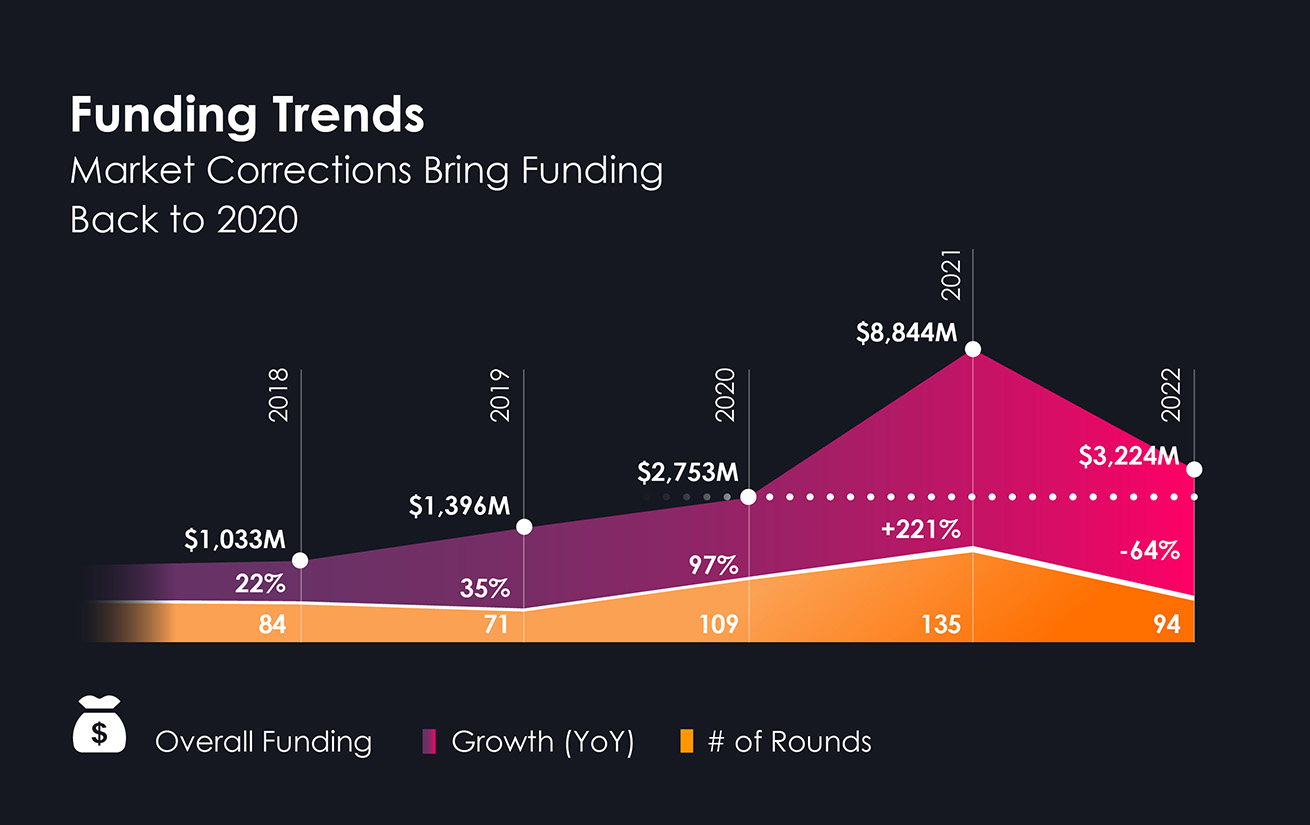
In 2022, all round funding for Israeli cybersecurity startups fell by a spectacular 64{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1}, from $8.84 billion in 2021 to $3.22 billion this calendar year, and the range of funding rounds decreased from 135 in 2021 to 94. When compared to over-all funding in 2020 ($2.75 billion above 109 funding rounds), it appears to be that 2021 was a blip on the radar, and that the industry is returning to exactly where it still left off in 2020.

The the greater part of funds that did move into Israel’s cybersecurity field poured instantly into seed rounds of early-stage startups.

Early stage will get the funding

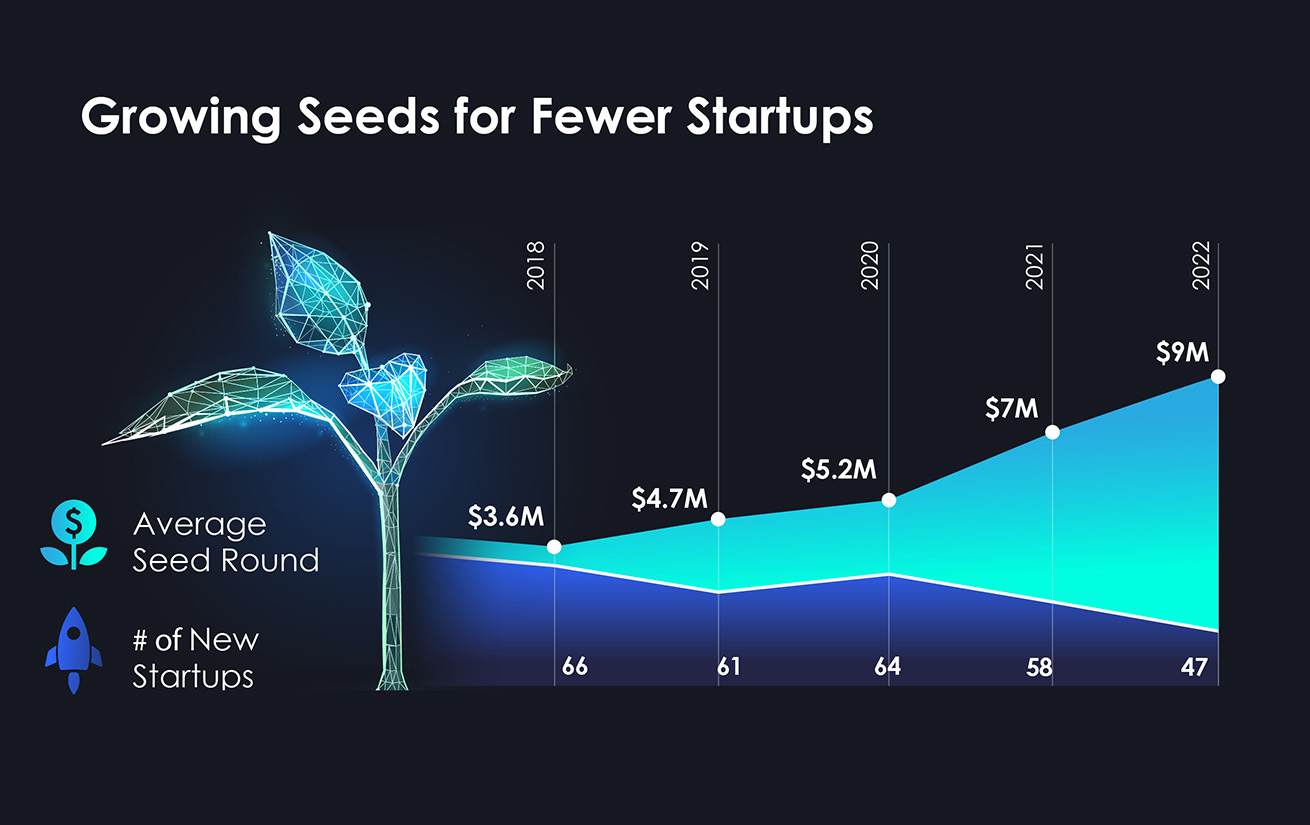
Our data show that the bulk of funds that did move into cybersecurity this calendar year poured straight into one very distinct place: seed rounds of early-stage cybersecurity startups. The average 2022 seed round truly shattered the 2021 history ($7 million), reaching a whopping $9 million. In whole, seed funding rose by 65{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1} this yr, from $233 million in 2021 to $384 million in 2022.

This putting sum of cash, dedicated to the earliest stages of corporation constructing, demonstrates ongoing investor self-confidence in the cybersecurity industry’s potential to innovate and build answers for increasingly acute threats.

Moreover, it signifies the problems in boosting Collection A rounds this calendar year, as investors’ thresholds for these rounds grew in mild of the financial crisis. While the quantity of Collection A rounds remained nearly unchanged since 2021 (30 rounds very last calendar year and 24 rounds in 2022), investors most popular to guidance the seed rounds of startups that will improve sustainably and cautiously from the get-go.

“Investors understand that seed funding has a apparent baseline, as the prices of developing a corporation have not reduced,” states Iren Reznikov, director of Company Development and Ventures at Sentinel A single. “They know that building a corporation from the floor up and ensuring that it reaches its Collection A spherical with utmost maturity even though hitting all of its benchmarks, expenses cash. At the very same time, traders expect founding teams to set very clear goals for achieving their Collection A and try to attain solution-sector fit at an early phase by partaking with future clients more rapidly.”

This self-confidence is shared by cybersecurity founders, who, even with this year’s industry volatility, however feel in the likely to develop a thing meaningful for organization safety and organization continuity. “Early-stage startups are ideal poised to answer to the shifting needs of a fiscally constrained sector,” states Slavik Markovich, co-founder and CEO of Descope, a stealth startup building a provider for software developers in the authentication space.

“A restricted overall economy is ordinarily accompanied by enhanced fraud and cyber attacks. Consumer adoption and conversion have turn into even additional significant in this current market, with companies seeking for methods that cut down friction for their finish shoppers in get to protect against any resources of churn. Founding groups at early-stage corporations that concentration on fixing these complications will carry on to bring in trader curiosity.”

Return of the cyberveterans

Recession hits cybersecurity companies hard as layoffs mount

Recession hits cybersecurity companies hard as layoffs mount

The cybersecurity business is not immune. This concept has been internalized over the earlier week in the technologies sector. It began with U.S. firm CrowdStrike, which is regarded one particular of the most significant gamers in the market. The company exposed excellent benefits in its financial studies for the third quarter, but the CEO admitted that customers are chopping expenditures and suspending buys.

On Wednesday, Israel’s SentinelOne, CrowdStrike’s sworn rival, released its economic reports that repeated the identical warning – now the quantities are very good, but it is tricky to dismiss the emerging weak spot in the corporate marketplace.

1 Watch gallery

כנס INTENT לחוקרי סייברכנס INTENT לחוקרי סייבר

Cybersecurity meeting.

(Tomer Foltyn Pictures)

“The macroeconomic things are manifested in a slower closing of discounts, especially of significant transactions,” Tomer Weingarten, founder and CEO of SentinelOne, reported yesterday immediately after the publication of the stories. “Shoppers are additional centered only on the most important and immediate security wants and reject the give in other regions”.

Nir Zuk’s Palo Alto Networks, the world’s most significant cyber organization in terms of market place capitalization, also posted superior benefits at the stop of November, but its managers also mentioned that the cyber marketplace, which is perceived as more resistant to the winds of economic downturn, is commencing to exhibit indicators of slowing down.

The words of the CEO of CrowdStrike sent its inventory to a sharp drop of 19{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1} in a single day previous week, which also mirrored on the stock of SentinelOne, which has misplaced about 10{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1} due to the fact then. Shares of Zscaler and Okta, other American cyber stars, also endured declines and even Palo Alto fell from its Mount Olympus and the record value it was traded at. SentinelOne has a market place cap of all-around $4 billion moving into Thursday, a lot less than 50 {b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1} of the value at which it was issued past year – thanks to which it now has $1.2 billion in hard cash.

And when businesses like CrowdStrike, Palo Alto or SentinelOne confess that the cyber industry is not immune, it is effortless to recognize why really a couple of startups in the subject have announced layoffs in the final week. Aqua Security, a cyber unicorn, parted approaches with just over 60 staff who make up 10{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1} of the workforce. A different unicorn, Perimeter 81, laid off 8{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1} of its workforce and Cognyte, which previously split from Verint, laid off 100 workers. Final thirty day period, Snyk also manufactured a deep go of laying off 200 workers, and at the exact same time Cybereason, Imperva and Checkmarx also parted strategies with personnel.

In the meantime, the public companies have prevented layoffs, with the exception of the Israeli Varonis, which laid off 110 workers – 5{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1} of the workforce. Nonetheless, Weingarten mentioned yesterday with the publication of the reports that SentinelOne has halted choosing and is generally investing in the teaching of the a lot of advertising and profits staff it recruited previous year.

In the meantime, it is still shedding income, and a whole lot, but revenues have doubled as opposed to the corresponding quarter to $115 million. The immediate advancement nevertheless does not include the expenditures that are increasing at the similar level, so the bottom line is that the organization recorded a decline of $98 million. The forecast for the current quarter, while the company improved it a bit, implies a slowdown in the progress fee. Quarterly revenues ought to achieve $125 million, so that SentinelOne will finish the total 12 months with a turnover of $420 million.

So what is precisely going on in the cyber industry? Up till now, the typical notion was that cyber is the past price to be cut, and this for the simple motive that it is an existential want. The other basic assumption is that the action of hackers and ransom demanders is not affected by financial cycles, if anything probably even the reverse – they also need additional revenue in see of inflation. Since of this, no one particular wishes to skimp on stability budgets and be accountable for a breach that cripples the corporation.

But in the area there is chat of the actuality that if in modern yrs the CISOs, people VPs of devices safety, been given every single spending budget they asked for from the CFOs or CEOs, nowadays the circumstance is distinct. The paying for binge has also produced a scenario the place corporations have armed on their own with several cyber programs, some of which aren’t even that helpful. This is possibly a different reason that now stability professionals are being despatched to 1st verify what specifically they acquired in the great yrs and what else can be carried out with these products.

And there is one thing else occurring in the cyber sector, even if it stays a little below the floor due to the fact most of the players in it have no incentive to acknowledge it – the rise of Microsoft’s ability. The large, which is not traditionally seen as a regular player in the cyber market, has drastically strengthened its technological answers in the subject, primarily these delivered with its cloud expert services. Among the other points, it did this through a sequence of purchases of Israeli startups, led by Adallom, but also Aorato, CyberX and other individuals.

In its most recent fiscal report, Microsoft astonished a lot of by indicating that its cyber enterprise presently generates yearly revenues of $15 billion and that it is rising by 40{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1} a calendar year. Microsoft is pushing its safety options not only with cloud providers, but also with Office. Microsoft designs to invest an additional $20 billion in bolstering its cyber answers, consequently only expanding the intensity of competitors in opposition to all the gamers in the sector, many of them Israeli, from Examine Level to CyberArk or Varonis. Google has obviously observed Microsoft’s go and ordered Mandiant in a $5.5 billion deal to strengthen its cyber reaction to cloud buyers and in general.

With or with no Microsoft, a person of the large questions now in the cyber market place is no matter if the slowdown and tighter budgets will bring about a desire for significant makes and nicely-identified companies so as not to danger doing the job with a startup that could not be below tomorrow. Or regardless of whether in its place, with the aim of saving and obtaining a boutique answer at the identical time, buyers will want to buy cyber options specifically from the smaller startups. These will be prepared to compromise much more on the rate and at times will even agree to present it for free in exchange for applying the customer’s title for income advertising to subsequent buyers. In the coming time period it will be easy to distinguish which providers have the most comprehensive and important answer and which of them are firms with a single aspect that can be obtained as element of a a lot more in depth remedy of a important player, even if of slightly lessen quality.

In the meantime, cyber shares have opened a negative gap in opposition to the S&P 500 index, even although Palo Alto Networks and Examine Stage control to preserve relative security. The declines make worth ranges that are starting off to look beautiful and many non-public expenditure funds are retaining an eye on cyber organizations with the goal of merging some of them and creating a likely giant. Of program, even the massive corporations themselves, from Microsoft to Look at Level, see the recent benefit stages and are getting ready to make acquisitions, which will make the cyber sector just one of the most fascinating to look at in 2023.