The Biden administration is shifting to carry out a new countrywide safety technique focused on halting hackers, as buzz about artificial intelligence applications raises issue between some specialists that criminals may possibly attempt to exploit AI abilities.
One particular goal of the administration system is to change the concentrate of blame away from the victims of cybercrime, U.S. stability officials mentioned. Soon after-the-point assessments usually concentrate on the focus on for currently being vulnerable adequate to hack — but if that target is a rural clinic, for instance, limitations could exists on what that clinic can do to shield against bad actors, particularly individuals backed by foreign governments.
As a substitute, the new program focuses on strengthening the general public-personal partnerships that inspire safety companies to share what they know about hacker networks in buy to convey them to justice.
Rising technological know-how will test the viability of the approach heading forward, experts informed ABC Information, specifically with AI posing new security issues.
The similar positive aspects witnessed in AI applications like ChatGPT from study lab OpenAI, which formulates human-like responses to issues posed by a person, are vulnerable to nefarious use, in accordance to Ari Jacoby, a tech govt who has targeted on working with AI to combat fraud.
Specified the volumes of publicly obtainable details on software program engineering, hackers could use the chat bots to create or enrich destructive computer system code, Jacoby said.
According to OpenAI’s person coverage, applying ChatGPT to write malware, generate hateful or destructive content or interact in fraudulent action is explicitly prohibited. The problem is no matter if tech corporations are capable of enforcing these types of rules as AI engineering spreads.
“The ChatGPTs of the globe — who do way additional great than damage — make accessible resources that can write software package code in significantly less than a moment that would have taken a poor actor or a undesirable network most likely times or weeks to run,” Jacoby said.
As a substitute of using ChatGPT to supply tips for recipes or generate simple perform e-mail, terrible actors could try to compose significant volumes of phishing e-mail that trick recipients into downloading malware or supplying up own monetary details.
Alternatively, similar equipment applied to examine and evaluate trends in significant sets of knowledge can likely be employed to struggle fraud, Jacoby explained. Credit score card firms, for example, could reward from remaining capable to detect anomalies in a customer’s actions to ascertain if buys are reliable.
In the meantime, the U.S. is dealing with a every day onslaught of cybersecurity breaches from Russian, Chinese and North Korea-backed groups, according to recent U.S. government assessments and personal cyber intelligence firms. Experts assume those initiatives will exam the resilience of the administration’s new cyber tactic.
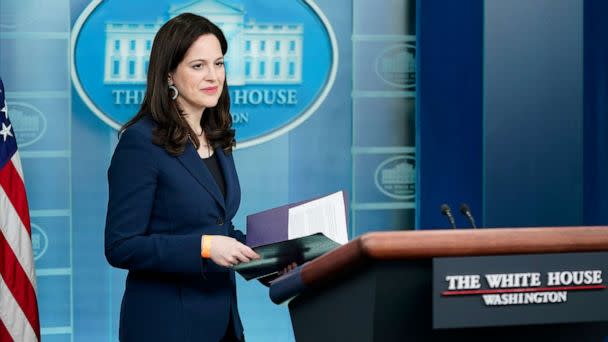
Photo: In this March 21, 2022 file photo Anne Neuberger, Deputy Nationwide Stability Advisor for Cyber and Emerging Know-how, arrives to communicate at a push briefing at the White House in Washington. (Patrick Semansky/AP, FILE)
“They are unbelievably complex and they are unbelievably properly-funded and nicely-tooled,” Jacoby explained. “They have a great deal of AI instruments at their disposal.”
A latest analysis of underground hacking communities by the cyber company Test Level Study observed on the net boards where by new approaches to hacking tools ended up reviewed, including a person discussion thread identified as “ChatGPT – Advantages of Malware.”
The author wrote they had been trying to use ChatGPT to recreate destructive computer code based on research papers about hacking.
Whilst the Biden administration’s tactic does not delve into the specifics of emerging technological innovation, these as AI, it truly is intended to be nimble enough to account for new developments in the promptly modifying cybersecurity landscape.
“These are multi-year initiatives where by we are going to uncover gaps and wherever Congress will then have to have to lean in to assistance us get to wherever we have to have to go,” acting National Cyber Director Kemba Walden stated at a forum dialogue of the strategy previous 7 days. “It’s a symphony, not a solitary movement.”
“This is an ongoing procedure,” she added.
Walden emphasized the significant position that cloud computing company providers play in securing data as a “pressure multiplier” for cyber threat first responders.
Google Cloud, for instance, delivers a wide variety of knowledge storage and internet site hosting providers. The company’s ability to defend its units was bolstered by its acquisition of the cybersecurity agency Mandiant past 12 months.
“Absolutely everyone has a shared duty below,” explained Stacy O’Mara, who leads govt tactic and partnership at Mandiant. “I believe that is the objective of the system — to strengthen this principle of a shared protection.”
“We’ve obtained a extended system in advance of us,” O’Mara claimed, ” but I’m encouraged by the administration’s initiatives.”
President Biden is about to approve a policy that goes considerably farther than any previous hard work to defend personal organizations from destructive hackers—and to retaliate against those people hackers with our very own cyberattacks.
The 35-webpage doc, titled “National Cybersecurity System,” differs from the dozen or so equivalent papers signed by presidents above the earlier quarter-century in two major strategies: Initially, it imposes required restrictions on a large swath of American industries. 2nd, it authorizes U.S. protection, intelligence, and law enforcement businesses to go on the offensive, hacking into the personal computer networks of criminals and foreign governments, in retaliation to—or preempting—their assaults on American networks.
“Our goal is to make malicious actors incapable of mounting sustained cyber-enabled strategies that would threaten the national stability or community security of the United States,” the document states in a 5-webpage area titled “Disrupt and Dismantle Risk Actions,” according to a draft completely considered by Slate. (The document has not however been publicly introduced, although it will be soon after Biden signs it, an celebration predicted sometime this month.)
Underneath the new system, the U.S. will “disrupt and dismantle” hostile networks as component of a persistent, continual campaign. This marketing campaign will be coordinated by the FBI’s Countrywide Cyber Investigative Joint Activity Power operating in tandem with all pertinent U.S. agencies—a systematic collaboration that has hardly ever been attempted and never in advance of publicized. Personal companies—both firms that are frequent targets of cyberattacks and firms that specialize in cybersecurity methods—will be whole associates in this effort and hard work, both to alert the government endeavor power of intrusions and to support repel them. (In the previous, lots of of these corporations, specifically in Silicon Valley, have been reluctant to be noticed cooperating with the government on these problems.)
The new strategy—which was in the functions for a great deal of 2022 underneath the supervision of senior White Residence officials—stems from the increasing recognition of two facts, which have lengthy been obvious to professionals.
Very first, mere guidelines on cybersecurity—which Washington has formerly allowed personal corporations to abide by voluntarily—have, for the most part, failed to block major intrusions by foreign governments or cybercriminals.
Next, purely defensive actions have also had constrained influence, as a intelligent hacker will at some point find means around them.
The United States has executed cyber-offensive operations for several a long time. Bill Clinton was the 1st president to admit this fact publicly. In 2012, Barack Obama issued Presidential Plan Directive No. 20, which set up strict controls, including that the president’s express permission was desired for all cyber-offensive operations. (Classified Leading Secret, it was 1 of quite a few files leaked by Edward Snowden.) In 2018, President Trump signed Nationwide Stability Presidential Memorandum No. 13, which loosened people controls, offering protection and intelligence organizations huge leeway to mount offensive campaigns on their own.
Gen. Paul Nakasone, who was and nonetheless is NSA director and Cyber Command chief (the two positions are typically held by the very same four-star officer), was the chief advocate of that strategy. In an post he afterwards wrote for Overseas Affairs, he described the mission, with its larger latitude, as “hunt forward” and “persistent engagement.”
Company lobbyists efficiently resisted necessary cybersecurity rules on private providers for several years. The new approach acknowledges that did notwork.
At the time, several feared that the finish of restricted controls would unleash surplus and blowback, and eventually damage protection. But, as one particular official who utilized to be between the fearful informed me previous week, “None of individuals terrible items took place.”
As a final result, Biden and his staff made the decision to drive the Trump-Nakasone coverage even more. The technique that Biden is established to approve addresses only those people offensive functions built to disrupt hostile actors’ attempts to hack into U.S. networks. At the same time, nonetheless, the Pentagon is drafting a new cyber approach, which applies the White Home paper’s ideas to cyber procedures, both equally defensive and broadly offensive.
The other sections of the Biden paper—which involves 30 internet pages dealing with purely defensive measures—outline continue to much more drastic departures from current guidelines to protect the nation’s “critical infrastructure.” That phrase, “critical infrastructure,” was coined in the mid-1990s and refers to financial sectors—such as banking, finance, electrical power, water operates, transportation devices, telecommunications, and crisis management services—that are necessary to modern-day societies and are linked to computer networks, this means they are susceptible to cyberattacks.
Presidents Bill Clinton, George W. Bush, and Barack Obama all signed orders and created companies to bolster the resiliency of these sectors. A few aides to all 3 presidents attempted to impose necessary cybersecurity regulations on providers in these sectors, but company lobbyists efficiently resisted their endeavours, as did some financial advisers, who warned (probably accurately) that rules would curtail innovation. So enforcement of the principles has been, till now, strictly voluntary.
The new tactic stems from a recognition that voluntary actions in most of people sectors don’t function. There are exceptions—for occasion, financial institutions. Cybersecurity is central to their enterprise if they get hacked much too often, shoppers will get their deposits somewhere else banks also have the income to employ really fantastic specialists. Even so, for general public utilities, these types of as energy crops, cybersecurity is pretty costly. Mandatory regulations are needed to prod them into motion.
At the similar time, the new strategy acknowledges that uniform expectations for all sectors—which some aides underneath earlier presidents tried using to formulate—don’t get the job done either. As an option, extra than a calendar year ago, the Biden White Property began analyzing every sector, in consultation with the federal agency that experienced authority in excess of each and every sector and with the providers that would be affected by polices.
For occasion, in accordance to a person formal, the TSA recognized 97 oil and gasoline pipelines that serviced at the very least 25,000 Us residents. The White Residence then held 3 meetings with executives of the businesses that owned the pipelines. At one assembly, just after staying vetted for protection clearances, the executives were briefed by intelligence officers on the threats their pipelines faced.
As a short while ago as a couple years in the past, lots of corporate executives perceived cyber threats as theoretical. Now they are clearly everythingbut.
Officials have also fulfilled with point out utility commissions on the threats to electric ability grids and on actions to increase protection. Just before Christmas, in a bill signed by Gov. Kathy Hochul, New York grew to become the initial point out to problem new necessary cybersecurity polices. It will be assisted by a number of federal specialists as perfectly as a chunk of the $1.5 billion that the White Home is allotting to states that take this leap. Similarly, this month, in accordance to 1 official, the EPA will difficulty new regulations on the cybersecurity of the nation’s waterworks.
Context is an additional massive big difference amongst Biden’s technique and earlier makes an attempt to impose rules. As just lately as a number of several years ago, quite a few company executives perceived cyber threats as theoretical. Now they are certainly something but. In 2020, Russia’s substantial hack on SolarWinds—which afflicted technique management equipment on the personal computers of more than 30,000 companies and companies included in significant infrastructure—was a big wake-up phone. In 2021, a criminal gang’s ransomware assault on Colonial Pipeline—which shut down the circulation of gasoline and jet fuel to 17 states right until Colonial paid 75 Bitcoins (at the time well worth $4.4 million) to the hacker group—was yet another.
The Colonial hack couldn’t have took place had even rudimentary stability measures been followed. It was a huge element of what led Biden to impose necessary rules on pipelines. The new system spreads such rules throughout the other vital industries.
Michael Daniel, Obama’s cyberpolicy coordinator who now heads the Cyber Threat Alliance, a nonprofit team of safety providers and IT firms, explained to me, “There’s certainly been a shift in business enterprise considering. It is one particular thing if your spreadsheets are wrecked—quite another if it’s your pacemaker. With recognition that cyberattacks can bring about physical injury, some degree of governing administration regulation is inevitable.”
Many of these companies also do small business abroad, wherever restrictions are a lot extra stringent. If they will need to follow restrictions in Europe, Australia, or Canada, they could as very well abide by them in this article, much too.
Nevertheless, the new technique won’t remedy all the troubles. There are various sectors—including foods and agriculture, unexpected emergency companies, and a number of producing industries—where Congress would require to move authorities to control. And the new Congress, at the very least on the Property aspect, doesn’t appear interested in passing significantly of anything at all, substantially fewer more rules on small business.
Even for sectors exactly where the govt department presently has authority, the strains of authority—which businesses can generate and implement which laws above whom—aren’t fully obvious. All through the drafting of the Nationwide Cybersecurity Technique, the two White Household officers in charge—Anne Neuberger, the deputy nationwide safety adviser for cyber and emerging systems (appointed by Biden), and Chris Inglis, the countrywide cyber director (a situation freshly designed by Congress just two many years back)—sometimes clashed more than these matters. Compromises ended up made, and a consensus was attained between the two of them and among the much more than 20 federal businesses. Nonetheless, there are, inevitably, some lingering ambiguities, which are to be settled in a subsequent “implementation strategy.”
It was way again in Oct 1997 when President Clinton’s Fee on Vital Infrastructure Safety warned of “cyber attacks” that could “paralyze or stress large segments of society” and “limit the flexibility of action of our nationwide leadership”—adding, “We ought to study to negotiate a new geography, the place borders are irrelevant and distances meaningless, wherever an enemy may possibly be capable to damage the important methods we depend on without the need of confronting our navy energy.”
A quarter-century later, Biden’s new strategy goes a long distance toward coming to grips with this new geography. But in a lot of techniques, we’re nevertheless negotiating.