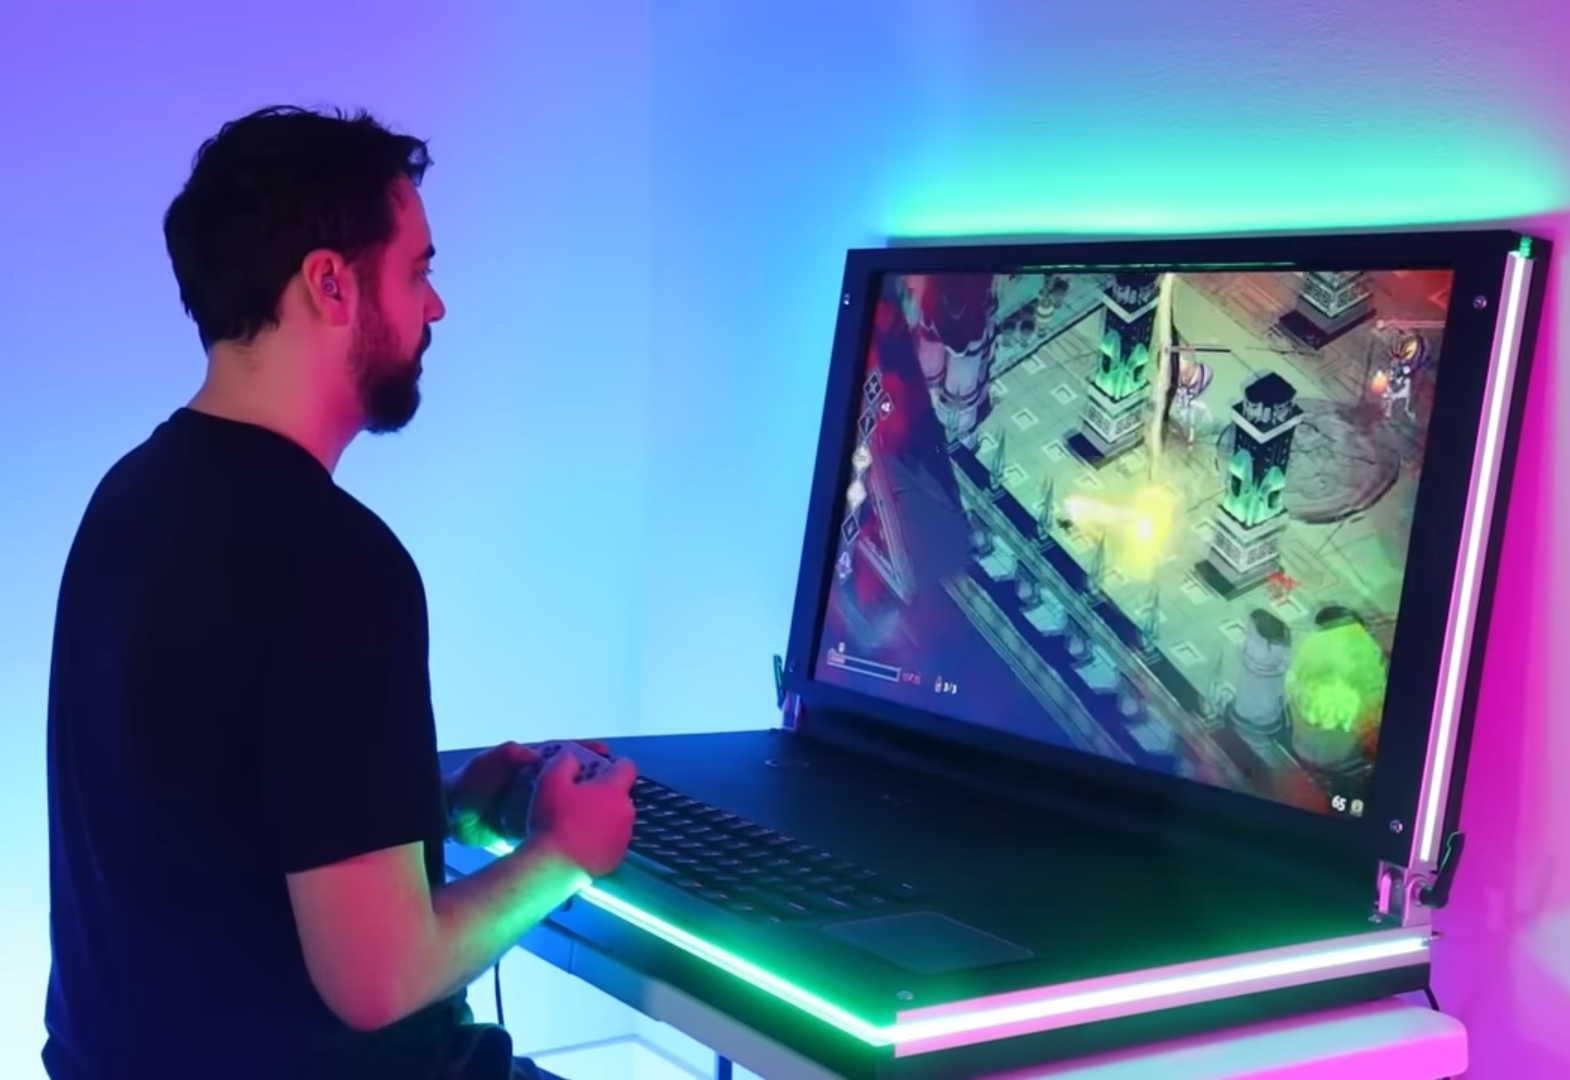
The BFL is built around a 43-inch TV screen. (Image Source: YouTube)
This wacky DIY project uses a 43-inch TV as its screen, and the computing power is provided via an Intel NUC 11 with i7-1165G7 processor and RTX 2060 dGPU that is hidden under the keyboard together with three high capacity batteries, which can sustain 260 W in full load.
YouTuber couple Evan and Katelyn came up with a crazy DIY project involving maybe the biggest laptop ever. How big? Think 43-inch big. The monster was named BFL (Big Fun Laptop) and it all started with the screen that is actually an LCD TV. Then a chassis was built around it, complete with personalized logo and some RGB light strips.
The chassis includes aluminum extrusions with two big hinges. Plywood was chosen for the upper and lower lids, while ABS sheets with a touch vinyl were added on the interior. Nevertheless, Evan and Katelyn tried to keep the laptop profile at a reasonable thickness, so they needed to find pretty compact components including three batteries that can provide enough power for a 260 W load.
One of the batteries is powering the screen alone, a second one is for a mini PC plus the peripherals attached to it, and the third one is for the LED strips. Of course, all these components needed to be fixed in place with a bunch of 3D-printed brackets. At the heart of the BFL lies a NUC 11 mini PC with Intel i7-1165G7 processor and RTX 2060 dGPU. Certainly not the fastest NUC, but a TSP of over 300 W would have probably needed four batteries. There is also a USB hub and a pretty big mechanical keyboard that still feels small for the laptop size.
It looks like the total thickness is around 4 inches, which is fair enough all things considered. The problem is the weight. This monster laptop is failing the portability test with flying colors as it weighs around 100 lbs (45.35 kg).
Bogdan Solca – Senior Tech Writer – 1959 articles published on Notebookcheck since 2017
I first stepped into the wondrous IT&C world when I was around seven years old. I was instantly fascinated by computerized graphics, whether they were from games or 3D applications like 3D Max. I’m also an avid reader of science fiction, an astrophysics aficionado, and a crypto geek. I started writing PC-related articles for Softpedia and a few blogs back in 2006. I joined the Notebookcheck team in the summer of 2017 and am currently a senior tech writer mostly covering processor, GPU, and laptop news.
Even with a global multibillion-greenback cybersecurity field, the menace from destructive cyber-activity, from each legal and point out actors, carries on to grow. Although quite a few cyber incidents are hardly ever described by their victims, Verizon’s 2022 Facts Breach Investigations Report observed that ransomware assaults rose 13 percent that year—more than the earlier five yrs blended. These breaches bundled attacks that threatened public well being and protection, with a number of hospitals across the United States compelled to terminate surgeries and divert people for the reason that they ended up locked out of their units.
Over the previous 10 years, adversaries of the United States have developed increasingly subtle offensive cyber-capabilities. As cybersecurity expert Dmitri Alperovitch has argued, “We do not have a cyber dilemma. We have a Russia, China, Iran, North Korea problem.” Despite the fact that the concentrate on malicious actors—whether nation-states or criminals—is vital, cyber-intrusions are a symptom, rather than a result in, of the ongoing vulnerability of U.S. engineering.
What the United States faces is less a cyber trouble than a broader technology and culture problem. The incentives for establishing and marketing technological know-how have eclipsed purchaser safety in significance—a craze that is not distinctive to software package and hardware industries but one particular that has notably pernicious outcomes simply because of the ubiquity of these systems. As Us citizens have built-in technological know-how into nearly every single aspect of their lives, they have unwittingly appear to take that it is standard for new program and units to be indefensible by layout. They accept products that are launched to current market with dozens, hundreds, or even countless numbers of flaws. They take that the cybersecurity stress falls disproportionately on consumers and tiny companies, which are often least knowledgeable of the menace and the very least capable of shielding them selves.
Widespread use of unsafe technologies is compounded by a widespread practice in quite a few businesses and firms of relegating cybersecurity to the “IT people” or to a chief data safety officer. They are provided this responsibility, but not the resources, influence, or accountability to be certain that stability is properly prioritized against price tag, general performance, speed to current market, and new options. When cybersecurity is considered a area of interest challenge, somewhat than a foundational business risk, organizations are not motivated to be section of a broader remedy. As a consequence, victims of cyber-intrusions also seldom share facts about malicious activity with the govt or with other companies, allowing adversaries to reuse the exact approaches to compromise many victims.
People in america have to have a new design, a single they can trust to be certain the security and integrity of the technology that they use every single hour of each day. Issues really should be mounted at the earliest achievable stage—when technological innovation is intended somewhat than when it is currently being utilised. Less than this new model, cybersecurity would in the long run be the obligation of every CEO and each and every board. Collaboration would be a prerequisite to self-preservation. These kinds of a tradition shift calls for the recognition that a cyberthreat to a single business is a danger to all organizations. To get there, incentives require to favor lengthy-term investments in the protection and resilience of the cyberspace ecosystem, and the responsibility for defending that ecosystem have to be redistributed to favor these most capable and ideal positioned to do so, as U.S. National Cyber Director Chris Inglis argued in Overseas Affairs final calendar year.
Federal government can sleek the way by making apparent its expectations that technological innovation is intended and developed with basic safety as a top rated priority, by advocating that cybersecurity be viewed as a CEO-amount enterprise risk, by offering alternatives for entities to share cyberthreat facts, by keeping itself accountable for currently being transparent and incorporating worth, and by making sure that regulatory frameworks motivate businesses to comply. The Cybersecurity and Infrastructure Protection Company (CISA), founded by the U.S. Congress in 2018 to serve as the country’s cyberdefense company, is focused on these goals.But authorities are unable to solve the problem. Technological innovation brands have to have to consider obligation for the stability results of their customers as a elementary situation of basic safety if not, the essential infrastructure of the United States, its communities, and its way of daily life will keep on being at untenable possibility.
UNSAFE AT ANY CPU Pace
This is not the very first time that American industry has produced security a secondary concern. For the initial 50 percent of the twentieth century, standard wisdom held that automotive mishaps were being the fault of poor motorists. Similarly, today, if a organization suffers a cybersecurity breach, the company itself is blamed if it did not patch a acknowledged vulnerability. Such an technique neglects to question why the vendor that manufactured the technology needed to problem so lots of patches in the very first place or why failure to put into action a patch allowed a harming breach to occur.
Any automobile created today has an array of conventional protection features—seatbelts, airbags, antilock brakes, and so on. No a person would assume of purchasing a car that did not have seatbelts or airbags, nor would everyone pay out additional to have these basic safety things put in. With cars and trucks, on the other hand, prospects can see for by themselves whether or not the proper protection features are integrated. That is not the case with insecure units or computer software. The penalties of making use of unsafe technological innovation are also more durable to measure—school districts are shut down, food provide chains disrupted, chemical compounds manipulated at h2o procedure plants. The easily apparent security issues with cars and trucks also led to a uncomplicated resolution: govt action to compel adoption of particular protection steps with proven greater outcomes. Whether vehicles or other sectors these kinds of as aviation or professional medical devices, it took crisis to power people today to aim on the will need for extra basic safety steps. These kinds of a safety disaster is previously here in the cyber-realm, and now is the time to tackle it.
Consumers and enterprises alike hope that cars and other products and solutions they buy from respected suppliers will not have possibility of harm. The exact same must be real of technology items. This expectation calls for a elementary change of duty. Technological innovation vendors and computer software developers have to acquire possession of their customers’ protection outcomes rather than treating each individual product as if it carries an implicit caveat emptor. To realize this, each technological innovation provider will have to start by developing merchandise that are equally “secure by default” and “secure by style and design.”
These principles are connected but unique. Safe-by-default goods have potent stability features—akin to seatbelts and airbags—at the time of invest in, without extra fees. Robust protection should be a conventional function of just about each individual technological know-how products, particularly these that underpin crucial infrastructure these kinds of as vitality, drinking water, transportation, communications, and unexpected emergency products and services. Attributes of powerful security by default will evolve in excess of time, but at a bare minimum, application sellers have to include things like in their essential pricing options that protected a user’s identification, obtain evidence of probable intrusions, and command entry to sensitive data fairly than as extra highly-priced options.
A cyberthreat to a person group is a threat to all businesses.
Equally essential is engineering that is safe by design and style. This is the expectation that engineering is purposely built, built, analyzed, and maintained to significantly cut down the quantity of exploitable flaws prior to it is launched to the market place for broad use. Obtaining this final result will need radical improvements in how technological know-how is made, which includes in the code utilized to produce application. Flaws usually wind up in technological know-how items because creators hurry to release them to customers and are frequently much more centered on element expansion than stability. This spots the load of protection on millions of organizations and individual conclude buyers, who are the least organized to deflect cyberthreats.
It will not be quick to make these alterations and persuade businesses to construct and supply extra protected goods, but the U.S. government can start out by defining distinct attributes of technological innovation goods that are safe by default and secure by structure. It can also connect with out firms that carry on to introduce insecurity into the fabric of the U.S. financial system, and it can persuade companies that are building progress. Certainly, a amount of technological know-how companies, which include Google, Amazon, and Salesforce, are shifting in this course, providing sturdy safety steps by default for their customers and introducing revolutionary advancements towards security by style.
Each and every business ought to need transparency from its know-how vendors about no matter whether they have adopted solid protection practices. A single way to push technological innovation firms to adopt such procedures is for every single firm that purchases engineering to contain basic safety prerequisites as simple, very easily recognized criteria prior to procurement or use. The Biden administration has taken critical measures toward this target in establishing software program security needs for federal contractors. It is also advocating for advancement and voluntary adoption of labels that would obviously and merely convey essential safety information about Internet-linked purchaser units, these as toddler screens and webcams.
Constructing on this development will require U.S. companies to impose ever more stringent secure-by-default and secure-by-style requirements in the federal procurement course of action, which will support prompt market place adjustments towards producing a safer cyberspace ecosystem. U.S. President Joe Biden’s 2021 cybersecurity executive get is spurring these attempts, but improve need to come from all angles: businesses throughout sectors need to dedicate to demanding sturdy safety practices when obtaining or upgrading technological innovation, and engineering companies should really commit to getting obligation for the stability outcomes of their shoppers. Each individual technological know-how company should consider it a duty to make certain that its products and solutions are safe and sound for use and to alert consumers when that is not the case.
This sort of needs may possibly pose issues for smaller technological innovation firms and new entrants to the current market. To make certain that impressive and disruptive organizations can thrive in an ecosystem where heightened safety financial commitment is the norm, enhancement of stronger safety techniques should concentrate on results instead than on prescriptive, doctrinaire needs, enabling new industry entrants to introduce inventive suggestions in which protection is a good differentiator instead than a price tag.
THE BUCK STOPS Right here
Although the transition to safer technologies is a more time-term endeavor, each and every firm can choose techniques nowadays that will boost its cybersecurity. Initial and foremost, in each organization, the duty for cybersecurity demands to be elevated from the IT section to the board, the CEO, and the senior govt amount.
The tendencies here are encouraging. In a National Affiliation of Company Directors 2019–2020 survey, 79 per cent of public business administrators indicated that their board’s comprehension of cyber risk experienced significantly improved about the previous two decades. The same review, having said that, identified that only 64 percent thought that their board’s knowledge of cyber possibility was powerful enough that they could present powerful oversight.
To enhance individuals quantities, shareholders will have to make CEOs and board users individually accountable for taking care of cyber chance. This is largely a cultural alter: the place cybersecurity is regarded a area of interest IT difficulty, it is intuitive for accountability to slide on the main information and facts protection officer when cybersecurity is regarded a core enterprise danger, it will be owned by the CEO and the board.
In each individual business enterprise, the duty for cybersecurity requirements to be elevated.
Board members have distinctive energy to establish a tradition of company cyber obligation. They must assure that they and other senior executives are effectively educated on cyber risk, that cybersecurity criteria are appropriately prioritized in each and every company and technology final decision, and that selections to acknowledge cyber threat are scrutinized and revisited frequently. They must ensure that the thresholds for reporting potential malicious action to senior administration are not established far too significant “near misses” really should be claimed alongside with intrusion tries that be successful. They must make sure that suitable extensive-expression safety investments are obtainable to address the basic safety consequences of antiquated technological know-how. Most significant, board associates really should see that chief facts safety officers have the influence and methods required to make critical conclusions on cybersecurity. Decisions to prioritize revenue over security must be created transparently, with apparent ownership by CEOs and boards. The follow of blaming the main facts security officer or the IT department for organizational failings ought to end.
Vital to advancing company cyber obligation as a make a difference of good governance is the enhancement of a popular established of practices that corporations can use to figure out their exposure to cybersecurity danger. The Cybersecurity Framework produced by the National Institute for Requirements and Technological innovation is thought of an exemplar for developing and evolving a firm’s cybersecurity program. Many companies, however—particularly little and medium companies that comprise the offer chains of more substantial entities—find it tough to satisfy people benchmarks, typically mainly because they deficiency sources. To address this challenge, the Cybersecurity Performance Ambitions, released by CISA in late 2022 in partnership with NIST, can enable corporations ascertain which safety steps are most essential to minimize chance. Encouragingly, score companies have begun incorporating cybersecurity into their designs for examining creditworthiness, action that can more encourage businesses to embrace cyber obligation as a make a difference of institutional governance.
ALL Together NOW
Sustainable cybersecurity will also need rethinking how governments and industries interact with just one yet another. When most providers detect a cyber-intrusion, much too generally their default response is: call the lawyers, provide in an incident response agency, and share info only to the bare minimum extent expected. They frequently neglect to report cyber-intrusions to the authorities for anxiety of regulatory liability and reputational destruction. In today’s highly linked globe, this is a race to the bottom.
Standard Paul Nakasone, head of the U.S. Cyber Command, wrote a number of years ago about the doctrine of persistent engagement, in which U.S. forces contend with overseas adversaries on a proactive and recurring foundation. From a defensive perspective, the U.S. authorities have to as an alternative shift to a posture of persistent collaboration. These types of a lifestyle change requires that sharing turn out to be the default response, exactly where info about destructive exercise, including intrusions, is presumed required for the prevalent good and urgently shared involving industry and govt. Federal government and market need to perform collectively with reciprocal expectations of transparency and worth, where business does not have to be involved about punitive sanction. At last, interactions amongst the government and the private sector really should be frictionless, so that collaboration emphasizes scale, shared platforms, and data-driven evaluation.
In 2021, Congress set up the Joint Cyber Defense Collaborative to progress this posture by creating 1 U.S. government system for cyberdefense preparing and operations. It is still early times for the JCDC, but given that its development, for the 1st time, the governing administration, the non-public sector, and U.S. international associates came alongside one another to create joint cyberdefense options and help authentic-time data sharing on difficulties from the U.S. response to Russia’s legal invasion of Ukraine to endeavours to assistance safeguard the 2022 midterm elections. In excess of the coming year, CISA will continue on these endeavours, which will incorporate constructing resilience to ransomware attacks in coordination with the Joint Ransomware Endeavor Pressure and the International Counter Ransomware Initiative and will deal with the root will cause of incidents as discovered by the Cyber Security Critique Board. As the JCDC carries on to evolve, CISA and governing administration partners will try to uphold their close of the discount by becoming clear, responsive, and adding value, but the JCDC will only realize success if associates throughout the country, in each individual sector of the financial system, be part of the exertion.
WITH A Minimal Help FROM MY Good friends
Even as the cybersecurity neighborhood takes ways to create a sustainable technique to cybersecurity by the common adoption of safe engineering, corporate cyber accountability, and persistent collaboration, it must proceed to help people today and smaller organizations defend them selves, recognizing that everybody has a accountability to sustain a risk-free cyberspace setting, just as drivers nonetheless bear obligation for driving securely, even with seatbelts and airbags are incorporated as regular functions.
The philanthropist Craig Newmark has a short while ago referred to as for focused investment decision in “cyber–civil defense”to raise public consciousness of on the web safety. Along equivalent traces, CISA has been engaged in developing cybersecurity into K–12 curricula performing with “target wealthy, cyber poor” entities this kind of as little businesses, school districts, water amenities, hospitals, and regional election places of work to be certain they have the tools essential to improve their cybersecurity and major a nationwide cyber cleanliness marketing campaign to support all Us residents from “K through Gray” remain safe on the internet by using uncomplicated ways such as turning on multifactor authentication. The ultimate purpose, having said that, is to radically enhance product or service security, so technologies prospects almost never need to have to secure their devices on their individual. Though some protection steps will turn into as straightforward to use as a seatbelt, most businesses really should be protected ahead of they even “buckle up.” This basic level of protection will not be realized below today’s failing product. It is time for a new tactic, and if the federal government and the non-public sector can develop have faith in and function with each other, cyberspace can turn into safer for everybody.
The acquisition, which Dell Technologies has yet to officially announce but did ensure, delivers the corporation a primary developer of cloud automation and orchestration capabilities for DevOps and ITSM environments.


Dell Technologies has quietly acquired Cloudify as a way to deliver greater cloud orchestration capabilities.
In accordance to TechCrunch, which Wednesday broke the information, Dell obtained Cloudify for about $100 million.
Dell Tuesday filed a Sort S-8 with the SEC titled Cloudify System Ltd. 2017 Share Incentive Plan in which Dell refers to issuing of Course C widespread stock “in respect of selected superb and unvested alternatives to obtain the common shares of Cloudify Platform Ltd., an Israeli private liability corporation.”
[Related: Michael Dell On ‘Embracing Developers’ And Multi-Cloud Future]
Cloudify did not answer to a CRN ask for for details by press time.
Nonetheless, a Dell spokesperson verified the acquisition by using e mail, composing, “Dell Technologies introduced that it has finished the acquisition of Cloudify. This transaction lets Dell to carry on to innovate our edge offerings.”
Herzliya, Israel-dependent Cloudify, which has its U.S. headquarters in New York, was started as an open-resource DevOps automation system offering what it calls ‘Environment as a Service’ technologies.
Cloudify’s surroundings-as-a-provider deals infrastructure, networking, and automation resources into certified blueprints that it claims its customers can use to handle heterogeneous cloud environments at scale, and to assist bridge the gap between DevOps and IT services management (ITSM).
The technological know-how allows DevOps groups working in hybrid cloud and cloud-indigenous environments to automate provisioning and update workflows.
Cloudify incorporates in its technologies ecosystem these partners as Amazon Web Services, Google Cloud Platform, Microsoft Azure, F5, Wind River Software program, and ServiceNow.
Dell, for years a pillar in the on-premises knowledge middle and finish user marketplaces, has in the past pair decades articulated its cloud approach.
The enterprise in January of 2022 launched new Apex as-a-company offerings and general public cloud integrations with the objective of moving buyers from multi-cloud ‘by default’ to multi-cloud ‘by design’ by integrating more deeply with community cloud leaders, giving stand-on your own computer software for public clouds, and rising its Apex portfolio and world footprint.
Dell followed up four months later on with the introduction of new multi-cloud safety choices focusing on AWS and Microsoft Azure environments.
Prior to its acquisition of Cloudify, Dell in 2013 obtained Enstratius, a company of cloud management products and services.
Joseph F. Kovar
Joseph F. Kovar is a senior editor and reporter for the storage and the non-tech-concentrated channel beats for CRN. He keeps visitors abreast of the most current problems similar to these types of locations as info daily life-cycle, company continuity and catastrophe restoration, and information centers, alongside with linked products and services and application, while highlighting some of the important traits that affect the IT channel general. He can be achieved at jkovar@thechannelcompany.com.
Victor initially got into world wide web layout in a way numerous will relate to – designing Neopets guild layouts and forum signatures on a pirated copy of Photoshop, for illustration. But apart from this, with his mum functioning as a taxi driver, Victor clarifies that artwork and structure weren’t specifically on his radar escalating up. It was a several terrific art teachers – who allow him tinker away on computer systems all through art lessons – that assisted his enthusiasm expand. A person in particular, who had previously taught at Kingston, nudged him in the direction of a graphic design and style degree at the establishment. Due to the fact graduating, Victor has worked as a designer for the BBC and Parliament. Not long ago, having said that, Victor give up his occupation to emphasis on generating websites for tasks extra aligned with his personal passions.
In realising the Mater web site, 1 of the aspects both of those Victor and Maddie are most happy of is the leading area of each and every contribution. “It available a room to participate in with imagery, reworking it in some way to create a low-carbon widespread expression,” Victor describes. The initially interaction of this apply is seen on the Chapter One page. Right here, each individual contribution is stated and the name of the creator is obvious, prior to reworking into an picture – composed of textural dots – when the cursor moves more than it. To compress these images in such a visually arresting way, Victor clarifies: “I wrote a minor bit of code to crunch the artist’s photographs into small files, and then we exploded just about every graphic back to its initial dimension, though erasing darker or lighter pixels, to see what remained.” For the next set of contributions, Victor describes that they needed a little something that did not entail as significantly processing. And so, Victor shrunk down pictures and laid them around supersized text. “It’s an inversion of how lots of internet websites take care of this part – with substantial images and small text. But once more it’s a single pushed by the desire to come across a inventive alternative that retains our effects on the world as tiny as doable,” Victor aspects.
On the lookout to the foreseeable future, Victor hopes that this reduced-carbon approach will be adopted and integrated by significant providers. “The fact is that a tweak to a site masses of individuals stop by, many of which are bloated with unnecessary code, will have a a lot larger influence than some thing that only reaches a niche audience,” he claims. Additionally, Victor sees there as staying a enormous untapped realm of expression ready to be unearthed. “Low carbon doesn’t will need to signify monotonous! So I hope a reconnection amongst the underlying materials of the world-wide-web and the internet sites we create can guide to a additional innovative, attention-grabbing net.” Making use of instinct and inventive difficulty fixing, all the although creating a little something arresting, the Mater internet site itself is a testament to the point that minimal-carbon web layout doesn’t come at the expense of attractive, complex visuals. Preparing on constructing your individual minimal-carbon website? Study on below for some helpful guidance.