
Hackers are quickly learning how to target cloud systems

Hackers are quickly learning how to target cloud systems
Illustration of a carbon cloud with an "X" on it, wiggling as if about to be deleted.

Illustration: Aïda Amer/Axios

Hackers are immediately locating flaws in organizations’ cloud infrastructure even with perceptions that the technologies is ironclad against cyberattacks.

The massive picture: Corporations have invested billions of bucks in latest years to move their digital data from classic, on-premise company storage solutions to the cloud. That expense is expected to keep expanding and attain shut to $600 billion this 12 months.

  • The superior price of relocating details was mostly paid out for one particular motive: It’s far more tricky for hackers to split into an organization’s cloud methods.
  • But the latest research and incidents underscore how swiftly destructive hackers are adapting to the new truth.

Driving the news: Attacks exploiting cloud devices just about doubled in 2022, and the variety of hacking teams that can goal the cloud tripled past year, in accordance to a CrowdStrike report produced previous week.

  • A large-achieving ransomware attack past month focused a vulnerability in a preferred VMware device made use of in cloud devices, leaving hundreds of units susceptible.
  • Bloomberg claimed past thirty day period that the the latest exposure of roughly a terabyte of Pentagon e-mails was likely due to a cloud configuration mistake.

What they are saying: “As much more organizations are relocating into the cloud, it results in being a significantly more eye-catching focus on for these risk actors, and they’re expending more time and resources making an attempt to get into that natural environment,” Adam Meyers, senior vice president of intelligence at CrowdStrike, explained to Axios.

  • “Everybody is performing it. We have witnessed 17-year-olds, and we have noticed the Russian SVR.”

By the figures: About eight in 10 organizations claimed they experienced a cloud protection incident in the previous calendar year, in accordance to a September report from Venafi.

  • 45{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1} of the businesses that confronted a cloud security incident seasoned at minimum 4 attacks all through that interval, the investigation uncovered.

Among the strains: The cloud is still far more safe than conventional methods, Meyers explained, but a huge driver in assaults are the security flaws accidentally injected any time organizations personalize cloud tools for their certain techniques.

  • Subsequently, most businesses also fall short to update their legacy cybersecurity equipment to spot those cloud configuration faults, Meyers additional.

The intrigue: Numerous hackers are quickly developing abilities to concentrate on cloud storage due to the fact of how fulfilling it can be.

  • Through standard assaults concentrating on onsite servers, destructive hackers usually require their have port-scanning instruments to detect what methods are in an enterprise and where the weak, exploitable spots are.
  • But for the duration of cloud attacks, those port scanners aren’t required, Meyers said. Destructive hackers who can navigate a cloud natural environment can use native resources inside the surroundings to much more stealthily research and establish what details is out there.
  • “You’ve got produced a Mentos of stability: crunchy on the outdoors, gentle and chewy on the inside,” Meyers stated.

Yes, but: Attacks targeting the cloud nevertheless start in quite a few of the identical ways as on-premise assaults: applying stolen worker login credentials.

  • For occasion, cloud stability organization Mitiga warned last 7 days that when hackers use respectable login qualifications to break in, the Google Cloud System fails to report a correct action log of the malicious actor’s steps, cyber trade publication Darkish Studying reviews.

The base line: As IT expending on the cloud carries on to improve, corporations want to make certain they are also examining their security sets to make sure they can handle new, cloud-relevant obstructions.

Indicator up for Axios’ cybersecurity e-newsletter Codebook here.
US ‘Disruptive Technology’ Strike Force to Target National Security Threats

US ‘Disruptive Technology’ Strike Force to Target National Security Threats

A best U.S. law enforcement official on Thursday unveiled a new “disruptive technology strike drive” tasked with safeguarding American technological know-how from international adversaries and other national safety threats.

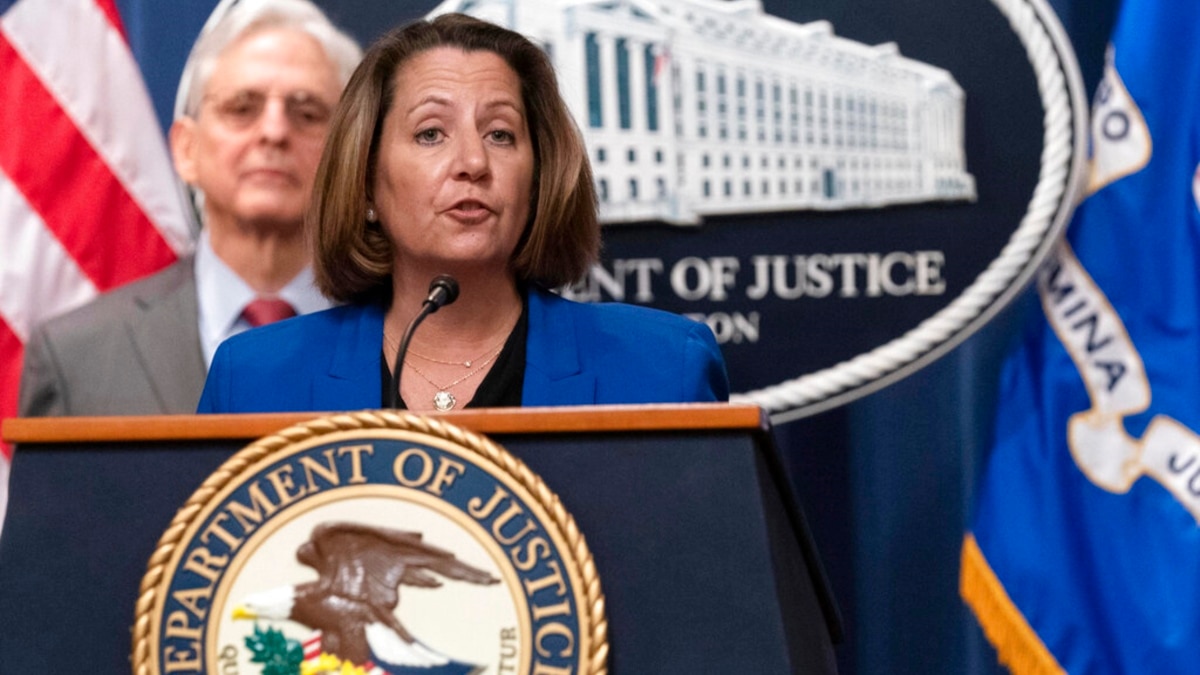
Deputy Attorney Normal Lisa Monaco, the No. 2 U.S. Justice Division official, created the announcement at a speech in London at Chatham Home. The initiative, Monaco stated, will be a joint effort involving her division and the U.S. Commerce Section, with a goal of blocking adversaries from “seeking to siphon our most effective technology.”

Monaco also dealt with problems about Chinese-owned video sharing app TikTok.

The U.S. government’s Committee on Overseas Expense in the United States, a impressive national safety system, in 2020 requested Chinese business ByteDance to divest TikTok due to the fact of fears that person data could be handed on to China’s govt. The divestment has not taken spot.

The committee and TikTok have been in talks for additional than two many years aiming to attain a national safety agreement.

“I will be aware I you should not use TikTok, and I would not suggest any person to do so for the reason that of these issues. The base line is China has been quite very clear that they are seeking to mold and put ahead the use and norms all over systems that advance their privileges, their pursuits,” Monaco said.

The Justice Department in the latest many years has more and more centered its endeavours on bringing felony scenarios to protect company mental house, U.S. supply chains and personal info about People in america from foreign adversaries, both through cyberattacks, theft or sanctions evasion.

U.S. law enforcement officials have reported that China by considerably remains the major danger to America’s technological innovation and financial security, a perspective that Monaco reiterated on Thursday.

“China’s doctrine of ‘civil-armed service fusion’ suggests that any advance by a Chinese firm with military application will have to be shared with the state,” Monaco said. “So if a firm operating in China collects your facts, it is a superior wager that the Chinese federal government is accessing it.”

Under previous President Donald Trump’s administration, the Justice Department produced a China initiative tasked with combating Chinese espionage and intellectual property theft.

President Joe Biden’s Justice Division later scrapped the title and re-concentrated the initiative amid criticism it was fueling racism by focusing on professors at U.S. universities in excess of no matter whether they disclosed economical ties to China.

The division did not back away from continuing to pursue nationwide safety circumstances involving China and its alleged endeavours to steal intellectual residence or other American details.

The Commerce Section previous yr imposed new export controls on superior computing and semiconductor parts in a maneuver designed to avert China from attaining particular chips.

Monaco explained on Thursday that the United States “ought to also pay back focus to how our adversaries can use personal investments in their firms to establish the most delicate systems, to gas their drive for a army and nationwide security edge.”

She pointed out that the Biden administration is “exploring how to observe the circulation of personal funds in critical sectors” to be certain it “doesn’t present our adversaries with a national security benefit.”

A bipartisan group of U.S. lawmakers past year identified as on Biden to concern an government get to increase oversight of investments by U.S. companies and men and women in China and other countries.