
How Technology Helps Restaurants Improve Safety, Quality, Consistency and Compliance   |

How Technology Helps Restaurants Improve Safety, Quality, Consistency and Compliance   |
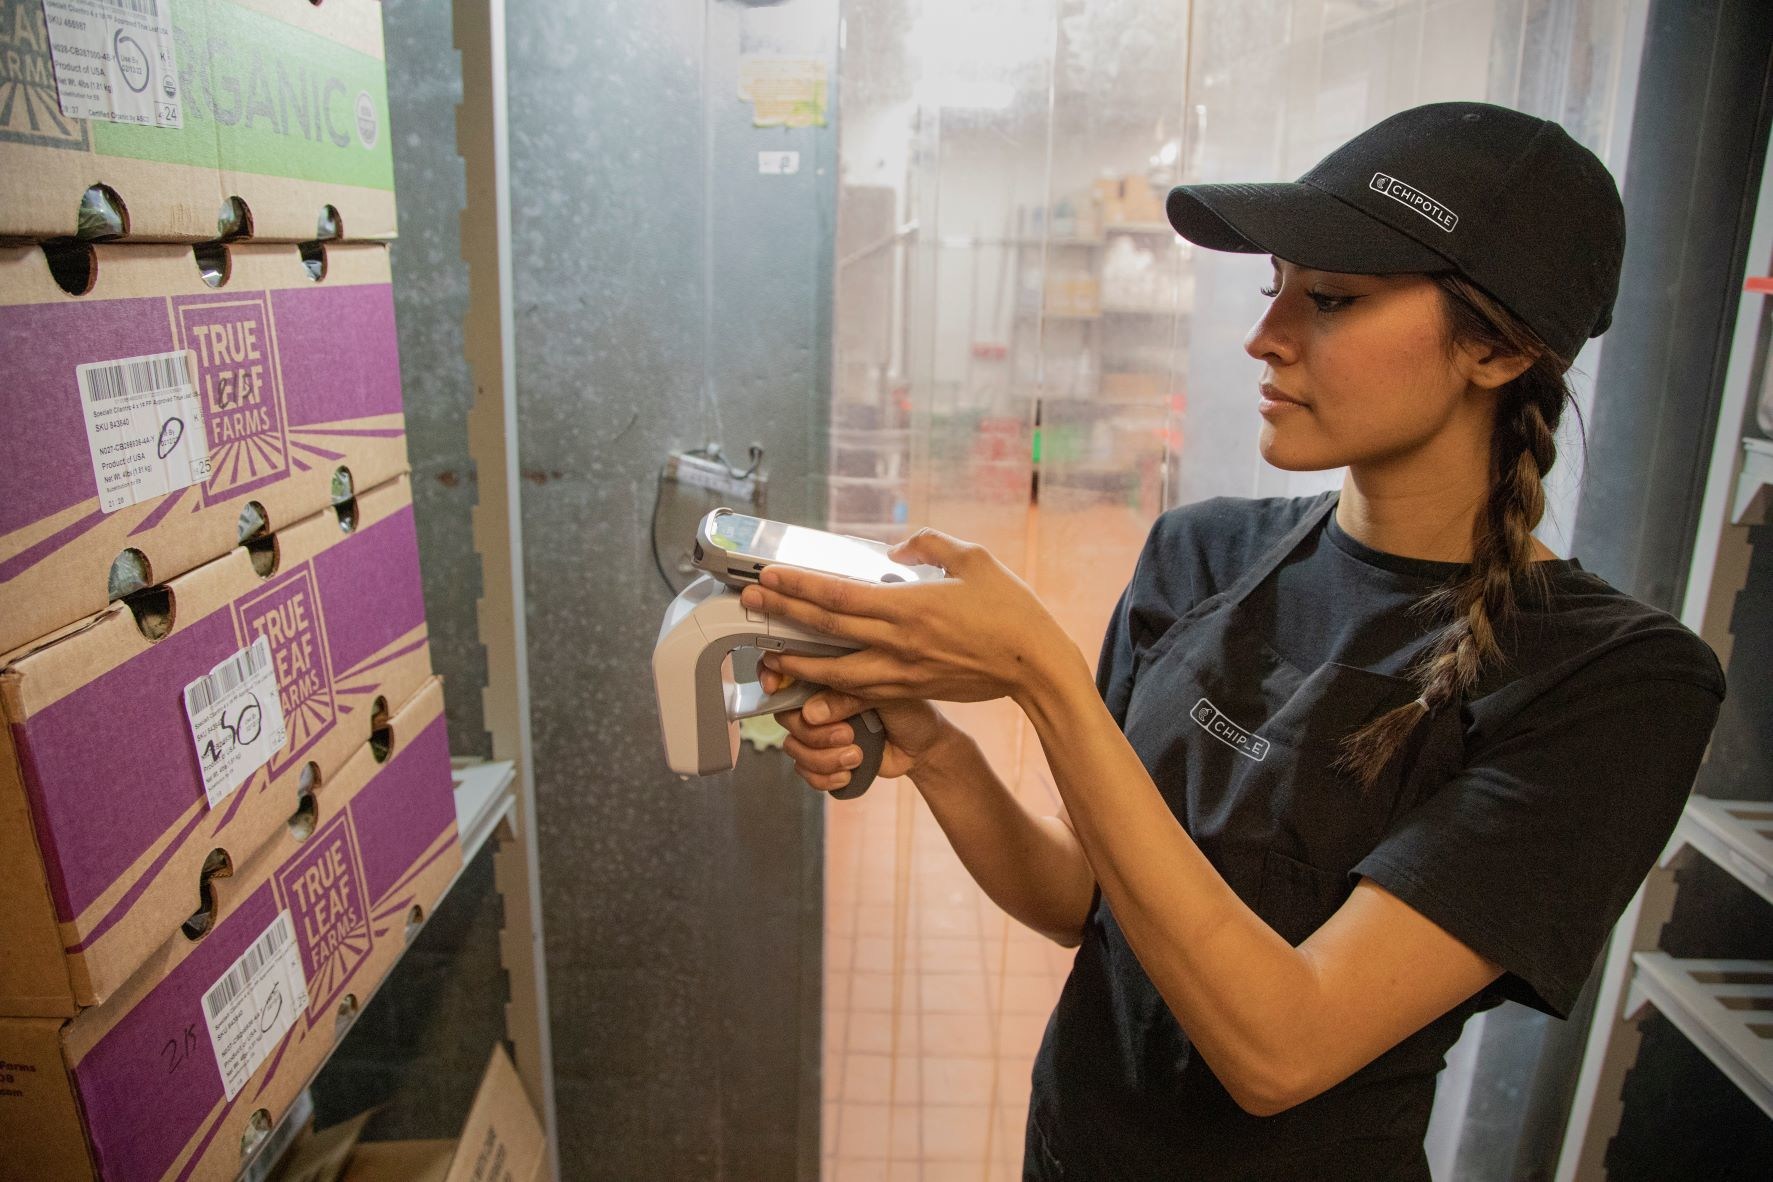
Chipotle is screening RFID technology to enhance its traceability and stock units. Chipotle is one of the 1st major restaurant firms to leverage RFID case labels to observe elements from suppliers to restaurants via serialization.


By Paul Damaren, Executive Vice President, Small business Improvement at RizePoint, and Francine L. Shaw, CEO of Savvy Foods Basic safety – 2.6.2024

Starbucks works by using AI and IOT to remotely monitor and fantastic-tune its espresso machines for a regular coffee knowledge. Chick-Fil-A is utilizing AI to increase food safety. Chipotle is piloting radio-frequency identification (RFID) label methods to enhance functions and trace ingredients. These manufacturers are demonstrating that tech methods are no for a longer time “nice to have” luxurious objects. They’re necessities for cafe manufacturers that prioritize continually great – and safe – ordeals.

Starbucks makes use of AI and IOT to remotely monitor and fine-tune its espresso equipment for a dependable coffee encounter.

As the cafe/hospitality labor lack is lastly easing, tech will be instrumental in onboarding new staff, strengthening teaching, guaranteeing safety and quality protocols are meticulously (and continuously) followed, maximizing compliance, and keeping cultures of excellence.

Below are some tips to complete this:

  • Adopt built-in electronic answers. Dining places ought to adopt integrated tech answers to boost protection, excellent, accuracy, transparency, regularity, and compliance – all variables that contribute to brand name excellence. Guide programs and disjointed tech stacks won’t present holistic views of crucial info throughout an company. Savvy operators are making use of integrated know-how to get obvious, exact insights for much better decision-making and more optimized operations.
  • Prioritize basic safety, high quality, and compliance. This yr marks the 30th anniversary of the Jack-in-the-Box foodborne disease outbreak, wherever 732 buyers have been sickened and four died. Yet, regrettably, foodborne sickness stays a large difficulty in our state. Every single year, 48 million (1 in 6) People get ill from contaminated food items or drinks. Our sector ought to do much better! Prioritize a food stuff protection lifestyle, exactly where all workers perform with each other to improve security and limit pitfalls.
  • Modernize your teaching efforts. Swap out your out-of-date schooling applications in favor of something additional present day, related, and tech driven. Build a collaborative tradition of studying, the place your total staff feels like they are “in it together” to create a protected manufacturer experience. Really do not just convey to workforce what to do but demonstrate why the policies are so critical. Employees will be a lot more probably to comply when they fully grasp why the guidelines are in put. Insert extra interactive tech things to your training method, these types of as microlearning platforms, learning administration methods, AI, and gamification, to make the info much more engaging and unforgettable. Also – coaching need to be an ongoing effort and hard work – not just a 1 and performed endeavor. Tech resources are instrumental in delivering key facts, reinforcing lessons, offering updates, and sending reminders.
  • Improve functions. Tech answers can enhance all aspects of your functions, from improving upon client loyalty packages to monitoring shopper practices so you can make better conclusions for the long run. Integrated tech instruments can assist with all areas of the enterprise, including budgets, scheduling, forecasting, stock, purchasing, and far more. Electronic tools are an investment decision, but they present a massive ROI, as they will permit your brand to save on labor expenditures, lessen the threat of human error, raise efficiency, streamline scheduling, and far more. All of these improvements will enhance important metrics, together with profitability.
  • Enhance traceability. Place absent the pencil and paper and enter information into tech techniques as an alternative. Tech instruments are the only way to speedily, easily, and properly keep track of your data – you simply just cannot do this applying antiquated paper units or Excel spreadsheets. And traceability matters throughout the full source chain. Food stuff security and QA must get started at foods products’ position of origin and keep on all along the provide chain right up until the food items is (securely) served to your visitors. Make it standard protocol to conduct typical supplier audits to be certain that all foods basic safety and QA procedures are currently being followed in advance of the foodstuff even arrives at your restaurant. Tech instruments will streamline and simplify this exertion.
  • Faucet into employees’ tech skills. Layoffs at tech businesses (which include Alphabet, Spotify, Twitter, and Meta) implies tech-savvy workers are wanting for new careers, and have useful tech skillsets, awareness, and skills that the hospitality business must leverage. If your new workforce provide tech expertise to the desk, use this to acquire new means to elevate functions, minimize food stuff waste, boost sustainability, and automate day to day jobs. Even if your new personnel didn’t occur from Google or Twitter, they’ll bring refreshing perspectives and ideas to your firm. Question for their ideas – they may perhaps challenge-address in a total new way.
  • Use reward techniques. Amid the labor shortages, your workforce have most likely been functioning additional shifts and using on more tasks, and might be emotion worn out, overcome, and/or burnt out. An inflow of hospitality workers will, hopefully, reduce some of this load. Exhibiting sincere appreciation for your employees’ hard do the job – and their commitment to remarkable basic safety and QA requirements – will go a long way in boosting employee satisfaction, inspiration, productivity, and loyalty. Deliver fiscal bonuses to employees who are going “above and beyond” to deliver a safe, large-top quality knowledge for your friends. Though you may possibly believe it’s not feasible to give out bonuses to continue to keep workers content, think about that shedding a entrance-line employee expenses a restaurant an regular of $5,864. It can make fantastic perception to give compact tokens of appreciation, like present playing cards to regional espresso retailers or a box of nice sweets. Spotlight an “employee of the month” to workers members who go the extra mile. These “seemingly small” gestures will be a enormous deal to your staff.

Places to eat might be concerned that they can’t afford to pay for to adopt tech methods but, frankly, they just can’t afford to pay for not to. As the labor lack ultimately softens and you welcome new workforce to your corporation, tech solutions will be instrumental in assisting your restaurant strengthen your basic safety, good quality, accuracy, transparency, consistency, and compliance. Try to remember: you can have the ideal menu, welcoming décor, and most beloved cooks in city, but the most important detail that your cafe can supply is a continually safe encounter.

Paul Damaren is Govt Vice President, Small business Improvement at RizePoint, a technological know-how chief in the meals safety, quality administration, compliance, and social responsibility room. RizePoint’s quality administration software program options assist companies, like Starbucks, McDonald’s, Marriott, and much more, retain manufacturer guarantees as a result of their excellent, security, and compliance endeavours. Consumers obtain better info, see needed actions previously, and act faster to proper issues prior to they develop into high-priced liabilities.

Francine L. Shaw, CEO of Savvy Food items Protection, is a prosperous entrepreneur, creator, podcast host, and speaker who spent 20+ several years operating in the foodservice market. Her career has provided accomplishing providers (running husband or wife, company/private trainer, overall health inspector, 3rd party inspector, adjunct professor) in many sectors of the foodservice business. She has penned 200+ posts for national trade journals and appeared on Dr. Oz, the BBC Earth Sequence Radio, and iHeart Radio as a food stuff basic safety expert.

Are you an field believed chief with a stage of perspective on cafe technology that you would like to share with our audience? If so, we invite you to review our editorial guidelines and submit your article for publishing thing to consider.
Cyber security expert surprised by lack of public charging port safety awareness

Cyber security expert surprised by lack of public charging port safety awareness
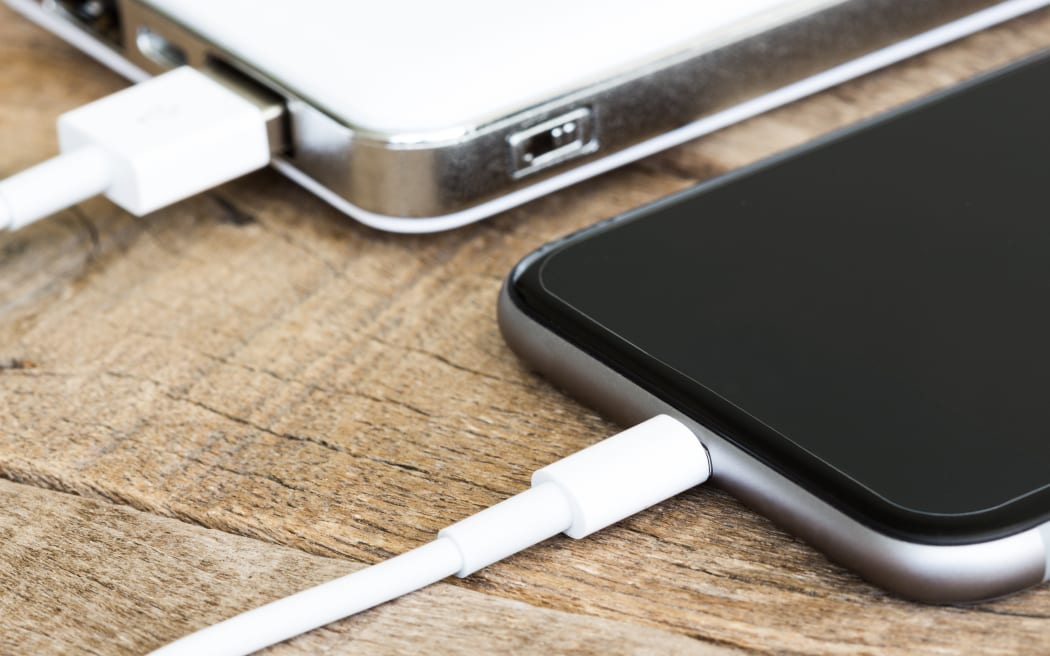
closeup phone charging white power bank portable devie

The potential risks of plugging gadgets into open up charging ports have been recognized for some time, but general public consciousness may well stay restricted.
Image: 123rf

A cyber stability qualified says he is amazed by how several persons in New Zealand keep on being unaware of potential risks posed by plugging telephones into USB chargers in community spaces.

Public charging stations are conveniently dotted around the outlets, airports and inns throughout the country.

Nevertheless, a new tweet by the the Federal Bureau of Details (FBI) warning the US community to prevent utilizing these because of to the risk of hacking. It has also served to remind New Zealanders of the hazards of utilizing community charging ports.

The FBI claimed “poor actors” experienced located ways to use these to introduce malware and monitoring application on to equipment.

Cyber security company Cert NZ has echoed the warnings. Menace and incident reaction team supervisor Jordan Heerspring told Checkpoint men and women ought to not to plug telephones and laptops instantly into people public USB charging ports.

“You really should be bringing your personal charging product, which you can plug into a wall socket, and then use that to charge your units,” he explained.

“In the airports you can expect to see community charging stations, some motels will have them even in the rooms. Some buses if they are pleasant extravagant buses, and even some planes will have them. So all of them are most secure to prevent, if you can.”

Heerspring explained it was not a significantly nicely-publicised piece of assistance, even if prolonged-standing.

“If I am remaining entirely trustworthy, I thought this was pretty community understanding. But talking to mates and spouse and children lately, I have found out that there are a whole lot of people who are not mindful of this. I am pretty happy that there is been some dialogue going all-around and raising that recognition for individuals.”

He suspected the FBI warning mirrored an maximize in cyber attacks involving charging ports in the US.

Even so, the fact was most ports had been in all probability good to use in New Zealand, Heerspring reported.

“We will not see a large amount of these attacks, but they’re genuinely simple points to retain you protected from, our advices is it is really ideal to stay clear of them.”

Hackers have devised ways to infiltrate the bits of application and components guiding the charging stations, so that an attacker can likely these use to load possibly destructive program onto equipment, or they can use that to extract details straight from units, he claimed.

“With the two of all those strategies, they’re going to be ready to extract own or other delicate or fiscal data from your machine if they are exploiting that distinct charging station.”

Cyber prison could accessibility the information and facts remotely, or may well have to return to the charging port, relying on the malware utilised, he claimed.

“It truly is type of like creating a street to the enemy camp. You can nonetheless have your gates up, so you will find continue to some safety measures that they will have to bypass, but giving them their accessibility invites them to do that.”

Being aware of your phone has been compromised is at times tricky, but there are some symptoms to look out for.

“There’s a handful of items that are truly worth wanting further into, like if your cellular phone is working very little by little, noticeably a lot more so than standard. Or if you get diverse apps or windows popping up that you really don’t assume or have not informed the product to do. Which is well worth getting investigated,” he claimed.

One more piece of essential suggestions was in no way plug a USB unit into your cell phone or laptop if you did not know its resource.

“If you obtain a USB unit, a tiny USB vital or get presented one – specifically if you will not absolutely believe in that human being – you shouldn’t be placing that into your own laptops or phones or other devices at household,” he explained.

“Additional generically, hold two-variable authentication on your accounts and have excellent password hygiene and those people a few items, along with retaining your gadgets updated, so patching to the most recent versions, will maintain you safeguarded from the bulk of the attacks out there.”

Amazon will spend $200 million on safety technology across its transportation network in 2023

Amazon will spend 0 million on safety technology across its transportation network in 2023

Safety is integral to every thing we do throughout our operations at Amazon—every working day, in each region, and especially on the street. As we function to produce for our clients, we carry on to innovate and progress basic safety attributes in the vans and vans we deploy, trying to keep the protection of our associates and communities exactly where we supply as our prime priority.

A challenge as elaborate as roadway safety calls for potent leadership throughout each the general public and personal sectors. Amazon has assisted guide the way in investments and improvements, and I’m very pleased to share some highlights of how Amazon is previously doing the job towards the objectives outlined in the U.S. Office of Transportation’s Countrywide Roadway Protection Method (NRSS). The examples underneath are just about every part of a $200 million financial investment in new security technological innovation, and portion of our continuing function to ensure Amazon autos and our shipping and delivery partners are protected on the street. It is our perception that the technologies we produce, together with improvements spearheaded by our field partners, can raise the bar on basic safety and lessen crash frequency and severity. And in a lot of situations, these innovations are improved for the environment, as well.

As we stick to by way of on our ongoing determination to safety, here are some of the tech-based mostly protection and sustainability methods we’re continuing to commit in this 12 months:

  • We’ve outfitted our middle mile trucking community, which is accountable for transport deals to and from our operations internet sites just before they’re dispatched for past mile supply to shoppers, with major protection technology, which includes computerized unexpected emergency braking, entrance-collision warning, steadiness management, lane-departure warning, facet-object detection, adaptive cruise regulate, and velocity limiters. Since 2017, Amazon tractors have also been equipped with driver-experiencing cameras that can enable recognize unsafe behaviors, like distracted driving, so drivers can be coached to prevent individuals behaviors from happening once again. Our trailers are outfitted with sensors to keep track of lights, anti-lock braking programs, cargo and door sensors, and more. Based on our entire engineering offer, devices manufacturers have indicated that Amazon is a pioneer in incorporating the most innovative security characteristics. And outside the house of our fleet, we’ve invested heavily in our route preparing navigation techniques and predictive analytics computer software to improved watch fleet protection. All of this is embedded into our cell technological know-how, referred to as Relay, that connects carriers and drivers to Amazon, and supplies them with navigation aid, actual-time driver-going through alerts, protection efficiency summaries, and further safety learning.
  • We’re also investing to expand in-motor vehicle digicam security know-how across our last mile supply community, which is established to assist reduce unsafe behavior in authentic time by minimizing driver-controllable safety incidents. This technological innovation identifies security occasions and delivers serious-time alerts. We began outfitting Amazon-branded shipping vans in the U.S. with this technological know-how in 2020 and, considering that rolling it out, we’ve found a 35 percent reduction in accident rates throughout our community. This technological innovation is a recreation-changer and will be in virtually 100 percent of Amazon branded cars by April 2023. This technologies is just a person of the basic safety attributes in our tailor made electrical delivery autos (EDVs) from Rivian, which are now providing Amazon offers in much more than 100 cities nationwide. In addition, these vans incorporate a 360-degree camera detection program so motorists can see exactly what is upcoming to them as they back again up and convert, unexpected emergency braking, rollaway detection, and extra. Beyond these in-motor vehicle systems, our Fleet Edge technology leverages facts to strengthen our routing software program to remedy for prevalent roadway problems these types of as construction, exact lane navigation, and unsafe maneuvers. This technological know-how has enhanced GPS accuracy by over 2.5 situations given that we began screening it, which aids our motorists be both equally safer and far more efficient—benefitting them, our communities, and our planet.
  • As we appear to the potential, we carry on to pilot cutting edge technologies in the transportation place. For example, we’re currently piloting strobing brake mild engineering in some of our trailers to present better visibility through braking to other folks on the road. This technological know-how has the possible to lower rear-stop collisions by as considerably as 30 per cent. And later on this year we’ll start out deploying an modern new basic safety feature in our trucking fleet that takes advantage of digital aspect mirror camera technology to minimize blind spots and boost the over-all safety of our presently market-major vans. As we pilot new technologies and learn about the basic safety efficacy, we’ll be ready to make info-pushed choices about whether or not and how to deploy these and other systems broadly across our fleet of automobiles and trailers.

We’re excited about the development we have manufactured to date and what our continued investments in 2023 will suggest as we do the job to repeatedly improve in both of those safety and sustainability. We will continue on to devote and invent to make sure our vans, delivery vans, trailers, and motorists are amid the safest on the road.

Why Companies Must Build Safety Into Tech Products

Why Companies Must Build Safety Into Tech Products

Even with a global multibillion-greenback cybersecurity field, the menace from destructive cyber-activity, from each legal and point out actors, carries on to grow. Although quite a few cyber incidents are hardly ever described by their victims, Verizon’s 2022 Facts Breach Investigations Report observed that ransomware assaults rose 13 percent that year—more than the earlier five yrs blended. These breaches bundled attacks that threatened public well being and protection, with a number of hospitals across the United States compelled to terminate surgeries and divert people for the reason that they ended up locked out of their units.

Over the previous 10 years, adversaries of the United States have developed increasingly subtle offensive cyber-capabilities. As cybersecurity expert Dmitri Alperovitch has argued, “We do not have a cyber dilemma. We have a Russia, China, Iran, North Korea problem.” Despite the fact that the concentrate on malicious actors—whether nation-states or criminals—is vital, cyber-intrusions are a symptom, rather than a result in, of the ongoing vulnerability of U.S. engineering.

What the United States faces is less a cyber trouble than a broader technology and culture problem. The incentives for establishing and marketing technological know-how have eclipsed purchaser safety in significance—a craze that is not distinctive to software package and hardware industries but one particular that has notably pernicious outcomes simply because of the ubiquity of these systems. As Us citizens have built-in technological know-how into nearly every single aspect of their lives, they have unwittingly appear to take that it is standard for new program and units to be indefensible by layout. They accept products that are launched to current market with dozens, hundreds, or even countless numbers of flaws. They take that the cybersecurity stress falls disproportionately on consumers and tiny companies, which are often least knowledgeable of the menace and the very least capable of shielding them selves.

Widespread use of unsafe technologies is compounded by a widespread practice in quite a few businesses and firms of relegating cybersecurity to the “IT people” or to a chief data safety officer. They are provided this responsibility, but not the resources, influence, or accountability to be certain that stability is properly prioritized against price tag, general performance, speed to current market, and new options. When cybersecurity is considered a area of interest challenge, somewhat than a foundational business risk, organizations are not motivated to be section of a broader remedy. As a consequence, victims of cyber-intrusions also seldom share facts about malicious activity with the govt or with other companies, allowing adversaries to reuse the exact approaches to compromise many victims.

People in america have to have a new design, a single they can trust to be certain the security and integrity of the technology that they use every single hour of each day. Issues really should be mounted at the earliest achievable stage—when technological innovation is intended somewhat than when it is currently being utilised. Less than this new model, cybersecurity would in the long run be the obligation of every CEO and each and every board. Collaboration would be a prerequisite to self-preservation. These kinds of a tradition shift calls for the recognition that a cyberthreat to a single business is a danger to all organizations. To get there, incentives require to favor lengthy-term investments in the protection and resilience of the cyberspace ecosystem, and the responsibility for defending that ecosystem have to be redistributed to favor these most capable and ideal positioned to do so, as U.S. National Cyber Director Chris Inglis argued in Overseas Affairs final calendar year.

Federal government can sleek the way by making apparent its expectations that technological innovation is intended and developed with basic safety as a top rated priority, by advocating that cybersecurity be viewed as a CEO-amount enterprise risk, by offering alternatives for entities to share cyberthreat facts, by keeping itself accountable for currently being transparent and incorporating worth, and by making sure that regulatory frameworks motivate businesses to comply. The Cybersecurity and Infrastructure Protection Company (CISA), founded by the U.S. Congress in 2018 to serve as the country’s cyberdefense company, is focused on these goals. But authorities are unable to solve the problem. Technological innovation brands have to have to consider obligation for the stability results of their customers as a elementary situation of basic safety if not, the essential infrastructure of the United States, its communities, and its way of daily life will keep on being at untenable possibility.

UNSAFE AT ANY CPU Pace

This is not the very first time that American industry has produced security a secondary concern. For the initial 50 percent of the twentieth century, standard wisdom held that automotive mishaps were being the fault of poor motorists. Similarly, today, if a organization suffers a cybersecurity breach, the company itself is blamed if it did not patch a acknowledged vulnerability. Such an technique neglects to question why the vendor that manufactured the technology needed to problem so lots of patches in the very first place or why failure to put into action a patch allowed a harming breach to occur.

Any automobile created today has an array of conventional protection features—seatbelts, airbags, antilock brakes, and so on. No a person would assume of purchasing a car that did not have seatbelts or airbags, nor would everyone pay out additional to have these basic safety things put in. With cars and trucks, on the other hand, prospects can see for by themselves whether or not the proper protection features are integrated. That is not the case with insecure units or computer software. The penalties of making use of unsafe technological innovation are also more durable to measure—school districts are shut down, food provide chains disrupted, chemical compounds manipulated at h2o procedure plants. The easily apparent security issues with cars and trucks also led to a uncomplicated resolution: govt action to compel adoption of particular protection steps with proven greater outcomes. Whether vehicles or other sectors these kinds of as aviation or professional medical devices, it took crisis to power people today to aim on the will need for extra basic safety steps. These kinds of a safety disaster is previously here in the cyber-realm, and now is the time to tackle it.

Consumers and enterprises alike hope that cars and other products and solutions they buy from respected suppliers will not have possibility of harm. The exact same must be real of technology items. This expectation calls for a elementary change of duty. Technological innovation vendors and computer software developers have to acquire possession of their customers’ protection outcomes rather than treating each individual product as if it carries an implicit caveat emptor. To realize this, each technological innovation provider will have to start by developing merchandise that are equally “secure by default” and “secure by style and design.”

These principles are connected but unique. Safe-by-default goods have potent stability features—akin to seatbelts and airbags—at the time of invest in, without extra fees. Robust protection should be a conventional function of just about each individual technological know-how products, particularly these that underpin crucial infrastructure these kinds of as vitality, drinking water, transportation, communications, and unexpected emergency products and services. Attributes of powerful security by default will evolve in excess of time, but at a bare minimum, application sellers have to include things like in their essential pricing options that protected a user’s identification, obtain evidence of probable intrusions, and command entry to sensitive data fairly than as extra highly-priced options.

A cyberthreat to a person group is a threat to all businesses.

Equally essential is engineering that is safe by design and style. This is the expectation that engineering is purposely built, built, analyzed, and maintained to significantly cut down the quantity of exploitable flaws prior to it is launched to the market place for broad use. Obtaining this final result will need radical improvements in how technological know-how is made, which includes in the code utilized to produce application. Flaws usually wind up in technological know-how items because creators hurry to release them to customers and are frequently much more centered on element expansion than stability. This spots the load of protection on millions of organizations and individual conclude buyers, who are the least organized to deflect cyberthreats.

It will not be quick to make these alterations and persuade businesses to construct and supply extra protected goods, but the U.S. government can start out by defining distinct attributes of technological innovation goods that are safe by default and secure by structure. It can also connect with out firms that carry on to introduce insecurity into the fabric of the U.S. financial system, and it can persuade companies that are building progress. Certainly, a amount of technological know-how companies, which include Google, Amazon, and Salesforce, are shifting in this course, providing sturdy safety steps by default for their customers and introducing revolutionary advancements towards security by style.

Each and every business ought to need transparency from its know-how vendors about no matter whether they have adopted solid protection practices. A single way to push technological innovation firms to adopt such procedures is for every single firm that purchases engineering to contain basic safety prerequisites as simple, very easily recognized criteria prior to procurement or use. The Biden administration has taken critical measures toward this target in establishing software program security needs for federal contractors. It is also advocating for advancement and voluntary adoption of labels that would obviously and merely convey essential safety information about Internet-linked purchaser units, these as toddler screens and webcams.

Constructing on this development will require U.S. companies to impose ever more stringent secure-by-default and secure-by-style requirements in the federal procurement course of action, which will support prompt market place adjustments towards producing a safer cyberspace ecosystem. U.S. President Joe Biden’s 2021 cybersecurity executive get is spurring these attempts, but improve need to come from all angles: businesses throughout sectors need to dedicate to demanding sturdy safety practices when obtaining or upgrading technological innovation, and engineering companies should really commit to getting obligation for the stability outcomes of their shoppers. Each individual technological know-how company should consider it a duty to make certain that its products and solutions are safe and sound for use and to alert consumers when that is not the case.

This sort of needs may possibly pose issues for smaller technological innovation firms and new entrants to the current market. To make certain that impressive and disruptive organizations can thrive in an ecosystem where heightened safety financial commitment is the norm, enhancement of stronger safety techniques should concentrate on results instead than on prescriptive, doctrinaire needs, enabling new industry entrants to introduce inventive suggestions in which protection is a good differentiator instead than a price tag.

THE BUCK STOPS Right here

Although the transition to safer technologies is a more time-term endeavor, each and every firm can choose techniques nowadays that will boost its cybersecurity. Initial and foremost, in each organization, the duty for cybersecurity demands to be elevated from the IT section to the board, the CEO, and the senior govt amount.

The tendencies here are encouraging. In a National Affiliation of Company Directors 2019–2020 survey, 79 per cent of public business administrators indicated that their board’s comprehension of cyber risk experienced significantly improved about the previous two decades. The same review, having said that, identified that only 64 percent thought that their board’s knowledge of cyber possibility was powerful enough that they could present powerful oversight.

To enhance individuals quantities, shareholders will have to make CEOs and board users individually accountable for taking care of cyber chance. This is largely a cultural alter: the place cybersecurity is regarded a area of interest IT difficulty, it is intuitive for accountability to slide on the main information and facts protection officer when cybersecurity is regarded a core enterprise danger, it will be owned by the CEO and the board.

In each individual business enterprise, the duty for cybersecurity requirements to be elevated.

Board members have distinctive energy to establish a tradition of company cyber obligation. They must assure that they and other senior executives are effectively educated on cyber risk, that cybersecurity criteria are appropriately prioritized in each and every company and technology final decision, and that selections to acknowledge cyber threat are scrutinized and revisited frequently. They must ensure that the thresholds for reporting potential malicious action to senior administration are not established far too significant “near misses” really should be claimed alongside with intrusion tries that be successful. They must make sure that suitable extensive-expression safety investments are obtainable to address the basic safety consequences of antiquated technological know-how. Most significant, board associates really should see that chief facts safety officers have the influence and methods required to make critical conclusions on cybersecurity. Decisions to prioritize revenue over security must be created transparently, with apparent ownership by CEOs and boards. The follow of blaming the main facts security officer or the IT department for organizational failings ought to end.

Vital to advancing company cyber obligation as a make a difference of good governance is the enhancement of a popular established of practices that corporations can use to figure out their exposure to cybersecurity danger. The Cybersecurity Framework produced by the National Institute for Requirements and Technological innovation is thought of an exemplar for developing and evolving a firm’s cybersecurity program. Many companies, however—particularly little and medium companies that comprise the offer chains of more substantial entities—find it tough to satisfy people benchmarks, typically mainly because they deficiency sources. To address this challenge, the Cybersecurity Performance Ambitions, released by CISA in late 2022 in partnership with NIST, can enable corporations ascertain which safety steps are most essential to minimize chance. Encouragingly, score companies have begun incorporating cybersecurity into their designs for examining creditworthiness, action that can more encourage businesses to embrace cyber obligation as a make a difference of institutional governance.

ALL Together NOW

Sustainable cybersecurity will also need rethinking how governments and industries interact with just one yet another. When most providers detect a cyber-intrusion, much too generally their default response is: call the lawyers, provide in an incident response agency, and share info only to the bare minimum extent expected. They frequently neglect to report cyber-intrusions to the authorities for anxiety of regulatory liability and reputational destruction. In today’s highly linked globe, this is a race to the bottom.

Standard Paul Nakasone, head of the U.S. Cyber Command, wrote a number of years ago about the doctrine of persistent engagement, in which U.S. forces contend with overseas adversaries on a proactive and recurring foundation. From a defensive perspective, the U.S. authorities have to as an alternative shift to a posture of persistent collaboration. These types of a lifestyle change requires that sharing turn out to be the default response, exactly where info about destructive exercise, including intrusions, is presumed required for the prevalent good and urgently shared involving industry and govt. Federal government and market need to perform collectively with reciprocal expectations of transparency and worth, where business does not have to be involved about punitive sanction. At last, interactions amongst the government and the private sector really should be frictionless, so that collaboration emphasizes scale, shared platforms, and data-driven evaluation.

In 2021, Congress set up the Joint Cyber Defense Collaborative to progress this posture by creating 1 U.S. government system for cyberdefense preparing and operations. It is still early times for the JCDC, but given that its development, for the 1st time, the governing administration, the non-public sector, and U.S. international associates came alongside one another to create joint cyberdefense options and help authentic-time data sharing on difficulties from the U.S. response to Russia’s legal invasion of Ukraine to endeavours to assistance safeguard the 2022 midterm elections. In excess of the coming year, CISA will continue on these endeavours, which will incorporate constructing resilience to ransomware attacks in coordination with the Joint Ransomware Endeavor Pressure and the International Counter Ransomware Initiative and will deal with the root will cause of incidents as discovered by the Cyber Security Critique Board. As the JCDC carries on to evolve, CISA and governing administration partners will try to uphold their close of the discount by becoming clear, responsive, and adding value, but the JCDC will only realize success if associates throughout the country, in each individual sector of the financial system, be part of the exertion.

WITH A Minimal Help FROM MY Good friends

Even as the cybersecurity neighborhood takes ways to create a sustainable technique to cybersecurity by the common adoption of safe engineering, corporate cyber accountability, and persistent collaboration, it must proceed to help people today and smaller organizations defend them selves, recognizing that everybody has a accountability to sustain a risk-free cyberspace setting, just as drivers nonetheless bear obligation for driving securely, even with seatbelts and airbags are incorporated as regular functions.

The philanthropist Craig Newmark has a short while ago referred to as for focused investment decision in “cyber–civil defense” to raise public consciousness of on the web safety. Along equivalent traces, CISA has been engaged in developing cybersecurity into K–12 curricula performing with “target wealthy, cyber poor” entities this kind of as little businesses, school districts, water amenities, hospitals, and regional election places of work to be certain they have the tools essential to improve their cybersecurity and major a nationwide cyber cleanliness marketing campaign to support all Us residents from “K through Gray” remain safe on the internet by using uncomplicated ways such as turning on multifactor authentication. The ultimate purpose, having said that, is to radically enhance product or service security, so technologies prospects almost never need to have to secure their devices on their individual. Though some protection steps will turn into as straightforward to use as a seatbelt, most businesses really should be protected ahead of they even “buckle up.” This basic level of protection will not be realized below today’s failing product. It is time for a new tactic, and if the federal government and the non-public sector can develop have faith in and function with each other, cyberspace can turn into safer for everybody.

Loading…

Bills vs. Bengals updates: ‘Monday Night Football’ game canceled after Buffalo safety Damar Hamlin suffers cardiac arrest

Bills vs. Bengals updates: ‘Monday Night Football’ game canceled after Buffalo safety Damar Hamlin suffers cardiac arrest

The Week 17 game between the Bills and Bengals has been suspended after an extremely scary injury to Buffalo safety Damar Hamlin.

Hamlin collapsed during the first quarter after making a tackle on Bengals receiver Tee Higgins. Medical staff administered CPR for several minutes before he was transported by ambulance to University of Cincinnati Medical Center. Per the NFL, he is currently in “critical condition.” 

The league released the following statement after the game was suspended for the night:

The NFL Players Association also released a statement:

Players were seen in tears as Hamlin received medical attention. Nearly the entire Bills team joined together in prayer as the ambulance left the field. 

Cincinnati held a 7-3 lead with 5:58 remaining in the first quarter when play was suspended. 

MORE: Damar Hamlin’s charity has received millions of dollars in donations to GoFundMe page since Bills-Bengals postponement 

The Sporting News is tracking live updates as the situation unfolds. 

Bills vs. Bengals score

  Q1  Q2  Q3  Q4  F 
Bills 3 — — — —
Bengals 7 — — — —

Bills vs. Bengals live updates, highlights from ‘Monday Night Football’

(All times Eastern.)

Thursday, Jan. 5

9:30 p.m.: The NFL officially announced Thursday evening that Bills-Bengals would not be resumed, and that it has been cancelled.

3:08 p.m. — According to the Associated Press, the NFL will not be resuming the game between Buffalo and Cincinnati. However, a league spokesman reportedly told The Buffalo News’ Jay Skurski no decisions have been made yet.

1:50 p.m. — In an update on Thursday afternoon, University of Cincinnati Medical Center doctors said Hamlin first began to wake up on Wednesday night. He asked, via pen and paper, who had won the Bills vs. Bengals game. 

11:51 a.m. — ESPN’s Adam Schefter said on Thursday he does not expect Bills vs. Bengals to be resumed. He believes final win percentages will be used to determine AFC playoff seeding, although other options are being considered. Those include allowing the No. 1 seed to choose between home-field advantage or a bye week, or potentially holding the AFC title game at a neutral site. 

10:29 a.m. — The Bills have now released another statement about Hamlin’s health. He has shown “remarkable improvement over the last 24 hours,” per the physicians caring for him at UC Medical Center, and “appears to be neurologically intact.”

He is still considered to be “critically ill” but is making “steady progress.” 

10:25 a.m. — Bills rookie cornerback Kaiir Elam posted an update about Hamlin on Twitter, saying that he is “doing better, awake and showing more signs of improvement.”

8:21 a.m. — ESPN’s Adam Schefter reports that Damar Hamlin’s father, Mario, addressed the Bills on a Zoom call Wednesday to provide an update on his son’s condition. He informed the team that Damar was “making progress.”

Wednesday, Jan. 4

9:16 p.m. — NFL EVP of Communications Jeff Miller offered some insight on what the NFL might do with regards to Bills-Bengals, and also acknowledged conversations are happening.

“That conversation about what we do with that game has begun,” Miller said Wednesday, per CBS Sports. “Troy, commissioner (Roger Goodell), some of the rest of us are involved in those conversations but they’re ongoing.

“Obviously we’re going to have to make a decision on that in the coming days, which we will. But there’s a lot of considerations in place there and a lot of people that we want to consult with — including the clubs involved — before that decision is final.”

In other words, conversations have started, but a decision isn’t imminent just yet.

2:29 p.m. — NFL executive vice president Troy Vincent says that the NFL hasn’t yet discussed postponing this week’s Bills vs. Patriots game. He did acknowledge that it would be a possibility if necessary, however.

1:30 p.m. — The Bills tweet that Hamlin is still in the ICU and in critical condition. However, there were “signs of improvement yesterday and overnight” and the ICU team will continue to monitor him.

12:29 p.m. — Rodney Thomas, a high school teammate of Damar Hamlin, said that he visited the hospital and that Hamlin is “doing good” and that he “has no doubt he’ll pull through.”

11:06 a.m. — Rooney also spoke to Cameron Wolfe of NFL Network on Wednesday. He said that “things are moving in the right direction” but again did not provide any medical updates on Hamlin.

10:42 a.m. — Harvey reports that Rooney told him Hamlin “still has a long way to go in his recovery” despite the “small, hopeful step” that occurred Wednesday.

9:27 a.m. — ESPN’s Coley Harvey spoke to Hamlin’s family friend Jordon Rooney on Monday. Rooney told Harvey that the family had gotten “promising readings” on Hamlin but he couldn’t go into specifics.

Hamlin remains in the ICU and in critical condition.

Tuesday, Jan. 3

8:51 p.m. — Glenn said Hamlin is on a ventilator and they’re attempting to get him to breathe on his own as he remains in the ICU. Glenn also said Hamlin has been flipped onto his stomach in order to help the blood in his lungs.

7:35 p.m. — Hamlin’s uncle, Doriann Glenn, said Hamlin is now using 50 percent of a ventilator instead of 100 percent. Despite having some damage on his lungs, Glenn says “that’s a good thing. That’s a good sign.”

1:32 p.m. — The NFL has also announced that the Bills vs. Bengals game will not be resumed this week. The league has “made no decision regarding the possible resumption of the game at a later date” as well.

1:26 p.m. — The Bills announce via a statement that Hamlin spent the night in the intensive care unit at the University of Cincinnati Medical Center. He remains there in critical condition.

11:49 a.m. — Hamlin’s family releases a statement thanking NFL fans for the “support shown to Damar during this difficult time.” They do not provide any more updates about Hamlin’s condition. 

1:48 a.m. — The Bills offer an official statement regarding what happened to Damar Hamlin.

12:41 a.m. — Paycor Stadium’s lights have gone blue for Damar Hamlin.

12:27 a.m. — The NFL still has not given an indication what will come of the Bills-Bengals game as the Bills return to Buffalo.

12:25 a.m. — NFL executive vice president of football operations Troy Vincent attempted to clarify details regarding news that the game would resume after a five-minute warming up period, which angered many. 

12:23 a.m. — The Buffalo Bills team busses depart Paycor Stadium

12:19 a.m. — Tee Higgins, who was involved in the play in which Hamlin collapsed, has tweeted, offering his prayers.

12:15 a.m. — The NFL held a conference call with reporters to provide clarifying details about what occurred in the wake of Hamlin’s injury. Unfortunately, no update was given on his health. 

Monday, Jan. 2

11:55 p.m. — ESPN Bills reporter Alaina Getzenberg has reported the majority of Bills team members have stayed in the locker room at Paycor Stadium. The team buses also still have not left. 

11:30 p.m. — Contrary to earlier reports, it now sounds like there will be no update forthcoming tonight from hospital officials. 

11:28 p.m. — Hamlin’s agent, Ira Turner, has issued a statement:

11:23 p.m. — In a post on Twitter, Josh Allen has asked for prayers in support of his teammate.

11:16 p.m. — Bills receiver Stefon Diggs was just shown on ESPN arriving at the hospital where Hamlin is receiving treatment. He appears to have traveled to University of Cincinnati Medical Center in an Uber and was on his own. 

11:06 p.m. — Joe Danneman of FOX19 Cincinnati is reporting the Bills are planning on flying back to Buffalo. However, some members of the organization will be staying behind with Hamlin and his family. 

10:53 p.m. — The sports world continues to hold its collective breath as we await an update on Hamlin. As of now, the information remains the same: The Bills safety is in critical condition at University of Cincinnati Medical Center. No players or coaches will be addressing the media tonight. However, local journalists have reported hospital officials are expected to provide an update sometime this evening. 

10:16 p.m. — In an official statement, the NFL has described Hamlin as being in “critical condition.” Here is the full statement from the league:

10:00 p.m. — We have just received word this game has officially been suspended by the NFL. There will be no more football tonight. It remains to be seen when, or if, this game will be completed. But for now, all that matters is the health of Damar Hamlin. 

9:55 p.m. — The two head coaches, Sean McDermott and Zac Taylor, just exchanged words in the tunnel. McDermott was on a phone call, then the two shook hands and spoke briefly. Members of the Bills’ staff have now begun clearing equipment off of the sideline. There’s no official word yet, but it appears very likely this game will be postponed or called off. 

9:45 p.m. — Per ESPN’s broadcast, Hamlin was transported by ambulance to the University of Cincinnati Medical Center. We’re still awaiting information on his condition. Here are the latest updates we have on Hamlin. 

9:28 p.m. — The game remains suspended as we await any sort of information on the condition of Bills safety Damar Hamlin. He collapsed on the field in the first quarter after making a tackle on Bengals receiver Tee Higgins. He was taken off the field in an ambulance after medical staff administered CPR for several minutes. As of right now, it’s unclear whether this game will resume tonight or not. But that’s of very little concern at the moment. There are simply no words to describe a situation as scary and unprecedented as this.

9:17 p.m. — The officials just announced this game has been temporarily suspended. Both teams are heading to the locker room. We will continue to provide updates on this situation as it develops. 

9:12 p.m. — Hamlin has been taken away in an ambulance. The entire Bills team was gathered in prayer on the field as it drove away. Hamlin’s current condition is unclear right now. It appears this game will continue shortly, but right now it’s hard to even imagine playing a football game after what just took place. 

9:07 p.m. — ESPN’s sideline reporter Lisa Salters just delivered an update and you could hear the emotion in her voice. Joe Buck reported that the medical staff has been administering CPR to Hamlin. We can only hope and pray for the best right now. A devastating and terrifying situation has unfolded here early in this game. 

9:03 p.m. — This is really a distressing situation. Josh Allen and several other Bills players are in tears as an ambulance has now come onto the field. Really worrying moments in Cincinnati right now.

8:59 p.m. — Scary scene here. Hamlin made the tackle on that last play and initially got up onto his feet, but he staggered and fell back to the turf. The medical staff is bringing a stretcher out. McDermott looks very concerned. 

8:56 p.m. — The Bengals come out swinging once again on their second drive of the night, and a Burrow pass to Tee Higgins picks up 13 yards to quickly move them across midfield. Another Bills defender is down hurt at the end of the play, this time it’s safety Damar Hamlin. Tough start to this game for Buffalo’s defense. 

8:53 p.m. — Allen’s left leg got rolled up on a bit at the end of that drive. It looked like his left knee may have even hyper-extended slightly. He was walking a little tenderly to the sideline, but he’s a pretty tough guy and it doesn’t seem like he’s in any danger of leaving this game. 

Bengals 7, Bills 3

8:51 p.m. FIELD GOAL — Tyler Bass connects from short range to put the Bills’ on the board. 

8:49 p.m. — A mishap on 2nd down brings up 3rd and 3 for Buffalo from inside the Bengals’ 10. Allen drops back and tosses left for Cole Beasley, but it goes off the receiver’s hands and falls incomplete. That will force a field goal attempt. 

8:47 p.m. — A second catch by Diggs picks up another Bills’ first down, then rookie running back James Cook enters the game and rips off two nice runs to move the ball into the red zone. 

8:44 p.m. — On 3rd and inches, Devin Singletary lowers his shoulder and bangs ahead for a first down. Buffalo has the ball across midfield, but they have to burn a timeout on the following play after Sean McDermott doesn’t like what he sees from the defense.  

8:42 p.m. — Buffalo’s first drive of the night starts as it often does — with an Allen completion to Diggs. That picks up 17 yards to pick up a quick first down.

8:41 p.m. — If that first drive is any indication, it could be a long night for this Bills defense. Let’s see how Josh Allen responds. 

Bengals 7, Bills 0

8:38 p.m. TOUCHDOWN — Wow, what an incredible start for Cincy! A lightning-quick drive ends in a touchdown after Burrow connects with Tyler Boyd in the back of the end zone! The Bengals have the lead in no time! 

8:36 p.m. — Burrow sneaks it up the middle to convert for a first down. One play later, he throws it over the middle to Hayden Hurst, who attempts a wild hurdle over a defender but gets dragged down inside the Bills’ 15-yard line. 

8:34 p.m. — Joe Mixon gets his first handoff of the night and powers forward to set up 3rd and inches. Buffalo cornerback Taron Johnson was shaken up and is down on the field. 

8:31 p.m. — On the first play from scrimmage, Burrow goes deep down the left sideline to Chase. Tre’Davious White had a hold of Chase in coverage, and that’ll draw a pass interference call. Rough start to the night for White. 

8:30 p.m. — Here we go. Kickoff is just moments away in this massive late-season AFC showdown. The Bengals won the toss and have elected to receive first. Burrow and his offense will take the field to get things underway.

8:21 p.m. — Joe Burrow and Ja’Marr Chase have formed another deadly duo recently. Chase hasn’t been held under 7 catches in a game since Week 4 against the Dolphins.

7:53 p.m. — Stefon Diggs: A man of the people. 

7:35 p.m. — This duo has been outstanding once again this season. They’ll need to be at their best in one of their biggest tests of the season tonight. 

7:23 p.m. — Joe Burrow has his team playing some great football at the right time. Can he and the Bengals topple the AFC’s top dog tonight?

What time is the NFL game tonight?

  • Date: Monday, Jan. 2
  • Time: 8:30 p.m. ET

The game is scheduled to kick off at 8:30 p.m. ET from Paycor Stadium in Cincinnati, Ohio. The weather forecast calls for cloudy skies with temperatures in the high 50s Fahrenheit and a chance of thunderstorms later in the evening. 

What channel is Bills vs. Bengals on today?

  • TV networks: ESPN (U.S.) | TSN1/3/4, RDS2 (Canada)
  • Live stream: ESPN.com, ESPN App, ESPN+, fuboTV (U.S.) | DAZN (Canada)

Buffalo and Cincinnati will face off on the final “Monday Night Football” broadcast of the season. ESPN will be airing the game nationwide in the United States, with Joe Buck (play-by-play), Troy Aikman (color commentary) and Lisa Salters (sideline reporting) on the call from Cincy.

Fans in the United States looking for a live stream can find one on fuboTV, which offers a free trial. Other options include ESPN.com, ESPN+ or the ESPN App. 

Viewers in Canada can tune in on TSN 1/3/4 or RDS2, or via live stream with DAZN, which features every NFL game. 

Sporting News’ Jacob Camenker also contributed to this report.