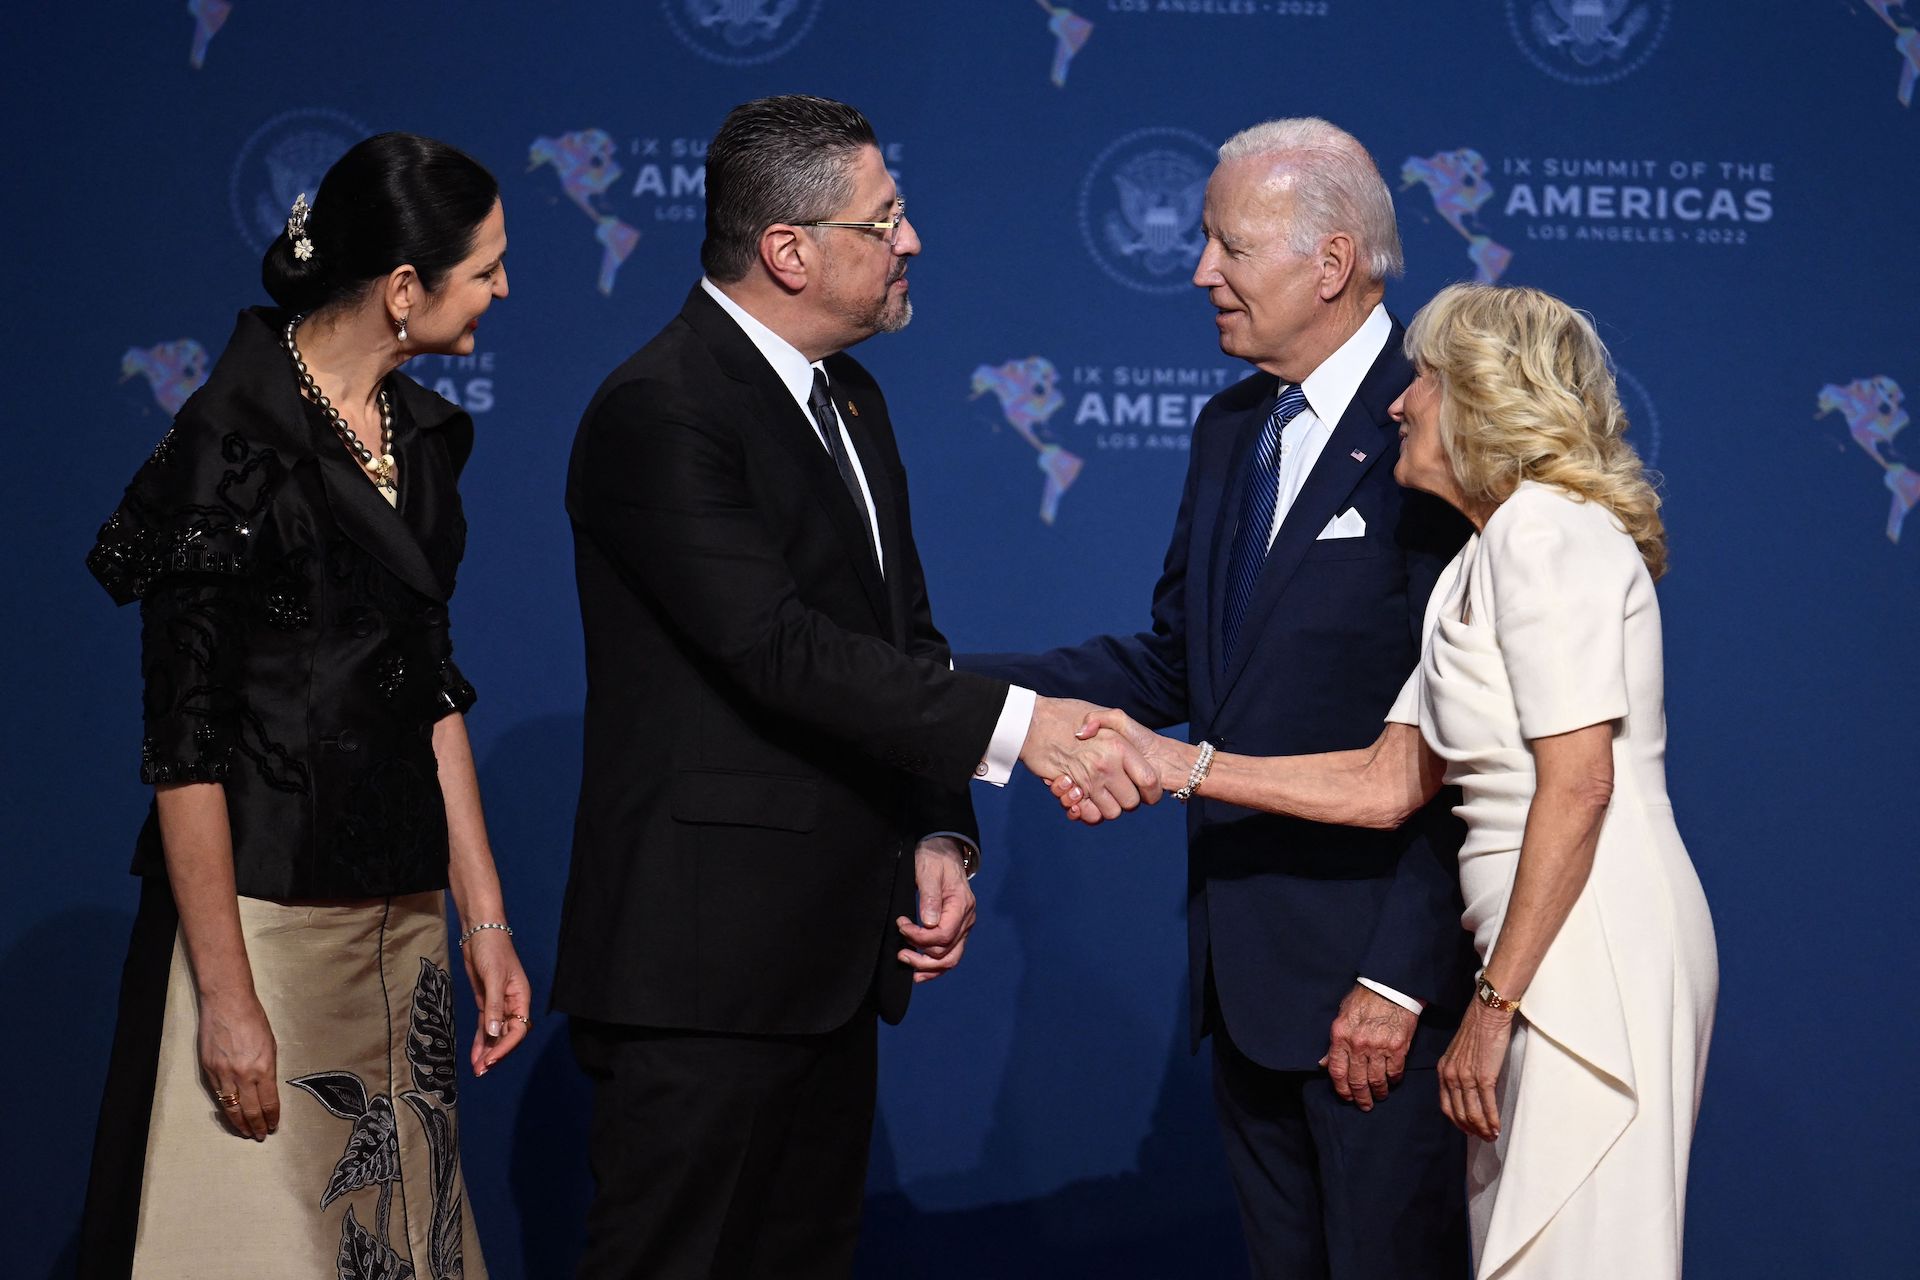
The U.S. govt will give Costa Rica with $25 million in assistance to bolster its cybersecurity initiatives, a senior administration official stated Wednesday, approximately a year right after the place experienced a collection of devastating ransomware assaults at the arms of a Russian-joined cybercrime team.
The funding will come in reaction to a “direct request” from Costa Rican President Rodrigo Chaves to President Biden, the official instructed reporters Wednesday.
“It will aid the authorities of Costa Rica’s get the job done to protected its networks and defend its essential infrastructure,” the formal reported. “It really displays the president’s broader endeavours to aid partners attempts to develop safe, open up and trustworthy digital infrastructure all-around the environment.”
The funding commitment to Costa Rica arrives a month right after U.S. Ambassador to Albania Yuri Kim declared a $25 million grant there in direct reaction to a series of damaging Iranian cyberattacks targeting Albanian government and non-public networks previous summertime. Albania severed diplomatic ties with Iran right after the assaults, and the U.S. government sanctioned the Iranian Ministry of Intelligence in response to the attacks.
The announcement of the Costa Rican cybersecurity aid was declared as Biden opened the 2nd Summit for Democracy along with the leaders of Costa Rica, the Netherlands, the Republic of Korea, the Republic of Zambia and many others. Costa Rica has also utilized to join the Counter Ransomware Initiative introduced late previous 12 months, the formal mentioned.
1 of Chaves’ very first formal functions following currently being sworn into office Might 8, 2022, was to declare a nationwide crisis as a end result of the Conti ransomware attack that struck a number of governing administration agencies April 17, pilfering the govt there of a lot more than 672 gigabytes of information. Two times prior, on Could 6, the U.S. State Office declared a reward of $10 million for details main to the identification or spot of any one who held a management purpose with Conti. An additional $5 million reward from the U.S. government was offered for any information major to the arrest and or conviction of anybody associated with or attempting to participate in a Conti ransomware attack.
Conti’s attack on Costa Rica hobbled significant solutions in the region, which includes tax assortment units and healthcare appointments. A second attack, afterwards in Could, connected to HIVE, strike the country. Brett Callow, a danger analyst with Emsisoft, explained the situation as “possibly the most major ransomware incident to day,” in reviews to Wired at the time.
In the days right after the Russian invasion of Ukraine, Conti posted a message declaring assistance of the Russian federal government. The public assistance in the long run fractured the organization, triggering enormous leak of Conti interior files and messages. That substance showed doable connections between some members of Conti management and aspects of the Russian government.
The “significance” of the attacks that Costa Rica endured bolstered the situation for U.S. funding, the formal reported Wednesday. Chaves believes his country’s aid for Ukraine “may have been a factor” in the scale of the attacks, the official said, underscoring the geopolitical implications of large-degree cybercrime.
“Clearly, in the current context, we realize that supporting our allies’ and partners’ security is crucial in the context of the function we’re executing supporting our European allies and partners from Russian cyberattacks, in the context of our broader opposition with China and the vital place Latin America plays in that as nicely,” the official explained Wednesday.
Safety is integral to every thing we do throughout our operations at Amazon—every working day, in each region, and especially on the street. As we function to produce for our clients, we carry on to innovate and progress basic safety attributes in the vans and vans we deploy, trying to keep the protection of our associates and communities exactly where we supply as our prime priority.
A challenge as elaborate as roadway safety calls for potent leadership throughout each the general public and personal sectors. Amazon has assisted guide the way in investments and improvements, and I’m very pleased to share some highlights of how Amazon is previously doing the job towards the objectives outlined in the U.S. Office of Transportation’s Countrywide Roadway Protection Method (NRSS). The examples underneath are just about every part of a $200 million financial investment in new security technological innovation, and portion of our continuing function to ensure Amazon autos and our shipping and delivery partners are protected on the street. It is our perception that the technologies we produce, together with improvements spearheaded by our field partners, can raise the bar on basic safety and lessen crash frequency and severity. And in a lot of situations, these innovations are improved for the environment, as well.
As we stick to by way of on our ongoing determination to safety, here are some of the tech-based mostly protection and sustainability methods we’re continuing to commit in this 12 months:
We’ve outfitted our middle mile trucking community, which is accountable for transport deals to and from our operations internet sites just before they’re dispatched for past mile supply to shoppers, with major protection technology, which includes computerized unexpected emergency braking, entrance-collision warning, steadiness management, lane-departure warning, facet-object detection, adaptive cruise regulate, and velocity limiters. Since 2017, Amazon tractors have also been equipped with driver-experiencing cameras that can enable recognize unsafe behaviors, like distracted driving, so drivers can be coached to prevent individuals behaviors from happening once again. Our trailers are outfitted with sensors to keep track of lights, anti-lock braking programs, cargo and door sensors, and more. Based on our entire engineering offer, devices manufacturers have indicated that Amazon is a pioneer in incorporating the most innovative security characteristics. And outside the house of our fleet, we’ve invested heavily in our route preparing navigation techniques and predictive analytics computer software to improved watch fleet protection. All of this is embedded into our cell technological know-how, referred to as Relay, that connects carriers and drivers to Amazon, and supplies them with navigation aid, actual-time driver-going through alerts, protection efficiency summaries, and further safety learning.
We’re also investing to expand in-motor vehicle digicam security know-how across our last mile supply community, which is established to assist reduce unsafe behavior in authentic time by minimizing driver-controllable safety incidents. This technological innovation identifies security occasions and delivers serious-time alerts. We began outfitting Amazon-branded shipping vans in the U.S. with this technological know-how in 2020 and, considering that rolling it out, we’ve found a 35 percent reduction in accident rates throughout our community. This technological innovation is a recreation-changer and will be in virtually 100 percent of Amazon branded cars by April 2023. This technologies is just a person of the basic safety attributes in our tailor made electrical delivery autos (EDVs) from Rivian, which are now providing Amazon offers in much more than 100 cities nationwide. In addition, these vans incorporate a 360-degree camera detection program so motorists can see exactly what is upcoming to them as they back again up and convert, unexpected emergency braking, rollaway detection, and extra. Beyond these in-motor vehicle systems, our Fleet Edge technology leverages facts to strengthen our routing software program to remedy for prevalent roadway problems these types of as construction, exact lane navigation, and unsafe maneuvers. This technological know-how has enhanced GPS accuracy by over 2.5 situations given that we began screening it, which aids our motorists be both equally safer and far more efficient—benefitting them, our communities, and our planet.
As we appear to the potential, we carry on to pilot cutting edge technologies in the transportation place. For example, we’re currently piloting strobing brake mild engineering in some of our trailers to present better visibility through braking to other folks on the road. This technological know-how has the possible to lower rear-stop collisions by as considerably as 30 per cent. And later on this year we’ll start out deploying an modern new basic safety feature in our trucking fleet that takes advantage of digital aspect mirror camera technology to minimize blind spots and boost the over-all safety of our presently market-major vans. As we pilot new technologies and learn about the basic safety efficacy, we’ll be ready to make info-pushed choices about whether or not and how to deploy these and other systems broadly across our fleet of automobiles and trailers.
We’re excited about the development we have manufactured to date and what our continued investments in 2023 will suggest as we do the job to repeatedly improve in both of those safety and sustainability. We will continue on to devote and invent to make sure our vans, delivery vans, trailers, and motorists are amid the safest on the road.
Do you struggle to hire and retain cybersecurity professionals? Does it seem like this problem is only getting worse, right when attackers are getting more sophisticated?
You’re not alone.
The International Information System Security Certification Consortium’s (ISC²) annual cybersecurity workforce study found a worldwide gap of 3.4 million cybersecurity workers — and that’s after this workforce grew just over 11{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1} from 2021 to 2022, adding 464,000 jobs last year alone.
This isn’t just a risk of burnout among the current security staff, but a risk to the whole organization. The same study found that a significant percentage of the 11,779 practitioners and decision makers it surveyed reported that the following things that they have experienced might have been mitigated if they had enough cybersecurity staff:
And, the study reported, each of these fears saw an increase year over year.
So why is it so hard to recruit security engineers? More and more, it seems more like it’s not them — it’s you.
Cybersecurity job descriptions trend toward the generic, yet excessive, putting an impossible load on one person. Security job ads not only tend to ask for unrealistic levels of experience and credentials, but they also lack connection to the specific organization’s challenges and to candidates’ desire to find purpose in what they do.
A lot has to change before the tech industry can even begin to fill the ever-increasing demand for cybersecurity. Read on to learn how to successfully recruit people to fill tech’s hottest jobs: cybersecurity professionals.
Broad Job Descriptions Scare Off Candidates
A big part of the problem with recruiting security professionals comes down to organizations not understanding their particular needs — which are subsequently reflected in catch-all job descriptions.
“When people say: ‘I want someone to do cybersecurity,’ they probably aren’t being very specific,” Olu Odeniyi, a cybersecurity and digital transformation consultant, told The New Stack.
Organizations don’t really know what they need because security is a broad field. For instance, the U.K. Cyber Security Council has actually identified 16 specializations within cybersecurity, which can encompass, include or sometimes overlap with information security and privacy.
An important part of his role is helping boards understand cybersecurity better. In fact, one of the most in-demand cybersecurity roles is creating cross-company security awareness. This typical lack of understanding is why Odeniyi had a client’s chairperson declare to his board: “We’ve had a cyber attack!” when really the company just had to address an important vulnerability.
Whether it’s privacy regulations, cyber threats or simply commercial risks, he continued, each organization has to ask itself what skills it really needs to keep itself secure: “An organization needs to do a risk assessment that’s unique to that organization.”
Odeniyi further recommended starting with the goals of the company, answering:
What’s critical to try and to achieve those goals?
What are the strategic requirements for those spaces?
What are the cybersecurity aspects to make that happen?
And then craft roles around those strategies.
As an example, Odeniyi told The New Stack about a mostly brick-and-mortar company that has made it part of its strategic goals to build an e-commerce site, application and back-office operations behind it. Cybersecurity and information security must be critical parts of that strategy from the start. Which roles are needed to help deliver that?
Then, he added, “Recruiters need to link these roles with the strategic objectives of the company so those people want to do that role,” and advertise them “not just as some sort of geek. Help them understand where they’re going, what they’re supporting.”
Sell the Purpose in Cybersecurity Roles
“We do a terrible job of marketing ourselves as an industry to get into,” Masha Sedova, co-founder and president of Elevate Security, told The New Stack.
“Most people think about cybersecurity as a hacker with a hoodie in a basement stealing bitcoins and hacking into systems. It’s actually about protecting someone’s retirement account so they can retire safely, protecting people who are vulnerable, protecting small businesses.”
Yet, she observed, the cybersecurity industry is missing the mark — and the marketing — in portraying the value of these roles to the betterment of lives. “I feel like we only show up with the hard edge,” she said. She advocated advertising security jobs as being less technical and more problem-solving, with an element of giving back and altruism.
“The mission of cybersecurity is incredibly powerful and it meets a lot of people’s need for making an impact for the world,” she said. “If we can change how we talk about it, if people can realize their time and energy can be used to be protective of digital citizens, we can attract a new generation.”
Not to disregard the technical prowess needed, Sedova clarified: “I think there are a lot of people who are capable of running the technical — but you don’t have to be a perfect coder.”
Biggest Barriers to Filling Security Jobs
There are many reasons the cybersecurity candidate pool is shallow, but everyone interviewed for this piece cited the same one: the absurdity of catch-all cybersecurity job ads.
“Job descriptions are often terrible. [They] ask for more experience than actually exists in a certain technology,” Chris Hughes, chief information security officer and co-founder of Aquia, a cybersecurity services company, as well as host of the Resilient Cyber podcast and adjunct professor at University of Maryland Global Campus, told The New Stack. “The requirements are ridiculous and people don’t apply.”
Even roles described as “entry-level” often come with unrealistic prerequisites.
“We put really high entry-level bars — minimum years of experience, certifications which are long and cumbersome to get, a degree in cybersecurity,” Sedova said, red-flagging these as both financial and time barriers to entry.
Before co-founding her own risk-management platform, she hired and managed security expert teams, including at Salesforce, and has found that folks coming from non-traditional backgrounds bring a great problem-solving mindset to security.
“The mission of cybersecurity is incredibly powerful and it meets a lot of people’s need for making an impact for the world. If we can change how we talk about it, if people can realize their time and energy can be used to be protective of digital citizens, we can attract a new generation.”
—Masha Sedova, co-founder and president, Elevate Security
Cybersecurity job descriptions, Odeniyi observed, often only focus on technical requirements. “People think cybersecurity is about IT,” he said. “Cybersecurity sits in the IT department, but cybersecurity is about people, processes, and tech — not just technology.”
In writing the job ad, focus on the goals and purpose of the role, and not on just the detailed tasks and certifications you think a candidate needs.
Unsure how to improve? Follow Naomi Buckwalter on LinkedIn, as the information security expert shares a new entry-level cybersecurity job daily, underlining good and bad examples, and flagging openings that are good for career changers and for non-technical versus technical candidates.
How to Improve Hiring Processes
On top of the off-putting job descriptions, it may actually be the arduous selection process itself that is deterring applicants.
“The hiring process for cybersecurity professionals can be difficult and time-consuming, discouraging some candidates from applying or preventing companies from pursuing specific candidates,” Philip Chan, adjunct professor at the School of Cybersecurity and Information Technology at the University of Maryland Global Campus, told The New Stack.
Even for someone interested in starting out in or moving into cybersecurity, there’s no clear path to entry beyond a degree, a bunch of certifications and an existing network.
“Job descriptions are often terrible. [They] ask for more experience than actually exists in a certain technology. The requirements are ridiculous and people don’t apply.”
—Chris Hughes, chief information security officer and co-founder, Aquia
“We don’t know how to interview creatively for these roles,” Sedova said, pointing to how other tech job processes leverage logic questions and other ways to work out how a candidate problem solves, while cybersecurity still heavily relies on past experience and certifications — despite the immense talent gap.
Recent research out of Harvard and Stanford Universities explored the characteristics of someone with a “security mindset,” which researchers qualified as three interconnected aspects:
Monitoring for potential security anomalies.
Investigating anomalies more deeply to identify security flaws.
Evaluating the relevance of those flaws in a larger context.
They found this mindset is developed by both professional and personal experience, with “curiosity about technical systems” emerging as the single most important quality for success in cybersecurity. The authors of the study suggested that employers and recruiters balance technical and qualitative evaluations:
“For example, they might combine a bug-bounty performance test with a task of explaining the relative risk of different bugs, given different sets of background assumptions. They might also ask candidates for their preferred sources of information about the relative risks of security flaws, or they might inquire about the candidate’s interactions with CISOs or other staff who are more likely to hold an evaluating-heavy role.”
It’s as much or more about thinking creatively and logically about vulnerabilities in a system, Sedova remarked, than it is about being able to put yourself in the mindset of an attacker. Can you create tests or experiences to test someone’s security mindset?
In both cybersecurity recruitment and advocacy, researchers at the University of Maryland, Baltimore County found that it’s essential to focus on situational context as well as on educating and speaking to different levels of technical understanding.
Upskilling for Security Skills In-House
In the absence of people to fill security jobs and considering that recruitment costs far more than retention, organizations should upskill their current employees.
“The field of cybersecurity is constantly evolving, which means that professionals need to update their skills and knowledge continuously,” Chan said. Companies trying to hire and retain cybersecurity professionals with constant training requirements can be challenging.”
Considering these trainings and certifications can cost upwards of $4,000, companies can consider paying for that education as a way to attract and retain talent.
A role Odeniyi would like to see more of in 2023 is cybersecurity culture management — “and I just made that role up because I’ve not seen it advertised,” he said.
Such a role would influence the whole culture of the company to consider the people, processes and training necessary to cultivate that cybersecurity mindset. An employer might be better at identifying the right personalities and skill sets among its existing staff rather than seeking them from outsiders.
Recognizing another gap, Odeniyi would like someone to lead the operationalization of cybersecurity, looking to define and support the continuous IT security operations in the needs of an organization.
“The fundamental issue is, technology changes very fast and faster than we can get laws and regulations in place to try to get faster, and faster than we can train up people into their sectors,” he said. This position would require someone with a cross-functional role and mindset.
Hughes pegged the most in-demand skill sets as cloud security and DevSecOps. Of course, these are not entry-level roles. But if someone has a background in Kubernetes and containers, he said, “having technical depth and soft skills — being able to communicate, and good relationships and rapport with developers and leaders” could make them good candidates.
Sedova spotted entry-level roles within a company that could make logical segues into cybersecurity work, like those who work in incident response, security operations center analysis, and junior project management roles.
Cyversity is a non-profit that offers courses and mentorship to bring more women and underrepresented minorities into cybersecurity. Sedova mentioned there are also a lot of cyber mentoring programs sponsored by banks and governments.
Any cybersecurity onboarding program needs to be grounded in psychological safety to counter imposter syndrome. Even very highly qualified security professionals, Sedova said, can have painful experiences that leave them feeling inadequate.
There are so few entry-level roles in the current cyber industry, which is all the more reason, she said, that companies need to provide coaching, being sure to say: “It’s OK to not know.”
Security Hiring Amplifies Tech’s Diversity Woes.
Michelle Lebesley, a security awareness lead who works as a consultant, argued that hiring managers shouldn’t be asking why cybersecurity professionals are hard to find, but rather flip it to: Why do you think people aren’t applying to your organization?
“If you’re looking for a good security engineer or a good security solutions architect, or my job, there are millions of us,” she said. “People self-select out because either they see the company doesn’t look welcoming or it’s all straight white people. Very few people will want to be the first Black person or disabled person at a company.”
“When you fail, it’s because ‘women can’t do cybersecurity’ or ‘Black people can’t do cybersecurity’ versus you’re new,” she said. “It’s a high-stakes game when you’re the only one in the room, which sucks.” So folks question if it’s even worth it: “Maybe I’ll go into a career that’s less high stakes and difficult to navigate.”
Like all things in tech, there’s a need for different voices to ask questions, which is how Lebesley described the crux of her day-to-day role in security awareness.
“You need the canaries in the coal mine,” she said. “ You need people from different backgrounds, a breadth of knowledge and life experience, but then they might not be considered,” in the typical cybersecurity job process.
Lebesley referred to loads of candidates who she described as “interested, motivated, whip-smart, incredibly great people, [but] their face doesn’t fit. Their name doesn’t sound right. It doesn’t sound like they will say yes. I honestly think it’s getting worse.”
“People self-select out because either they see the company doesn’t look welcoming or it’s all straight white people. Very few people will want to be the first Black person or disabled person at a company.”
—Michelle Lebesley, security awareness consultant
And with the tech layoffs, there’s a reasonable fear that there will be a backslide on the recent push for more diverse teams.
Cybersecurity hiring processes are notoriously gatekeeping, even for the tech industry. Every person interviewed for this piece cited a person’s network as the most common way to find a cybersecurity job — and building that network often favors people who have the time and money to attend conferences.
Similarly, as interviewing.io found, there’s a technical interview practice gap, where candidates from traditional backgrounds — and especially those from the top 20 American computer science programs — widely outperform those from non-traditional backgrounds, such as boot camp graduates or professionals who are self-taught.
Facing so many hurdles, Lebesley predicts those marginalized in cybersecurity will start to create their own companies and organizations.
She already sees this on Black-led social media platforms and predicted that safe spaces will continue to crop up as a solution to hostile work environments in 2023: “People just want to work in a safe environment for a company they believe in.”
Jennifer Riggins is a culture side of tech storyteller, journalist, writer, and event and podcast host, helping to share the stories where culture and technology collide and to translate the impact of the tech we are building. She has been…