
In 2022 by yourself, global cyberattacks elevated by 38{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1}, ensuing in considerable business enterprise reduction, such as economic and reputational problems. Meanwhile, company protection budgets have risen drastically simply because of the escalating sophistication of attacks and the number of cybersecurity methods introduced into the sector. With this rise in threats, budgets, and options, how prepared are industries and nations to effectively tackle present day cyber danger?
CYE’s new Cybersecurity Maturity Report 2023 tackles this issue by shedding mild on the power of cybersecurity in distinct sectors, organization sizes, and countries. It highlights which industries and international locations have the most robust cyber postures and which are lagging, as effectively as the most commonplace vulnerabilities in present-day cyber risk landscape.
The investigation is based mostly on two years’ well worth of details, collected from more than 500 organizations in 15 countries, and spanning 11 industries and a variety of enterprise measurements. It actions cybersecurity maturity throughout 7 unique protection domains, together with software degree security, community level security, identification administration and remote entry, and far more.
Listed here are the top findings:
Finding #1: Much larger Budgets You should not Automatically Signify Improved Cybersecurity
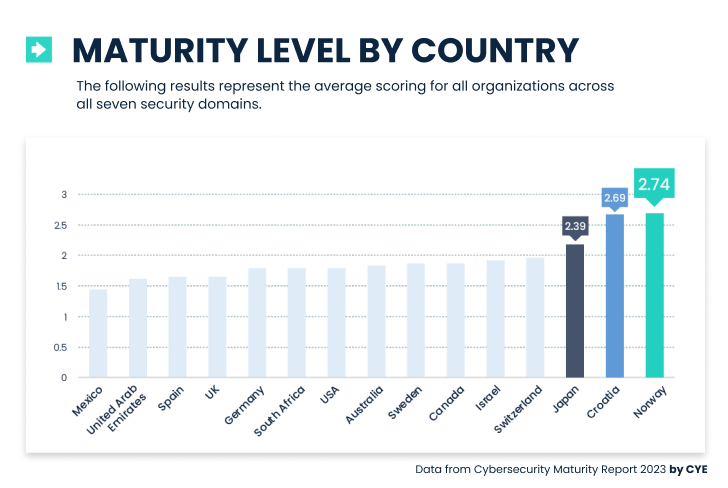
Among the nations, Norway scored the greatest on in general cybersecurity maturity level, adopted by Croatia and Japan. Whilst these international locations do not have the significant cybersecurity budgets of countries these kinds of as the US, United kingdom, and Germany, they do have state-of-the-art regulatory programs. Other feasible motives that Norway, Croatia, and Japan took the direct include early cybersecurity adoption in these countries and unified arranging by governments and companies. This obtaining illustrates how big economical investments do not necessarily translate into significant maturity amounts.
Acquiring #2: Tech Businesses Rating Typical
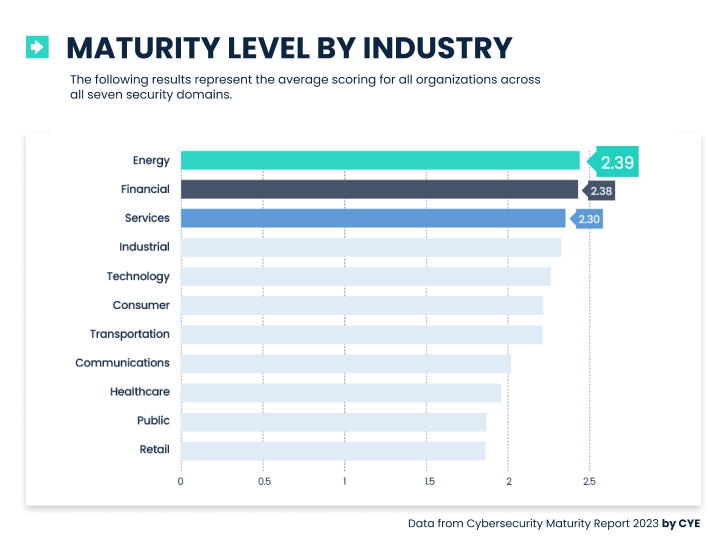
Amongst sectors, electrical power and economic industries arrived out on major for in general cybersecurity maturity amount, though healthcare, retail, and federal government businesses ended up among the the most affordable. Amazingly, the tech business scored about common, which is quite possibly simply because of the larger sized attack surface area this sort of businesses typically need to protect in comparison to other sectors.
The average rating could also be because tech companies are inclined to adopt new technologies that could be notably susceptible to assaults and exploits. In addition, tech companies are inclined to experience growth a lot a lot quicker than other sectors, which can be an added obstacle when striving to retain a solid cyber posture.
Finding #3: Modest and Medium Corporations Score Bigger Than Massive Companies
Incredibly, modest- and medium-sized companies experienced better cybersecurity maturity scores than organizations with about 10,000 staff members. This could be due to the fact little businesses may well have an easier time defending their tiny attack surfaces. With medium-sized organizations, investing in cybersecurity options is clearly a priority. When it will come to big businesses, however, obtaining to protect this sort of a huge attack surface area plainly has an result on the degree of cybersecurity maturity.
Getting #4: Approximately A single-Third of Businesses Deficiency Effective Password Guidelines
The research found that 32{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1} of companies had been identified to have weak password policies—a highly solvable problem that firms apparently have not sufficiently tackled. In addition, 23{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1} of corporations had been observed to have weak authentication mechanisms. This is regarding, mainly because the blend of the two challenges empowers hackers, who can then just log in with minimum effort.
Click listed here to download the complete report.
Recommendations for Improved Cybersecurity Maturity
The all round takeaway from the report is that most corporations are not adequately ready for the threat of cyberattacks. Having said that, companies can still accomplish a large cybersecurity maturity posture without having a substantial spending plan, if they strategy and expend effectively.
To secure themselves, companies should invest in abilities, relatively than applications complete extensive assessments to stop hackers from exploiting vulnerabilities and acquire an integrated tactic to cybersecurity with board-amount accountability. Cybersecurity optimization options this sort of as CYE can help by combining technological innovation, people today, and processes to deal with organizational cyber possibility and accomplish cyber threat quantification to understand threats and prioritize mitigation.
Program a demo to see how you can boost your cybersecurity maturity.
