3 Overlooked Cybersecurity Breaches

3 Overlooked Cybersecurity Breaches

In this article are three of the worst breaches, attacker techniques and tactics of 2022, and the security controls that can deliver effective, organization safety protection for them.

#1: 2 RaaS Attacks in 13 Months

Ransomware as a services is a type of assault in which the ransomware software package and infrastructure are leased out to the attackers. These ransomware providers can be acquired on the darkish world-wide-web from other threat actors and ransomware gangs. Frequent buying strategies include things like buying the overall tool, working with the current infrastructure although paying out for every infection, or permitting other attackers complete the provider even though sharing profits with them.

In this assault, the threat actor consists of a person of the most common ransomware teams, specializing in obtain through third get-togethers, though the focused corporation is a medium-sized retailer with dozens of web sites in the United States.

The menace actors made use of ransomware as a company to breach the victim’s network. They have been ready to exploit third-celebration credentials to achieve first access, development laterally, and ransom the enterprise, all in just mere minutes.

The swiftness of this assault was abnormal. In most RaaS conditions, attackers ordinarily keep in the networks for months and months before demanding ransom. What is specially fascinating about this attack is that the business was ransomed in minutes, with no need for discovery or weeks of lateral movement.

A log investigation revealed that the attackers targeted servers that did not exist in this technique. As it turns out, the sufferer was in the beginning breached and ransomed 13 months before this second ransomware attack. Subsequently, the initially attacker team monetized the first attack not only via the ransom they received, but also by offering the firm’s network facts to the 2nd ransomware group.

In the 13 months in between the two assaults, the sufferer altered its community and taken out servers, but the new attackers had been not informed of these architectural modifications. The scripts they formulated had been developed for the earlier community map. This also points out how they were being ready to attack so rapidly – they had a good deal of facts about the community. The primary lesson here is that ransomware assaults can be repeated by diverse groups, specially if the target pays well.

“RaaS assaults these kinds of as this a person are a very good example of how entire visibility enables for early alerting. A global, converged, cloud-native SASE platform that supports all edges, like Cato Networks provides comprehensive community visibility into community situations that are invisible to other vendors or may possibly go under the radar as benign occasions. And, remaining able to absolutely contextualize the occasions will allow for early detection and remediation.

#2: The Important Infrastructure Assault on Radiation Alert Networks

Attacks on significant infrastructure are turning into a lot more frequent and extra hazardous. Breaches of drinking water provide crops, sewage units and other these types of infrastructures could put hundreds of thousands of citizens at chance of a human crisis. These infrastructures are also turning into far more vulnerable, and attack surface area administration applications for OSINT like Shodan and Censys make it possible for security teams to discover such vulnerabilities with relieve.

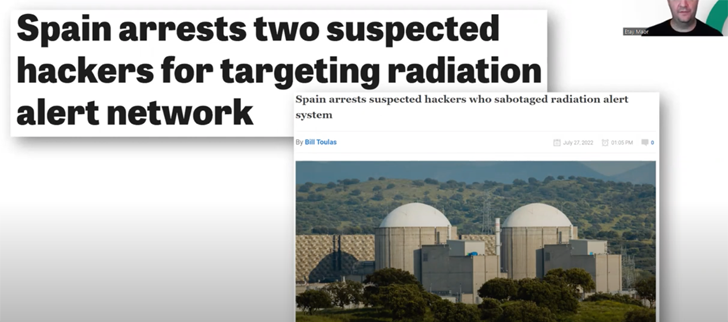
In 2021, two hackers ended up suspected of focusing on radiation notify networks. Their attack relied on two insiders that labored for a third social gathering. These insiders disabled the radiation warn programs, noticeably debilitating their capability to watch radiation assaults. The attackers ended up then capable to delete significant application and disable radiation gauges (which is part of the infrastructure by itself).
Cybersecurity Breaches

“Sadly, scanning for vulnerable units in essential infrastructure is less difficult than at any time. While several these types of corporations have a number of layers of stability, they are however using level alternatives to test and defend their infrastructure fairly than just one technique that can search holistically at the total assault lifecycle. Breaches are hardly ever just a phishing dilemma, or a credentials problem, or a vulnerable procedure trouble – they are generally a mix of various compromises executed by the menace actor,” reported Etay Maor, Sr. Director of Security Method at Cato Networks.

#3: The A few-Move Ransomware Attack That Started with Phishing

The 3rd assault is also a ransomware assault. This time, it consisted of a few methods:

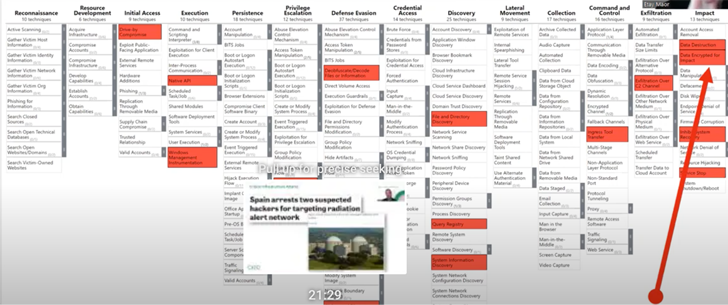
1. Infiltration – The attacker was able to achieve entry to the community by means of a phishing assault. The victim clicked on a hyperlink that generated a link to an exterior web page, which resulted in the obtain of the payload.

2. Community action – In the next section, the attacker progressed laterally in the community for two weeks. All through this time, it collected admin passwords and applied in-memory fileless malware. Then on New Year’s Eve, it carried out the encryption. This day was decided on considering that it was (rightfully) assumed the security crew would be off on holiday vacation.

3. Exfiltration – Eventually, the attackers uploaded the knowledge out of the community.

In addition to these three principal techniques, supplemental sub-approaches were utilized through the attack and the victim’s place stability methods were not equipped to block this assault.
Cybersecurity Breaches

“A many choke level strategy, 1 that appears horizontally (so to converse) at the assault rather than as a set of vertical, disjointed challenges, is the way to enhance detection, mitigation and avoidance of this kind of threats. Opposed to well-known perception, the attacker requires to be appropriate several situations and the defenders only need to have to be right just after. The underlying systems to employ a multiple choke position solution are whole network visibility by using a cloud-native backbone, and a solitary move stability stack that is based on ZTNA.” mentioned Etay Maor, Sr. Director of Protection Approach at Cato Networks.

How Do Safety Place Options Stack Up?

It is popular for security professionals to succumb to the “solitary point of failure fallacy”. Nonetheless, cyber-attacks are complex activities that rarely require just 1 tactic or method which is the bring about of the breach. Thus, an all-encompassing outlook is necessary to effectively mitigate cyber-attacks. Safety level remedies are a resolution for solitary factors of failure. These tools can detect pitfalls, but they will not join the dots, which could and has led to a breach.

This is Observe Out for in the Coming Months

According to ongoing safety analysis conducted by Cato Networks Security Staff, they have discovered two added vulnerabilities and exploit makes an attempt that they advocate which include in your upcoming safety designs:

1. Log4j

Though Log4j created its debut as early as December of 2021, the sounds its creating hasn’t died down. Log4j is still getting employed by attackers to exploit devices, as not all corporations have been ready to patch their Log4j vulnerabilities or detect Log4j assaults, in what is identified as “virtual patching”. They recommend prioritizing Log4j mitigation.

2. Misconfigured Firewalls and VPNs

Security methods like firewalls and VPNs have become access points for attackers. Patching them has turn into significantly tricky, specifically in the period of architecture cloudification and distant perform. It is suggested to shell out near interest to these parts as they are more and more vulnerable.

How to Lessen Your Assault Area and Acquire Visibility into the Community

To cut down the assault area, protection industry experts want visibility into their networks. Visibility relies on a few pillars:

  • Actionable info – that can be applied to mitigate assaults
  • Trusted data – that minimizes the amount of phony positives
  • Timely data – to make certain mitigation happens right before the attack has an influence

When an organization has complete visibility to the exercise on their network they can contextualize the info, choose whether or not the exercise witnessed should be allowed, denied, monitored, restricted (or any other motion) and then have the ability to enforce this conclusion. All these things have to be applied to each entity, be it a consumer, device, cloud application and so forth. All the time everywhere you go. That is what SASE is all about.
Found this article interesting? Observe us on Twitter and LinkedIn to browse extra exclusive material we publish.

Cybersecurity Budgets Are Going Up. So Why Aren’t Breaches Going Down?

Cybersecurity Budgets Are Going Up. So Why Aren’t Breaches Going Down?

Over the previous number of a long time, cybersecurity has develop into a major concern for enterprises about the world. With the whole cost of cybercrime in 2023 forecasted to arrive at $8 Trillion – with a T, not a B – it’s no ponder that cybersecurity is major of brain for leaders across all industries and areas.

On the other hand, irrespective of expanding attention and budgets for cybersecurity in current years, attacks have only develop into much more common and extra serious. When threat actors are turning into more and more subtle and arranged, this is just one piece to the puzzle in analyzing why cybercrime carries on to rise and what corporations can do to keep safe.

🔓 Unlock the upcoming of cybersecurity: Get forward of the sport with 2023 Cyber Safety Trends Forecast! Discover the significant traits of 2022 and understand how to guard your enterprise from rising threats in the coming yr. ⚡ Get your insider’s information to cybersecurity now!

An abundance of cyber paying out, a scarcity of cyber security

It’s straightforward to believe that the remedy to the cybersecurity challenge is money– to use far more stability specialists, to commit in a lot more equipment and technological know-how. If only it were that basic.

For a person point, expert cyber experts are in shorter provide. The (ISC)2 estimates that there are 3.4 Million unfilled cyber positions globally– a 26{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1} boost 12 months-on-year from 2020 to 2021. Additionally, nearly 70{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1} of cybersecurity workers “come to feel their group does not have adequate cybersecurity team to be productive.” So, even if an business has the price range to use a smaller military of cybersecurity specialists, they may not be in a position to find them.

In addition, info from the previous various years shows that businesses are investing extra and far more on cybersecurity just about every 12 months. Gartner predicts that world paying out on protection and possibility administration will develop by additional than 11{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1} in 2023, up to $188 Billion from just $158 Billion in 2021. This trend is envisioned to carry on, with globally cybersecurity paying out forecasted to climb 11{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1} each 12 months by way of 2026 to arrive at a full of $267.3 billion.

Even with these important increases in expending, and several organizations acquiring a myriad of commercial-off-the-shelf protection solutions– one study observed that the common organization has 76 protection systems deployed– breaches of company networks, programs, and info only proceed to turn out to be far more routine.

Breaches are turning into more frequent – and more expensive

It really is no secret that cybercrime is a significant challenge, but accurately how much of a issue is it? Some facts indicates that the amount of cyber attacks was 38{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1} better in 2022 than the past year. That arrives immediately after a described 50{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1} spike yr-on-year from 2020 to 2021.

Although not all of these attacks are focused or advanced, the sheer volume of attacks raises the chance that one assault will go undetected– and it only requires just one thriving attack for an business to experience really serious expenses and reputational destruction.

All far too typically, companies respond to cyber incidents only soon after the attack is at an highly developed stage, with incredibly several clues on how the breach transpired and what the menace actors may possibly be just after. This leaves safety teams scrambling to capture up, which slows down the reaction and recovery procedures.

Unfortunately, as the time it requires to return to enterprise as usual improves, so also does the charge of the incident. In accordance to the 2022 IBM Charge of a Information Breach report, it normally takes the regular business a staggering 277 days to entirely establish and include a breach. This provides the normal value of a info breach up to $4.35 Million – a determine large enough to pose an existential threat to several SMBs. Even for larger sized enterprises, this quantity of income is very little to scoff at.

A strategic change is wanted to give businesses the ability to anticipate threats, implement preventative procedures, and increase agility to detect and eliminate threats as rapidly as possible.

The journey to impactful intelligence

With out exception, each group with a digital presence will working experience cyber assaults. The most successful strategy is to establish and react to the attack as early as doable. The quicker a menace is detected and eradicated, the decrease the probability that the attack will be productive and outcome in damages to the group.

So the issue gets: how can companies lessen the sum of time it requires to detect and defeat a threat? The response: impactful intelligence that improves visibility on pitfalls and enables cyber agility in responding to and taking down threats.

In the Infosec environment, it really is usually claimed that menace intelligence ought to be “actionable.” This is legitimate, but it is just just one factor of what constitutes worthwhile intelligence. In present-day hostile menace landscape, intelligence will have to be impactful.

Impactful risk intelligence will have to have 4 properties:

  • Correct – the intelligence need to be true and correct
  • Applicable – the intelligence have to be pertinent to the group
  • Actionable – there ought to be steps the group can choose to defeat the menace
  • Charge Successful – the cost of the danger must be better than the charge of remediation

This new framework provides a will have to-desired change from looking at cybersecurity as strictly a complex dilemma, to a new frame of mind in which cybersecurity is considered as a business challenge that should be tackled in an efficient and value-effective manner. Menace intelligence can no for a longer period just be an expense– it must be a business-enabler that supplies measurable benefit to the organization.

Cyberint, a top danger intelligence vendor headquartered in Israel, is driving the evolution to impactful intelligence with the Argos Edge system. To learn far more about Cyberint’s new strategy to danger intelligence, test out this webinar on the Journey To Impactful Intelligence with Cyberint CEO Yochai Corem.

https://www.youtube.com/check out?v=vN_5YDEHiqw

There are always risks concerned when it arrives to cybersecurity, but impactful intelligence substantially minimizes the likelihood of a high priced breach and strengthens stability posture to the finest extent attainable. The time for impactful intelligence is on us.


Observed this posting interesting? Observe us on Twitter and LinkedIn to browse a lot more special content material we post.

LastPass hack: Cybersecurity experts sound the alarm over data breaches

LastPass hack: Cybersecurity experts sound the alarm over data breaches

Cybersecurity authorities are expressing worry in excess of the most current data breach suffered by password supervisor LastPass, as the cloud safety firm remains mum in the deal with of a course-motion lawsuit joined to numerous hacks on the organization past year.

LastPass initial alerted buyers in August 2022 that “an unauthorized bash obtained accessibility to parts” of its network by a developer’s compromised account, and determined at the time that no consumer info or encrypted password vaults were being accessed by the hacker.

LastPass logo phone

Cybersecurity experts are sounding the alarm above the prolong of safety breaches suffered by password supervisor LastPass. (Photo Illustration by Mateusz Slodkowski/SOPA Photos/LightRocket by way of Getty Photos / Getty Photos)

The enterprise then admitted a 2nd breach in late November, declaring another person utilized info accessed in the August hack to “attain entry to sure components of our customers’ information.” LastPass insisted users’ passwords remained safely and securely encrypted at that time.

But In the firm’s most recent weblog update on Dec. 22 regarding the safety incidents, LastPass CEO Karim Toubba acknowledged that a “danger actor” experienced copied a backup of shopper vault knowledge that integrated “fully-encrypted sensitive fields such as web page usernames and passwords, secure notes, and kind-milled data.” That has authorities sounding the alarm.

CHATGPT Being Used TO Write MALWARE, RANSOMWARE: Stories

Yiddy Lemmer, who owns IT support and cybersecurity company CompuConnect primarily based out of New York, advised FOX Business he continue to suggests men and women use password administrators to hold their details secure — but he no lengthier recommends LastPass. In reality, he stop employing LastPass himself a handful of weeks back just after identifying the extent of the breach.

internet hacker computer

A hacker was capable to access LastPass customer details in numerous stability breaches final 12 months. (Jakub Porzycki/NurPhoto by using Getty Visuals / Getty Illustrations or photos)

“When I learned the depths of how bad it was, I switched appropriate away,” Lemmer mentioned. “I am not heading to wait around all over for the next hack until it receives even worse.” Lemmer now makes use of LastPass rival Bitwarden to deal with his passwords.

Nashville, Tennessee-based mostly cybersecurity agency Galactic Advisors sent out a warning to buyers above the LastPass hack on Jan. 3, saying it experienced “gained data indicating that some of the unencrypted information” uncovered in the attack “could be made use of for extra than phishing.”

CHICK-FIL-A URGES Buyers TO Acquire Action, INVESTIGATES ‘FRAUDULENT ACTIVITY’ ON Mobile Application ACCOUNTS

The similar week, LastPass was strike with a course-action lawsuit from a former shopper who claims the hack resulted in someone accessing the non-public keys he had stored on LastPass to steal around $53,000 really worth of bitcoin.

LastPass hack

Password manager LastPass experienced multiple details breaches in 2022. (Image by Leon Neal/Getty Visuals / Getty Pictures)

LastPass CEO Toubba has not provided an update on the protection incidents on the company’s blog site given that Dec. 22, and the firm has not still responded to several requests for remark from FOX Enterprise.

Russ Reeder, CEO of cybersecurity company Netrix Global, claims it is essential for companies to offer obvious communications to both equally tell clientele and protect those people impacted by info breaches early on.

GET FOX Enterprise ON THE GO BY CLICKING Listed here

He extra, “It is terrifying when a password keeper enterprise we have all been educated to count on will get breached.”

LogMeIn declared in Dec. 2021 that it was spinning off LastPass as a standalone company. At the time, LastPass experienced 30 million end users and served a lot more than 85,000 companies.