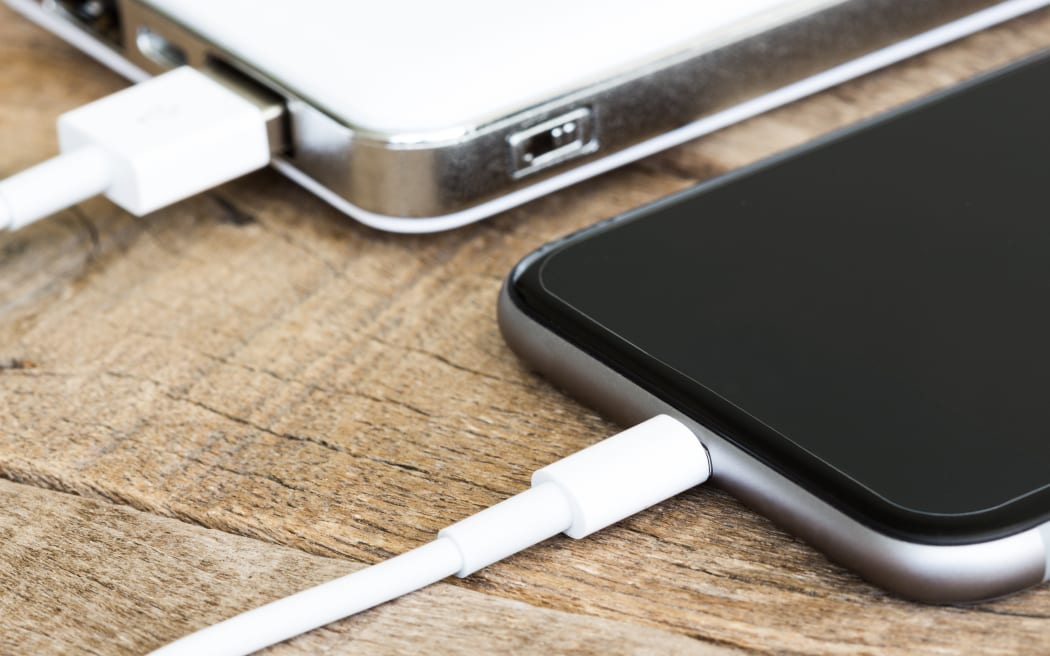
The potential risks of plugging gadgets into open up charging ports have been recognized for some time, but general public consciousness may well stay restricted. Image: 123rf
A cyber stability qualified says he is amazed by how several persons in New Zealand keep on being unaware of potential risks posed by plugging telephones into USB chargers in community spaces.
Public charging stations are conveniently dotted around the outlets, airports and inns throughout the country.
Nevertheless, a new tweet by the the Federal Bureau of Details (FBI) warning the US community to prevent utilizing these because of to the risk of hacking. It has also served to remind New Zealanders of the hazards of utilizing community charging ports.
The FBI claimed “poor actors” experienced located ways to use these to introduce malware and monitoring application on to equipment.
Cyber security company Cert NZ has echoed the warnings. Menace and incident reaction team supervisor Jordan Heerspring told Checkpoint men and women ought to not to plug telephones and laptops instantly into people public USB charging ports.
“You really should be bringing your personal charging product, which you can plug into a wall socket, and then use that to charge your units,” he explained.
“In the airports you can expect to see community charging stations, some motels will have them even in the rooms. Some buses if they are pleasant extravagant buses, and even some planes will have them. So all of them are most secure to prevent, if you can.”
Heerspring explained it was not a significantly nicely-publicised piece of assistance, even if prolonged-standing.
“If I am remaining entirely trustworthy, I thought this was pretty community understanding. But talking to mates and spouse and children lately, I have found out that there are a whole lot of people who are not mindful of this. I am pretty happy that there is been some dialogue going all-around and raising that recognition for individuals.”
He suspected the FBI warning mirrored an maximize in cyber attacks involving charging ports in the US.
Even so, the fact was most ports had been in all probability good to use in New Zealand, Heerspring reported.
“We will not see a large amount of these attacks, but they’re genuinely simple points to retain you protected from, our advices is it is really ideal to stay clear of them.”
Hackers have devised ways to infiltrate the bits of application and components guiding the charging stations, so that an attacker can likely these use to load possibly destructive program onto equipment, or they can use that to extract details straight from units, he claimed.
“With the two of all those strategies, they’re going to be ready to extract own or other delicate or fiscal data from your machine if they are exploiting that distinct charging station.”
Cyber prison could accessibility the information and facts remotely, or may well have to return to the charging port, relying on the malware utilised, he claimed.
“It truly is type of like creating a street to the enemy camp. You can nonetheless have your gates up, so you will find continue to some safety measures that they will have to bypass, but giving them their accessibility invites them to do that.”
Being aware of your phone has been compromised is at times tricky, but there are some symptoms to look out for.
“There’s a handful of items that are truly worth wanting further into, like if your cellular phone is working very little by little, noticeably a lot more so than standard. Or if you get diverse apps or windows popping up that you really don’t assume or have not informed the product to do. Which is well worth getting investigated,” he claimed.
One more piece of essential suggestions was in no way plug a USB unit into your cell phone or laptop if you did not know its resource.
“If you obtain a USB unit, a tiny USB vital or get presented one – specifically if you will not absolutely believe in that human being – you shouldn’t be placing that into your own laptops or phones or other devices at household,” he explained.
“Additional generically, hold two-variable authentication on your accounts and have excellent password hygiene and those people a few items, along with retaining your gadgets updated, so patching to the most recent versions, will maintain you safeguarded from the bulk of the attacks out there.”
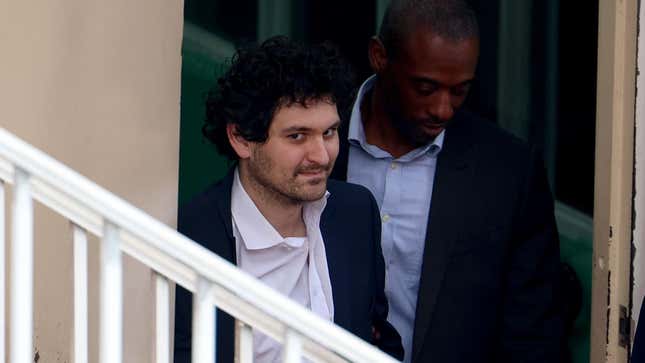
FTX, the once beloved crypto exchange that went down in a ball of financially flames last November, appears to have spent very little effort protecting its customers’ vast reserves of digital assets. The company’s latest bankruptcy report reveals that, in addition to managing its finances like a Jim-Beam-swigging monkey, the disgraced crypto exchange also had some of the worst cybersecurity practices imaginable.
Of course, we’ve known that FTX sucked at cyber since at least last November when, less than 24 hours after the company declared Chapter 11 bankruptcy and its former CEO, Sam Bankman-Fried, aka SBF stepped down, the company suffered a massive digital robbery. The robber, whoever they were, made off with $432 million in assets, a bundle of digital cash that is still unaccounted for—just like a whole lot more of FTX customers’ money.
At the time, the hacking incident seemed like just more bad news on top of an already epic shit sundae, but now we have a little more context for the episode. Monday’s report, which extensively reviews the company’s failure to put basic digital protections in place, is a comic masterpiece that will make you wonder how the company didn’t get hacked earlier.
G/O Media may get a commission
Save $400
2021 14″ 1TB MacBook Pro
MacBook Pro’s are the way to go Up to 10-core CPU delivers up to 3.7x faster performance to fly through pro workflows quicker than ever. Up to 32-core GPU with up to 13x faster performance for graphics-intensive apps and games
“The FTX Group failed to implement basic, widely accepted security controls to protect crypto assets. Each failure was egregious in the context of a business entrusted with customer transactions,” the filing states. Here are some of the takeaways about those failures.
FTX Didn’t Have a Cybersecurity Staff
Despite being a company tasked with protecting tens of billions of dollars in crypto assets, FTX had no dedicated cybersecurity staff, according to Monday’s filing. None. The company never bothered to hire a CISO (a chief information security officer) to manage the company’s risks for them. Instead, they relied on two of the company’s software developers who, the report notes, did not have formal training in security and whose jobs put them at odds with prioritizing security. The report states:
The FTX Group had no independent Chief Information Security Officer, no employee with appropriate training or experience tasked with fulfilling the responsibilities of such a role, and no established processes for assessing cyber risk, implementing security controls, or responding to cyber incidents in real time…as with critical controls in other areas, the FTX Group grossly deprioritized and ignored cybersecurity controls, a remarkable fact given that, in essence, the FTX Group’s entire business—its assets, infrastructure, and intellectual property—consisted of computer code and technology.
Granted, lots of tech companies suffer from staffing shortages when it comes to cybersecurity but that’s really only excusable if you’re a unicorn or a startup and don’t have the manpower or capital to hire competent people. In the days before its implosion, FTX was reported to be worth as much as $32 billion. Suffice it to say, I think they could’ve hired a guy.
FTX Pretty Much Never Used Cold Storage, the Industry Standard
Another really dumb thing that FTX did was fail to keep its users’ crypto assets in cold storage—a standard security practice that most crypto exchanges claim to abide by.
In general, crypto assets can be stored in two separate ways: “hot wallets,” which are software-based accounts connected to the internet; and “cold storage,” which is an offline, hardware-based form of storage. Cold storage is considered secure, while “hot wallets” are riskier, because—being linked to the web—they can (and often do) get hacked.
Common wisdom suggests that companies keep just as much crypto in hot wallets as necessary to keep accounts liquid, while the rest of the crypto should be kept in cold storage. However, FTX didn’t do that; instead, the report says it kept “virtually all” of its customers’ assets in hot wallets.
Did FTX not know that cold storage was more secure or something? Nope, worse than being too stupid to implement proper controls, the exchange’s leadership appears to have just not given much of a shit.
“The FTX Group undoubtedly recognized how a prudent crypto exchange should operate, because when asked by third parties to describe the extent to which it used cold storage, it lied,” the report states, listing off a number of examples in which FTX executives—including SBF—claimed that they kept users’ assets in cold storage. In one instance, the company told investors that, in keeping with industry best practices, it kept a small amount of crypto in hot wallets, while the rest was “stored offline in air gapped encrypted laptops, which are geographically distributed.” But this was, according to the report, just bullshit.
Instead, as the report notes, “the FTX Group made little use of cold storage” except in Japan, “where [it was] required by regulation to use” it.
Private Cryptographic Keys Were Left Unencrypted
Another totally idiotic thing that the FTX peeps did is keep clients’ sensitive cryptographic keys and seed phrases stored in plaintext documents that were apparently accessible by staff.
In crypto, the key or seed phrase is the password that gets you inside a user’s individual wallet. Suffice it to say, industry standards compel crypto exchanges to keep that information encrypted and, thus, safe from prying eyes. Not so, with FTX—which apparently kept keys that could open wallets worth tens of millions of dollars unencrypted, in plaintext, just lying around in AWS.
According to the report, this was part and parcel of a generally disorganized approach to security, in which “private keys and seed phrases used by FTX.com, FTX.US, and Alameda were stored in various locations throughout the FTX Group’s computing environment in a disorganized fashion, using a variety of insecure methods and without any uniform or documented procedure.”
The FTX Gang Didn’t Really Use Multi-Factor Authentication
SBF and his merry band of hipsters also apparently “failed to effectively enforce the use” of multi-factor authentication (MFA)—a very basic form of web security that pretty much everybody who works in an office knows about. The recently released report states that the crypto exchange’s leadership “failed to implement in an appropriate fashion even the most widely accepted controls relating to Identity and Access Management (“IAM”).” This included a failure to use MFA as well as single-sign on services—also widely considered to be an industry best practice.
And much, much more!
There are a lot of other hilarious jewels of security negligence that FTX appears to have committed, so I’d suggest reading the full report if you want your jaw to drop to the floor.
TikTok is a “possible danger vector” to the United States, reported John F. Plumb, assistant secretary of protection for place coverage and principal cyber advisor to the secretary of protection.
TikTok is a social media, video clip-web hosting company owned by the Chinese business ByteDance.
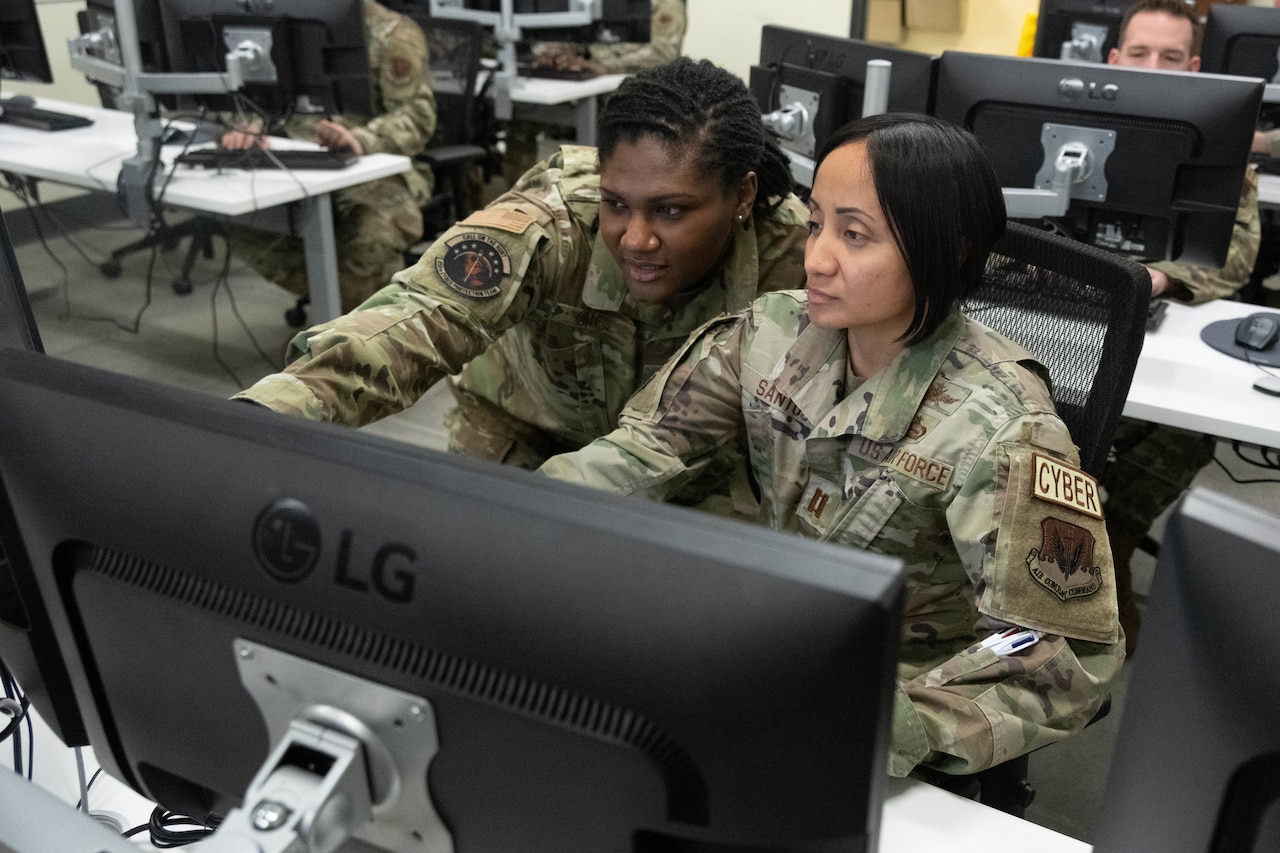
Users of the Property Armed Expert services Committee’s subcommittee on cyber, data technologies and innovation heard testimony from Plumb and Army Gen. Paul M. Nakasone, commander of U.S. Cyber Command, director of the Countrywide Security Company and chief of the Central Safety Provider.
The dilemma with TikTok is that a massive selection of People use it, and China might have the ability to immediate misinformation through it, as effectively as gather knowledge from it, stated Plumb. The scale and scope of the platform is problematic.
Policy makers need to have to be aware of these threats, be capable to quantify them, and be equipped to choose motion versus them, he mentioned.
Nakasone mentioned, “If you consider one particular-3rd of the grownup populace gets their news from this application, a person-sixth of our little ones are indicating they are consistently on this app, if you take into consideration that there is certainly 150 million persons each solitary day that are clearly touching this application, this offers a international nation a system for information and facts operations, a system for surveillance, and a problem we have with regards to who controls that details.”
The division has by now prohibited the use of TikTok on govt phones, the basic mentioned.
“I imagine the broader discussion clearly rests with the policymakers now. Surely, this is a piece that our country has to consider,” he explained.
There are likely to be other programs like this, and there needs to be a coverage in spot that balances the capacity to share facts with protection from adversaries’ means to conduct surveillance and details functions from the United States, Nakasone explained.
The general said you can find a distinction involving TikTok and American-primarily based social media platforms.
China has now said they’re heading to “touch the info at any time they want to touch this info. This considerations me,” Nakasone said.
Plumb reported that for decades, China has made use of its cyber capabilities to steal delicate details, mental home and exploration from U.S. public- and non-public-sector establishments, together with the protection industrial foundation.
“Chinese cyber intrusions are the most prolific in the planet. In disaster, PRC [China’s] leaders think that accomplishing data dominance will empower them to seize and hold the strategic initiative, disrupt our potential to mobilize, to project and sustain the joint power, and to guarantee the PRC’s wished-for close point out,” Plumb stated, referring to China.
Plumb also testified that Russia engages in persistent, malicious cyber activities to help its world espionage strategies, steal mental home, disrupt essential infrastructure and promote disinformation.
Russia has also shown that it utilizes cyber as a key ingredient of its wartime system, notably from Ukraine, he reported.
Other persistent cyber threats come up from North Korea, Iran and transnational prison corporations, Plumb mentioned.
“Alongside one another, our adversaries use cyberspace to carry out functions against the Section of Defense Info Community and the U.S. homeland. They do this to weaken our allies and partners and to undermine U.S. passions,” Plumb reported.
Plumb described steps the division has taken in both equally defensive and offensive cyberspace. He mentioned the president’s fiscal year 2024 finances request bundled $13.5 billion for cyberspace things to do, prioritizing investments in cyberspace workforce, operations, investigation and capabilities.
“Operating in cyberspace today is an vital element of the department’s capability to prevent aggression and make sure our nation’s security,” he mentioned.
It is one of China’s most popular shopping apps, selling clothing, groceries and just about everything else under the sun to more than 750 million users a month.
But according to cybersecurity researchers, it can also bypass users’ cell phone security to monitor activities on other apps, check notifications, read private messages and change settings.
And once installed, it’s tough to remove.
While many apps collect vast troves of user data, sometimes without explicit consent, experts say e-commerce giant Pinduoduohas taken violations of privacy and data security to the next level.
In a detailed investigation, CNN spoke to half a dozen cybersecurity teams from Asia, Europe and the United States — as well as multiple former and current Pinduoduo employees — after receiving a tipoff.
Multiple experts identified the presence of malware on the Pinduoduo app that exploited vulnerabilities in Android operating systems. Company insiders said the exploits were utilized to spy on users and competitors, allegedly to boost sales.
“We haven’t seen a mainstream app like this trying to escalate their privileges to gain access to things that they’re not supposed to gain access to,” said Mikko Hyppönen, chief research officer at WithSecure, a Finnish cybersecurity firm.
“This is highly unusual, and it is pretty damning for Pinduoduo.”
Malware, short for malicious software, refers to any software developed to steal data or interfere with computer systems and mobile devices.
Evidence of sophisticated malware in the Pinduoduo app comes amid intense scrutiny of Chinese-developed apps like TikTok over concerns about data security.
Some American lawmakers are pushing for a national ban on the popular short-video app, whose CEO Shou Chew was grilled by Congress for five hours last week about its relations with the Chinese government.
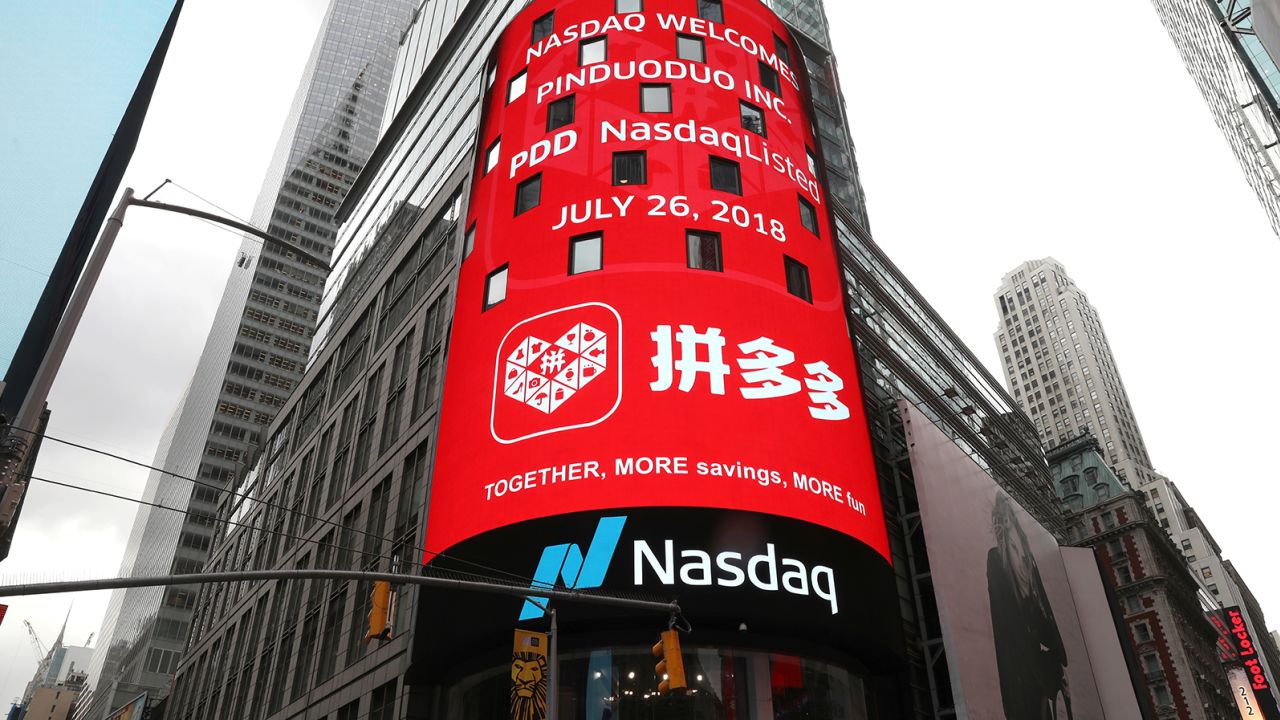
The revelations are also likely to draw more attention to Pinduoduo’s international sister app, Temu, which is topping US download charts and fast expanding in other Western markets. Both are owned by Nasdaq-listed PDD, a multinational company with roots in China.
While Temu has not been implicated, Pinduoduo’s alleged actions risk casting a shadow over its sister app’s global expansion.
There is no evidence that Pinduoduo has handed data to the Chinese government. But as Beijing enjoys significant leverage over businesses under its jurisdiction, there are concerns from US lawmakers that any company operating in China could be forced to cooperate with a broad range of security activities.
The findings follow Google’s suspension of Pinduoduo from its Play Store in March, citing malware identified in versions of the app.
An ensuing report from Bloomberg said a Russian cybersecurity firm had also identified potential malware in the app.
Pinduoduo has previously rejected “the speculation and accusation that Pinduoduo app is malicious.”
CNN has contacted PDD multiple times over email and phone for comment, but has not received a response.
Pinduoduo, which boasts a user base that accounts for three quarters of China’s online population anda market value three times that of eBay
(EBAY), wasn’t always an online shopping behemoth.
Founded in 2015 in Shanghai by Colin Huang, a former Google employee, the startup was fighting to establish itself in a market long dominated by e-commerce stalwarts Alibaba
(BABA) and JD.com
(JD).
It succeeded by offering steep discounts on friends-and-family group buying orders and focusing on lower-income rural areas.
Pinduoduo posted triple digit growth in monthly users until the end of 2018, the year it listed in New York. By the middle of 2020, though, the increase in monthly users had slowed to around 50{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1} and would continue to decline, according to its earnings reports.
It was in 2020, according to a current Pinduoduo employee, that the company set up a team of about 100 engineers and product managers to dig for vulnerabilities in Android phones, develop ways to exploit them — and turn that into profit.
According to the source, who requested anonymity for fear of reprisals, the company only targeted users in rural areas and smaller towns initially, while avoiding users in megacities such as Beijing and Shanghai.
“The goal was to reduce the risk of being exposed,” they said.
By collecting expansive data on user activities, the company was able to create a comprehensive portrait of users’ habits, interests and preferences, according to the source.
This allowed it to improve its machine learning model to offer more personalized push notifications and ads, attracting users to open the app and place orders, they said.
The team was disbanded in early March, the source added, after questions about their activities came to light.
PDD didn’t reply to CNN’s repeated requests for comment on the team.
Approached by CNN, researchers from Tel Aviv-based cyber firm Check Point Research, Delaware-based app security startup Oversecured and Hyppönen’s WithSecure conducted independent analysis of the 6.49.0 version of the app, released on Chinese app stores in late February.
Google Play is not available in China, and Android users in the country download their apps from local stores. In March, when Google suspended Pinduoduo, it said it had found malware in off-Play versions of the app.
The researchers found code designed to achieve “privilege escalation”: a type of cyberattack that exploits a vulnerable operating system to gain a higher level of access to data than it’s supposed to have, according to experts.
“Our team has reverse engineered that code and we can confirm that it tries to escalate rights, tries to gain access to things normal apps wouldn’t be able to do on Android phones,” said Hyppönen.
The app was able to continue running in the background and prevent itself from being uninstalled, which allowed it to boost its monthly active user rates, Hyppönen said. It also had the ability to spy on competitors by tracking activity on other shopping apps and getting information from them, he added.
Check Point Research additionally identified ways in which the app was able to evade scrutiny.
The app deployed a method that allowed it to push updates without an app store review process meant to detect malicious applications, the researchers said.
They also identified in some plug-ins the intent to obscure potentially malicious components by hiding them under legitimate file names, such as Google’s.
“Such a technique is widely used by malware developers that inject malicious code into applications that have legitimate functionality,” they said.
In China, about three quarters of smartphone users are on the Android system. Apple
(AAPL)’s iPhone has 25{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1} market share, according to Daniel Ives of Wedbush Securities.
Sergey Toshin, the founder of Oversecured, said Pinduoduo’s malware specifically targeted different Android-based operating systems, including those used by Samsung, Huawei, Xiaomi and Oppo.
CNN has reached out to these companies for comment.
Toshin described Pinduoduo as “the most dangerous malware” ever found among mainstream apps.
“I’ve never seen anything like this before. It’s like, super expansive,” he said.
Most phone manufacturers globally customize the core Android software, the Android Open Source Project (AOSP), to add unique features and applications to their own devices.
Toshin found Pinduoduo to have exploited about 50 Android system vulnerabilities. Most of the exploits were tailor made for customized parts known as the original equipment manufacturer (OEM) code, which tends to be audited less often than AOSP and is therefore more prone to vulnerabilities, he said.
Pinduoduo also exploited a number of AOSP vulnerabilities, including one which was flagged by Toshin to Google in February 2022. Google fixed the bug this March, he said.
According to Toshin, the exploits allowed Pinduoduo access to users’ locations, contacts, calendars, notifications and photo albums without their consent. They were also able to change system settings and access users’ social network accounts and chats, he said.
Of the six teams CNN spoke to for this story, three did not conduct full examinations. But their primary reviews showed that Pinduoduo asked for a large number of permissions beyond the normal functions of a shopping app.
They included “potentially invasive permissions” such as “set wallpaper” and “download without notification,” said René Mayrhofer, head of the Institute of Networks and Security at the Johannes Kepler University Linz in Austria.
Suspicions about malware in Pinduoduo’s app were first raised in late February in a report by a Chinese cybersecurity firm called Dark Navy. Even though the analysis didn’t directly name the shopping giant, the report spread quickly among other researchers, who did name the company. Some of the analysts followed up with their own reports confirming the original findings.
Soon after, on March 5, Pinduoduo issued a new update of its app, version 6.50.0, which removed the exploits, according to two experts who CNN spoke to.
Two days after the update, Pinduoduo disbanded the team of engineers and product managers who had developed the exploits, according to the Pinduoduo source.
The next day, team members found themselves locked out of Pinduoduo’s bespoke workplace communication app, Knock, and lost access to files on the company’s internal network. Engineers also found their access to big data, data sheets and the log system revoked, the source said.
Most of the team were transferred to work at Temu. They were assigned to different departments at the subsidiary, with some working on marketing or developing push notifications, according to the source.
A core group of about 20 cybersecurity engineers who specialize in finding and exploiting vulnerabilities remain at Pinduoduo, they said.
Toshin of Oversecured, who looked into the update, said although the exploits were removed, the underlying code was still there and could be reactivated to carry out attacks.
Pinduoduo has been able to grow its user base against a backdrop of the Chinese government’s regulatory clampdown on Big Tech that began in late 2020.
That year, the Ministry of Industry and Information Technology launched a sweeping crackdown on apps that illegally collect and use personal data.
In 2021, Beijing passed its first comprehensive data privacy legislation.
The Personal Information Protection Law stipulates that no party should illegally collect, process or transmit personal information. They’re also banned from exploiting internet-related security vulnerabilities or engaging in actions that endanger cybersecurity.
Pinduoduo’s apparent malware would be a violation of those laws, tech policy experts say, and should have been detected by the regulator.
“This would be embarrassing for the Ministry of Industry and Information Technology, because this is their job,” said Kendra Schaefer, a tech policy expert at Trivium China, a consultancy. “They’re supposed to check Pinduoduo, and the fact that they didn’t find (anything) is embarrassing for the regulator.”
The ministry has regularly published lists to name and shame apps found to have undermined user privacy or other rights. It also publishes a separate list of apps that are removed from app stores for failing to comply with regulations.
Pinduoduo did not appear on any of the lists.
CNN has reached out to the Ministry of Industry and Information Technology and the Cyberspace Administration of China for comment.
On Chinese social media, some cybersecurity experts questioned why regulators haven’t taken any action.
“Probably none of our regulators can understand coding and programming, nor do they understand technology. You can’t even understand the malicious code when it’s shoved right in front of your face,” a cybersecurity expert with 1.8 million followers wrote last week in a viral post on Weibo, a Twitter-like platform.
Time to rely on: Concerns cybersecurity consumers talk to and how to response them
4 means cybersecurity startups can strengthen adoption and shorten time to value
Creating solutions and firms in cybersecurity is not an effortless undertaking mainly because in many methods, the sector behaves otherwise from other folks. To start, it is extremely crowded, with hundreds and countless numbers of undifferentiated alternatives promising to address all stability troubles and much more typically than not, falling quick of their promises. Additionally, it is an unbelievably dynamic place with the landscape often shifting right away.
As a solution leader, I fulfill several business people and startup founders and see above and around how the large vast majority get slowed down by the identical styles of issues. In this put up, I am hunting at six problems of developing items in cybersecurity and ways to prevail over them.
1. The challenge of buyer discovery
As a product or service leader, I fulfill many business owners and startup founders and see over and in excess of how the vast vast majority get slowed down by the very same varieties of issues.
In most industries, buyers and finish buyers are open up to chatting to vendors because they identify that software suppliers are there to establish their issues, soreness details and inefficiencies, and make methods that clear away them. The exact same, unfortunately, are unable to be mentioned about cybersecurity where by handful of leaders (Chief Info Safety Officers or CISOs) or practitioners are open to acquiring transparent conversations with strangers. There are various factors why this is the situation:
Protection groups are chronically overextended and understaffed, and as a result cannot prioritize talking to sellers more than enhancing the safety posture of their organization.
CISOs and practitioners alike are inundated by suppliers who achieve out from all fronts — phone calls, e-mail, social media messages and conferences, to identify a handful of.
Product administrators and founders are likely to request the very same forms of inquiries that an adversary would (what goods the enterprise is applying, wherever their gaps are, and so forth.) — questions that can only be answered if there is a amount of have confidence in amongst events.
All this makes the life of cybersecurity solution leaders exceptionally tricky as it fundamentally makes them unable to do customer discovery, discover about suffering details and brainstorm possible methods. Listed here are some of the means to deal with this:
Construct relationships with CISOs and security practitioners by attending occasions, workshops and webinars.
Check with current customers, VCs and design and style companions for introductions to people today in their community.
When PMs get an prospect to chat to stability men and women, use that time to check with issues and be curious, as an alternative of pitching their products and solutions and options.
2. Working with standard merchandise administration frameworks
For the initially three months of the year, we’ve been pursuing new merchandise launches and updates in cloud stability, XDR, SASE and extra.


New Solutions To Know
An array of new cybersecurity product or service releases during the initially quarter built for a chaotic get started to 2023 in the security field. Cybersecurity companies that introduced key new solutions and function updates all through the initial three months of the yr provided suppliers this kind of as CrowdStrike, Zscaler, Palo Alto Networks, Sophos and Microsoft.
Major themes of the cybersecurity item launches in Q1 integrated the use of AI and ML for increasing cyberdefense, like the use of generative AI in a few circumstances. Important item segments that we tracked in the very first quarter integrated cloud stability, concentrated on defense of cloud environments such as AWS, Microsoft Azure and Google Cloud protected access service edge (SASE) and zero have confidence in network accessibility (ZTNA) for shielding hybrid and remote workforce entry to apps and prolonged detection and reaction (XDR) for correlating protection facts across instruments and prioritizing threats.
[Related:
10 Cybersecurity Companies Making Moves: March 2023]
As Q1 of 2023 arrived to a shut, specifics about what could be a single of the greatest cyberattacks in latest memory arrived to mild, as scientists from protection vendors including CrowdStrike and SentinelOne disclosed that communications app maker 3CX — as well as an untold variety of its finish consumers — had grow to be the target of a application provide chain attack reminiscent of the extensively felt SolarWinds breach of 2020. The attack underscored the have to have for cybersecurity goods that can pinpoint legitimate attacks amid the numerous alerts generated by today’s threat detection tools, as properly as the great importance of safeguarding the software growth system.
What follows are the critical specifics on 15 new cybersecurity merchandise to know from Q1 of 2023.
Kyle Alspach
Kyle Alspach is a Senior Editor at CRN focused on cybersecurity. His protection spans information, evaluation and deep dives on the cybersecurity industry, with a concentrate on quickly-increasing segments such as cloud protection, application stability and identification security. He can be achieved at kalspach@thechannelcompany.com.