Recession hits cybersecurity companies hard as layoffs mount

Recession hits cybersecurity companies hard as layoffs mount

The cybersecurity business is not immune. This concept has been internalized over the earlier week in the technologies sector. It began with U.S. firm CrowdStrike, which is regarded one particular of the most significant gamers in the market. The company exposed excellent benefits in its financial studies for the third quarter, but the CEO admitted that customers are chopping expenditures and suspending buys.

On Wednesday, Israel’s SentinelOne, CrowdStrike’s sworn rival, released its economic reports that repeated the identical warning – now the quantities are very good, but it is tricky to dismiss the emerging weak spot in the corporate marketplace.

1 Watch gallery

כנס INTENT לחוקרי סייברכנס INTENT לחוקרי סייבר

Cybersecurity meeting.

(Tomer Foltyn Pictures)

“The macroeconomic things are manifested in a slower closing of discounts, especially of significant transactions,” Tomer Weingarten, founder and CEO of SentinelOne, reported yesterday immediately after the publication of the stories. “Shoppers are additional centered only on the most important and immediate security wants and reject the give in other regions”.

Nir Zuk’s Palo Alto Networks, the world’s most significant cyber organization in terms of market place capitalization, also posted superior benefits at the stop of November, but its managers also mentioned that the cyber marketplace, which is perceived as more resistant to the winds of economic downturn, is commencing to exhibit indicators of slowing down.

The words of the CEO of CrowdStrike sent its inventory to a sharp drop of 19{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1} in a single day previous week, which also mirrored on the stock of SentinelOne, which has misplaced about 10{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1} due to the fact then. Shares of Zscaler and Okta, other American cyber stars, also endured declines and even Palo Alto fell from its Mount Olympus and the record value it was traded at. SentinelOne has a market place cap of all-around $4 billion moving into Thursday, a lot less than 50 {b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1} of the value at which it was issued past year – thanks to which it now has $1.2 billion in hard cash.

And when businesses like CrowdStrike, Palo Alto or SentinelOne confess that the cyber industry is not immune, it is effortless to recognize why really a couple of startups in the subject have announced layoffs in the final week. Aqua Security, a cyber unicorn, parted approaches with just over 60 staff who make up 10{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1} of the workforce. A different unicorn, Perimeter 81, laid off 8{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1} of its workforce and Cognyte, which previously split from Verint, laid off 100 workers. Final thirty day period, Snyk also manufactured a deep go of laying off 200 workers, and at the exact same time Cybereason, Imperva and Checkmarx also parted strategies with personnel.

In the meantime, the public companies have prevented layoffs, with the exception of the Israeli Varonis, which laid off 110 workers – 5{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1} of the workforce. Nonetheless, Weingarten mentioned yesterday with the publication of the reports that SentinelOne has halted choosing and is generally investing in the teaching of the a lot of advertising and profits staff it recruited previous year.

In the meantime, it is still shedding income, and a whole lot, but revenues have doubled as opposed to the corresponding quarter to $115 million. The immediate advancement nevertheless does not include the expenditures that are increasing at the similar level, so the bottom line is that the organization recorded a decline of $98 million. The forecast for the current quarter, while the company improved it a bit, implies a slowdown in the progress fee. Quarterly revenues ought to achieve $125 million, so that SentinelOne will finish the total 12 months with a turnover of $420 million.

So what is precisely going on in the cyber industry? Up till now, the typical notion was that cyber is the past price to be cut, and this for the simple motive that it is an existential want. The other basic assumption is that the action of hackers and ransom demanders is not affected by financial cycles, if anything probably even the reverse – they also need additional revenue in see of inflation. Since of this, no one particular wishes to skimp on stability budgets and be accountable for a breach that cripples the corporation.

But in the area there is chat of the actuality that if in modern yrs the CISOs, people VPs of devices safety, been given every single spending budget they asked for from the CFOs or CEOs, nowadays the circumstance is distinct. The paying for binge has also produced a scenario the place corporations have armed on their own with several cyber programs, some of which aren’t even that helpful. This is possibly a different reason that now stability professionals are being despatched to 1st verify what specifically they acquired in the great yrs and what else can be carried out with these products.

And there is one thing else occurring in the cyber sector, even if it stays a little below the floor due to the fact most of the players in it have no incentive to acknowledge it – the rise of Microsoft’s ability. The large, which is not traditionally seen as a regular player in the cyber market, has drastically strengthened its technological answers in the subject, primarily these delivered with its cloud expert services. Among the other points, it did this through a sequence of purchases of Israeli startups, led by Adallom, but also Aorato, CyberX and other individuals.

In its most recent fiscal report, Microsoft astonished a lot of by indicating that its cyber enterprise presently generates yearly revenues of $15 billion and that it is rising by 40{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1} a calendar year. Microsoft is pushing its safety options not only with cloud providers, but also with Office. Microsoft designs to invest an additional $20 billion in bolstering its cyber answers, consequently only expanding the intensity of competitors in opposition to all the gamers in the sector, many of them Israeli, from Examine Level to CyberArk or Varonis. Google has obviously observed Microsoft’s go and ordered Mandiant in a $5.5 billion deal to strengthen its cyber reaction to cloud buyers and in general.

With or with no Microsoft, a person of the large questions now in the cyber market place is no matter if the slowdown and tighter budgets will bring about a desire for significant makes and nicely-identified companies so as not to danger doing the job with a startup that could not be below tomorrow. Or regardless of whether in its place, with the aim of saving and obtaining a boutique answer at the identical time, buyers will want to buy cyber options specifically from the smaller startups. These will be prepared to compromise much more on the rate and at times will even agree to present it for free in exchange for applying the customer’s title for income advertising to subsequent buyers. In the coming time period it will be easy to distinguish which providers have the most comprehensive and important answer and which of them are firms with a single aspect that can be obtained as element of a a lot more in depth remedy of a important player, even if of slightly lessen quality.

In the meantime, cyber shares have opened a negative gap in opposition to the S&P 500 index, even although Palo Alto Networks and Examine Stage control to preserve relative security. The declines make worth ranges that are starting off to look beautiful and many non-public expenditure funds are retaining an eye on cyber organizations with the goal of merging some of them and creating a likely giant. Of program, even the massive corporations themselves, from Microsoft to Look at Level, see the recent benefit stages and are getting ready to make acquisitions, which will make the cyber sector just one of the most fascinating to look at in 2023.

What White House cyber team thinks about it

What White House cyber team thinks about it

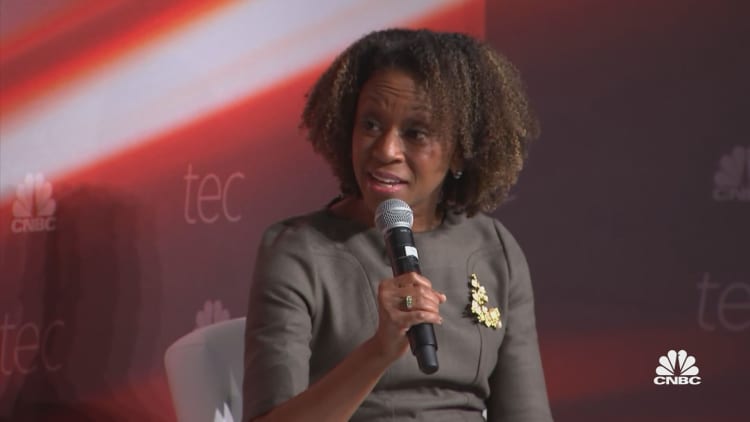
Cyber security education needs to be increased to ward off threats, Principal Deputy National Cyber Director says

Right after Federal Bureau of Investigation Director Christopher Wray explained to lawmakers this 7 days that he has countrywide safety problems about TikTok’s functions in the U.S., a vital member of the White House’s Office of the National Cyber Director expressed support for the FBI and “any measure that will raise security,” but stopped brief of voicing aid for a ban on TikTok that some govt officers assume is needed.

The Biden White Household hasn’t produced any resolve but on a TikTok ban, Kemba Walden, Principal Deputy National Cyber Director, claimed at the CNBC Technologies Govt Council Summit on Tuesday. But growing on her view of a sophisticated national security difficulty with the nation’s major know-how rival, she additional, “we want to concentration on getting in entrance of the adversary. We do not want to just take a reactionary posture in developing policy. We really don’t want transgressors to set our agenda. … We are considerably additional focused on strategic outlook. What is our agenda, and let the transgressors chase us. … If we are reactionary, we continue being reactionary. And there is a spot for that … but if we continue to be in that room, we are just losing a lot more bit by bit.”

With countrywide protection the concentrate, she stated the White Residence is looking at strategic investments to identify how to make domestic units far more resilient and counter information functions. But she also reported TikTok has a accountability to uphold.

“All of these platforms, such as TikTok, will have to preserve security in intellect,” she explained. “Each individual stakeholder has a function in this place, together with the users of TikTok, the builders … all platforms have that obligation in purchase to be equipped to have a net that provides on what we assume, and so I assist any evaluate that will increase safety so that our communities can thrive safely.”

TikTok, which is owned by Beijing-primarily based tech large ByteDance, is applied by over 1 billion folks worldwide each month.

Artur Widak | Nurphoto | Getty Visuals

Wray informed members of the Residence Homeland Protection Committee in a listening to about around the globe threats on Tuesday that he is “particularly concerned” about TikTok’s functions in the U.S.

“They include the probability that the Chinese federal government could use it to regulate details collection on millions of consumers. Or management the suggestion algorithm, which could be employed for influence operations if they so selected. Or to regulate program on hundreds of thousands of equipment, which offers it opportunity to probably technically compromise particular products,” Wray mentioned.

Walden reported she is anxious about TikTok’s impact on youngsters, but also framed the problem in phrases of the bigger issue of adequately educating the younger for the online planet of data.

“I have young adults who expend their whole life on TikTok and since it is so absorbing, but you do ponder about the Chinese government’s inspiration in feeding all of that information stream to thousands and thousands of Americans. And then also all the monitoring that goes along with that,” reported CNBC’s Senior Washington Correspondent Eamon Javers all through the interview. “So you communicate about security has to be a precedence, but if Beijing has very distinct priorities than you do, how do you consider this substantial influence procedure that China is functioning on TikTok for hundreds of thousands of Us residents? At the exact same time they’re obtaining a very various standpoint on what they want the outcome to be.”

“I have young children much too, and I would like that just like drivers licenses are required in advance of they drive a automobile, would not it be charming if they had been needed to have a license?” Walden mentioned in reaction to Javers’ question. She pressured that there was no formal program for the U.S. authorities to make an investment specifically associated to this idea, but included, “which is type of exactly where I start out to believe about assisting our learners, supporting our communities turn out to be much more resilient. It can be not just the know-how and the apps, it’s the people today and the processes and doctrine. … My 9-yr-previous could result in a nationwide safety incident and that’s terrifying, ideal?”

Issues above the Chinese-owned video platform’s capacity to defend U.S. person info from China have developed amid govt officials and customers of Congress in modern months. A Federal Communications Commissioner explained before this month that the U.S. govt should really ban TikTok, and the Committee on Overseas Investment in the U.S. (CFIUS) in the Treasury Office is examining the company’s opportunity national stability implications.

Walden mentioned CFIUS performs an crucial job in countrywide security and cybersecurity, but is ordinarily used as “a surgical knife, not a hammer.”

“I assume it would be a miscalculation for CFIUS to be utilized as a system to establish broad plan. But they absolutely have a potent resource,” she mentioned.

The concern lies with a Chinese law that makes it possible for the governing administration to pressure providers to hand about internal facts. TikTok guardian-firm ByteDance has continued to keep that it isn’t going to retail outlet U.S. person data in China, the place the legislation could be used.

Wray reported on Tuesday that legislation by yourself was “lots of purpose by alone to be very concerned.”

In a assertion, a TikTok spokesperson instructed CNBC on Tuesday that “we are self-assured that we are on a path to thoroughly satisfy all sensible U.S. nationwide protection issues.”

Strengthening cybersecurity education

Walden, who became the 1st person named to her White House cybersecurity placement in May following serving as the assistant general counsel in Microsoft’s digital crimes device, pressured the function of instruction on various situations during the interview with Javers.

“Regardless of what an app is undertaking, we need to actually elevate cybersecurity education in our devices and increase cyber awareness amongst our people today to make certain they’re resilient,” she explained. “Important pondering is a great antidote to some of the perform that other transgressors are working on.”

The Workplace of the National Cyber Director was founded by the Biden administration in 2021, with Chris Inglis remaining named the initial National Cyber Director. The workplace serves as a principal advisor to the president on cybersecurity plan and strategy, aiming to guarantee that Individuals can “share in the full added benefits” of the electronic ecosystem even though addressing and mitigating the dangers and threats located in cyberspace.

Walden explained rising cybersecurity education and learning is just just one of the methods the White Residence is aiming to “get in entrance of the adversary.”

Correction: Owing to an editing error, an before version of this short article misattributed a quote to Kemba Walden, Principal Deputy National Cyber Director. The posting has been up-to-date to contain appropriate attribution.

FBI Director Christopher Wray raises national security concerns over TikTok

Top cybersecurity threats for 2023

Top cybersecurity threats for 2023

Next yr, cybercriminals will be as busy as at any time. Are IT departments completely ready?

Top cybersecurity threats for 2023
Picture: WhataWin/Adobe Stock

Likely into 2023, cybersecurity is nevertheless topping the checklist of CIO concerns. This comes as no surprise. In the first 50 {b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1} of 2022, there ended up 2.8 billion worldwide malware attacks and 236.1 million ransomware attacks. By yr close 2022, it is envisioned that six billion phishing assaults will have been introduced.

SEE: Password breach: Why pop lifestyle and passwords really don’t blend (absolutely free PDF) (TechRepublic)

Listed here are eight best protection threats that IT is probable to see in 2023.

Top rated 8 security threats for following 12 months

1. Malware

Malware is destructive program that is injected into networks and devices with the intention of producing disruption to pcs, servers, workstations and networks. Malware can extract private information and facts, deny provider and obtain entry to methods.

IT departments use safety computer software and firewalls to observe and intercept malware in advance of it gains entry to networks and devices, but malware negative actors continue to evolve ways to elude these defenses. That makes sustaining latest updates to security application and firewalls vital.

2. Ransomware

Ransomware is a sort of malware. It blocks entry to a method or threatens to publish proprietary data. Ransomware perpetrators need that their sufferer corporations spend them income ransoms to unlock devices or return facts.

So much in 2022, ransomware attacks on organizations are 33{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1} increased than they were being in 2021. A lot of companies concur to pay out ransoms to get their programs back again, only to be hit all over again by the identical ransomware perpetrators.

Ransomware assaults are highly-priced. They can destruction organization reputations. Many instances ransomware can enter a corporate community by way of a channel that is open with a vendor or a supplier that has weaker security on its community.

A single action organizations can consider is to audit the protection actions that their suppliers and sellers use to be certain that the stop-to-finish provide chain is secure.

3. Phishing

Pretty much anyone has been given a suspicious e mail, or worse still, an electronic mail that seems to be authentic and from a dependable get together but isn’t. This email trickery is recognized as phishing.

Phishing is a significant threat to providers because it is effortless for unsuspecting personnel to open bogus email messages and unleash viruses. Worker instruction on how to identify phony email messages, report them and hardly ever open up them can definitely help. IT should workforce with HR to make certain that audio email patterns are taught.

4. IoT

In 2020, 61{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1} of providers were being using IoT, and this proportion only proceeds to improve. With the growth of IoT, protection threats also mature. IoT sellers are infamous for utilizing little to no protection on their equipment. IT can fight this menace by vetting IoT distributors upfront in the RFP course of action for protection and by resetting IoT protection defaults on equipment so they conform to corporate specifications.

If your corporation is wanting for additional steerage on IoT protection, the professionals at TechRepublic Quality have put collectively an e-book for IT leaders that is filled with what to glimpse out for and tactics to deal with threats.

5. Internal personnel

Disgruntled employees can sabotage networks or make off with mental property and proprietary data, and staff who apply poor safety patterns can inadvertently share passwords and leave devices unprotected. This is why there has been an uptick in the selection of businesses that use social engineering audits to look at how very well staff safety insurance policies and techniques are performing. In 2023, social engineering audits will proceed to be used so IT can check the robustness of its workforce protection policies and tactics.

6. Information poisoning

An IBM 2022 research found that 35{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1} of firms were being working with AI in their company and 42{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1} ended up exploring it. Artificial intelligence is going to open up up new options for organizations in each individual sector. However, the negative actors know this, as well.

Conditions of data poisoning in AI systems have started to look. In a information poisoning, a destructive actor finds a way to inject corrupted information into an AI technique that will skew the results of an AI inquiry, most likely returning an AI final result to organization decision makers that is untrue.

Data poisoning is a new attack vector into company units. One particular way to safeguard from it is to consistently observe your AI outcomes. If you abruptly see a method trending appreciably away from what it has disclosed in the previous, it is time to search at the integrity of the info.

7. New technological innovation

Companies are adopting new technological innovation like biometrics. These systems yield enormous benefits, but they also introduce new stability hazards given that IT has limited experience with them. A single stage IT can choose is to very carefully vet each and every new engineering and its sellers right before signing a order arrangement.

8. Multi-layer stability

How a great deal safety is sufficient? If you’ve firewalled your community, mounted security monitoring and interception software program, secured your servers, issued multi-variable identification signal-ons to employees and executed information encryption, but you forgot to lock physical services that contains servers or to put in the most recent safety updates on smartphones, are you coated?

There are numerous layers of security that IT will have to batten down and keep track of. IT can tighten up security by producing a checklist for each individual security breach issue in a workflow.

Is Your Board Prepared for New Cybersecurity Regulations?

Is Your Board Prepared for New Cybersecurity Regulations?

Boards are now shelling out interest to the need to take part in cybersecurity oversight. Not only are the implications sparking concern, but the new rules are upping the ante and changing the game.

Boards have a specifically essential role to make certain acceptable administration of cyber danger as aspect of their fiduciary and oversight purpose. As cyber threats enhance and organizations around the world bolster their cybersecurity budgets, the regulatory group, together with the SEC, is advancing new prerequisites providers will will need to know about as they enhance their cyber strategy.

Most organizations we’ve analyzed focus on cyber defense alternatively than cyber resilience, and we consider that is a blunder. Resiliency is additional than just protection it’s a system for restoration and business continuation. Being resilient suggests that you’ve done as a lot as you can to defend and detect a cyber incident, and you have also finished as a great deal as you can to make certain you can proceed to operate when an incident takes place. A business who invests only in defense is not taking care of the danger connected with acquiring up and running yet again in the function of a cyber incident.

Our analysis implies that most board associates consider it’s not a matter of if, but when their firm will knowledge a cyber occasion. The top aim of a cyber-resilient firm would be zero disruption from a cyber breach. That will make the focus on resilience far more essential.

New SEC Rules Will Change the Board’s Part

In March 2022, the SEC issued a proposed rule titled Cybersecurity Danger Management, Technique, Governance, and Incident Disclosure.  In it, the SEC describes its intention to demand general public corporations to disclose no matter if their boards have users with cybersecurity experience: “Cybersecurity is by now amongst the prime priorities of lots of boards of directors and cybersecurity incidents and other challenges are regarded as a single of the greatest threats to providers. Accordingly, investors may locate disclosure of no matter whether any board members have cybersecurity skills to be crucial as they contemplate their investment in the registrant as nicely as their votes on the election of administrators of the registrant.”

The SEC will shortly need corporations to disclose their cybersecurity governance abilities, together with the board’s oversight of cyber chance, a description of management’s role in evaluating and running cyber hazards, the applicable knowledge of these kinds of administration, and management’s purpose in implementing the registrant’s cybersecurity procedures, strategies, and procedures. Exclusively, wherever pertinent to board oversight, registrants will be needed to disclose:

  • regardless of whether the complete board, a specific board member, or a board committee is dependable for the oversight of cyber pitfalls,
  • the processes by which the board is informed about cyber hazards, and the frequency of its discussions on this topic,
  • regardless of whether and how the board or specified board committee considers cyber threats as section of its small business tactic, possibility administration, and fiscal oversight.

The fantastic information is that boards are creating progress in this area. Recent study we conducted with analysis lover Proofpoint confirmed that just about two thirds of board customers consider the organization is at threat of a material cyber assault. Almost 3 quarters of respondents felt the investment decision their business has created in cybersecurity is ample, and about the same volume come to feel cybersecurity is a top rated priority.  Seventy-6 {b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1} reported that cybersecurity matters are mentioned at every single board meeting, or extra often than that.

Nevertheless, our investigation also uncovered attitudes and beliefs that have to alter. Only 23{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1} of board associates assume the danger of an attack on their firm is extremely probable. About 47{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1} believe that their business is unprepared for a cyber assault, begging the issue “what are they carrying out about this?”  And about a single 3rd of board customers say they interact with the CISO only when he/she is presenting to the board. There is plainly home for improvement in aligning board members with the companies cybersecurity priorities.

Board Member Cybersecurity Attitude Adjustment

To give proper oversight and comply with the regulatory ecosystem, board members are going to have to up their cybersecurity recreation. It’s no extended suitable to just listen to about the protections set in put, or the effects of the most recent phishing workout. Board members ought to get the place that cyber assaults are probably, and training their oversight role to make sure that executives and administrators have built suitable and ideal preparations to reply and recover. Soon after all, if we believe just about every group has a possible chance of becoming breached or attacked, and it is not probable to be 100{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1} protected from each and every assault, the most rational solution is to make sure the business can get better with minimal or no harm to operations, to the economical bottom line, and to the organization’s reputation.

Creating resiliency in an business requires right oversight from the boardroom dependent on a obvious strategy crafted on business enterprise and economic evaluation. Below are a number of tales about how providers we studied have carried out this.

A monetary companies business CEO realized his board was not well versed in the enterprise context or fiscal exposure possibility from a cyber attack. He hired a third-bash consulting organization to perform a cybersecurity maturity evaluation. The enterprise CISO offered the effects of the report to the business hazard administration subcommittee, producing a effective dialogue all over the small business and economical effect of various investments in cybersecurity. What-ifs about investing in diverse amounts of maturity assisted the board have an understanding of the economical/threat tradeoffs and presented them with both a language and viewpoint required to perform the required oversight of cybersecurity strategies supplied by the government staff.

Another group targeted their board on the alignment of their cybersecurity method and operational risk. The CISO, in collaboration with the main chance officer, leverage fiscal analytics to aid with bridging the hole among the cyber exposures to operational losses. The board was able to recognize the publicity of the corporation from a hazard point of view, resulting in optimizing their cyber insurance plan as a way to mitigate the recently recognized possibility.

By working with the language of risk, resiliency and status in cybersecurity discussions with board customers, operational executives are capable to bridge the gaps that generally manifest amongst the technical requires witnessed to fulfill cybersecurity wants, and the oversight obligations executed by boards. Perhaps this was greatest articulated by Peter R. Gleason, the president and CEO of the National Association of Corporate Directors (NACD), when he mentioned, “We have listened to from many administrators the require to realize the financial publicity ensuing from cyber possibility, heading further than the menace-targeted, complex cyber presentations most boards receive.”

As we significantly rely on boards to prolong their fiduciary duties to cybersecurity designs, operational professionals should also just take a function by presenting individuals programs in a way that align with the way boards ideal add.  Conference the new regulatory prerequisites can be greater achieved by aligning how operational leaders talk about cybersecurity with their boards.

Raise Cybersecurity Knowledge in your Boardroom

In this article are some actionable insights to start currently so your board fulfills (or exceeds) the new SEC recommendations, and provides the ideal amount of oversight to cybersecurity ideas:

1. Establish a frequent language for discussing the sophisticated issues of cyber threat and resilience.

Boards want to simplify bewildering, technical discussions loaded with nuanced safety phrases. It’s not that these are unimportant, it is just not as efficient for the board as an economic investigation that demonstrates how cyberattacks endanger businesses financially in the brief and long term and how the organization will be back again up and jogging, i.e. resilient. Our research displays that insurance firms are taking the direct here, as they shifting the cyber discussion from a hugely technological and ambiguous safety just one to a single exactly where enterprises can fully grasp and effectively handle their fiscal exposure.

2. Retain cyber resiliency on the board’s agenda and in conversations with management.

Our exploration implies that boards are listening to about cybersecurity from administration but the discussions ought to take location extra normally. It’s not a “one and done” kind of choice it is a continually changing and relocating goal.  The far more typically the board is exposed to the cyber-circumstance of their business, the a lot more relaxed and far more pro they grow to be.

3. Build broader bridges amongst cybersecurity executives and board members.

Board associates need to have obtain to, and interactions with, cybersecurity authorities inside the business. Although inviting CISOs to report to the board can help with identification, it does not build robust connections among board associates and protection executives. Come across strategies to facilitate this romantic relationship.

In our investigation, we have noticed board associates reaching out to CISOs in involving board meetings to go over cybersecurity headlines, to share individual incidents that may possibly take place, and just to get superior acquainted. That way, when there is an urgent need to have for the board to weigh in on a cybersecurity situation, the partnership is by now in position and the conversations are much more related and clear.  A cyber incident is not the time to build the bridge that must happen very long in advance of the challenging discussions have to choose put.

Board training to meet up with the SEC prerequisites can take place organically if both the board and running executives just somewhat tweak their technique.  Wondering in terms of resiliency as an alternative of safety, balancing the business and specialized risks, speaking about cybersecurity in terms of financial exposures, and expanding the frequency of dialogue of the cybersecurity landscape confronted by the firm, will assistance directors on boards get ready for and satisfy the SEC policies probable to come.  And that will go a extended way in direction of growing organizational resiliency.

Federal payroll website for over 170 agencies gets a cybersecurity update

Federal payroll website for over 170 agencies gets a cybersecurity update

Above 170 companies are now looking at a new login system to access federal employees’ payroll info, and other kinds of facts for human assets administration.

The Nationwide Finance Middle, an company housed underneath the Agriculture Office, has introduced a multi-variable authentication technique for its federal consumers to obtain the payroll and staff internet site.

“Our final decision to apply multi-aspect authentication is a best apply that makes it possible for NFC to safe programs by providing a multi-layered method to…

Browse Extra

Above 170 agencies are now looking at a new login procedure to entry federal employees’ payroll information, and other kinds of information for human sources administration.

The National Finance Heart, an company housed under the Agriculture Section, has released a multi-aspect authentication procedure for its federal buyers to obtain the payroll and personnel web site.

“Our conclusion to employ multi-aspect authentication is a greatest practice that allows NFC to protected techniques by providing a multi-layered method to securing user accounts, thus producing the account significantly less likely to make it possible for unauthorized obtain,” a USDA spokesperson mentioned in an electronic mail to Federal Information Network.

The NFC is 1 of the four big federal payroll companies for companies. NFC partners with additional than 170 businesses, and gives payroll products and services to much more than 600,000 federal staff — making it especially significant to protect feds’ economic information and facts with enhanced cybersecurity tactics. Multi-issue authentication demands customers to verify their identification through various techniques, intending block any users who shouldn’t have accessibility to private information.

With the web-site update, the NFC has also come to be a single of many businesses hoping to get techniques to comply with the White House’s federal cybersecurity and zero have confidence in requirements.

“USDA will go on to adhere to and carry out all federal mandates, govt orders and Nationwide Institute of Specifications and Engineering (NIST) steering to ensure the security of all worker and customers’ accounts, facts and details,” the spokesperson mentioned.

Implementing multi-element authentication is just a person part of governmentwide cybersecurity specifications for federal businesses. It’s provided, for occasion, in the Federal Details Security Modernization Act (FISMA), which demands agencies to build a possibility administration framework and be certain specified stability controls. It is also element of cybersecurity direction from NIST, as effectively as the Biden administration’s executive order on enhancing the nation’s stability. Multi-aspect authentication is furthermore a need underneath the White House’s zero have confidence in strategy, which the Biden administration introduced in January of this calendar year.

But there is even now a long way to go to attain governmentwide compliance with the White House’s security specifications. Although the White Property produced its zero trust strategy back again in January, several agencies have considering that then created only minimal development on employing multi-variable authentication. As of now, most businesses have not adopted multi-variable authentication throughout all of their units, even if they are employing it in some locations. Just 13 agencies have fully adopted the practice throughout all of their enterprises.

Some fears over cybersecurity have also arisen together with the increase of remote get the job done and telework for federal workforce, which may possibly open up the doorway to larger possible for cybersecurity hazards.

“The rising reliance on distant function has companies grappling with the challenge of unmanaged individual equipment of staff members staying utilized for function. They normally really don’t have the similar degree of defense that corporation-owned devices do, nor can these equipment be monitored for abnormal or anomalous behavior,” the spokesperson stated.

But multi-element authentication on NFC’s internet site can enable mitigate that sort of danger, according to the spokesperson. It is portion of the motive that the company carried out the adjust in Oct.

And the update to NFC’s internet site is not the only forthcoming adjust for the agency when it arrives to cybersecurity. Alongside with implementing a multi-element authentication system, the company also programs to before long increase endpoint detection and response, application source chain inventory, and asset visibility and vulnerability detection. USDA will also continue on to maintain trainings for workers on the value of guarding personalized information. All of those ideas are also necessities less than the White House’s zero have faith in guidance, as well as the cybersecurity executive get.

Some of these demands from the zero believe in guidance are beginning to get tough deadlines, far too. According to a the latest Workplace of Administration and Spending budget memo, agencies have a 90-working day deadline, setting up from Sept. 14, to inventory all of their 3rd-bash computer software.

In basic, not all kinds of multi-component authentication are similarly safe. Eric Mill, senior advisor to the federal chief information officer, has stated that SMS textual content messages and drive notifications, for occasion, are even now susceptible to phishing attacks. Mill has also said that the changes beneath the White House zero have faith in approach have a a lot more significant intention — and broader implications — than just utilizing a multi-issue authentication method for federal businesses.

“We’re looking at a key architectural change for the federal government. And we know that is a multi-year procedure,” Mill mentioned in January, when the White Home in the beginning produced the zero believe in method. “We’re making an attempt to both equally layout an oversight and timing process that reflects the urgency with which we need to move and the fact of the dimensions of the do the job that is happening.”


Five Cybersecurity Predictions That Will Likely Come True In 2023 And Five That Won’t

Five Cybersecurity Predictions That Will Likely Come True In 2023 And Five That Won’t

Christopher Prewitt is CTO at Inversion6, dependable for assisting establish protection-similar solutions and expert services for buyers.

Total, cybersecurity remains a very reactive marketplace. Yet, every single yr the specialists try out to identify the dominant technology trends and how attackers could try to leverage them in the coming months.

With that in head, I’d like to tackle 10 widespread predictions for 2023. Centered on my expertise in cybersecurity, below are 5 that I assume will verify proper and 5 that most likely won’t.

1. Attackers will weaponize artificial intelligence and device learning.

Bogus. It’s not that they could not go after these far more innovative approaches it is that they simply just really do not need them. New productive attacks in opposition to Uber, Twitter and some others verify that easy source chain-based mostly strategies, company e mail compromises and credential-dependent assaults nonetheless operate just high-quality.

Sure, new techniques are getting introduced to stop multi-aspect authentication fatigue and minimize off the quick routes to obtain, but they’ll uncover a workaround. Bottom line, why would an attacker construct tables of facts for a machine finding out motor when they can mail a Microsoft Term document to a number of of your staff members and get every thing they require?

2. Government polices are about to balloon.

Legitimate. Even with the new comprehending concerning the U.S. and the EU, there will proceed to be modifications in global privacy specifications. In the meantime, new protection laws will certainly come from the SEC. We’re also very likely to see much more executive orders, more Congressional committee conferences and a large amount much more talking total from politicians in the coming 12 months.

And but, for all their expansion in amount and complexity, most of these restrictions will almost certainly deficiency serious teeth. We haven’t seen any true shakeups since the birth of the “accept all cookies” button. This is not likely to modify in 2023.

3. Hacktivism is on the rise.

True. From a cybersecurity point of view, the ongoing conflict in Ukraine is notable as the very first war to prompt big-scale cyberattacks from nonmilitary citizens of other nations.

The Ukrainian army has mainly outsourced their offensive cyber operations to hackers across the globe, who are now attacking Russian infrastructure as the two a pastime and a political assertion. I would be expecting these sorts of offensive operations across borders to develop into more mainstream in the coming yr. The outcomes could prove pretty unpredictable.

4. Mobile products will finally be focused by attackers.

Untrue. There are usually efforts in this house (and heaps of definitely expensive zero days), but commodity attacks from these platforms aren’t happening as professionals have predicted.

Apple and Google do a good work securing their units, and they stay substantially much less risky than business operating techniques. On leading of this, most people up grade to a new cellphone each individual two several years, inadvertently restricting the exposure chance that comes with managing an outdated system.

5. Zero-have faith in styles are about to have a substantial influence on safety.

Legitimate. As additional and much more organizations abandon their internally hosted knowledge centers and migrate to the cloud, they will ever more depend on zero-have faith in products to boost safety and avert lateral motion.

In the close to upcoming, this new actuality will essentially change how we carry out penetration tests and how we secure our networks. Jointly, a cloud workload and a zero-belief design will basically eviscerate the network edge and may even take out the need to have for major community safety for some businesses.

6. The following significant hack will target a hyperscaler/cloud company.

Bogus. These vendors might certainly be hacked (we have presently witnessed some firms facing concerns), but the impact is unlikely to be massive-scale. It’s significantly a lot more probable that cloud consoles would be the future huge focus on for assault.

As organizations migrate workloads and servers to the cloud, these cloud consoles develop into the delicate underbelly of the complete organization. We have viewed lots of these cases in the past, but I believe that the danger is rising even larger as significantly less experienced companies start out migrating to the cloud.

7. Lively reaction will turn into the default defense posture.

Legitimate. Traditionally, the sector has progressed from preventive to detective controls. Continue to, alerts and timely response have accomplished minor to slow the threats. As a result, we could well see units get started to self-evaluate and reply to assaults in genuine-time applying locked accounts, compelled password resets, network comprise methods or other strategies to stop facts from egressing.

If things get terrible enough, we can anticipate to see these features turn into default configurations, and we will start off going through auto-responses from several of the platforms we use and operate.

8. 5G will support reduce cyberattacks.

Fake. In fairness, 5G presents personal networks to prevent direct web obtain to their fleet of gadgets, which will assist some know-how vendors beef up their safety. Also, the increased bandwidth of 5G is mostly a wash for safety given that bandwidth alone has not been a significant hurdle for attackers in the earlier.

Still, 5G will probably supply an even greater prospect for assaults, specifically IoT vulnerabilities. It is not a flaw so a great deal as a attribute it’s uncomplicated math dependent on the sheer amount of new equipment that will be coming on the web thanks to this new engineering.

9. Governments will be additional direct on attribution.

Real. In 2022, we observed various public experiences of U.S. espionage attempts in China. This falls in line with the U.S. government’s latest pattern of outing its own cybersecurity enemies by identify.

As China, Iran, North Korea and many others continue to acquire their defensive capabilities, we’ll most likely hear much more and a lot more about attribution of attacks. We can also anticipate to listen to far more about the U.S.’ cyber functions, irrespective of whether we like it or not.

10. Cyber insurance coverage will assist much more firms cope with uncertainty.

Untrue. The cyber insurance coverage current market saw some drastic variations in 2022. Costs are way up carriers are starting to be less and much less, and in 2023 a lot of consumers will probable facial area even far more new necessities to obtain coverage, together with mandatory external vulnerability scans and 3rd-party validation.

We’ll continue to see some solutions out there for compact- and medium-sized corporations (plans that offer you entry to products and services but essentially purpose as self-insurance plan), but in general, we are currently viewing numerous companies abandon their policy renewals for 2023.


Forbes Technological know-how Council is an invitation-only neighborhood for globe-course CIOs, CTOs and engineering executives. Do I qualify?