Rhode Island Online Businesses Use JPG Designs for Web Design and Development

Rhode Island Online Businesses Use JPG Designs for Web Design and Development
JPG Designs Logo
JPG Designs 1

JPG Styles is a Rhode Island net advancement and digital marketing company in Warwick. They supply web page growth, Seo, and online advertising.

If there is a single matter that can be crucial to a business’ accomplishment, it is a present day, skilled and cell pleasant web site.”

— Jeff Pratt, Operator of JPG Patterns

WARWICK, RHODE ISLAND, UNITED STATES, November 14, 2022 /EINPresswire.com/ — With growing consumer demand from customers for on the internet expert services and world-wide-web utilization, a dedicated web site for e-commerce or products and services has come to be a requirement for businesses close to the world. Irrespective of whether an proven retail store or a startup, a excellent, responsive site with purposeful UI and UX is necessary for attracting clients and traders. Nonetheless, it can be tough for business house owners devoid of expertise and knowledge in coding, the hottest Website positioning strategies, SERP updates, and more to style and design a internet site that increases their on the internet presence and profitability. For them, hiring a net style and design enterprise is a fantastic alternative. For instance, quite a few firms in Rhode Island have benefited from operating with JPG Styles, which presents comprehensive web page solutions, which include web page structure & growth, SME, brand designing, Web optimization, and website web hosting.

Brick-and-mortar organizations and people with out programming language expertise can truly feel that creating a website for their small business is tough. As a result, they might research on-line for net style and design companies to identify a developer in Rhode Island. Nevertheless, discovering a skilled internet developer on the internet who fulfills the small business necessities and can integrate the best systems into their web site is hard. Even so, some trustworthy electronic service vendors, these as JPG Designs in RI, layout and develop business internet sites and provide full purchaser satisfaction.

“I am incredibly glad we chose JPG Types to design and style our new website! Jeff and Zach were good to perform with and did all the things we hoped to make it attractive and specialist.” – Alfred Paul

In buy to produce a website that attracts people and boosts an on the web business’s visibility, a skilled web development company will consider the time to find out about its target viewers, the field, and shopper expectations. Then, the net designer will design the web-site with the inputs, enterprise aims, and functionality expected from the consumer. A skilled internet developer RI organization can also ensure relieve of navigation, optimum load speed, and outstanding consumer working experience in the internet site growth process. These technological factors enable business enterprise web sites to entice shoppers and deliver organic development. For case in point, JPG Styles has a 25-point checklist just before it launches a entirely-functional website on the net.

Besides coming up with a spectacular web-site optimized for mobile and desktop, a web style and design enterprise can also offer net web hosting and maintenance remedies. These are important components to assure an online internet site runs efficiently, 24/7, and is safe from glitches and security breaches. Even though launching a site is 1 issue, employing the ideal Search engine optimization approaches and on the net internet marketing to make it a productive enterprise demands enable from Web optimization and digital internet marketing gurus. As a end result, lots of Rhode Island organizations pick a entire-services company like JPG Designs, which gives a finish package deal, from world-wide-web planning and growth to nearby and global Web optimization.

About JPG Patterns

JPG Layouts is a 5-star rated internet progress and on the net advertising business in Warwick, Rhode Island, specializing in internet style, logo structure, lookup motor optimization (Website positioning), and net marketing and advertising. They have offered professional web design, Website positioning, and marketing and advertising options to hundreds of firms in Rhode Island and Southern Massachusetts considering that 2010.

JPG Styles
&#13
785 Main Ave, Warwick,
&#13
RI 02886, United States
&#13
+14017379321

Jeff Pratt
JPG Patterns
+1 401-737-9321
email us here

Website Design and style Companies in Rhode Island (RI)

Microsoft finally acknowledges gaming performance issues on Windows 11 22H2, blocks update

Microsoft finally acknowledges gaming performance issues on Windows 11 22H2, blocks update

Nearly as soon as the Windows 11 2022 update (variation 22H2) went public in September, users started noticing gaming and other similar functionality concerns on the new element update. The very first to complain ended up people who were being working Nvidia graphics playing cards in their programs. Nvidia blamed Microsoft for the troubles, as the former said new GPU debugging applications in Windows 11 22H2 ended up messing factors up, main to reduce effectiveness in games. And the problems have persisted in spite of Nvidia releasing motorists to resolve the difficulty.

Rapid-forward practically two months, Microsoft has eventually acknowledged the problems and has confirmed that Nvidia was suitable in its evaluation of the underlying dilemma. On its Home windows overall health dashboard, the Redmond organization has released information about the concern and has blocked the update on impacted equipment. Microsoft writes:

Some video games and apps may well expertise lower than expected overall performance or stuttering on Home windows 11, edition 22H2. Influenced games and applications are inadvertently enabling GPU efficiency debugging capabilities not intended to be utilized by individuals.

To safeguard your update knowledge, we have used a compatibility maintain on equipment impacted by this problem from staying made available or putting in Home windows 11, model 22H2.

A workaround has also been provided, suggesting that consumers update their game titles and linked applications:

Workaround: If you are now on Windows 11, model 22H2 and are suffering from this difficulty, you may possibly be able to resolve it by updating your game titles and gaming associated applications to the hottest version available. If you are uncertain how to update the video games and apps you have put in, you will require to seek the advice of the developer of those video games and applications but most will update immediately through the retail store they were being acquired from or right when opening them.

Last but not least, Microsoft has said that it is working on a correct for the challenge and has requested people not to manually update their OS:

Future measures: We are working on a resolution and will supply an update in an impending launch. Note: We recommend that you do not attempt to manually improve working with the Update now button or the Media Generation Resource right until this situation has been resolved and the safeguard eliminated.

Apart from complications on Nvidia GPUs, reviewers and game testers have also been complaining of buggy performance on AMD’s Ryzen CPUs. While AMD claimed it did not see any this kind of troubles on its end, some of the testers carry on stressing that the challenge is in fact actual, citing a lot more tests.

Supply: Microsoft

Linux gaming laptops may finally get Nvidia Advanced Optimus support in near future

Linux gaming laptops may finally get Nvidia Advanced Optimus support in near future

Nvidia is apparently contemplating a new user-house API (uAPI) for dynamic multiplexer (MUX) switching in Linux laptops. Now, MUX switching is dealt with by the vga-swicheroo infrastructure in the Linux kernel. Having said that, Nvidia feels that vga-switcheroo just isn’t reduce out for dynamic MUX switching also recognised as Advanced Optimus.&#13

For individuals not mindful, modern Home windows laptops utilize computerized switching in between the reduced-electrical power built-in graphics in the CPU and the extra electrical power-hungry discrete GPU (if offered) in buy to decrease energy intake during non-intensive duties. This is named MSHybrid or, in Nvidia talk, Optimus. Whilst Optimus does convey battery lifestyle positive aspects, all the frames created by the dGPU will have to move by the iGPU that can turn out to be a opportunity bottleneck dependent on the workload.&#13

A MUX swap allows the person to physically change the routing and bypass the iGPU altogether. This ought to deliver a perceivable advancement in frames aside from making it possible for other features this sort of as Nvidia ShadowPlay capture for the Home windows desktop or variable refresh price technology this sort of as G-Sync. Laptops these types of as the Asus ROG Strix Scar 15 allow for the user to change the MUX from within just Windows, but this necessitates a process restart every single time. &#13

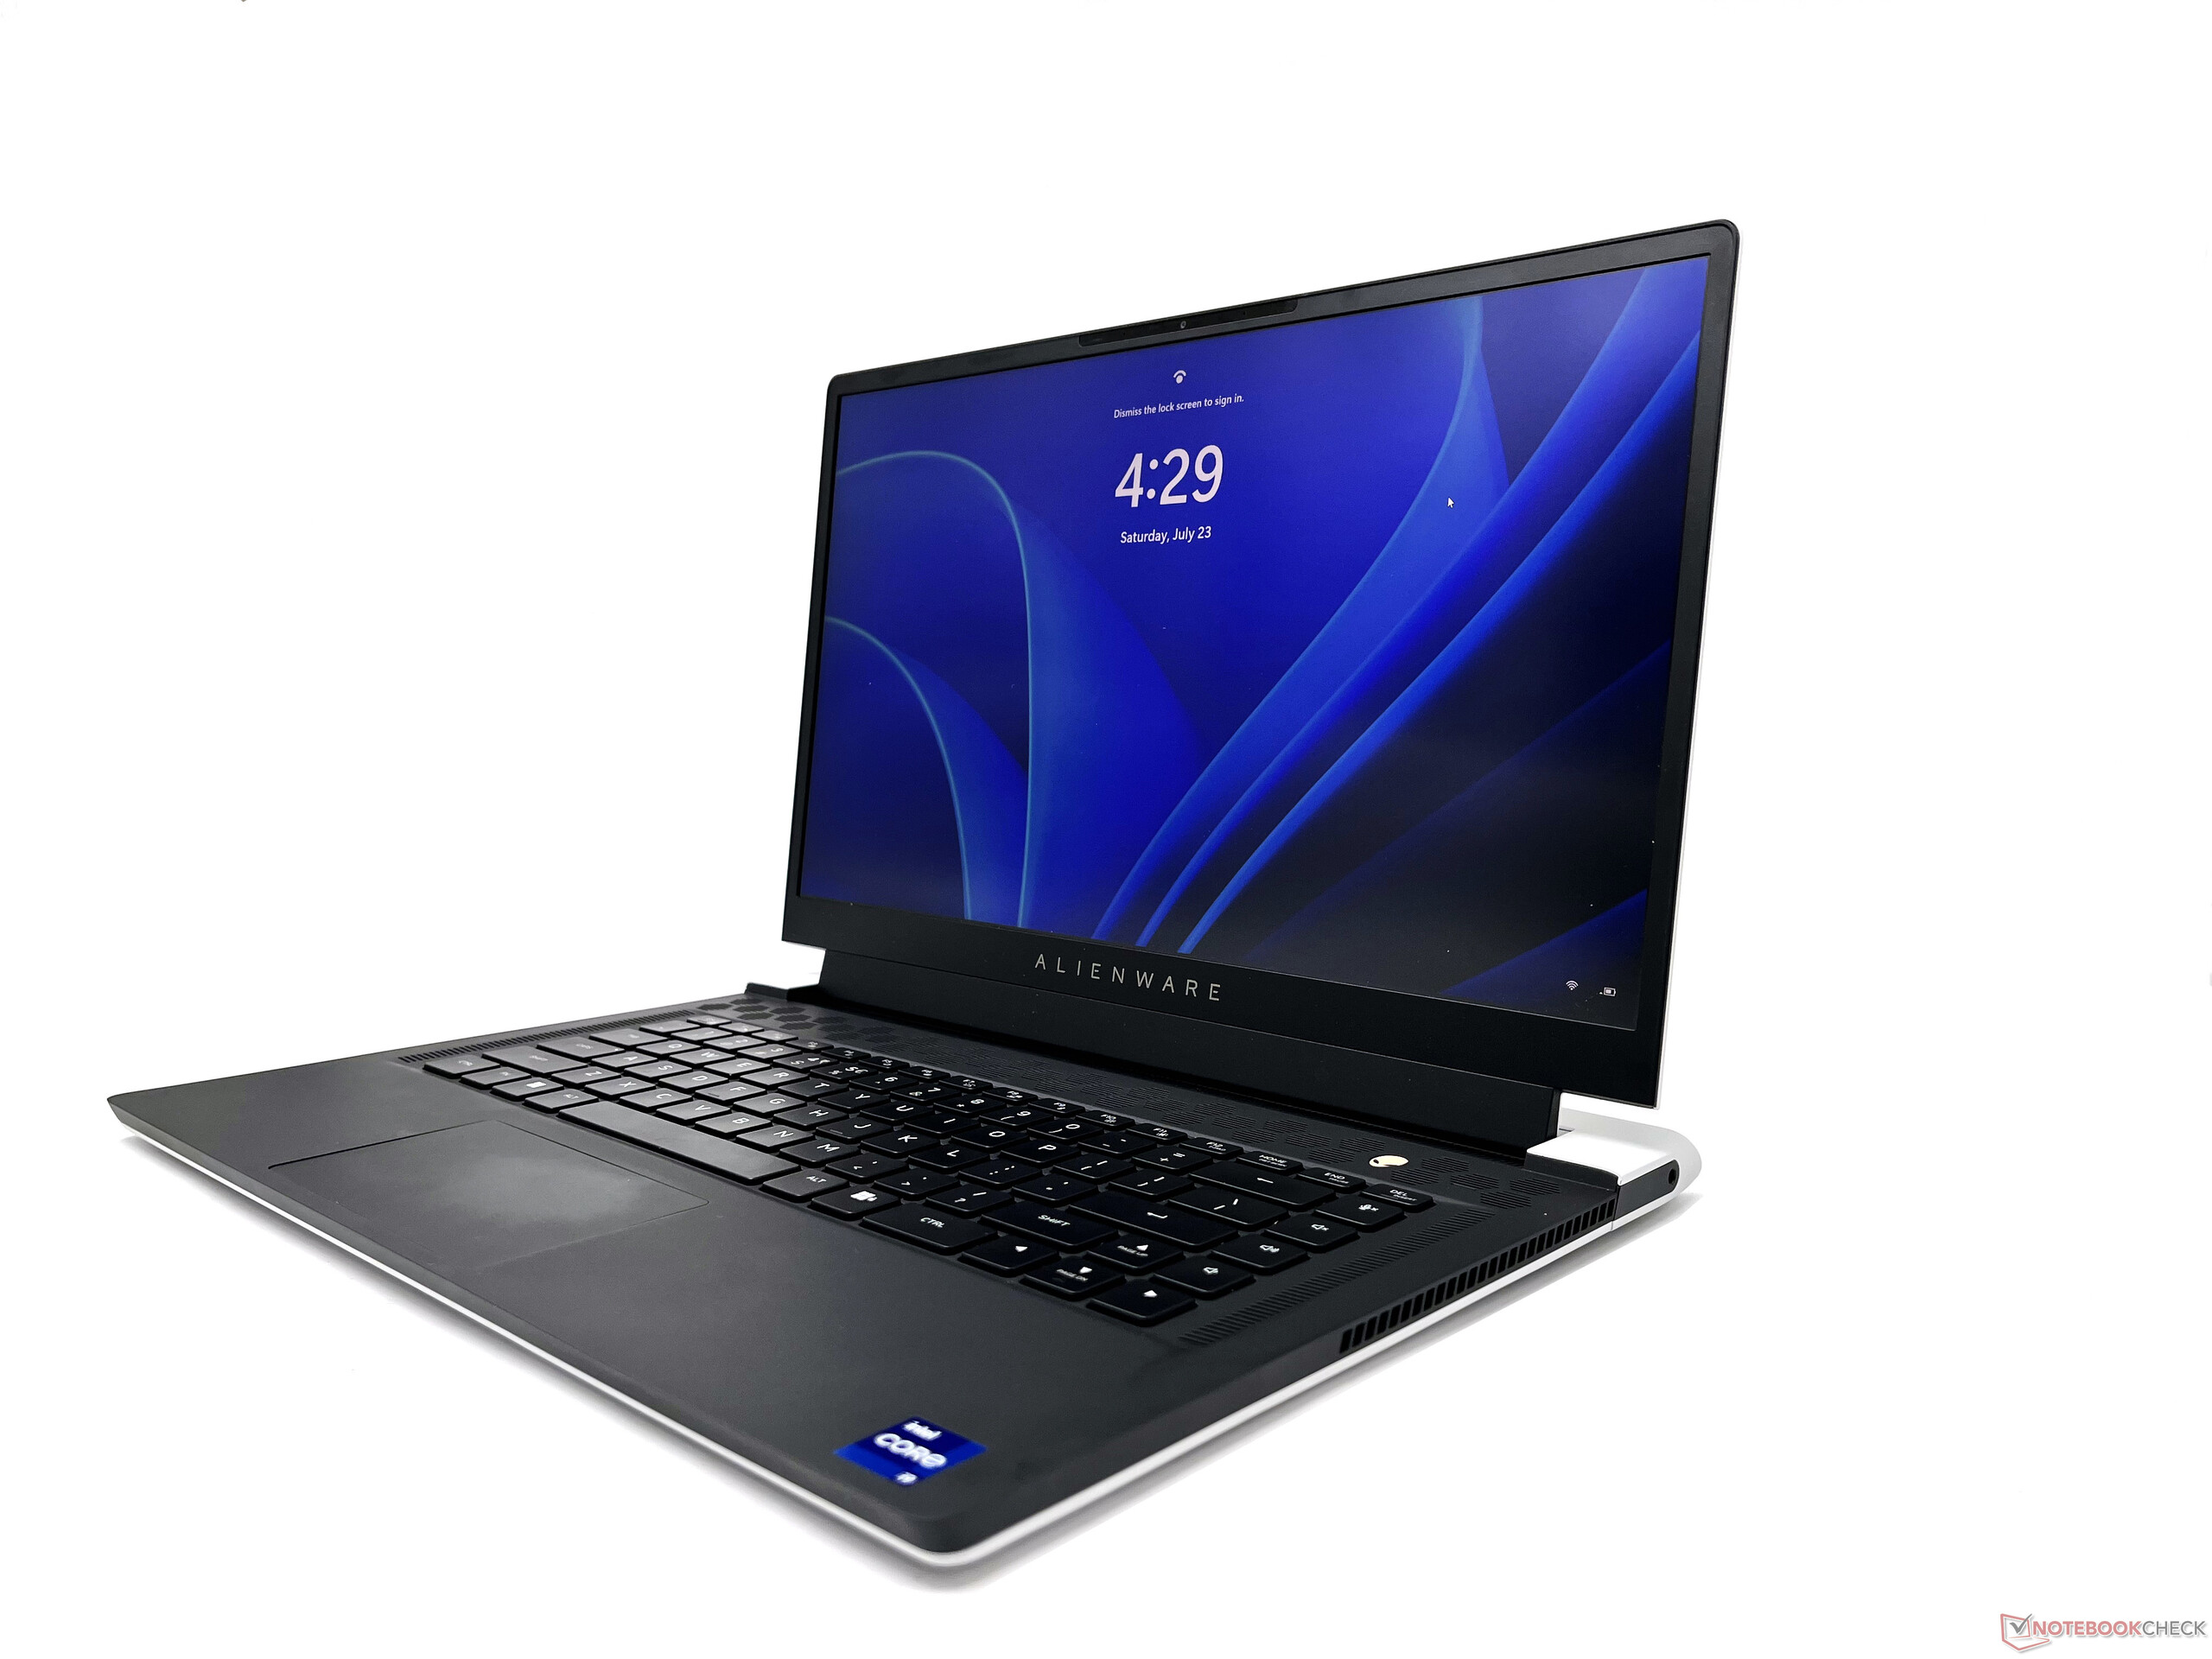
On the other hand, laptops this sort of as the Alienware x15 R2 provide what is called Innovative Optimus or dynamic MUX switching that can transform the MUX routing on the fly. Nvidia claims that Advanced Optimus can present enhanced frame charges, lowered latency, and assist for G-Sync displays routinely without the consumer possessing to worry about manually switching MUX selections in the BIOS or reboot each individual time there’s a environment change.&#13

Now, Nvidia desires to deliver this ability to the Linux kernel. Nvidia software package engineer Daniel Dadap posted a proposal for an “RFC-DRM-based uAPI for Dynamic Mux Switching” on freedesktop.org. In accordance to the Nvidia engineer, vga-switcheroo is unsuitable for MUX switching when the exhibit is lively. This is due to the fact the current implementation assumes that MUX switching is attainable only when neither GPU is driving the screen. &#13

One particular technique would be to increase vga-switcheroo’s performance, but that would also demand including userspace abilities as properly. Vga-switcheroo also assumes that there can be only one MUX in a program involving the iGPU and the dGPU. Whilst this is correct to a substantial extent, Nvidia notes that this assumption can impede some present and foreseeable future patterns that can use numerous MUXs (a person for the internal panel and one for the exterior, for instance). Nvidia has been internally tests and has even created an early X11/GLX prototype for dynamic MUX, according to Dadap.&#13

The proposal calls for a new uAPI although also coupling the MUX extra tightly with the Linux Immediate Rendering Manager (DRM)-Kernel Manner Setting (KMS). Primarily, the dynamic MUX handle purpose will have to be assigned to a manner-setting shopper these types of as an X server or the Wayland compositor that currently has context of what is being drawn on screen.&#13

More specialized facts and probable roadblocks about Nvidia’s proposal to give Highly developed Optimus on Linux can be observed at the Source connection underneath. At present, Nvidia is soliciting opinions from the community. If this proposal without a doubt materializes, the hybrid graphics expertise on Linux may perhaps ultimately be on par with what is presently out there in Home windows laptops right now.&#13

Buy the Alienware x15 R2 with Main i9-12900H and RTX 3080 Ti on Amazon

A More Efficient, Innovative and Greener 11.11 Runs Wholly on Alibaba Cloud

A More Efficient, Innovative and Greener 11.11 Runs Wholly on Alibaba Cloud

International primary cloud company acquiring much more with less although doubling the use of clean strength at important facts facilities all through the world’s most significant global browsing festival

HANGZHOU, China, November 14, 2022–(Small business WIRE)–Alibaba Cloud, the electronic engineering and intelligence spine of Alibaba Group, has when all over again excelled in its mission of supporting the group’s 11.11 World wide Procuring Festival, many thanks to its high-effectiveness computing and impressive know-how. Drawing on self-developed infrastructure updates, the group observed an 8{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1} year-on-year conserving in computing cost for each useful resource device from April 1 to November 11.

“The breadth and depth of cloud technological innovation deployment all through this year’s 11.11 has when all over again showcased Alibaba’s greatest cloud and know-how apply be it by way of essential architecture like self-proprietary engineering powering higher-overall performance computing and database products, or customer-going through XR (extended truth) and livestreaming systems. We intend to carry on implementing these proven abilities to even greater provide our consumers and support them to be much more successful, revolutionary and greener in their very own digital transformation journeys,” explained Li Cheng, Main Technology Officer (CTO) of Alibaba Group.

Undertaking a lot more with much less by means of cloud-native and serverless improvements

This year’s 11.11 was powered by Alibaba Cloud’s focused processing unit for the Apsara Cloud operating program. The upgraded infrastructure procedure, considerably enhanced effectiveness of computing, storage and network in data facilities supporting the function, while also reducing network latency. For instance, with this new upgrade supported by cloud-native technological know-how, ordering, pre-sale harmony payment and refunding could be introduced at the same time with an enhanced scalability and decreased latency.

In the course of this year’s 11.11, the front web page of Taobao, just one of Alibaba’s e-commerce platforms, was upgraded by the latest serverless technological innovation, making it possible for for automated scaling with excessive elasticity primarily based on actual workloads.

Alibaba Cloud’s cloud-native databases goods also appreciably expanded the capacity of consumers’ purchasing carts by additional than a double, from 120 goods to 300. The ApsaraDB for Redis Enhanced Edition (Tair), a cloud-based in-memory database support for enterprises, supports new capabilities these types of as products grouping and sorting, enabling individuals to organize their purchasing cart in accordance to their have preferences. They could also make use of the ‘select’ function to love cross-merchant discounts, to pre-order items and use vouchers for a much more gratifying purchasing experience.

Modern technological know-how delivers additional immersive consumer expertise

A much more immersive browsing practical experience was produced this calendar year many thanks to Alibaba’s proprietary engineering in supporting prolonged reality. Alibaba’s technological innovation in 3D modeling leverages a neural radiance discipline (NeRF), a neural community technologies for creating novel views of advanced 3D scenes. All through this year’s 11.11, it assisted deluxe retail and furniture brands, like Burberry, Estee Lauder and SK-II, to develop digital shops on the e-commerce system Tmall.

By self-formulated 3D renderings that realistically stand for organic light-weight, flames and natural flowing drinking water, an outside mother nature scene was crafted for sportswear manufacturers like Descente (Japan), to showcase its most up-to-date items in a lively and invigorating natural environment. People can also see the goods in 3 proportions, enabling them to examine facts up near, or test on their decided on watches and equipment pretty much thanks to AR systems. Individuals are also cost-free to organize unique products of home furniture indoors, or tents for out of doors tenting.

A different new expressive conversation arrived from an XR-run marketplace on Tmall and Taobao. Utilizing the automated 3D area development technological innovation from Alibaba’s research institute DAMO Academy, a digital browsing road was built, that includes over 700 products and solutions from 70 makes including 30 internationally-regarded franchises, this kind of as Sanrio’s legendary Hi Kitty, and Hollywood’s franchise Minions. Shoppers can choose their possess avatars, test out the solutions and area them in their virtual shopping carts.

Through this year’s 12-day competition from Oct 31 to November 11, approximately 2 million packages ended up delivered by Xiaomanlv vehicles, Alibaba’s final-mile logistics vehicle. This is double the offer supply quantity from the exact same period of time last yr. The logistics robotic was deployed in above 400 campuses throughout China, which has enormously decreased the time of queuing for deal deliveries throughout peak hours.

A greener 11.11 powered by clear energy

In addition to its cloud computing options assisting to cut down power use, Alibaba Cloud’s five hyper-scale knowledge facilities throughout China also doubled the sum of clear power utilised to support this year’s 11.11 compared to previous 12 months. More than 32 million kilowatt-several hours of energy made use of by Alibaba Cloud to guidance 11.11 this calendar year came from renewable power, up by 30{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1} on a each day basis common compared to final year. Additionally, Alibaba Cloud’s Heyuan information center, the cloud company’s premier hyper-scale information centre in South China, now operates solely on cleanse strength. Alibaba Cloud’s self-formulated immersion cooling technological know-how has minimized the power usage of the info centers, with power use usefulness (PUE) reaching as very low as 1.09 – a entire world-top degree.

Alibaba Cloud has also labored with Tmall to leverage the carbon administration platform, Electrical power Expert. It delivered online carbon footprint modeling, calculations and certifications for more than 40 manufacturers in various sectors, like paper & pulp, foods and personal care, to support them categorize very low-carbon goods, recognize carbon emission methods and conduct knowledgeable sustainability procedures to minimize carbon emissions.

About Alibaba Cloud

Set up in 2009, Alibaba Cloud (www.alibabacloud.com) is the electronic technological know-how and intelligence spine of Alibaba Team. It offers a finish suite of cloud expert services to shoppers around the globe, including elastic computing, databases, storage, community virtualization services, massive-scale computing, security, management and application providers, big details analytics, a machine studying system and IoT services. Alibaba taken care of its place as the 3rd major general public cloud IaaS provider provider globally due to the fact 2018, according to IDC. Alibaba is the world’s 3rd major and Asia Pacific’s primary IaaS service provider by earnings in U.S. pounds due to the fact 2018, in accordance to Gartner.

Check out source edition on businesswire.com: https://www.businesswire.com/information/house/20221113005119/en/

Contacts

Xiaoyi Shao
Alibaba Group
+86 18658170996
shaoxiaoyi.sxy@alibaba-inc.com

Is Your Board Prepared for New Cybersecurity Regulations?

Is Your Board Prepared for New Cybersecurity Regulations?

Boards are now shelling out interest to the need to take part in cybersecurity oversight. Not only are the implications sparking concern, but the new rules are upping the ante and changing the game.

Boards have a specifically essential role to make certain acceptable administration of cyber danger as aspect of their fiduciary and oversight purpose. As cyber threats enhance and organizations around the world bolster their cybersecurity budgets, the regulatory group, together with the SEC, is advancing new prerequisites providers will will need to know about as they enhance their cyber strategy.

Most organizations we’ve analyzed focus on cyber defense alternatively than cyber resilience, and we consider that is a blunder. Resiliency is additional than just protection it’s a system for restoration and business continuation. Being resilient suggests that you’ve done as a lot as you can to defend and detect a cyber incident, and you have also finished as a great deal as you can to make certain you can proceed to operate when an incident takes place. A business who invests only in defense is not taking care of the danger connected with acquiring up and running yet again in the function of a cyber incident.

Our analysis implies that most board associates consider it’s not a matter of if, but when their firm will knowledge a cyber occasion. The top aim of a cyber-resilient firm would be zero disruption from a cyber breach. That will make the focus on resilience far more essential.

New SEC Rules Will Change the Board’s Part

In March 2022, the SEC issued a proposed rule titled Cybersecurity Danger Management, Technique, Governance, and Incident Disclosure.  In it, the SEC describes its intention to demand general public corporations to disclose no matter if their boards have users with cybersecurity experience: “Cybersecurity is by now amongst the prime priorities of lots of boards of directors and cybersecurity incidents and other challenges are regarded as a single of the greatest threats to providers. Accordingly, investors may locate disclosure of no matter whether any board members have cybersecurity skills to be crucial as they contemplate their investment in the registrant as nicely as their votes on the election of administrators of the registrant.”

The SEC will shortly need corporations to disclose their cybersecurity governance abilities, together with the board’s oversight of cyber chance, a description of management’s role in evaluating and running cyber hazards, the applicable knowledge of these kinds of administration, and management’s purpose in implementing the registrant’s cybersecurity procedures, strategies, and procedures. Exclusively, wherever pertinent to board oversight, registrants will be needed to disclose:

  • regardless of whether the complete board, a specific board member, or a board committee is dependable for the oversight of cyber pitfalls,
  • the processes by which the board is informed about cyber hazards, and the frequency of its discussions on this topic,
  • regardless of whether and how the board or specified board committee considers cyber threats as section of its small business tactic, possibility administration, and fiscal oversight.

The fantastic information is that boards are creating progress in this area. Recent study we conducted with analysis lover Proofpoint confirmed that just about two thirds of board customers consider the organization is at threat of a material cyber assault. Almost 3 quarters of respondents felt the investment decision their business has created in cybersecurity is ample, and about the same volume come to feel cybersecurity is a top rated priority.  Seventy-6 {b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1} reported that cybersecurity matters are mentioned at every single board meeting, or extra often than that.

Nevertheless, our investigation also uncovered attitudes and beliefs that have to alter. Only 23{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1} of board associates assume the danger of an attack on their firm is extremely probable. About 47{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1} believe that their business is unprepared for a cyber assault, begging the issue “what are they carrying out about this?”  And about a single 3rd of board customers say they interact with the CISO only when he/she is presenting to the board. There is plainly home for improvement in aligning board members with the companies cybersecurity priorities.

Board Member Cybersecurity Attitude Adjustment

To give proper oversight and comply with the regulatory ecosystem, board members are going to have to up their cybersecurity recreation. It’s no extended suitable to just listen to about the protections set in put, or the effects of the most recent phishing workout. Board members ought to get the place that cyber assaults are probably, and training their oversight role to make sure that executives and administrators have built suitable and ideal preparations to reply and recover. Soon after all, if we believe just about every group has a possible chance of becoming breached or attacked, and it is not probable to be 100{b7c9e2c88beb1a84f22d94ab877a147f4adc4b3519717f3f957a0f34e16918d1} protected from each and every assault, the most rational solution is to make sure the business can get better with minimal or no harm to operations, to the economical bottom line, and to the organization’s reputation.

Creating resiliency in an business requires right oversight from the boardroom dependent on a obvious strategy crafted on business enterprise and economic evaluation. Below are a number of tales about how providers we studied have carried out this.

A monetary companies business CEO realized his board was not well versed in the enterprise context or fiscal exposure possibility from a cyber attack. He hired a third-bash consulting organization to perform a cybersecurity maturity evaluation. The enterprise CISO offered the effects of the report to the business hazard administration subcommittee, producing a effective dialogue all over the small business and economical effect of various investments in cybersecurity. What-ifs about investing in diverse amounts of maturity assisted the board have an understanding of the economical/threat tradeoffs and presented them with both a language and viewpoint required to perform the required oversight of cybersecurity strategies supplied by the government staff.

Another group targeted their board on the alignment of their cybersecurity method and operational risk. The CISO, in collaboration with the main chance officer, leverage fiscal analytics to aid with bridging the hole among the cyber exposures to operational losses. The board was able to recognize the publicity of the corporation from a hazard point of view, resulting in optimizing their cyber insurance plan as a way to mitigate the recently recognized possibility.

By working with the language of risk, resiliency and status in cybersecurity discussions with board customers, operational executives are capable to bridge the gaps that generally manifest amongst the technical requires witnessed to fulfill cybersecurity wants, and the oversight obligations executed by boards. Perhaps this was greatest articulated by Peter R. Gleason, the president and CEO of the National Association of Corporate Directors (NACD), when he mentioned, “We have listened to from many administrators the require to realize the financial publicity ensuing from cyber possibility, heading further than the menace-targeted, complex cyber presentations most boards receive.”

As we significantly rely on boards to prolong their fiduciary duties to cybersecurity designs, operational professionals should also just take a function by presenting individuals programs in a way that align with the way boards ideal add.  Conference the new regulatory prerequisites can be greater achieved by aligning how operational leaders talk about cybersecurity with their boards.

Raise Cybersecurity Knowledge in your Boardroom

In this article are some actionable insights to start currently so your board fulfills (or exceeds) the new SEC recommendations, and provides the ideal amount of oversight to cybersecurity ideas:

1. Establish a frequent language for discussing the sophisticated issues of cyber threat and resilience.

Boards want to simplify bewildering, technical discussions loaded with nuanced safety phrases. It’s not that these are unimportant, it is just not as efficient for the board as an economic investigation that demonstrates how cyberattacks endanger businesses financially in the brief and long term and how the organization will be back again up and jogging, i.e. resilient. Our research displays that insurance firms are taking the direct here, as they shifting the cyber discussion from a hugely technological and ambiguous safety just one to a single exactly where enterprises can fully grasp and effectively handle their fiscal exposure.

2. Retain cyber resiliency on the board’s agenda and in conversations with management.

Our exploration implies that boards are listening to about cybersecurity from administration but the discussions ought to take location extra normally. It’s not a “one and done” kind of choice it is a continually changing and relocating goal.  The far more typically the board is exposed to the cyber-circumstance of their business, the a lot more relaxed and far more pro they grow to be.

3. Build broader bridges amongst cybersecurity executives and board members.

Board associates need to have obtain to, and interactions with, cybersecurity authorities inside the business. Although inviting CISOs to report to the board can help with identification, it does not build robust connections among board associates and protection executives. Come across strategies to facilitate this romantic relationship.

In our investigation, we have noticed board associates reaching out to CISOs in involving board meetings to go over cybersecurity headlines, to share individual incidents that may possibly take place, and just to get superior acquainted. That way, when there is an urgent need to have for the board to weigh in on a cybersecurity situation, the partnership is by now in position and the conversations are much more related and clear.  A cyber incident is not the time to build the bridge that must happen very long in advance of the challenging discussions have to choose put.

Board training to meet up with the SEC prerequisites can take place organically if both the board and running executives just somewhat tweak their technique.  Wondering in terms of resiliency as an alternative of safety, balancing the business and specialized risks, speaking about cybersecurity in terms of financial exposures, and expanding the frequency of dialogue of the cybersecurity landscape confronted by the firm, will assistance directors on boards get ready for and satisfy the SEC policies probable to come.  And that will go a extended way in direction of growing organizational resiliency.

The Beginner’s Guide to ITSM (IT Service Management)

The Beginner’s Guide to ITSM (IT Service Management)

ITSM (short for information technology service management) is defined as the structured practice of meeting an organization’s technology requirements by treating its users as customers and every requirement as a service request, which has to be fulfilled keeping in mind the organization’s resources and quality standards. This article provides an overview of the concept of ITSM. It explains the processes of IT service management and its importance in an enterprise.

What Is ITSM?

ITSM (short for information technology service management) is defined as the structured practice of meeting an organization’s technology requirements by treating its users as customers and every requirement as a service request, which has to be fulfilled keeping in mind the organization’s resources and quality standards. 

It is the process through which IT personnel oversee the comprehensive delivery of information technology services to clients. This comprises IT services’ design, creation, delivery, and support functions and activities.

ITSM is predicated on the premise that information technology should be provided as a service. An example of ITSM scenarios may entail requesting new equipment, such as headphones, for a contact center. One would send your requirement through a portal, complete a request with all pertinent details, and start a routine procedure. Then, one would place the request in the queue of the IT staff, wherein incoming requests are prioritized and treated accordingly.

People often mistake ITSM for basic IT assistance due to their frequent interactions with IT. ITSM teams manage all types of workplace technology, including endpoint devices, servers, and mission-critical software applications.

IT teams use many frameworks to govern their work—additional ideas, such as COBIT, SIAM, IT4IT, Lean Six Sigma, etc. However, ITSM and DevOps are the most frequently discussed. ITIL (Information Technology Infrastructure Library) is one of the most commonly used ITSM methodologies. It may assist businesses in adapting to continuous change and expansion. ITIL 4 is the most recent collection of standards that leads teams through a company- and customer-centric IT framework. It encourages cooperation, ease of use, and feedback.

IT Service Administration (ITSM) is the process of creating, providing, managing, and enhancing the IT services an organization offers to end customers. ITSM, in its essence, covers the management and administration of an organization. It emphasizes harmonizing IT procedures and IT solutions to promote business expansion.

The importance of ITSM in an enterprise

ITSM is advantageous for the IT department, and service management practices may benefit the organization as a whole. It increases efficiency and production. A systematic management method also aligns IT with business objectives by standardizing service delivery depending on finances, resources, and outcomes. It saves expenses and hazards and eventually enhances customer satisfaction.

The top three justifications for using ITSM are:

  1. Minimizing the risk from digital disruption

The risk associated with any transition may seem catastrophically high, especially if the transformation is inadequately conceived, evaluated, or conveyed to the company and team members. With ITSM, the likelihood of large service or business outages is drastically minimized. Formalized rules, procedures, and responsibilities facilitate effective communication with customers and other stakeholders.

  1. Managing costs while scaling

As organizations expand in size and complexity, IT departments must recruit additional personnel or risk being overburdened with tactical and operational activities. IT service management may facilitate the scalability of IT operations without the need for additional staffing, owing to automation tools that decrease IT operators’ manual intervention.

  1. Driving visibility and accountability

ITSM helps IT administrators to monitor the resolution of events and service requests. It provides transparency into the way the IT group provides services. IT managers may check incident logs to ensure services are offered consistently and following company rules and procedures. In addition, they may monitor business activities on the company’s network and identify policy violations.

Currently, information technologies include and integrate duties and responsibilities from all areas of a business. Customers anticipate that companies are competent enough to manage these services on an ongoing basis. Businesses rely on IT Service Management (ITSM) to successfully organize these operations and procedures while guaranteeing that they provide genuine customer value.

See More: DevOps vs. Agile Methodology: Key Differences and Similarities 

The evolution of modern ITSM

One may trace the first application of ITSM principles to when IT companies utilized massive mainframe infrastructures. Over time, the technology and the functions reached a high degree of maturity. Managing change, production scheduling, configuration, recovery procedures, performance management, and availability management are among the most outstanding examples of ITSM approaches.

The critical distinction between mainframe settings of the past and ITSM practices of today is that mainframes often used a centralized system. One may, nonetheless, use ITSM for both centralized and decentralized systems. In addition, mainframe technology was mostly technology-based and provided as stand-alone practices, while ITSM focused on various integrated services to meet business objectives.

ITSM is closely associated with ITIL (Information Technology Infrastructure Library). ITIL is the official document of the Cabinet Office of the United Kingdom, and it addresses several related issues as independent disciplines. The most recent edition of ITIL is its 4th edition, which introduces significant enhancements over the 2011 edition, which is a modification of the 2007 edition.

Frameworks from information technology service management (ITSM)

Let us now examine the various ITSM frameworks currently in use:

  • MOF: The Microsoft Operations Framework (MOF) is a collection of 23 publications that describe the procedures for developing, delivering, and maintaining IT services. The overarching objective of the MOF is to provide an environment where IT and business may collaborate effectively toward operational maturity.
  • COBIT: COBIT, an acronym for Control Objectives for Information and Related Technologies, provides tools for constructing, monitoring, and enhancing the implementation and risk management solutions. The COBIT Core Model has forty goals for governance and management.
  • TOGAF: The Open Group Architectural Framework (TOGAF) is a structure and technique designed to identify business objectives and connect them with software development-related architecture objectives. This 1996-created high-level architecture continues to demonstrate its relevance in the DevOps age.
  • ITIL: ITIL, launched in the 1980s, offers businesses guidance on using technology for transformational change, development, and innovation. ITIL 4 provides the service management skills necessary to adapt IT to cloud, Agile, and DevOps scenarios.

See More: What Is CI/CD? Definition, Process, Benefits, and Best Practices for 2022

Prominent ITSM Processes 

The stages of a service’s life cycle, from conception through delivery, are often referred to as ITSM processes. These are the ten most essential ITSM procedures one must understand:

1. Incident management

ITIL defines an incident as “an unanticipated interruption or degradation of an IT service”. In addition, it highlights that an incident could also include something that is not apparent to the user, such as a component failure identified by systems monitoring tools. The primary objective of this procedure is to return the service to regular functioning as rapidly as possible while minimizing the effect on business activities. Consequently, the SLA must define “normal operation.”

2. Change management

This is one of the most critical processes for enhancing the availability of your IT services. Before any modification, big or small, can be made to the IT Service, it must be planned and well-considered, and one must understand the ramifications. This does not imply that one must slow down changes since the process may be adjusted to each company’s requirements, but it does imply that each change is examined in some way before being implemented. This alone results in fewer errors, enhancing your IT services’ availability.

3. Service order fulfillment

The delivery of software licenses and hardware components must be expedited so that customers may perform their duties or become productive promptly after joining a company. In addition to controlling expenses, businesses must ensure they only purchase what is necessary and do not have depreciating licenses or hardware lying on the shelf. An efficient fulfillment process may prevent this from occurring and guarantee the proper monitoring of assets.

4. Service level agreement (SLA) management

It is essential to understand the business’s IT service requirements. Uncertainty may indicate that the service offered is not supporting the company and that the IT services being delivered exceed its current needs. Both of these might incur costs for a company. This procedure enables the implementation of the appropriate service level agreements (SLAs) to guarantee that the IT service fulfills business requirements.

5. Access management

This method involves account credentials. Because password renewals are the most frequent requests within access management, automating the fulfillment of such requests may allow an organization with, say, 600,000 yearly password resets to save up to $1,850,000 per year. Such cost reductions are frequent among businesses with robust ITSM installation.

See More: What Is Configuration Management? Working, Tools, and Importance

6. Continual service improvement (CSI)

Successfully implementing IT procedures should not be the ultimate stage for any organization. There is always space for growth and improvement depending on challenges that arise, client requests, and user input. Metrics and key performance indicators (KPIs) are crucial in identifying improvement or change areas. IT teams may embrace processes such as IT service appraisals, process assessments, and CSI project management as a component of CSI.

7. Demand and capacity planning

This ITSM process is designed to examine and forecast upcoming requirements for the defined IT services and ensure that sufficient IT resources are readily available to meet current and future corporate needs at a reasonable cost. It is closely linked to financial management, which manages the company’s IT budget, expenditure, and other financials, as well as IT service portfolio or catalog management. 

8. Supplier management

Businesses need to monitor their vendors: are they performing well? Will they remain in existence next year? Are they providing the support and quality that the company requires? Are you spending money on solutions people no longer need? A solid supplier management approach allows businesses to answer these and other questions. It also enables companies to present the vendor with a blueprint of the organization’s plans, allowing them to serve future demands better. If one manages the partnership proactively, one should seldom need to impose SLA penalties.

9. Problem management

Discovering and addressing the causes of problems in an IT service is known as problem management. It is not only a matter of locating and resolving occurrences but also of recognizing and comprehending the underlying reasons for an incident and determining the most effective way to eliminate that root cause. One may resolve the issue after service is restored, but the problem persists till root causes and contributory factors are addressed. Consequently, issue management should be an ongoing and widespread process across many teams, including IT, cybersecurity, and software developers.

10. Knowledge management

Knowledge management is collecting, assessing, storing, and disseminating IT service desk knowledge. It is meant to help service desk teams make the appropriate choices throughout the service life cycle and issue resolution process by regulating and managing the flow of information effectively. ITIL4 identifies knowledge management as the critical process that delivers insights to all other ITSM operations.

See More: What Is Value Stream Mapping? Definition, Working, and Examples

ITSM Best Practices

Now that we have discussed the meaning of IT service management (ITSM) and its key processes in detail, let us look at how you can optimize it. Here are six best practices to help you make the most of ITSM in your organization:

1. Strategically deploy IT service automation

Automation is among the essential ITSM best practices. However, applying automation to inefficiencies will exacerbate that wastage. Therefore, automating the most vital and well-mapped processes is a crucial aspect of automation.

Automation serves many crucial functions, including freeing human agents for more complex duties, providing consumers with self-service so that they may better assist their customers, and establishing a self-reliant self-service value chain. These measures constitute the shift-left initiative, which entails transferring Level 0/1 requests to self-service and conserving agent capacity for Level 2 and above so that consumers are treated more effectively and fulfilled.

2. Be ready to embrace an organization-wide culture shift

Implementing ITSM in businesses may be quite the “culture shock” for the workforce. The implementation process will likely fail if the workforce is not well prepared.

This is why all workers require some rudimentary training and an awareness of the modifications they need to adjust to after implementing the ITSM framework. Organizations can only reverse the mindset until the workers are prepared to accept the transformations that are being made to the organization. Otherwise, it will likely lead to significant resistance and revenue loss.

3. Don’t avoid customizations altogether

Numerous organizations invest in new technology, expecting it to function as advertised. Any customization will likely bring integration problems, complexity, and errors; therefore, IT departments implement technology solutions. However, the effort and time saved with the “out of the box” installation of ITSM solutions don’t necessarily translate into meaningful business value.

Even the most clearly defined technological solutions must be set and often adapted to meet particular business, technical, or service requirements.

4. Augment self-service with knowledge-centric service (KCS)

Knowledge-centered service (KCS) is the ideal complement to self-service since it may become the means for developing and curating information already being gathered as part of the help desk’s troubleshooting and problem-solving activities.

Using this information to create new items in the knowledge base increases the likelihood that someone encountering an issue may discover the relevant content and resolve it without submitting a ticket. Not only does this save valuable time, but it also enables the IT help desk personnel to concentrate on significant issues or concerns rather than the most common inquiries, such as password reset assistance or accessing a calendar to arrange a meeting space.

5. Centralize the fulfillment process using a help desk

Consumers of administrative IT services, whether they’re clients or workers, must have several options for contacting your company in the event of a problem. For instance, they may employ web chat, mail, call, self-service, etc., as communication methods. With so many diverse channels accessible to users, how can a single system record and manage incidents? Effective IT help desk solutions may assist here. ITSM agents may monitor every engagement, regardless of whether users submitted it via online forms or emails.

Keeping track of everything in a single location minimizes switching between multiple tools. Agents will be able to react to all incidents and queries from a single dashboard, as opposed to utilizing a different application for each channel.

6. Improve the effects of ITSM with the right metrics 

IT managers must define key performance indicators (KPIs) for the IT services management solutions and any self-service extensions to fine-tune their strategy and identify process improvements. Without KPIs, it is impossible to determine if the team is doing well. This necessitates methods for defining performance and collecting data that could accurately represent what happened, both negatively and positively. Some of these metrics include:

  • Average ticket resolution time
  • Self-service usage
  • Month-to-month cost per transaction
  • Overall customer satisfaction (CSAT)
  • Level Zero Solvable (LZS), i.e., requests resolved without raising a ticket.

See More: ZenDesk, Spiceworks Cloud Help Desk or N-Able: Which ITSM Tool Is Best for Businesses?

Takeaway 

IT service management, or ITSM, came into its own during the pandemic. ITSM framework and solutions allowed organizations to function relatively smoothly, even remotely. Companies could switch to new ways of working in a matter of weeks and have the technology to support them. ITSM is essential for business success in the best of times and as part of your business continuity plan when technical support is indispensable. 

Did you find the information you were looking for about ITSM? Tell us on Facebook, Twitter, and LinkedIn. We’d love to hear from you! 

MORE ON IT STRATEGY